The Myanmar military’s raid on the KK Park cybercrime center has temporarily slowed the flow of scam operators and workers fleeing across the border to Thailand. Despite the destruction of the site, Myanmar’s online scam activities and associated human trafficking continue in the region. #KKPark #MyanmarCybercrime…
Category: Cyber Security News

Caller ID spoofing causes significant financial losses worldwide, primarily due to scams and frauds using manipulated caller information. Europol emphasizes the need for international cooperation and advanced technical measures to combat these increasingly sophisticated attacks. #CallerIDSpoofing #Europol #VoIP #Swatting #SpoofingAsAService…
A new Android malware family called Herodotus employs random delays in its input routines to mimic human behavior and evade detection. It is offered as a malware-as-a-service and is being used in SMS phishing campaigns targeting users in Italy and Brazil. #Herodotus #AndroidMalware #ThreatFabric #Brokewell
A new malware-as-a-service platform called Atroposia offers cybercriminals advanced remote access trojan capabilities for as low as $200 per month. It features stealthy persistence, data theft, privilege escalation, and evasion techniques, increasing the threat landscape for Windows systems. #Atroposia #Varonis #RARATrojan #CybercrimeTools
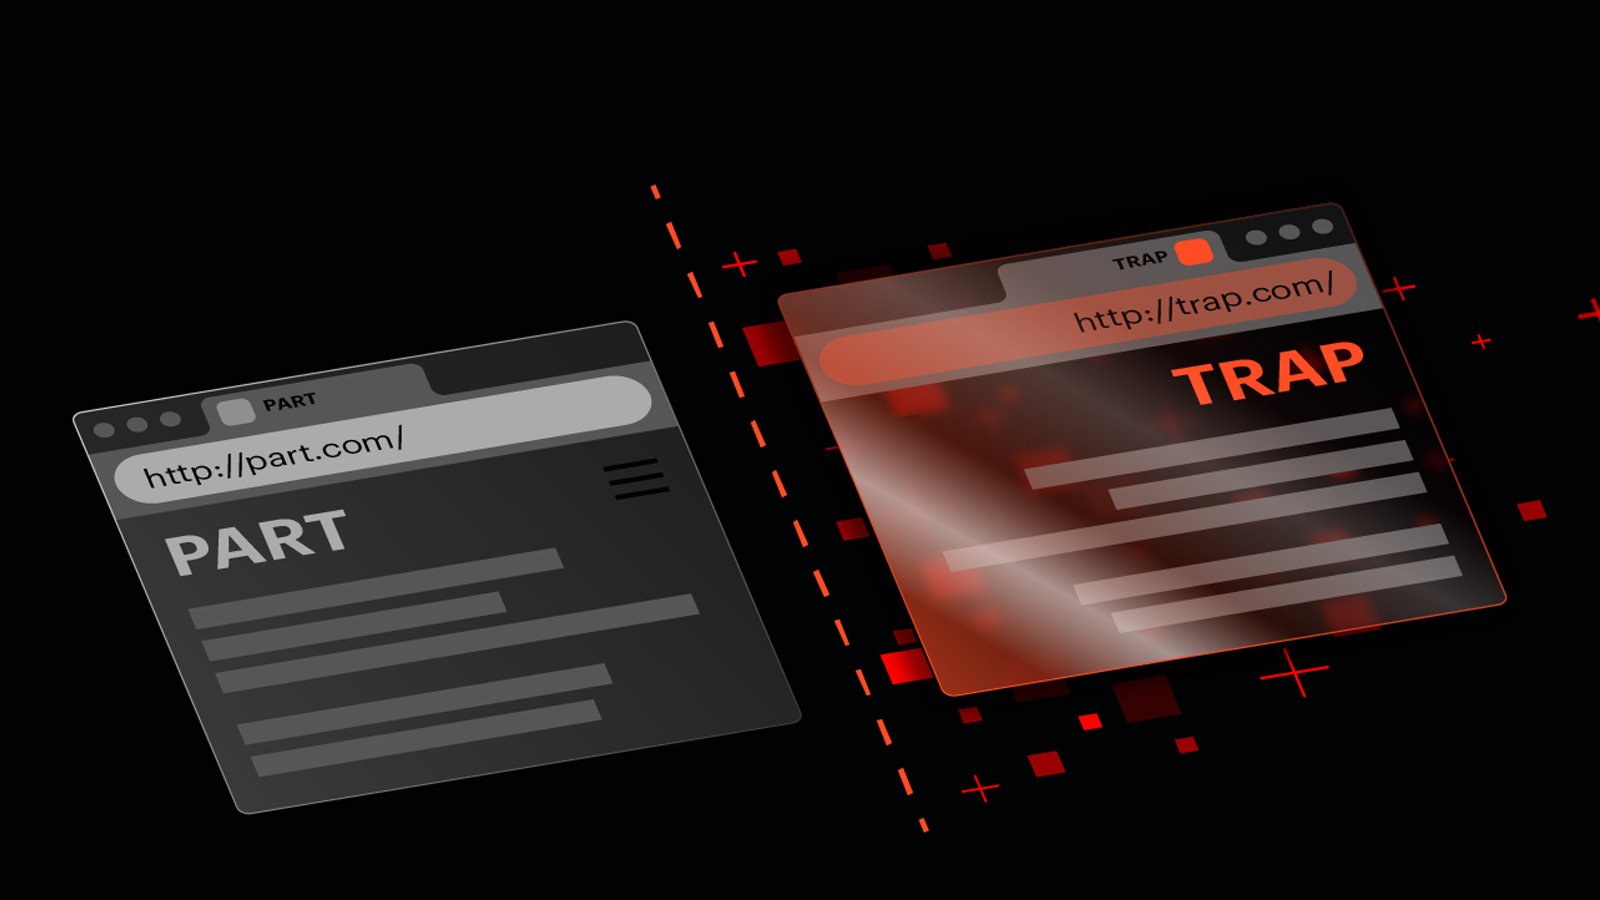
Varonis Threat Labs highlights a decade-old vulnerability involving URL spoofing through BiDi Swap, exploiting Unicode and text direction manipulation. This technique enables attackers to create deceptive URLs that appear legitimate, increasing phishing risks and data breaches. #BiDiSwap #UnicodeSpoofing

A recently patched Google Chrome vulnerability (CVE-2025-2783) was exploited to distribute espionage tools by Italian firm Memento Labs, targeting organizations in Russia and Belarus. This campaign involved spear-phishing emails and the deployment of sophisticated malware like LeetAgent and Dante spyware, linked to known threat clusters such as Operation ForumTroll and TaxOff….

This article discusses strategies for small security teams to enhance Google Workspace security, highlighting key practices such as MFA, secure sharing defaults, and threat detection. It emphasizes the importance of extending native controls with solutions like Material Security to address gaps and automate responses to modern cloud threats. #GoogleWorkspace #MaterialSecurity…

Early cyber threat detection is essential for minimizing damage, reducing costs, and enabling business growth. Utilizing threat intelligence feeds and instant context tools transforms security from a reactive task into a strategic advantage. #ThreatIntelligence #EarlyDetection…
Cybersecurity firm Synthient has uncovered a massive database containing 183 million unique leaked email addresses, primarily shared on Telegram and originating from infostealer malware infections. The data, verified as genuine and integrated into Have I Been Pwned, highlights ongoing risks from credential theft and emphasizes the need for strong authentication measures….
Cybercriminals, likely the FIN11 threat group, have exploited vulnerabilities in Oracle E-Business Suite to steal data from major organizations including Schneider Electric and Emerson. The stolen information, amounting to terabytes, has been leaked on the Cl0p ransomware leak website, indicating severe security breaches. #FIN11 #Cl0p #OracleEBS #Emerson #SchneiderElectric…

Sublime Security has successfully raised over $150 million in a Series C funding round to expand its AI-driven email security platform and global presence. Their innovative security solutions are already adopted by major organizations such as Spotify and Snowflake, addressing sophisticated cyber threats with autonomous AI agents. #SublimeSecurity #AIEmailProtection…

A major international cybercrime ring was dismantled after hackers stole ₹47 crore from Wisdom Finance in a two-and-a-half-hour breach. Authorities linked the operation to Dubai masterminds and arrested two Indian suspects while recovering a partial sum of stolen funds. #CybercrimeRing #InternationalHackers…

A critical vulnerability (CVE-2025-55315) in QNAP’s NetBak PC Agent allows attackers to exploit HTTP Request Smuggling techniques to bypass security controls and access sensitive data. Immediate patching and updating ASP.NET Core runtime components are essential to protect backup systems and prevent unauthorized access. #CVE-2025-55315 #ASP.NETCore #QNAP #BackupSecurity…

Daily Recap, Ransomware Payments show shifting attacker economics in Q3 2025 as payments declined, signaling changing payout dynamics across the threat landscape. The Qilin Ransomware combines a Linux payload with a BYOVD exploit for hybrid attacks, broadening its cross-environment impact. #Qilin Ransomware #BYOVD

A threat actor known as SideWinder has targeted diplomatic entities, including an Indian embassy and organizations across South Asia, with evolving malware deployment tactics. Their campaigns involve sophisticated phishing using PDF and Word documents to deliver modular malware for espionage activities. #SideWinder #ModuleInstaller #StealerBot #NewDelhiEmbassy #SouthAsiaThreats…