A supply chain attack exploited leaked access tokens in the Open VSX registry, leading to malicious extension uploads and a malware campaign called ‘GlassWorm’. The incident was promptly contained, with security measures enhanced to prevent future breaches. #GlassWorm #OpenVSX #EclipseFoundation
Category: Cyber Security News
A hacker claimed responsibility for a major security breach at the University of Pennsylvania, exposing data on 1.2 million donors and internal systems. The attacker accessed sensitive information and used Salesforce Marketing Cloud to send offensive emails, highlighting significant security vulnerabilities. #PennDataBreach #SalesforceHacked

Daily Recap, Nation-state operations show Sandworm leveraging an LNK exploit and an OpenSSH over Tor obfs4 backdoor to target Belarus military, while China-linked groups deploy tools like Airstalk, UNC6384 exploiting CVE-2025-9491, and TICK leveraging Lanscope zero-day. The roundup also covers WSUS vulnerability exploits, Elementor King Addons flaws, and ongoing incidents, including UPenn investigations and Conti-related extradition, with regulatory and defense developments across FCC, CFPB, and password hygiene.
#Sandworm #Airstalk #UNC6384 #PlugX #Lanscope #BadCandy #GlassWorm #Meduza #WSUS #ElementorKing #UPenn #Conti #FCC #CFPB #Sling #ShadowAI #Aardvark
A Chinese-linked hacking group is exploiting the Windows zero-day vulnerability CVE-2025-9491 to target European diplomats and government agencies, deploying PlugX RAT malware through spearphishing campaigns. Experts attribute these operations to UNC6384 (Mustang Panda), highlighting the growing scope of their cyber-espionage activities across Europe. #CVE2025-9491 #MustangPanda…
Chinese cyber-espionage group ‘Bronze Butler’ exploited a zero-day flaw in Motex Lanscope Endpoint Manager to deploy malware and steal sensitive data. This attack highlights the importance of timely patching to prevent exploitation of critical vulnerabilities. #BronzeButler #CVE202561932
Windows 11 Build 26220.7051 introduces new features like Ask Copilot on the taskbar, enhancing AI interaction. The update also improves Xbox gaming, Bluetooth audio sharing, and ARM device performance. #Windows11 #AskCopilot

The Australian Signals Directorate reports ongoing cyber attacks exploiting the critical CVE-2023-20198 vulnerability in unpatched Cisco IOS XE devices, utilizing a new implant called BADCANDY. Threat actors, including Chinese-linked groups like Salt Typhoon, have infected hundreds of devices, emphasizing the importance of applying patches and device hardening. #CVE2023-20198 #SaltTyphoon…

Researchers from Cyble Research and Intelligence Labs have uncovered a sophisticated malware campaign targeting Belarusian military personnel involved in UAV operations, utilizing weaponized ZIP archives and advanced evasion techniques. The operation is linked to Russian threat actor Sandworm (APT44), employing stealthy communication channels such as Tor and OpenSSH for persistent espionage…
A popular WordPress Elementor plugin, King Addons, was found vulnerable to critical security flaws allowing full site takeover. The vulnerabilities include unauthenticated file upload and privilege escalation issues that can be exploited without authentication. #KingAddons #WordPressSecurity…
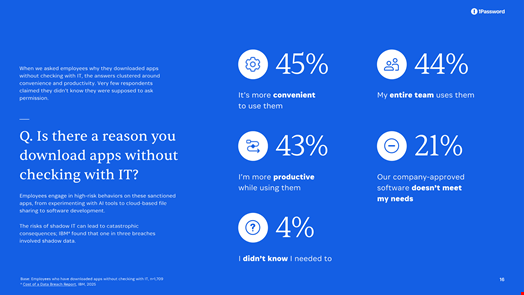
Shadow AI is increasingly prevalent as a form of shadow IT, driven by productivity needs and unawareness of risks. The 1Password report highlights its potential to violate legal standards and introduce malware, urging organizations to implement robust AI governance. #ShadowAI #GenerativeAI…
Daily Recap, A ransomware attack impacted Conduent and 10.5 million people, highlighting extortion and data-exfiltration risks, while law enforcement and threat groups drive attribution updates across Conti, AdaptixC2, and exploits sales networks. The week also covered China-linked APT intrusions, Bronze Butler, Ribbon breaches, and diverse vulnerability advisories affecting VMware, XWiki, Docker, Jenkins, and iMessage, with ongoing ICS disruptions in Canada and rising NFC relay malware across Europe.
#Conduent #Conti #AdaptixC2 #BronzeButler #Ribbon #XWiki #VMware #Docker #Jenkins #iMessage #ICS #BadCandy #Meduza #EclipseOpenVSX
Microsoft is introducing a new “shared audio” feature in Windows 11, enabling simultaneous audio sharing across two Bluetooth devices using Bluetooth LE Audio broadcast technology. This feature enhances user experience for activities like studying or family movie watching on supported devices. #BluetoothLEAudio #Windows11SharedAudio
This article highlights the red flags and detection methods for scams involving fake PayPal emails and tech support fraud. It emphasizes the importance of vigilance and verified contact channels to avoid falling victim to these scams. #PayPalScam #TechSupportFraud…

Attackers are exploiting the recently patched CVE-2025-59287 WSUS vulnerability to deploy infostealer malware on unpatched Windows servers. Multiple threat actors are actively targeting vulnerable systems for data exfiltration and credential harvesting. #CVE-2025-59287 #WSUS #Infostealer #WindowsServers #CyberThreats…

OpenAI has introduced Aardvark, an autonomous security researcher powered by GPT-5, aimed at detecting and fixing code vulnerabilities automatically. This tool integrates into software development pipelines, enhancing security by proactively identifying threats in real-time. #GPT5 #Aardvark…