The web content highlights the increasing security risks associated with modern browsers, which are often overlooked in enterprise cybersecurity strategies. It emphasizes the limitations of traditional browser sandboxing and presents Keep Aware’s solution for real-time threat detection and prevention. #BrowserSandbox #CredentialTheft #MaliciousExtensions #LateralMovement #KeepAware
Category: Cyber Security News
European authorities have arrested nine individuals involved in a cryptocurrency fraud network that stole over €600 million through fake investment platforms. The operation highlights the ongoing threat of large-scale crypto scams and money laundering across Europe. #Eurojust #CryptoFraud

Ransomware attacks are sophisticated threats that encrypt data and demand payment, often employing advanced tactics like double extortion. Wazuh provides an integrated solution for detecting, preventing, and responding to such ransomware threats through comprehensive monitoring and automation. #DOGEBigBalls #GunraRansomware…

Cybersecurity experts have revealed four vulnerabilities in Microsoft Teams that could enable impersonation and social engineering attacks, risking sensitive information and security breaches. Microsoft has issued patches for some of these flaws, but the flaws significantly undermine trust in collaboration tools, attracting malicious actors like cybercriminals and state-sponsored groups. #MicrosoftTeams #CVE202438197…

A critical security flaw in the “@react-native-community/cli” npm package has been patched, which allowed remote attackers to execute arbitrary OS commands. The vulnerability, CVE-2025-11953, posed a significant risk due to its ease of exploitation and broad attack surface. #ReactNative #CVE202511953…
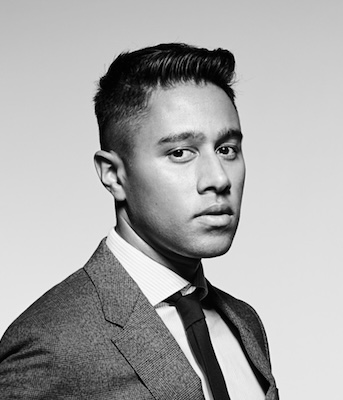
Kunal Agarwal’s journey from a childhood hacker to the founder of dope.security highlights his deep understanding of cybersecurity and hacking culture. His experiences emphasize the importance of ethical hacking and understanding vulnerabilities to develop secure web gateways. #KunalAgarwal #dopeSecurity #CyberHacker #SecureWebGateway…
Cybercriminals are hacking into surface transportation companies through fake load postings and malicious email campaigns to deploy remote access tools and hijack shipments. These attacks facilitate cargo theft and can significantly disrupt supply chains, often involving organized crime groups in various countries. #Proofpoint #CargoHijacking…
A critical vulnerability (CVE-2025-11953) has been discovered in the React Native Community CLI NPM package, which could allow threat actors to execute arbitrary commands on affected systems. The issue has been promptly patched by Meta, urging developers to update to version 20.0.0 to mitigate risks. #CVE202511953 #ReactNative…
Federal prosecutors in the US have charged three individuals involved in BlackCat ransomware attacks on five companies, including medical and engineering firms, between May and November 2023. The accused leveraged insider knowledge from cybersecurity firms to execute these attacks and extort over $1 million through cryptocurrency. #BlackCat #ALPHV #DigitalMint #SygniaCybersecurity…

Apple has released security updates for iOS 26.1 and iPadOS 26.1, addressing multiple vulnerabilities across supported devices. These patches enhance security by fixing flaws that could allow unauthorized data access, system crashes, or privacy breaches. #AppleSecurityUpdate #iOS26.1 #iPadOS26.1 #Vulnerabilities #DeviceProtection…
China’s amended Cybersecurity Law, effective from January 2026, emphasizes AI safety, enforcement, and clearer incident reporting. The revisions expand enforcement measures, clarify data protection obligations, and extend extraterritorial jurisdiction over cyber threats. #CybersecurityLaw #AIRegulation…

Lawmakers are urging the FTC to investigate Flock Safety for cybersecurity lapses, including the lack of mandatory multi-factor authentication (MFA) for law enforcement access. Concerns arise over stolen logins and potential unauthorized access to sensitive license plate data. #FlockSafety #MFA #LawEnforcementDataPrivacy…

Over 760 Android apps are abusing NFC and HCE to steal payment data, targeting global banks and payment systems since April 2024. These malicious applications operate via remote command-and-control servers and Telegram bots, making detection challenging. #NFCRelayAttacks #AndroidThreats…
Australian authorities successfully used a covert messaging app, AN0M, to infiltrate criminal networks and make numerous arrests. The case highlights the effectiveness and legal challenges of exploiting backdoored encryption tools in law enforcement operations. #AN0M #OperationIronside…
Threat actors are exploiting a critical vulnerability in the JobMonster WordPress theme, allowing them to hijack administrator accounts when social login is enabled. This security flaw has been fixed in version 4.8.2, and immediate action is recommended. #CVE-2025-5397 #JobMonster #WordPressVulnerability