
A former Trump official has been appointed as executive chairman of NSO Group, now owned by outside investors. The company, known for spyware like Pegasus, faces legal challenges and court orders restricting its operations, especially targeting WhatsApp users. #NSOGroup #Pegasus #WhatsApp #DavidFriedman…
Category: Cyber Security News

California privacy authorities are advancing legislation to enhance protections for whistleblowers, expand residents’ data deletion rights, and simplify privacy request processes for consumers. These measures aim to strengthen data privacy enforcement and empower individuals and insiders to hold companies accountable. #CaliforniaPrivacy #WhistleblowerProtection…
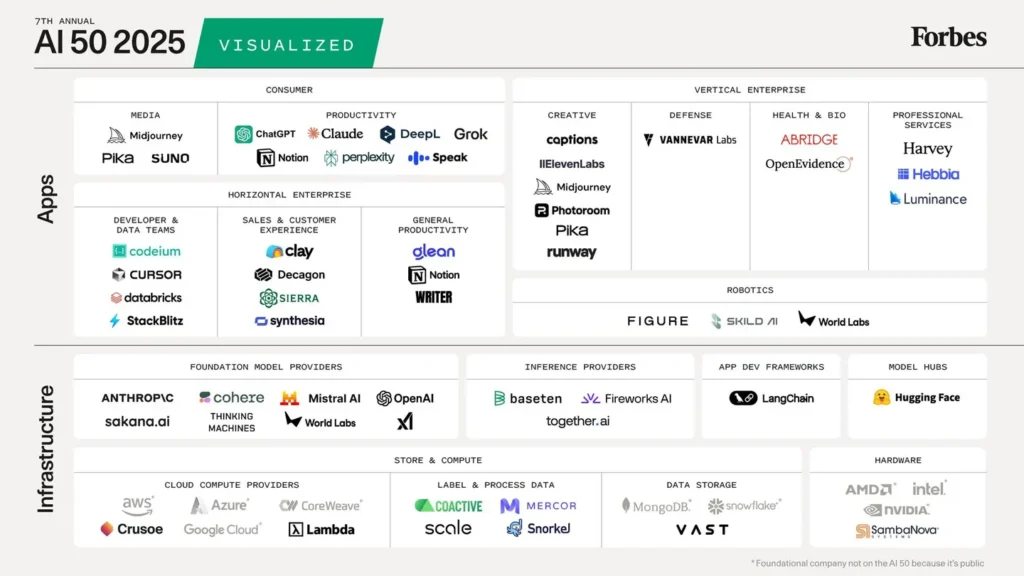
Wiz’s in-depth analysis of GitHub repositories of top AI companies revealed that 65% had leaked sensitive secrets like API keys and tokens, potentially exposing private data and models. Many firms lacked effective disclosure channels or failed to respond to disclosures, underscoring the need for better secrets management and detection strategies. #GitHubLeaks…
Phishing attacks are increasingly occurring through non-email channels such as social media and messaging apps, with LinkedIn becoming a prime target for sophisticated spear-phishing campaigns against executives. Organizations must adapt their security strategies to detect and block these multi-channel threats effectively. #LinkedInPhishing #SpearPhishingCampaigns

A widespread phishing campaign targeting the hospitality industry uses spear-phishing emails impersonating Booking.com to infect hotel systems with PureRAT malware, stealing credentials and personal data. The campaign has been active since April 2025, employing sophisticated social engineering tactics and marketplaces for stolen Booking.com logs. #PureRAT #Booking.com #Expedia #LolzTeam…

The Browser Security Report 2025 highlights how the browser has become the central threat surface for enterprise security, especially with increasing AI and SaaS adoption. It reveals significant gaps in traditional security controls like DLP and EDR in monitoring browser-based risks such as data exfiltration through GenAI, extensions, and session hijacking….

The U.S. government is working to temporarily reopen funding and reauthorize the 2015 Cybersecurity Information Sharing Act (CISA) until January 30, amid ongoing legislative debates. This law plays a crucial role in encouraging private-sector threat data sharing with safeguards, and its long-term renewal is under consideration. #CISA #ThreatSharing #CyberLegislation…

Kyiv and other Ukrainian cities experienced extensive blackouts and communication disruptions following a massive missile and drone attack on Ukraine’s energy infrastructure. Russian cyber and kinetic operations aim to destabilize Ukraine’s critical systems, especially as winter approaches. #Sandworm #EnergyInfrastructure…
The resurgence of GlassWorm malware in the Open VSX registry highlights ongoing threats from malicious extensions targeting developers and organizations. The attack employs Unicode hiding techniques and exploits the Solana blockchain for command-and-control, affecting a global range of victims. #GlassWorm #OpenVSX #Solana #GitHub #CyberThreats…
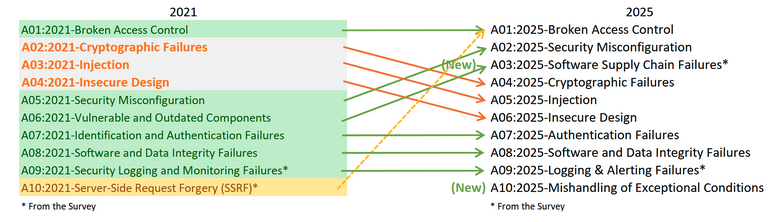
The OWASP Top 10 list for 2025 has been updated with two new categories and a reshuffled order reflecting recent cybersecurity threats to web applications. Notably, Broken Access Control remains top, while Security Misconfiguration and Software Supply Chain Failures have climbed higher on the list. #OWASP #Top10 #SoftwareSupplyChain…

Recent vulnerabilities in the Runc container runtime have been identified that could allow attackers to escape containers and gain root access to host systems. Although patches have been released, these vulnerabilities pose a significant threat to systems running Kubernetes and Docker, especially when untrusted container images are used. #Runc #ContainerBreakouts…
HIPB allows users to check if their accounts have been involved in data breaches, but sensitive breaches require verification. The system includes 74 sensitive breaches like Adult FriendFinder and Ashley Madison, ensuring privacy for affected users. #HaveIBeenPwned #SensitiveBreaches…

Microsoft is launching a new Teams update that allows users to chat with anyone using just an email address, increasing connectivity across multiple platforms. However, security experts warn that this feature significantly enlarges the attack surface, raising risks of phishing, malware distribution, and data breaches. #MicrosoftTeams #B2BGuest #Phishing #OAuth #Malware…
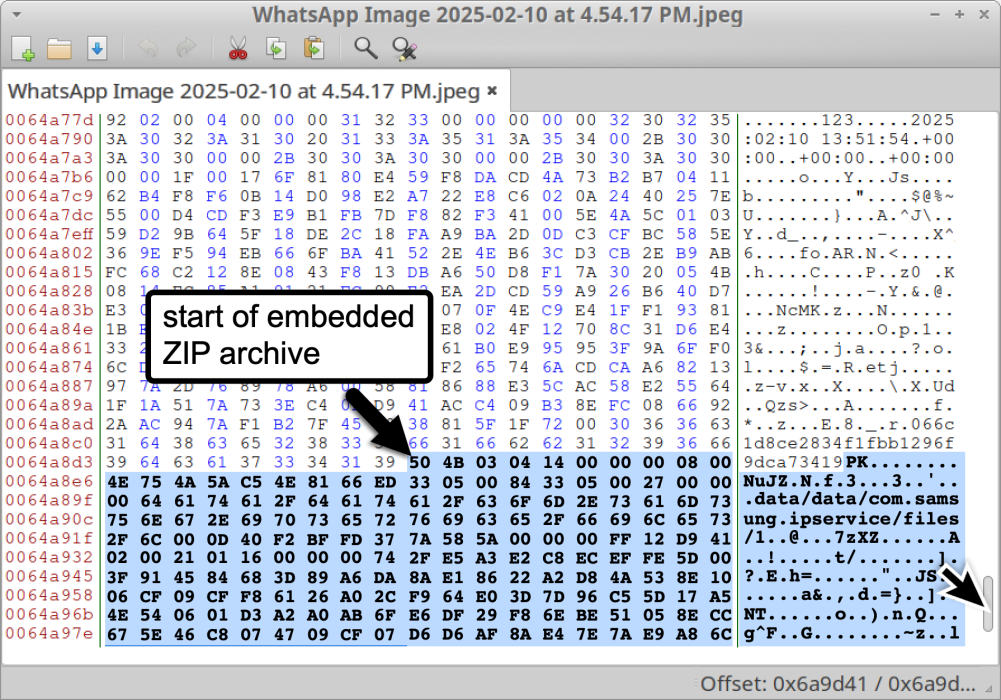
Cybersecurity researchers have uncovered a sophisticated Android spyware campaign called LANDFALL that exploits a zero-day vulnerability in Samsung Galaxy devices to deliver surveillance tools via malicious images in WhatsApp messages. The campaign demonstrates the widespread use of DNG image processing vulnerabilities across mobile platforms, highlighting targeted intrusion activities mainly in the…

Cyberattacks on Android devices surged in sectors like energy, healthcare, and manufacturing between June 2024 and May 2025, highlighting increasing vulnerabilities in critical industries. The proliferation of IoT devices in these sectors has created extensive attack surfaces, with sectors like education and transportation also experiencing significant malware activity. #Zscaler #IoTattacks…