
Amazon’s threat intelligence uncovers a cyber-espionage campaign exploiting zero-day vulnerabilities in Cisco and Citrix systems, targeting critical identity and network access infrastructure. The campaign demonstrates the increasing risk of advanced persistent threats leveraging previously unknown flaws to gain unauthorized access. #CVE-2025-5777 #CVE-2025-20337…
Category: Cyber Security News

Daily Recap, Microsoft patched 63 flaws including a Windows kernel zero-day and released multiple out-of-band updates and ESU fixes, while other vendors issued patches for Intel, Adobe, Ivanti, Synology, SAP, and more amid ongoing exploitation and zero-days in Citrix, Cisco ISE, and Zoom. The report also covers phishing kits, Android and WhatsApp malware, Qilin ransomware activity, North Korea and China-related espionage, and industry events and guidance on AI supply chain attacks.
#Triofox #Citrix #CiscoISE #Zoom #Qilin #FantasyHub #Maverick #NorthKorea #China #AI_Supply_Chain #Pwn2Own
Google has taken legal action to shut down the Lighthouse phishing-as-a-service platform, which has been used by cybercriminals to conduct SMS smishing attacks impersonating USPS and E-ZPass. The platform has affected over 1 million victims worldwide, stealing millions of payment cards and personal information. #Lighthouse #WangDuoYu

Amazon’s threat intelligence team uncovered sophisticated attacks exploiting zero-day vulnerabilities in Cisco ISE and Citrix NetScaler products, deploying custom malware to compromise enterprise networks. The campaigns highlight the importance of layered security and vigilant monitoring of critical identity and network access control systems. #CVE-2025-5777 #CVE-2025-20337…

Google has taken legal action against Chinese hackers operating the Lighthouse phishing platform, which has targeted over 1 million users worldwide. The operation has caused massive financial losses and exploited trusted brands through phishing campaigns. #Lighthouse #SmishingTriad…

Russian authorities are limiting mobile internet access for citizens returning from abroad to prevent Ukrainian drones from using domestic SIM cards for navigation. These measures, often justified as wartime security efforts, have caused widespread outages and are part of broader legal and security policy changes. #UkrainianDrones #FSB #Ulyanovsk…
Federal civilian agencies are failing to adequately patch vulnerable Cisco devices, leaving them exposed to ongoing exploitation by threat actors. CISA has identified devices that remain vulnerable despite being reported as patched, emphasizing the urgent need for corrective action. #CISA #CiscoVulnerabilities…

The U.S. is launching a specialized strike force to dismantle Southeast Asian cyber scam operations that have defrauded Americans of over $10 billion in 2024. The effort involves multiple agencies and targets scam centers supported by armed groups and organized crime, focusing on Burma, Cambodia, and Laos. #Myanmar #CyberScamCenters…

The 2025 CISO Forum Virtual Summit is an online event that connects cybersecurity leaders to discuss emerging threats and strategies, including AI risks and cloud governance. Attendees will gain practical insights on AI integration, risk management, and decentralized governance. #AIrisks #CloudGovernance…
This article emphasizes the importance of shifting from traditional signature-based security measures to behavior-driven detection to combat modern ransomware threats effectively. It advocates for a unified, cloud-native approach like SASE that integrates detection, prevention, and operational controls to minimize damage and improve response times. #MITREATT&CK #TTPs…
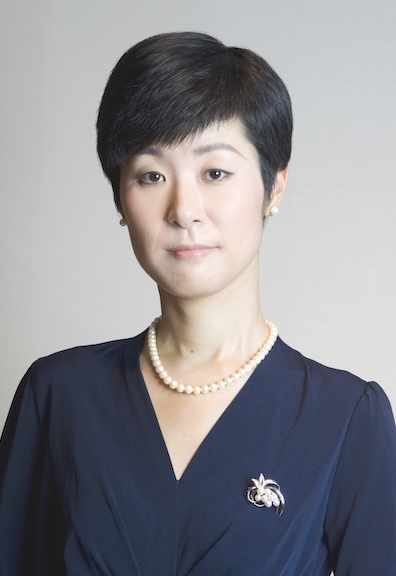
Mihoko Matsubara, an expert in global cybersecurity strategy, discusses differences in cyber threat activity between Japan, Russia, China, and Western countries, emphasizing Japan’s solitary hackers and its cultural factors. She highlights lessons from Ukraine’s resilience against cyberattacks, the strategic behavior of Russia and China, and explores the future challenges posed by…

Australian businesses are increasingly adopting artificial intelligence, but this trend also raises cybersecurity risks, especially for small and medium enterprises. CPA Australia emphasizes the need for stronger digital defenses to protect against AI-driven cyber threats. #CPA Australia #AI cybersecurity…

This article explores the legal battle between The New York Times and OpenAI over data preservation and copyright infringement related to ChatGPT training data. It highlights how ongoing litigation could reshape data retention policies and privacy obligations across the AI industry. #NYTimesLawsuit #OpenAIDataspecific #AIprivacy…
As organizations increasingly use AI assistants and autonomous agents, security frameworks need to evolve to address agentic identities. Applying Zero Trust principles to these AI agents is crucial for maintaining security, accountability, and minimizing risks associated with excessive privileges. #TokenSecurity #ZeroTrust #AIagents #AgenticIdentities
Microsoft has fixed a bug causing false end-of-support warnings on Windows 10 systems despite ongoing security updates. The issue was related to specific Windows 10 editions under the Extended Security Updates program and has been addressed with a recent cumulative update. #Windows10 #ExtendedSecurityUpdates