
President Donald Trump signed a bill that temporarily restores key cybersecurity laws, including the 2015 Cybersecurity and Infrastructure Security Act and the State and Local Cybersecurity Grant Program. This short-term renewal helps prevent immediate cyber threats, but Congress must secure a long-term reauthorization to ensure continuous protection. #CybersecurityAct2015 #StateLocalCybersecurityGrant…
Category: Cyber Security News

Researchers have uncovered a sophisticated large-scale phishing campaign targeting clients of Aruba S.p.A., an Italy-based web hosting provider. The attack involved a fake login and payment site, utilizing advanced techniques like CAPTCHA filtering and Telegram bot coordination to steal sensitive data. #ArubaS.p.A. #PhishingKits…

Kazakhstan has passed a law banning “LGBT propaganda” in media and online, aligning with other authoritarian states’ restrictions on LGBTQ+ content and free expression. Critics argue that these laws aim to suppress dissent and increase restrictions on minority rights and online privacy. #Kazakhstan #LGBTPropaganda #HumanRightsViolations…
CISA warns about two critical vulnerabilities in Cisco Secure Firewall products exploited in the China-linked ArcaneDoor espionage campaign. Immediate patching and assessment are required to prevent malware deployment, data exfiltration, and potential denial-of-service attacks. #CiscoSecureFirewall #ArcaneDoor…
A global law enforcement operation successfully disrupted major cybercrime networks involving Rhadamanthys, VenomRAT, and the Elysium botnet. This coordinated effort seized domains, disrupted servers, and arrested individuals, significantly impacting cybercriminal activities. #Rhadamanthys #VenomRAT #Elysium…
A security researcher uncovered a critical SSRF vulnerability in ChatGPT’s custom GPT actions, which could have led to cloud infrastructure exposure. The flaw was promptly patched by OpenAI after being reported through their bug bounty program. #ChatGPT #SSRF #AzureIMDS #OpenSecurity #BugCrowd…
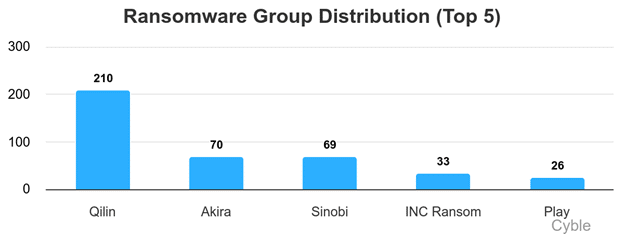
Ransomware attacks increased by 30% in October, reaching the second-highest level on record with 623 incidents. The Qilin group remained the most active threat actor, exploiting critical vulnerabilities and targeting key industries worldwide. #Qilin #LockBit #RansomHub #Medusa…

Law enforcement agencies across nine countries have successfully taken down over 1,000 servers associated with the Rhadamanthys infostealer, VenomRAT, and Elysium botnet, marking a significant international effort against cybercrime. The operation, supported by multiple cybersecurity firms, resulted in arrests and the seizure of domain names, disrupting thousands of infected systems and stealing credentials worth millions of euros. #Rhadamanthys #VenomRAT #ElysiumBotnet #OperationEndgame
CISA has issued warnings and emergency directives urging U.S. federal agencies to urgently patch two critical vulnerabilities in Cisco ASA and Firepower devices, which are actively exploited in ongoing attacks. Despite previous updates, some organizations remain unpatched, leaving their networks vulnerable to remote code execution and complete device takeover. #CISA #CiscoASA #ZeroDay #ArcaneDoor
The Uhale Android-based digital picture frames contain critical security vulnerabilities that allow malware to be downloaded and executed automatically at boot. The devices have been linked to malware families such as Mezmess and Voi1d, raising concerns over widespread security risks. #Uhale #Mezmess #Voi1d #AndroidVulnerabilities
Microsoft is introducing a new “Prevent screen capture” feature for Teams Premium, which blocks screenshots and recordings on Windows and Android devices during meetings. The feature aims to enhance the security of sensitive meeting content but can be bypassed by taking photos of the screen. #MicrosoftTeams #PreventScreenCapture

The UK government has introduced the Cyber Security and Resilience Bill to enhance national security and protect critical infrastructure, including the regulation of managed service providers and critical suppliers. The legislation incorporates updates inspired by the EU’s NIS2 directive, emphasizing incident reporting, supply chain management, and stronger enforcement powers. #NIS2 #CyberSecurityBill…

A major law enforcement operation has disrupted the Rhadamanthys stealer infrastructure, causing widespread panic among threat actors. This coordinated effort has compromised the malware’s command-and-control servers, halting its operations and preventing access through standard methods. #Rhadamanthys #TorOnion #LawEnforcement…

Cybercriminals are reusing old malware like DarkComet RAT by hiding it inside seemingly legitimate Bitcoin software, targeting cryptocurrency users. This malware allows hackers to control infected computers, steal keystrokes, and access sensitive information, posing a significant threat to digital currency security. #DarkComet #BitcoinWallet #CryptoThreats…

A North Korean-linked hacking group, KONNI, has used a sophisticated two-part attack involving spear phishing and remote device wiping to target Android users, primarily in South Korea. The attack leverages trust and popular platforms like KakaoTalk to spread malware and erase data remotely. #KONNI #APT37 #NorthKorea #KakaoTalk #AndroidSecurity…