Fortinet has patched a critical zero-day vulnerability in FortiWeb, which is actively exploited in the wild. This flaw allows unauthenticated attackers to execute malicious commands, prompting urgent patches and mitigation measures. #CVE-2025-64446 #FortiWeb
Category: Cyber Security News
Anthropic reports a Chinese state-sponsored group conducted a largely automated cyber-espionage campaign using its Claude Code AI model, targeting high-value entities. Despite skepticism from security experts about the capabilities and evidence, Anthropic claims this is the first documented large-scale autonomous AI-driven intrusion. #GTG-1002 #ClaudeCodeAI

This article discusses the ongoing espionage campaign by the Iranian threat actor APT42, known as SpearSpecter, targeting high-value Iranian officials and their families. The campaign employs advanced social engineering, credential harvesting, and persistent malware deployment techniques to infiltrate and exfiltrate data from targeted organizations. #APT42 #SpearSpecter…

Cybersecurity researchers have identified critical vulnerabilities in AI inference engines from Meta, Nvidia, Microsoft, and open-source projects caused by unsafe use of ZeroMQ and Python’s pickle deserialization. These flaws could allow attackers to execute arbitrary code, escalate privileges, and compromise AI infrastructure and developer tools. #MetaLlama #NvidiaTensorRT #SGLang…

North Korean threat actors are now using JSON storage services to host malicious payloads and target software developers through professional networking platforms. This campaign involves sophisticated tactics like obfuscated code and multiple payloads such as BeaverTail and TsunamiKit. #NorthKorea #ContagiousInterview…

A Russian port operator, Port Alliance, experienced a multi-day cyberattack involving a DDoS assault aimed at disrupting port operations, but the infrastructure remained operational. The attack involved a botnet of over 15,000 IPs and was part of a broader pattern of cyber threats targeting logistics amid the Russia-Ukraine conflict. #PortAlliance #DDoS…
A coalition of civil society groups and trade unions is protesting the European Commission’s proposed changes to key digital laws, including GDPR and the EU AI Act, which threaten data privacy and protection standards. The proposed amendments aim to streamline regulations but are criticized for weakening protections, increasing data processing, and…
Anthropic’s study reveals a Chinese espionage group utilized their AI system, Claude, to execute autonomous cyberattacks on multiple high-value targets, marking a significant milestone in AI-driven cyber warfare. The attack demonstrated AI’s capability to independently conduct reconnaissance, exploitation, and data exfiltration, raising concerns about the future of autonomous cyber threats. #ClaudeAI…
This cybersecurity roundup highlights recent incidents including the Yanluowang ransomware group’s activities and a significant Windows Kerberos vulnerability. Key developments include targeted ransomware attacks, critical software patches, and innovative bug bounty programs. #Yanluowang #Pwn2Own #CVE-2025-60704…
The US Department of Defense, now called the Department of War, is implementing CYBERCOM 2.0 to enhance its cyber force capabilities through a comprehensive revamp of recruitment, training, and operational models. This initiative aims to improve cyber lethality, retain talent, and build a more agile and specialized cyber workforce to address…
U.S. federal authorities have launched a new task force to dismantle Chinese cryptocurrency scam networks responsible for nearly $10 billion in American losses annually. The team is actively seizing assets, tracking illicit funds, and collaborating internationally to shut down scam operations in Southeast Asia. #PrinceGroup #ChineseOrganizedCrime
Checkout.com was breached by the ShinyHunters group through a compromised legacy cloud storage system, leading to data exfiltration of sensitive merchant information. The company refused to pay a ransom and is enhancing its security, donating the ransom amount to cybersecurity research centers. #ShinyHunters #Checkoutcom #LegacySystem
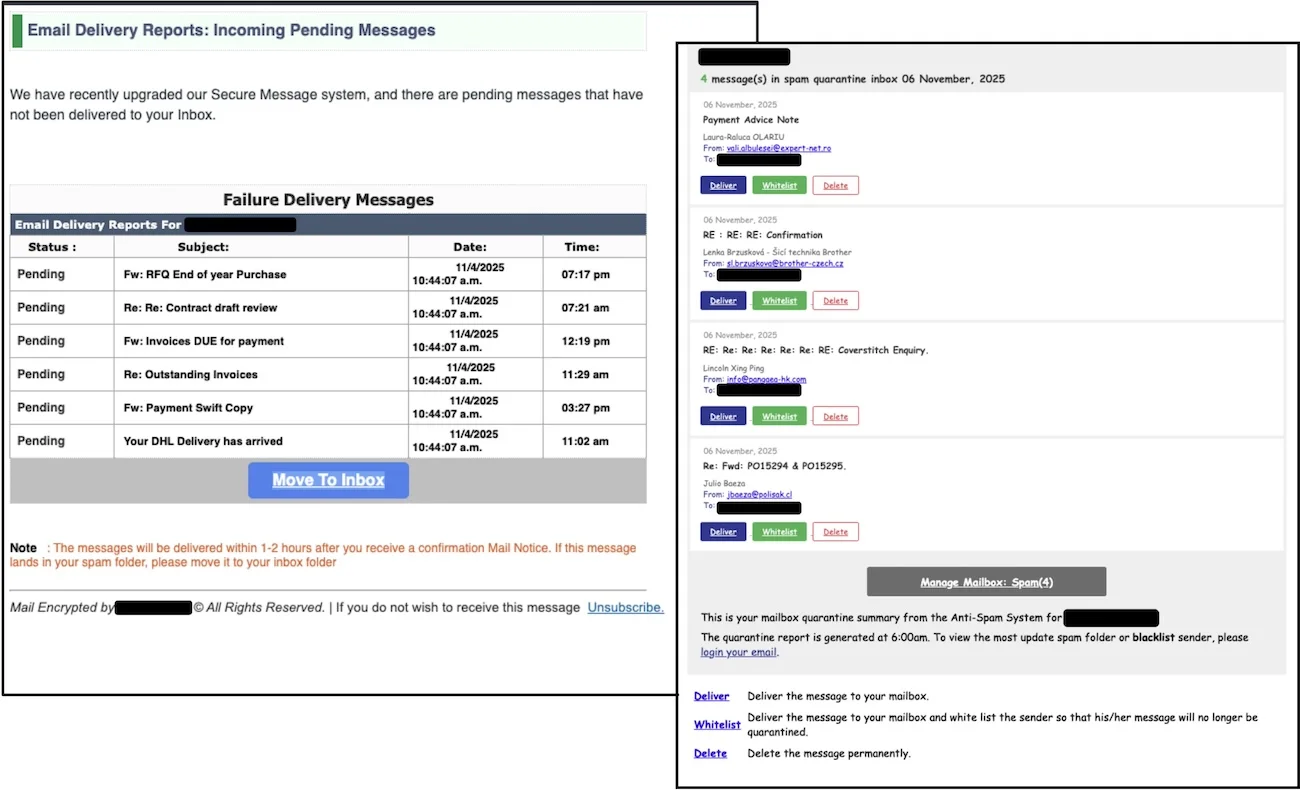
A new phishing campaign is targeting users with emails that appear to come from their own email domain, aiming to steal login credentials through fake login pages. Users are urged to be cautious with unsolicited links and verify email legitimacy to avoid falling victim. #Phishing #ImpersonationEmails…
GitHub has released security updates for several versions of GitHub Enterprise Server to fix known vulnerabilities, including CVE-2025-11892 which may have been exploited. Users are urged to review the advisories and apply patches immediately. #GitHubEnterpriseServer #CVE202511892…

Siemens has reported multiple vulnerabilities affecting their LOGO! series devices, with some vulnerabilities allowing remote code execution and device manipulation. CISA recommends implementing workarounds and staying updated through Siemens’ security advisories to mitigate potential risks. #Siemens #LOGO! #ICSVulnerabilities…