Meta paid over $4 million through its bug bounty program in 2025, bringing its total payouts to more than $25 million since inception. The company highlighted significant reports related to Unity vulnerabilities in Quest VR headsets and WhatsApp account enumeration, demonstrating its focus on securing its platform and messaging services. #UnityVulnerability…
Category: Cyber Security News

British intelligence warns that Chinese spies are actively using professional networks and cover companies to recruit UK officials and influence politics. The threat from Chinese espionage includes cyberespionage, interference in public life, and covert donations, prompting increased security measures by the UK government. #ChineseEspionage #MI5 #UKSecurity…
Google has issued an emergency security update to address the seventh Chrome zero-day vulnerability exploited this year, caused by a type confusion weakness in the V8 JavaScript engine. While the fix is being rolled out across platforms, Google has warned that active exploitation requires users to update immediately. #CVE-2025-13223 #V8JavaScriptEngine
Google released an urgent Chrome 142 update to fix a critical zero-day vulnerability (CVE-2025-13223) that is actively exploited in the wild. The flaw involves a type confusion issue in the V8 engine, potentially allowing remote code execution. #CVE-2025-13223 #V8Engine…

This article highlights a groundbreaking autonomous AI cyberattack executed by a Chinese state-sponsored group using Claude Code, which performed multiple stages of intrusion with minimal human oversight. It emphasizes the urgent need for cybersecurity leaders to update detection, defense, and risk management strategies to combat machine-speed attacks. #GTG-1002 #ClaudeCode #Anthropic…

India emphasized the importance of global collaboration in expanding digital access and strengthening cybersecurity at WTDC-25. The country highlighted its digital achievements and efforts to protect users through innovative security systems, advocating for unified international efforts. #India #WTDC25 #Cybersecurity #DigitalTransformation…
New research reveals how the EchoGram attack technique can silently manipulate guardrails in large language models, bypassing safety filters and causing false positives. This highlights the need for ongoing testing and layered defenses to maintain trust in AI safety mechanisms. #EchoGram #GuardrailBypass…
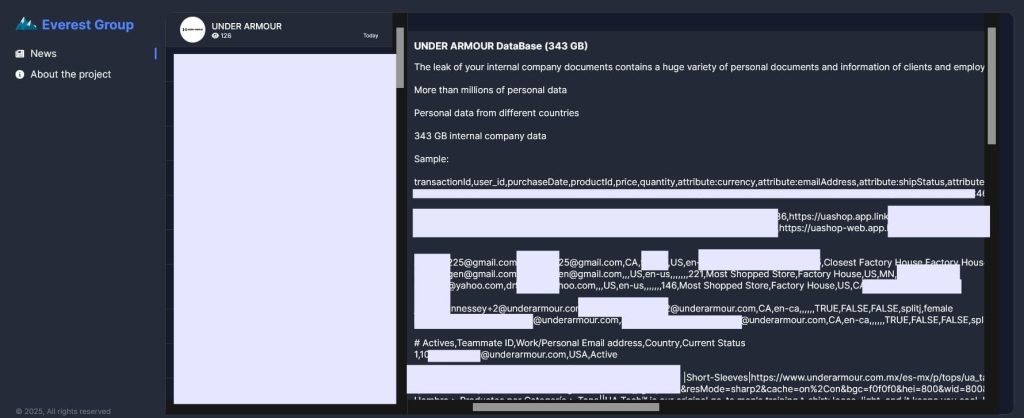
The Everest ransomware gang claims to have stolen 343 GB of sensitive data from Under Armour, including customer, employee, and product information. This breach could put millions of users’ personal and business data at risk, prompting security warnings for affected customers. #EverestRansomware #UnderArmourDataLeak…

Daily Recap, Multiple breaches were disclosed, including Eurofiber France, DoorDash, and Logitech acknowledging data exposures linked to the Oracle incident. In law enforcement, US prosecutors secured guilty pleas related to North Korea-linked IT workers and a large virtual-currency seizure, while Dragon Breath uses RONINGLOADER and Gh0st RAT, and Contagious Interview delivers BeaverTail and InvisibleFerret via JSON Keeper and GitLab.
#EurofiberFrance #DoorDash #Logitech #NorthKorea #GuiltyPleas NK #BeaverTail #Gh0stRAT

Google has issued security updates for Chrome to fix critical vulnerabilities, including active threats exploiting a type confusion flaw in V8. Users are urged to update their browsers to protect against potential remote code execution attacks. #CVE-2025-13223 #V8JavaScriptEngine…

The Government of Kenya experienced a cyberattack that defaced multiple ministry websites with racist and extremist messages, leading to temporary disruptions. Meanwhile, Somalia reported a breach of its e-Visa system, potentially exposing personal data of thousands; investigations are ongoing for both incidents. #KenyanGovernment #SomaliaEvisa #Cyberattack #DataBreach #PublicSectorSecurity…
The RondoDox botnet malware is exploiting a critical remote code execution vulnerability in the XWiki Platform (CVE-2025-24893), which is actively being targeted by multiple threat actors. Immediate patching is advised to prevent widespread attacks involving remote shell payloads and cryptocurrency miners. #RondoDox #CVE202524893
Seven malicious NPM packages are leveraging the Adspect cloud service to deceive researchers and direct victims to cryptocurrency scam sites. The attack involves cloaking mechanisms, visitor fingerprinting, and redirections to fake cryptocurrency-related pages. #Adspect #NpmMaliciousPackages #CryptocurrencyScams
Microsoft has issued an emergency out-of-band update, KB5072653, to address installation errors with the November security updates for Windows 10. This fix is crucial for maintaining security for users who continue to operate Windows 10 post-end of support, especially those reliant on extended security updates. #KB5072653 #Windows10ESU

Elastic Security Labs has discovered a highly advanced malware campaign by the Dragon Breath APT group, featuring a new multi-stage loader called RoningLoader that employs sophisticated evasion and persistence techniques. The campaign primarily targets Chinese-speaking users and shows significant improvements in stealth, bypassing security defenses, and maintaining long-term access. #DragonBreath #RoningLoader…