Microsoft has announced that WINS support will be phased out in Windows Server releases after Windows Server 2025, with full removal expected by November 2034. Organizations are urged to migrate to DNS solutions to avoid service disruptions, as WINS becomes obsolete and unsupported. #WindowsServer2025 #WINSdeprecation
Category: Cyber Security News
Microsoft is testing a new optional feature to preload File Explorer in the background, aiming to enhance launch speeds and overall performance on Windows 11. Additionally, Microsoft is updating File Explorer’s context menu to streamline user experience, with these features currently available to Windows Insiders. #Windows11 #FileExplorerPerformance
Harvard University suffered a voice phishing attack that compromised its Alumni Affairs and Development systems, exposing personal information of students, alumni, donors, staff, and faculty. The breach did not include sensitive financial or Social Security data, but Harvard is working with law enforcement and cybersecurity experts to investigate. #VoicePhishing #OracleZeroDay
Hundreds of malicious packages infected with Shai-Hulud malware have been published on npm to steal secrets from developers and CI/CD pipelines, with stolen data uploaded to GitHub repositories. The attack has rapidly expanded, affecting well-known packages like Zapier, ENS Domains, and PostHog, highlighting the ongoing risk of supply-chain compromises. #ShaiHulud #npmSupplyChain
Modern organizations must transition from legacy patch management tools like SCCM and WSUS to cloud-native solutions to ensure effective security coverage for hybrid workforces. Cloud-based patch management improves compliance, reduces costs, and mitigates risks associated with outdated, on-premises architectures. #SCCM #WSUS #HybridWork #CloudNativePatching

CrowdStrike’s research highlights that DeepSeek-R1 generates more security vulnerabilities in response to politically sensitive prompts, especially when discussing topics like Tibet, Uyghurs, or Falun Gong. The study raises concerns about potential misuse of Chinese-made AI models for generating insecure code and disinformation. #DeepSeek #CrowdStrike…

Multiple cybersecurity firms warn of a second wave of npm supply chain attacks dubbed Sha1-Hulud, which compromise packages and steal sensitive credentials. The campaign employs malicious scripts during package installation to exfiltrate secrets and potentially cause data destruction, representing an escalation in attack tactics. #Sha1Hulud #npmSupplyChain…

The UK lawmakers emphasize the need for software vendors to be held accountable to mitigate growing cybersecurity threats and protect national security. They recommend legal liability for developers, mandatory incident reporting, and increased incentives for cyber resilience. #JaguarLandRover #CyberResilience #SoftwareLiability…

A pro-Ukraine hacktivist group claimed responsibility for disrupting a Russian postal operator in eastern Ukraine, destroying thousands of devices and affecting its systems. The incident coincided with ongoing regional conflicts, highlighting the increased cyber activity in occupied territories. #DonbasPost #UkrainianCyberAlliance…
Mazda confirmed it was targeted in the recent Oracle E-Business Suite hacking campaign, but no system disruptions or data leakage occurred. The attack is linked to the Cl0p ransomware group, which claims to have stolen data from multiple organizations, although the extent of the breach remains uncertain. #Cl0p #OracleEBS #Mazda…
Microsoft introduces an experimental AI-driven feature called ‘agent workspace’ in Windows 11, designed to automate tasks through isolated AI agents with strict security controls. However, Microsoft warns that enabling this feature could pose security risks such as cross-prompt injection and malicious actions, emphasizing careful user management. #Windows11 #AgentWorkspace #AIsecurity #MicrosoftCopilot…
CrowdStrike has confirmed that an insider, not a security breach, leaked sensitive company screenshots to cybercriminals. The threat actors, linked to Scattered Lapsus$ Hunters, paid for access and claimed to have targeted numerous Salesforce customers. #CrowdStrike #InsiderLeak #ScatteredLapsusHunters #Gainsight #Salesforce…

Grafana Labs warns of a critical vulnerability, CVE-2025-41115, that could allow attackers to impersonate administrators through SCIM settings. Organizations using Grafana Enterprise or Cloud plans should review their configurations to prevent privilege escalation risks. #CVE-2025-41115 #GrafanaLabs #SCIM #SAML…
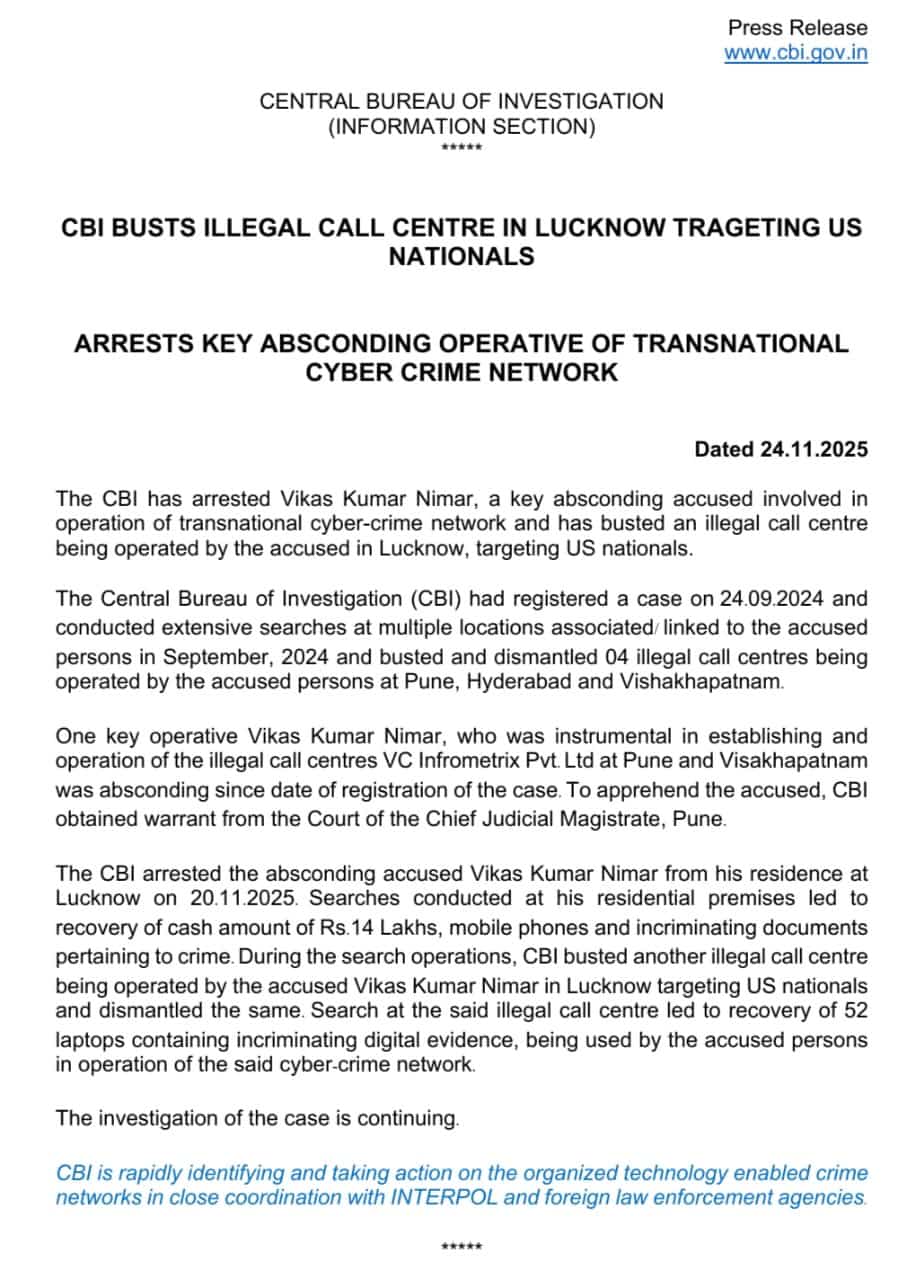
Indian authorities, led by the CBI, have dismantled multiple illegal call centers involved in transnational tech support scams targeting US victims, arresting key fugitive Vikas Kumar Nimar. This ongoing Operation Chakra highlights international collaboration in combating cybercrime, with a focus on cryptocurrency laundering networks and digital evidence recovery. #VikasKumarNimar #OperationChakra…

Black Friday presents a surge in online shopping activity, making it a prime target for cybercriminals using tactics like phishing, malware, and fake websites. Both consumers and retailers must adopt vigilant security practices to resist these evolving cyber threats. #BlackFriday #Phishing #FakeRetailWebsites…