
North Korean-linked threat actors are exploiting the critical React2Shell flaw to deploy EtherRAT, a sophisticated remote access trojan that uses Ethereum smart contracts for command-and-control. This campaign, known as Contagious Interview, targets Web3 developers through fake job offers and leverages the npm ecosystem for malware distribution. #NorthKorea #EtherHiding…
Category: Cyber Security News

A criminal group called the Social Engineering Enterprise engaged in social engineering, hacking, and physical theft to steal over $263 million in cryptocurrency. Several members, including Evan Tangeman, laundered stolen funds and used lavish lifestyles to hide their activities. #SocialEngineeringEnterprise #CryptoTheft…
Microsoft released security patches for 57 vulnerabilities in December 2025, including critical fixes for zero-day flaws actively exploited in the wild. The updates mainly target Windows, Office, and other Microsoft products to prevent privilege escalation and remote code execution attacks. #CVE-2025-62221 #OfficeVulnerabilities…
Adobe has released patches for nearly 140 vulnerabilities across its products, including critical bugs in ColdFusion and Experience Manager (AEM). Prompt application of these updates is urged to protect against potential exploitation. #ColdFusion #ExperienceManager #AdobeVulnerabilities…

Britain has imposed sanctions on Russian media outlets and entities accused of spreading disinformation and conducting cyber activities against the UK and its allies. The UK emphasizes the need for international cooperation to counter hybrid threats like information warfare and cyber attacks. #Rybar #Pravfond #Dugin #i-Soon #IntegrityTechnologyGroup…

The Australian government has implemented a social media ban for children under 16, affecting major platforms like Facebook, TikTok, and YouTube. This law aims to protect minors’ mental health but faces legal challenges, opposition, and enforcement difficulties. #OnlineSafetyAct2021 #AustralianSocialMediaBan…

Daily Recap, AI and browser security dominate this edition as NCSC warns about prompt injection and Google layers defenses in Chrome/Gemini to curb indirect prompts and agentic browsing, while Zero Trust guidance promotes safer AI integrations via the Shared Signals Framework.
Meanwhile, the threat landscape features a high-severity XXE in Apache Tika raising CVE risk to 10.0, new CSS/SVG clickjacking bypass techniques, ValleyRAT deliveries by Silver Fox APT, JS#SMUGGLER-driven NetSupport RAT and malicious VSCode extensions, Shanya EXE packing for stealthy payloads, Broadside botnet activity, STAC6565 targeting Canada, a multi-billion ransomware extortion wave with billions paid and a US bounty on Iranian hackers, plus regulatory and industry shifts impacting AI, data sharing, and outsourced security.
#ValleyRAT #JS#Smuggler #NetSupportRAT #ShanyaEXE #BroadsideBotnet #STAC6565 #Canada #IranianHackers #Chrome #Gemini
Organizations need a systematic approach to maintain visibility, security, and compliance across their IT infrastructure through IT hygiene practices. Wazuh’s open-source platform helps organizations achieve this by providing comprehensive tools for asset management, configuration monitoring, and vulnerability detection. #Wazuh #ITHygiene
Ivanti has issued security updates for multiple vulnerabilities in its Endpoint Manager (EPM) software, including a critical cross-site scripting flaw. These vulnerabilities pose risks primarily to exposed internet-facing instances, with potential remote code execution and session hijacking. #CVE-2025-10573 #EPM #Ivanti
Microsoft has released important cumulative updates for Windows 11 versions 25H2/24H2 and 23H2, addressing security vulnerabilities, bugs, and including new features. These mandatory updates incorporate December 2025 Patch Tuesday security patches and introduce enhancements like enhanced File Explorer dark mode, Virtual Workspaces, and new gaming features.
#Windows11 #PatchTuesday #FileExplorer #VirtualWorkspaces #WindowsSecurity
Microsoft has released Windows 11 KB5072033 and KB5071417 cumulative updates for versions 25H2/24H2 and 23H2 to fix security vulnerabilities, bugs, and add new features.
Today’s updates are mandatory as they contain the December 2025 Patch Tuesday security patches for vulnerabilities discovered in previous months.
You can install today’s update by going to Start > Settings > Windows Update and clicking on ‘Check for Updates.’
December 2025 Update
Fortinet has issued security updates to fix two critical vulnerabilities in multiple products, preventing potential SAML signature abuse. Administrators are advised to disable FortiCloud SSO login temporarily until updates are applied. #FortiOS #FortiWeb #CVE202559718 #CVE202559719
This article summarizes Microsoft’s December 2025 Patch Tuesday, which addressed 57 vulnerabilities including one actively exploited zero-day. Key threats include remote code execution and privilege escalation flaws across diverse Microsoft products. #CVE202562221 #CVE202564671
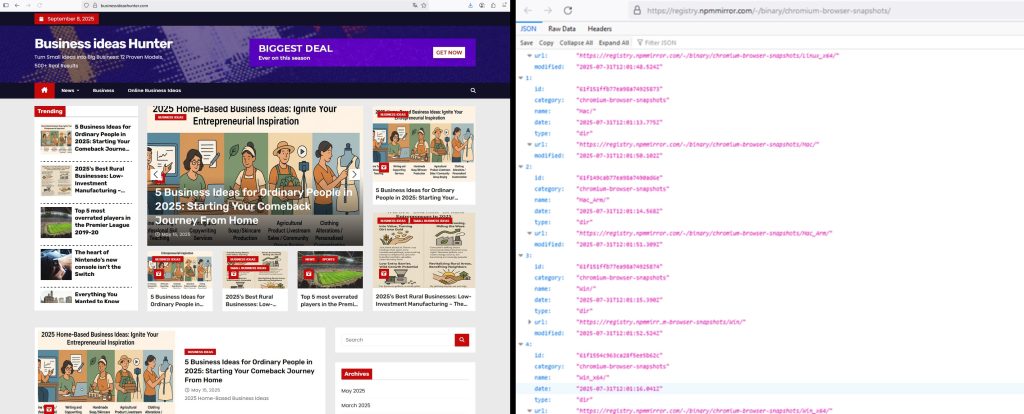
A new trojan named ChrimeraWire is being leveraged to artificially boost search engine rankings by simulating real user activity in Google Chrome. Researchers from Doctor Web detailed its infection process, capabilities, and potential for future expansion. #ChrimeraWire #SEOManipulation…
The rise of initial access brokers has significantly expanded the cyberattack ecosystem, enabling both state-backed and criminal groups to conduct large-scale intrusion campaigns with greater ease and sophistication. This trend emphasizes the increasing importance of prioritizing identity security, supply chain protection, and operational technology hardening for national security and organizational resilience….
Cybersecurity researchers have reported a significant rise in ransomware attacks targeting hypervisors, with the Akira group leading this trend. These attacks threaten virtualized infrastructure by bypassing traditional security measures, emphasizing the need for enhanced defenses. #AkiraRansomware #HypervisorAttacks…