CISA has mandated US federal agencies to patch a critical GeoServer vulnerability (CVE-2025-58360) actively exploited through XXE injection attacks. The vulnerability allows attackers to retrieve files, cause denial-of-service, or perform SSRF attacks, with thousands of instances exposed online. #GeoServer #XXE
Category: Cyber Security News
A new Windows zero-day vulnerability affecting the Remote Access Connection Manager (RasMan) service allows attackers to crash the service and potentially escalate privileges. ACROS Security offers free, unofficial patches via 0Patch until Microsoft provides an official fix. #RasMan #ZeroDayVulnerability

The U.S. CISA has issued an urgent patch recommendation for the CVE-2025-55182 vulnerability affecting React Server Components, which can be exploited through a simple HTTP request to execute privileged JavaScript. Threat actors are actively exploiting the flaw across various platforms, targeting government, infrastructure, and high-value technology assets. #CISA #React2Shell #CVE2025-55182…

The React team has issued security updates to fix multiple vulnerabilities in React Server Components that could lead to denial-of-service or source code exposure. These flaws were identified through active security research and exploit testing, emphasizing the importance of prompt updates. #ReactServerComponents #CVEs #ServerFunctionVulnerabilities…

The browser has become the primary interface for enterprise GenAI use, exposing new security risks due to sensitive data sharing and expanded permissions. Implementing a comprehensive security strategy involving policies, isolation, data controls, and user education is essential to mitigate these risks while enabling productivity. #GenAIThreats #BrowserSecurity…
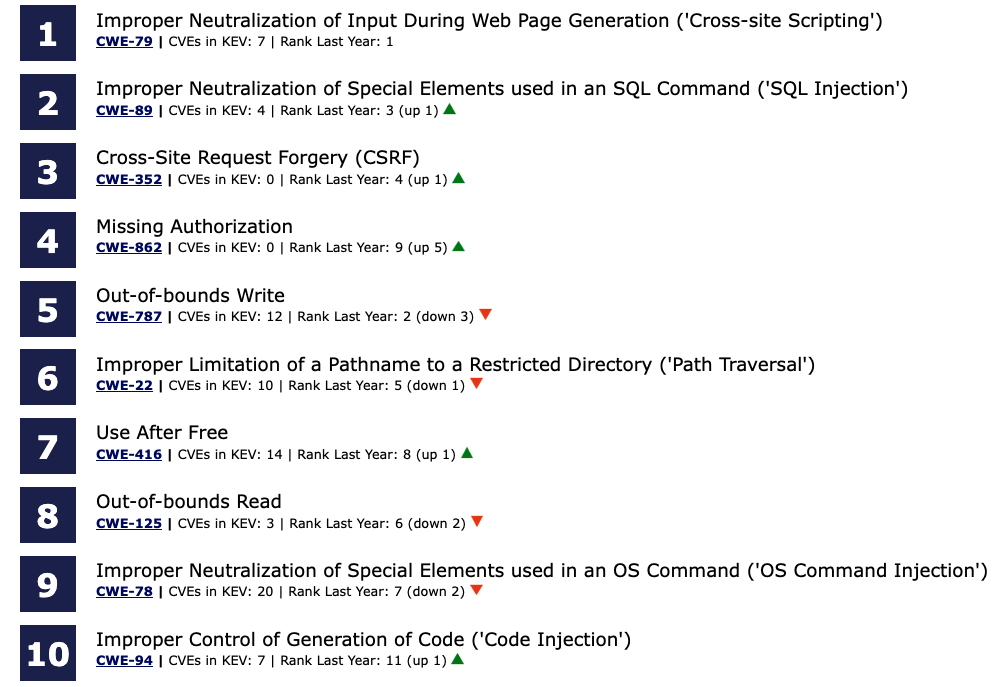
The MITRE Corporation has updated the CWE Top 25 list for 2025, highlighting the most dangerous software weaknesses and their current rankings. Key vulnerabilities include cross-site scripting, SQL injection, and missing authorization, with new entries such as buffer overflows and improper access control. #CWE #MITRE #XSS #SQLInjection #BufferOverflow #AuthorizationBreach…
The US CISA agency has issued a warning about malicious exploitation of a critical vulnerability in GeoServer (CVE-2025-58360), which can lead to data breaches, SSRF attacks, or DoS. The vulnerability has been actively exploited in the wild since late November, prompting urgent patches and updates. #GeoServer #CVE202558360…

A US-based company, Fieldtex Products, suffered a data breach attributed to the Akira ransomware group, exposing sensitive healthcare information of over 238,000 individuals. The attack involved unauthorized access to protected health data and the theft of extensive corporate documents. #Akira #FieldtexProducts…

A cyberattack targeted Russia’s digital military draft system, compromising sensitive data and source code from a key developer, Micord. The breach raises concerns about the security of Russia’s modernization efforts for its wartime enlistment process. #Cyberattack #RussiaDraftSystem…

Daily Recap, authorities pursue a broad set of cybercrime actions—from Myanmar digital arrest-fraud charges and Accenture fraud to FedRAMP-related contractor concerns and indictments targeting Russian-linked hacktivists. The recap also flags data breaches and privacy risks at Pierce County Library, LastPass fines, Petco Vetco exposure, doorbell and camera privacy debates, and widespread vulnerabilities and malware activity including NANOREMOTE, BRICKSTORM, Mirai, CastleLoader, Spiderman Phishing, DroidLock, and large Docker Hub credential leaks.
#NANOREMOTE #BRICKSTORM #WarpPanda #LastPass #PierceLibrary #Petco #Vetco #DroidLock #CastleLoader #SpidermanPhishing #DockerHub #Mirai
An international coalition led by ACE has successfully dismantled India’s popular piracy platform MKVCinemas and other illegal streaming services, significantly reducing online copyright infringement. These efforts targeted platforms and tools with millions of visitors, emphasizing the importance of sustained anti-piracy actions to protect creators and lawful content distribution. #MKVCinemas #Photocall #Streameast #RareBreedTV
The MITRE report highlights the top 25 most dangerous software weaknesses from June 2024 to June 2025, emphasizing their severity and exploitation potential. Notably, Cross-Site Scripting remains the most common vulnerability, while new entries like Buffer Overflows and Authorization Bypass are gaining importance. #CrossSiteScripting #BufferOverflow #CISA

A severe security vulnerability affecting OSGeo GeoServer has been added to the CISA KEV catalog due to active exploitation. It involves an XML External Entity (XXE) flaw that could allow attackers to access files, conduct SSRF, or cause DoS attacks. #CVE2025-58360 #GeoServerVulnerability…
President Donald Trump has signed an executive order to prevent states from creating their own regulations for artificial intelligence, emphasizing the need for a unified approach in the AI industry amidst global competition. The order aims to challenge state laws, restrict funding for non-compliant programs, and promote federal oversight of AI…
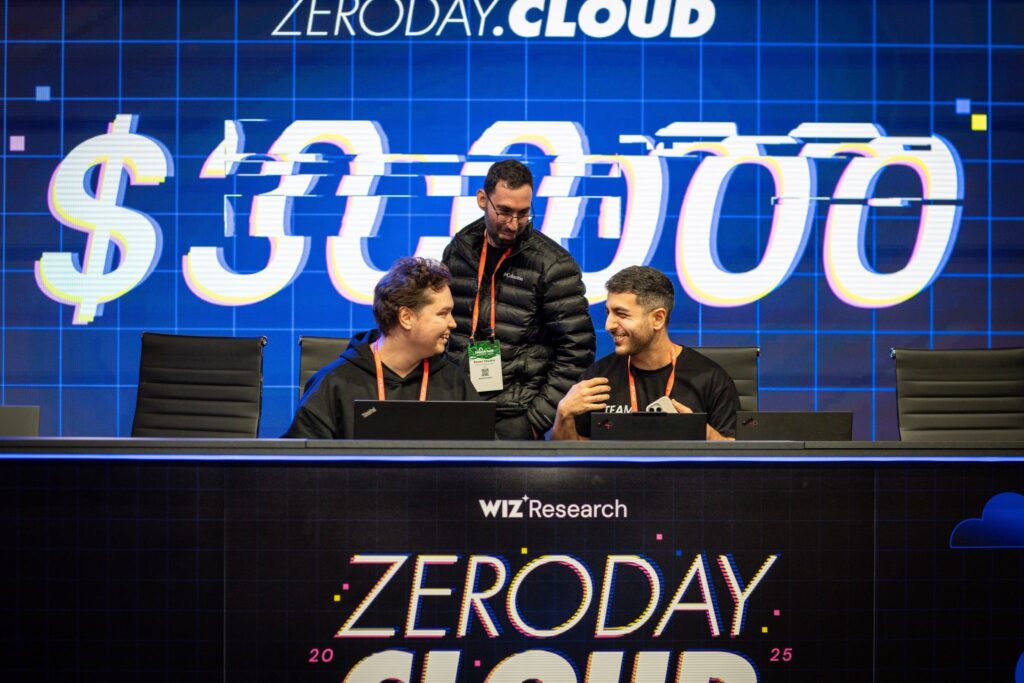
Researchers earned $320,000 at the Zeroday.Cloud hacking event for discovering vulnerabilities in cloud and AI technologies. The competition involved major cloud providers like AWS, Google Cloud, and Microsoft, focusing on open source systems such as Redis, PostgreSQL, and the Linux kernel. #ZerodayCloud #Redis #PostgreSQL #LinuxKernel…