
Cisco reports a critical cyberattack targeting its Secure Email Gateway and Web Manager appliances exploiting CVE-2025-20393. The campaign allows attackers to gain root access and maintain long-term control over compromised devices, emphasizing the importance of proper configuration and security measures. #CVE-2025-20393 #AsyncOS…
Category: Cyber Security News
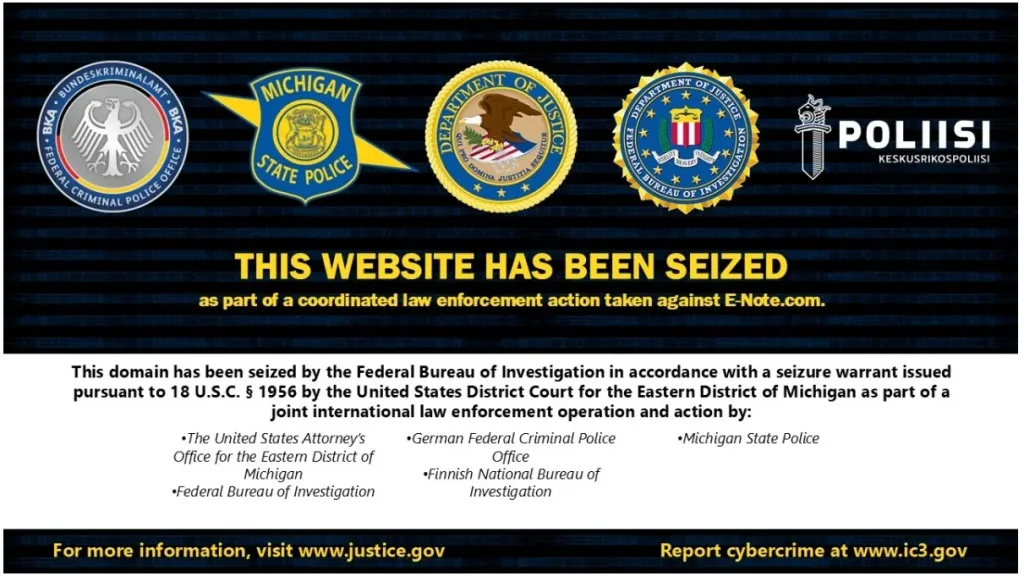
The FBI, in collaboration with international partners, has dismantled the E-Note cryptocurrency exchange, which was used for laundering over $70 million linked to cybercrime activities such as ransomware and account takeovers. This operation highlights the global effort to combat transnational cybercriminal infrastructure and money laundering networks.
#FBI #E-Note #cryptocurrency #ransomeware #moneylaundering…

Daily Recap, state-sponsored GRU-linked groups such as Sandworm and APT44 have pivoted from zero-days to weaponizing misconfigured edge devices, persistently targeting energy, telecom and cloud infrastructure across 2021–2025, with some operations disrupted by private defenders. The recap also highlights a range of threats, from Android RaaS Cellik and GhostPoster campaigns to credential phishing by APT28 and ForumTroll, notable incidents at PDVSA, KT, Askul and Hama Film, and ongoing supply-chain and vulnerability activities involving Fortinet flaws and AWS IAM abuse. #GRU #Sandworm #APT44 #APT28 #ForumTroll #GhostPoster #Cellik #TracerFody #PDVSA #KT #Askul #HamaFilm
Cisco has issued a warning about an unpatched zero-day vulnerability (CVE-2025-20393) affecting its Secure Email Gateway and Web Manager appliances, which is being exploited in active attacks linked to Chinese threat actors. Organizations using affected systems should restrict access, monitor logs, and follow Cisco’s security advisories to mitigate risks. #CVE2025-20393 #UAT9686 #AquaShell
Threat actors are exploiting WhatsApp’s device-linking feature through a campaign called GhostPairing, which allows them to hijack accounts without requiring authentication. This attack enables access to chat history and media, and can lead to impersonation and fraud, spreading beyond Czechia to other regions. #GhostPairing #WhatsAppHijack
Amazon’s AWS GuardDuty team has identified a crypto-mining campaign that exploits compromised IAM credentials to target EC2 and ECS services, employing persistent methods to hinder incident response. The threat actor used a malicious Docker image and automated scripts to maximize mining operations, causing financial and resource exhaustion for AWS customers. #CryptoMining #IAMCompromise
French authorities arrested a 22-year-old suspect following a cyberattack on the Ministry of the Interior, linked to a protest by BreachForums. The attack involved unauthorized access, data theft, and potential revenge claims from hacking groups. #BreachForums #ShinyHunters
The Zeroday Cloud hacking competition in London awarded $320,000 to researchers for discovering critical zero-day vulnerabilities in cloud infrastructure components. The event highlighted significant security flaws in database systems, containerized environments, and cloud tenancy isolation, showcasing the evolving cyber threat landscape. #Redis #PostgreSQL #LinuxKernel #MariaDB #CloudSecurity

SonicWall has released security updates to fix a vulnerability in SMA 100 series appliances that is actively being exploited. The flaw allows local privilege escalation and, when combined with another vulnerability, can enable remote code execution with root privileges. #CVE2025-40602 #SonicWall #SMA100…

Cisco has issued a warning about a critical zero-day vulnerability in Cisco AsyncOS software, actively exploited by a China-linked APT group known as UAT-9686. The threat involves bypassing security with remote command execution, affecting multiple appliances and prompting federal mitigation efforts. #CVE202520593 #UAT9686…

ASUS Live Update software has a critical vulnerability (CVE-2025-59374) caused by a supply chain compromise, currently actively exploited. This issue stems from malicious code embedded in affected versions, linked to the Operation ShadowHammer campaign targeting specific users. #OperationShadowHammer #CVE2025-59374…

A digital rights organization, noyb, claims that TikTok and Grindr violate European data protection laws by tracking user activities across apps without proper consent, especially involving sensitive data like sexual orientation. The case highlights the ongoing debate on data privacy, app transparency, and enforcement of GDPR regulations in Europe. #TikTok #Grindr…

The FBI and international law enforcement agencies shut down the cryptocurrency exchange E-Note, which facilitated over $70 million in illicit transactions related to ransomware and cyberattacks. The operation targeted a Russian national, Mykhalio Chudnovets, who operated E-Note and was involved in money laundering since 2010. #E-Note #MykhalioChudnovets…

Recent cybersecurity breaches affected SoundCloud, PornHub, and Mixpanel, exposing user data and disrupting services. Investigations reveal these incidents involve hacking groups like ShinyHunters, with companies working alongside law enforcement to mitigate damage. #Mixpanel #ShinyHunters…

A Chinese cyber-espionage group called Ink Dragon is transforming compromised servers into active communication nodes using sophisticated relay architecture. Their expansion into European government targets highlights the evolving threat landscape and the importance of patching vulnerabilities. #INKDRAGON #ShadowPad…