
A China-linked APT group, Evasive Panda, conducted targeted cyber espionage campaigns using DNS poisoning to deliver the MgBot backdoor. The group has shown advanced techniques to evade detection and maintain persistence on victim systems. #EvasivePanda #MgBot…
Category: Cyber Security News

Trust Wallet has urged users to update their Chrome extension to prevent further losses after a security incident affected about $7 million worth of digital assets. The breach involved malicious code in version 2.68, which allowed hackers to extract wallet mnemonics and drain funds, possibly by insiders or nation-state actors. #TrustWallet…

Georgian authorities have detained former security service head Grigol Liluashvili on bribery charges related to protecting illegal call centers involved in international scams. The case highlights ongoing corruption and the complicity of top officials in facilitating cyber-enabled financial crimes. #Georgia #ScamCallCenters…

Pro-Russian hacker group NoName057(16) claimed responsibility for a DDoS attack that temporarily disrupted France’s postal and banking services during the holiday season. The attack impacted online parcel tracking, mail delivery, and banking access, but authorities confirmed no customer data was compromised. #NoName05716 #DDoSattack #LaPoste #FrenchGovernment…

ParrotOS 7 introduces a complete rewrite of the operating system, focusing on architectural improvements and community-driven development. The new version features a switch to KDE Plasma 6, Debian 13, and added AI tools, supporting RISC-V and other platforms. #ParrotOS #KDEPlasma6 #Debian13 #AItools #RISC-V…
A critical vulnerability in the Net-SNMP software, CVE-2025-68615, affects its snmptrapd component and can lead to crashes or remote code execution. Organizations should urgently update to version 5.9.5 or later and ensure proper network segmentation to mitigate risks. #NetSNMP #CVE202568615…

Daily Recap, CISA warns of active exploitation of the Digiever DS-2105 Pro remote-code-execution flaw and a severe MongoDB RCE, both now listed in Known Exploited Vulnerabilities. The activity includes threats from APT37 and campaigns like IconCat and PCPcat, signaling espionage-style operations and large-scale server compromises. #DigieverRCE #APT37
Multiple users reported their Trust Wallet Chrome extension was compromised on December 24, leading to over $6 million in stolen cryptocurrency assets. Threat actors exploited a malicious update and a phishing campaign to exfiltrate wallet data and trick users into revealing seed phrases. #TrustWallet #ChromeExtensionSecurity

A severe security vulnerability has been identified in LangChain Core, enabling attackers to extract secrets and manipulate LLM responses through prompt injection. Users are urged to update to the latest patched versions to mitigate potential exploitation. #LangChainCore #CVE-2025-68664…

An Uzbek surveillance system used for tracking vehicles has been left publicly exposed online, revealing sensitive data including locations and footage of vehicles across major cities. This security lapse highlights the risks of unsecured license plate monitoring systems domestically and internationally. #Uzbekistan #licenseplatereaders…
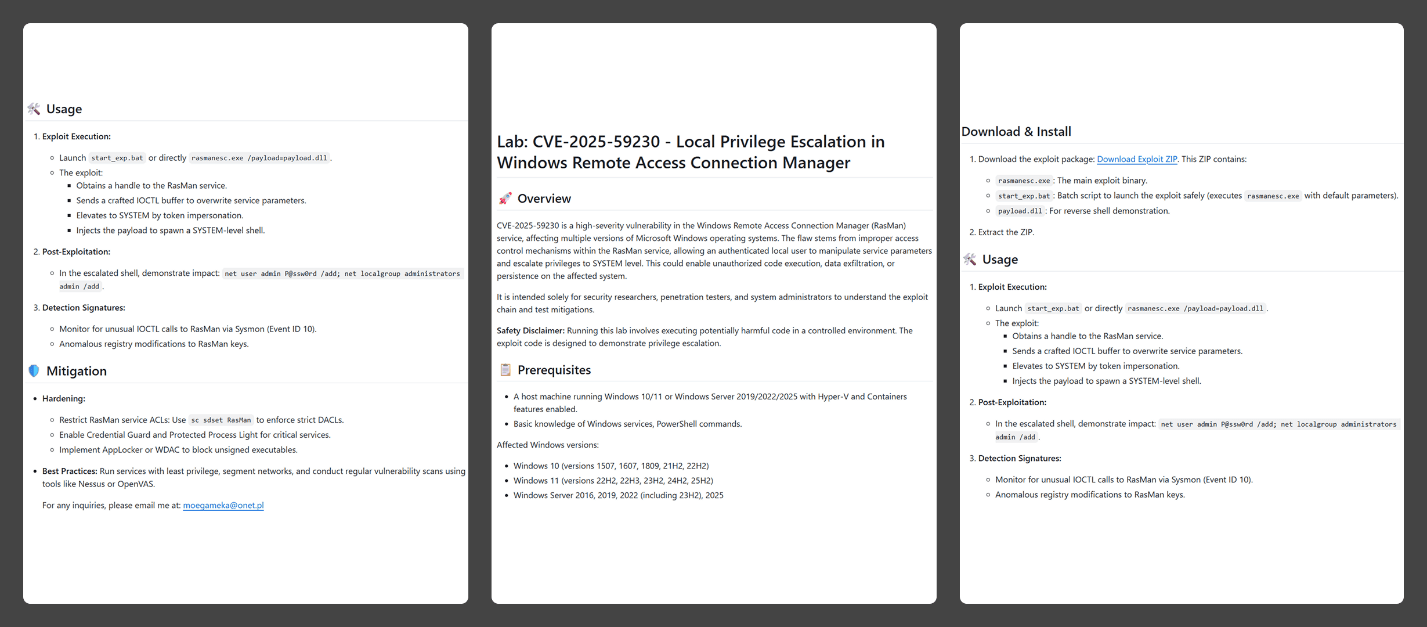
In early 2025, the Webrat malware family was discovered targeting gamers, security researchers, and students by disguising itself as exploits, game cheats, and cracked software. The campaign involves distributing malicious files via GitHub and other repositories to infect systems and facilitate remote control and data theft. #Webrat #CyberThreats…

The U.S. National Institute of Standards and Technology is partnering with MITRE to establish two research centers aimed at advancing AI and safeguarding critical infrastructure against AI-enabled cyber threats. These initiatives focus on fostering AI-driven innovation in manufacturing and infrastructure sectors, emphasizing collaboration with industry stakeholders. #NIST #MITRE #AIResearchCenters #CriticalInfrastructure #CyberThreats…

The 2022 LastPass data breach’s encrypted vault backups have been exploited over years, with Russian cybercriminals cracking weak master passwords to steal cryptocurrency assets until late 2025. Threat analysis reveals links to Russian exchanges and sophisticated laundering techniques, emphasizing ongoing risks in digital asset security. #LastPass #TRMLabs #RussianCybercriminals #CryptocurrencyTheft…

ThreatsDay Bulletin: Stealth Loaders, AI Chatbot Flaws AI Exploits, Docker Hack, and 15 More Stories
Cybersecurity is evolving with attackers blending into normal tech environments using sophisticated tactics like open-source tools, AI, and social engineering. The future of defense depends on increased awareness of these subtle and innovative threats. #Nezha #RokRAT…

The U.S. CISA has listed a critical security flaw in Digiever DS-2105 Pro NVRs, which is actively exploited by cyber attackers. Threat actors are using this vulnerability to deploy botnets like Mirai and ShadowV2, especially on unpatched devices. #CVE-2023-52163 #Mirai #ShadowV2…