Meta confirmed a password reset vulnerability on Instagram but denied a data breach, despite claims of leaked user data online. Cybercriminals leaked information from over 17 million accounts, but cybersecurity experts state this data is from a 2022 leak and not associated with the password reset issue. #Meta #Instagram #DataLeak #Malwarebytes…
Category: Cyber Security News
Cyber Insights 2026 predicts a rapidly evolving cybersecurity landscape where CISOs face increasing complexity, AI-induced risks, regulatory pressures, and burnout. The role will transform into a broader executive position, emphasizing AI governance, personal liability, and organizational resilience. #CISO #AIThreats…
Dr. Amit Chaubey discusses the expanding “2026 Business Blast Radius,” emphasizing how external dependencies and geopolitical risks threaten global infrastructure and organizational resilience. The rising cyber threats, including AI-enabled identity attacks and cloud exploits, demand a collective, proactive security approach. #ChakraX #GlobalCyberThreats…

Cybersecurity researchers have uncovered widespread reconnaissance campaigns targeting large language models (LLMs), indicating plans for future cyberattacks. The campaigns involved probing major LLM families and exploiting SSRF vulnerabilities, highlighting the expanding attack surface of AI systems. #GreyNoise #CVEExploitations…

Daily Recap, state-linked actors from China and Russia exploited VMware ESXi zero-days and edge-device flaws and deployed UAT-7290 Linux malware/ORB nodes to breach telecoms and energy-sector targets. Phishing and crypto-crime activities persisted, with the FBI warning of Kimsuky using malicious QR codes in spear-phishing and misconfigured email routing enabling internal-spoofed phishing, while the Astaroth worm spread in Brazil and the Truebit theft highlighted ongoing ransomware and crypto-exploitation alongside privacy and data-breach concerns. #UAT-7290 #ESXi #Astaroth #Truebit #Kimsuky #FBI #NSA #Cisco #Grok #X #ChatGPTHealth #EEOC #CPPA #CISA #PowerPoint #HPE #DNS

North Korean APT group Kimsuky has been using spear-phishing campaigns involving malicious QR codes to target government agencies, think tanks, and strategic firms worldwide. The FBI warns that these Quishing attacks are highly effective, bypass traditional security measures, and can lead to credential theft, malware deployment, and persistent access. #Kimsuky #Quishing…

An ongoing internet blackout in Iran has severely limited communication during nationwide unrest triggered by economic collapse and political rebellion. Efforts to restore connectivity include potential cyber and physical alternatives, with international concern over human rights violations. #IranBlackout #Starlink #Cyberattacks #IranProtests…

Cisco Talos has exposed UAT-7290, a Chinese-nexus threat actor focusing on critical infrastructure, especially telecom networks in South Asia and Southeastern Europe. This group builds long-term attack infrastructure and acts both as spies and facilitators for other hacker groups. #UAT-7290 #ChinaNexus #CriticalInfrastructure #SoutheasternEurope…

A ransomware attack targeted the University of Hawaiʻi Cancer Center, exposing sensitive participant data without timely notification. The university’s response and transparency remain limited, raising concerns about cybersecurity protocols and law compliance. #HITechHui #FBI #Cyberattack…
California authorities have fined Datamasters for selling health and personal data without proper registration, highlighting enforcement under the California Delete Act. The company faced penalties and operational restrictions after reselling sensitive information of millions, including data related to medical conditions, age, race, and political views. #Datamasters #CaliforniaDeleteAct
Instagram fixed a bug that allowed mass password reset requests and clarified that no security breach occurred despite data being leaked online. The leaked information, which includes personal details of over 17 million accounts, is likely compiled from previous scraping incidents and does not contain passwords. #InstagramAPI #DataLeak

MuddyWater APT group has shifted from scripting tools to a new Rust-based malware called “RustyWater” to evade detection and target critical sectors in the Middle East. This sophisticated attack involves spearphishing campaigns using malicious Word documents to deploy resilient, modular implants. #MuddyWater #RustyWater…
Microsoft will retire the “Send to Kindle” feature in Microsoft Word after February 2026, encouraging users to send documents via the dedicated website instead. This change will remove the ability to send Word files directly from Word’s export menu while maintaining formatting but losing comments and tracked changes. #SendToKindle #MicrosoftWord #KindleIntegration
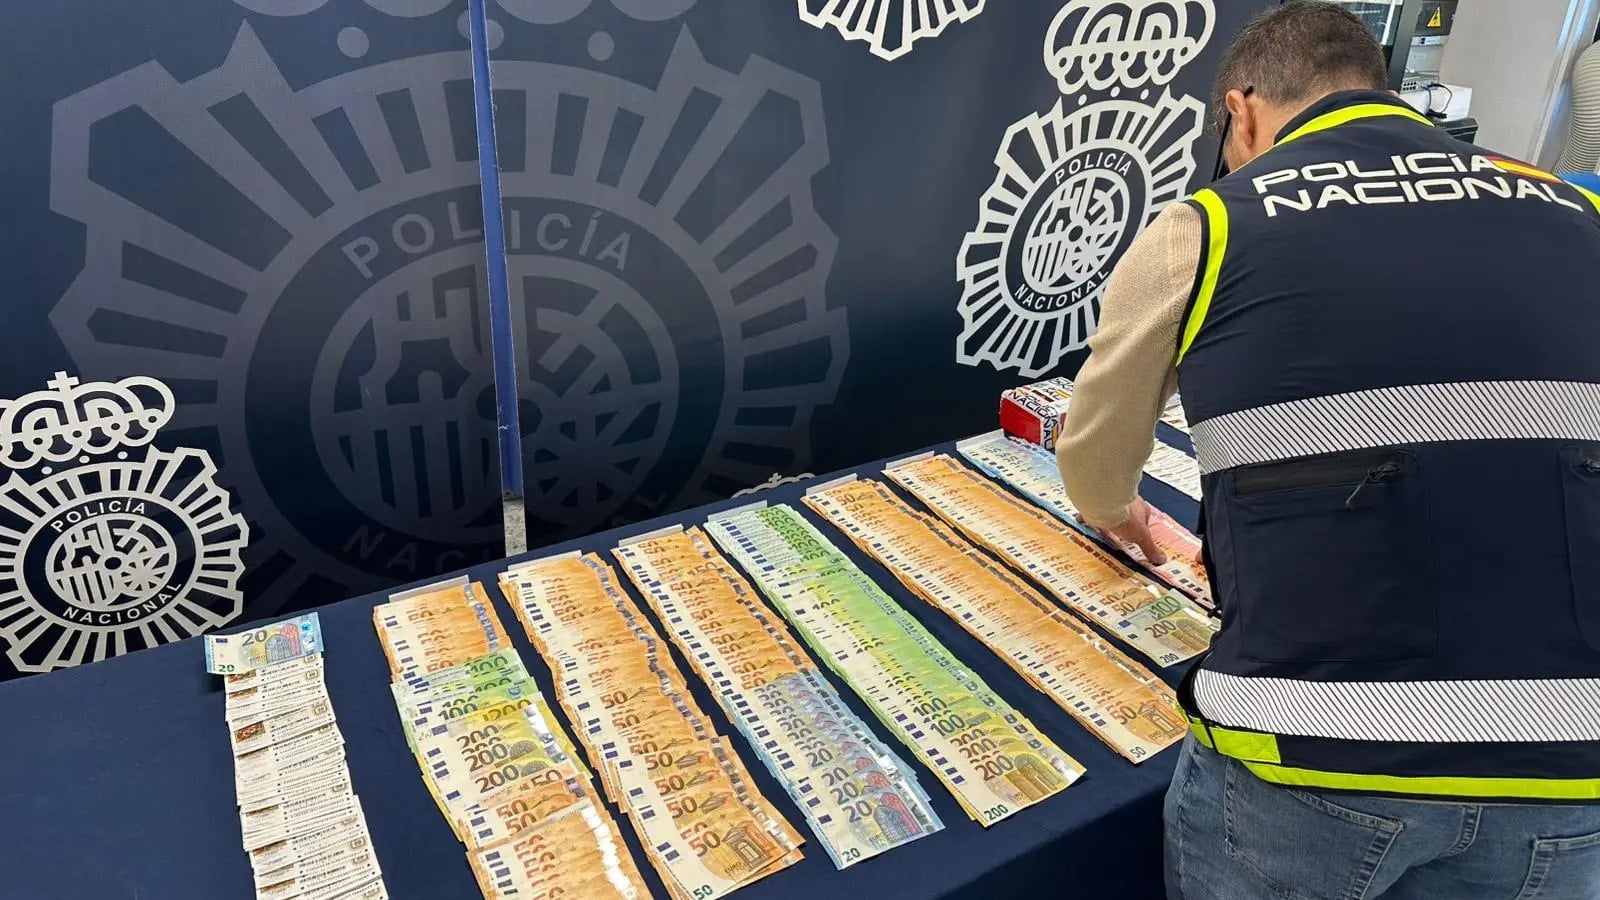
Authorities in Spain have dismantled a cyber fraud network linked to the notorious Black Axe group, arresting 34 suspects involved in man-in-the-middle scams such as Business Email Compromise. The operation uncovered extensive money laundering activities and highlighted the global reach of Black Axe’s cybercrime operations. #BlackAxe #BusinessEmailCompromise
The recent breach of BreachForums resulted in the leak of its user database, which could pose risks to affected users and law enforcement investigations. Despite claims of a temporary, single exposure, sensitive data such as member IP addresses and PGP keys have been leaked. #BreachForums #ShinyHunters