
Ukraine undergoes a significant government reshuffle, including the removal of key security officials amidst ongoing tensions with Russia. Highlights include changes in Ukraine’s intelligence and defense leadership, reflecting strategic shifts in its national security approach. #SBU #BlackSeaOperations…
Category: Cyber Security News

A Tennessee man is expected to plead guilty to a misdemeanor for hacking into the federal Supreme Court’s electronic case filing system. The case highlights ongoing cybersecurity challenges faced by the federal judicial system and recent data breaches involving cyberattacks from sophisticated hackers. #SupremeCourtHacking #PACER #Cyberattacks…
The United States led a UN effort to combat North Korea’s cyber activities, including IT worker schemes and cryptocurrency thefts funded by several countries. The report highlights international cooperation issues and North Korea’s ongoing efforts to bypass sanctions for nuclear and weapons programs. #NorthKorea #CryptoTheft #UNSanctions #CyberEspionage…
Microsoft’s latest Patch Tuesday for 2026 fixes 112 vulnerabilities, including an actively exploited zero-day, CVE-2026-20805, in Windows. Threat actors have likely exploited this flaw to achieve remote code execution, emphasizing the importance of timely patches. #CVE-2026-20805 #WindowsZeroDay…

Adobe released security updates for 11 products in January 2026, fixing 25 vulnerabilities including a critical XML External Entity (XXE) injection flaw in Apache Tika modules used by ColdFusion. These patches help prevent exploits like information leaks, SSRF, DoS, and remote code execution, but Adobe reports no known active attacks. #ApacheTika…

CrowdStrike plans to acquire Seraphic Security for approximately $420 million to enhance browser security and zero-trust protections. This move will integrate Seraphic’s browser-native security with CrowdStrike’s Falcon platform and SGNL’s identity security, offering comprehensive protection from endpoint to cloud. #SeraphicSecurity #FalconPlatform…
This article highlights the importance of DNS security as a key component of internet infrastructure, emphasizing the risks posed by various DNS attacks. It discusses the types of attacks, their impacts, and strategies for prevention, especially in cloud environments. #DNSHijacking #DNSThreats…
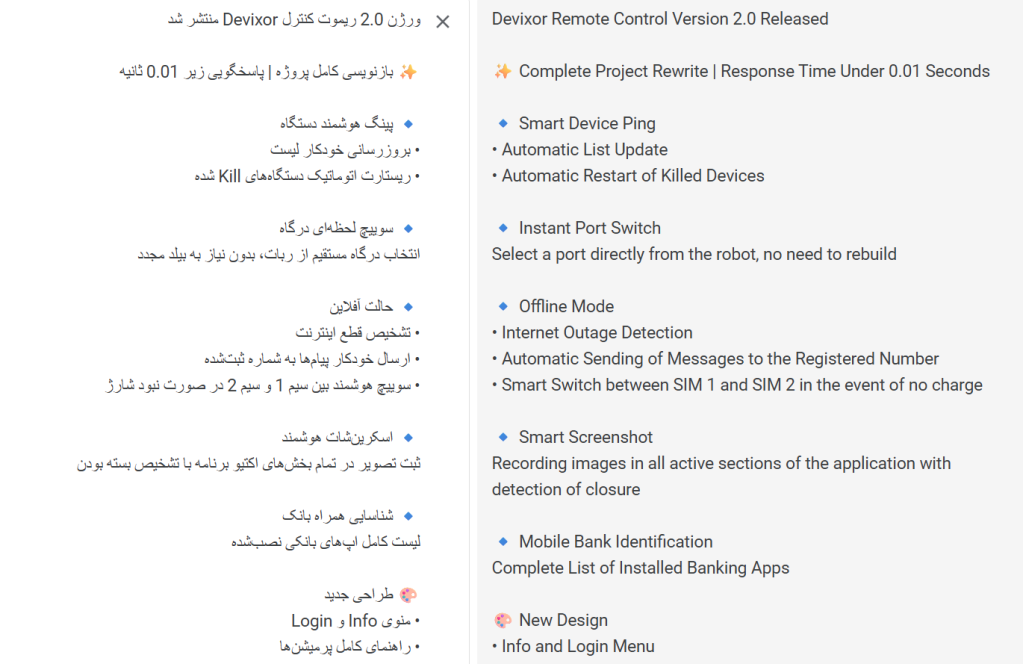
A new Android banking malware called deVixor combines traditional credential theft with advanced ransomware capabilities, targeting Iranian users initially. This malware operates as a scalable, service-driven platform using Telegram and Firebase for control and updates, indicating ongoing criminal activity. #deVixor #AndroidRansomware…

Authorities in Spain have arrested 34 members of the Black Axe organization, disrupting their extensive criminal network involved in scams, money laundering, and vehicle trafficking. The operation highlighted the group’s hierarchical structure and diverse criminal activities, with ongoing arrests and investigations. #BlackAxe #BusinessEmailCompromise…

Meta fixed a vulnerability in Instagram’s password reset process that allowed third parties to request reset emails, but denied any system breach. Recent data leaks, including a database for sale on cybercrime forums, pose serious privacy and safety risks, with affected data potentially circulating on the dark web. #InstagramPasswordReset #DarkWebLeak…

Daily Recap, State-linked APTs are in the spotlight as Kimsuky conducts quishing campaigns, UAT-7290 targets telecoms across South Asia and Europe, and MuddyWater shifts to stealthy Rust implants dubbed ‘RustyWater’. In data and privacy, breaches touch the Hawaii Cancer Center and Instagram, California bans health-data resales, Iran endures a long internet outage, and Microsoft retires the Send to Kindle feature in Word. #Kimsuky #RustyWater
Internal sources confirm that a breach involving Target’s source code and internal systems has occurred, with evidence suggesting that real systems and proprietary data were leaked online. The incident has prompted security measures including an “accelerated” access restriction to Target’s internal Git server. #TargetDataLeak #InsiderThreats

Despite advancements in technology, attackers are still leveraging traditional methods like supply chain exploitation and phishing, but more efficiently using AI automation. Defenders are urged to focus on fixing fundamental security issues such as permissions, supply chain verification, and authentication to effectively combat modern threats. #SupplyChainAttacks #Phishing #Attackers…

Cybersecurity researchers have uncovered VoidLink, a sophisticated malware framework targeting Linux-based cloud environments for long-term stealthy access. The malware’s modular and adaptive design, linked to Chinese threat actors, demonstrates a focus on cloud services like AWS, Azure, and Google Cloud. #VoidLink #CloudThreats…

AI agents are evolving from writing code to executing entire workflows, which can significantly speed up development but also introduce new security risks. The article emphasizes the importance of securing Machine Control Protocols (MCPs) to prevent malicious activities and highlights the dangers of compromised MCPs and shadow API keys. #AgenticAI #MCP…