Recent cybersecurity research reveals a vulnerable point in natural language interfaces like Google Gemini, which can be exploited via indirect prompt injection in Google Calendar. Attackers can bypass privacy controls and covertly exfiltrate sensitive data without traditional hacking methods. #GoogleGemini #PromptInjection…
Category: Cyber Security News
A critical zero-day vulnerability in Cloudflare’s WAF allowed attackers to bypass security protections and access origin servers directly by exploiting a flaw in handling ACME certificate validation traffic. Cloudflare addressed the issue by updating its logic to restrict WAF disabling to valid challenge tokens only. #Cloudflare #ACMEChallenge…
Ingram Micro suffered a ransomware attack in July 2025 that exposed personal and employment data of over 42,000 employees. The incident was claimed by the group SafePay, which demanded ransom and threatened data publication, affecting the company’s operations and customer trust. #SafePay #IngramMicro #DataBreach…

A Telegram-based illicit marketplace, Tudou Guarantee, is ceasing its major operations after processing over $12 billion in transactions, marking a significant shift in the cyber fraud landscape. Despite this, other marketplaces like HuiOne Guarantee and Xinbi Guarantee continue to operate, indicating a persistent threat environment. #TudouGuarantee #HuiOneGuarantee #XinbiGuarantee #PrinceGroup #PigButchering…
The UK’s NCSC issues a warning about persistent threats from Russian-aligned hacktivist groups such as NoName057(16), which conduct DDoS attacks mainly targeting government and local entities. These ideologically driven attackers aim to disrupt operations and damage reputations, emphasizing the need for organizations to enhance resilience and scalability. #NoName057(16) #DDoSia…

A vulnerability in Google’s AI assistant Gemini allowed attackers to leak private meeting details through malicious Calendar events, exploited via prompt injection. Google has acknowledged and fixed the security flaw. #GoogleGemini #CalendarVulnerability…
A new malware strain called PDFSider is being used by ransomware threat actors to gain long-term access to a Fortune 100 finance company’s Windows systems. The malware employs sophisticated techniques like DLL side-loading and encrypted communication, highlighting advanced cyberattack capabilities. #PDFSider #QilinRansomware
A malicious campaign utilizing the NexShield extension crashes browsers and delivers ModeloRAT malware, targeting corporate and individual users. Researchers link the attack to the threat actor KongTuke, demonstrating evolving tactics to compromise enterprise networks. #KongTuke #ModeloRAT

Genians Security Center uncovers “Operation Poseidon,” an advanced campaign by the Konni APT group exploiting trusted ad infrastructure to deliver malware. This tactic emphasizes the evolving sophistication of nation-state cyber threats targeting South Korean sectors. #Konni #OperationPoseidon…

A new cyber espionage campaign targeting Afghanistan’s government has been discovered, involving social engineering and the use of fake official documents. The threat group, Nomad Leopard, demonstrates operational errors and low-to-moderate sophistication but still poses regional risks. #NomadLeopard #APTGroup…
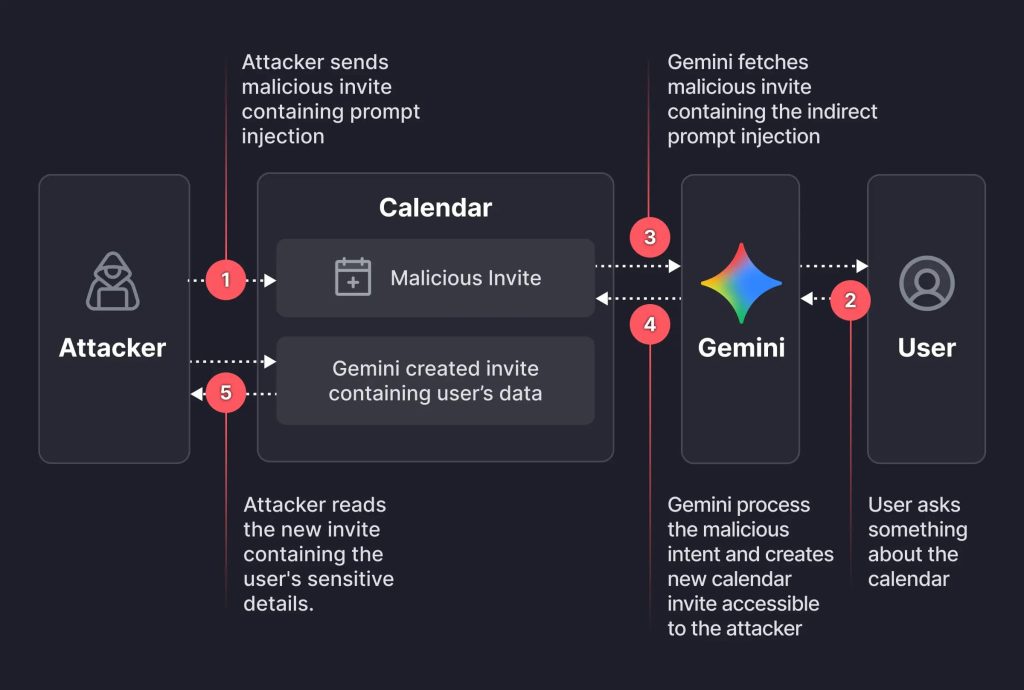
A recent discovery reveals that AI assistants like Google Gemini can be exploited through hidden commands in simple meeting invites, leading to data theft without user interaction. This highlights the emerging threat of indirect prompt injection attacks that manipulate AI reasoning by hiding malicious instructions in plain sight. #GoogleGemini #IndirectPromptInjection…
The U.K. government warns of ongoing DDoS attacks linked to Russian-aligned hacktivist groups targeting critical infrastructure and government services. Despite law enforcement disruptions, these hackers remain active, posing significant operational threats. #NoName057(16) #OperationEastwood

Cybersecurity researchers have uncovered a vulnerability in Google Gemini that uses indirect prompt injection to bypass privacy controls and extract private calendar data. This highlights the growing security risks associated with AI-enabled features and their potential for misuse. #GoogleGemini #PromptInjection…
A ransomware attack on Ingram Micro in July 2025 led to a significant data breach affecting over 42,000 individuals, including personal and employment information. The SafePay ransomware group claimed responsibility, exposing sensitive data and causing a major system outage. #SafePay #IngramMicro #DataBreach
A Jordanian man pleaded guilty to operating as an access broker, selling network access to over 50 companies for fraudulent purposes. This case highlights the role of initial access brokers in facilitating cyberattacks and the ongoing threats to corporate networks. #AccessBroker #InitialAccess #CyberCrime