
Google-owned Mandiant reported an expansion in extortion-style attacks tied to ShinyHunters that use vishing and fake credential-harvesting sites to steal SSO credentials and MFA codes. The attackers — tracked as UNC6661, UNC6671, and UNC6240 — are targeting cloud SaaS platforms (including Okta, SharePoint, and OneDrive) to exfiltrate sensitive data and extort…
Category: Cyber Security News

A Farsi-speaking threat actor aligned with Iranian state interests has been linked to RedKitten, a campaign that uses Farsi-named XLSM spreadsheets with malicious VBA macros to drop a C# implant via AppDomainManager injection and deploy the SloppyMIO backdoor. SloppyMIO retrieves steganographic configuration from GitHub and Google Drive, uses the Telegram Bot…

Hackers compromised an official eScan update server and pushed malicious updates that deployed multi-stage malware, including a “Reload.exe” payload that modified the HOSTS file, blocked automatic updates, and established persistence via scheduled tasks. eScan isolated the affected servers and released a manual cleanup utility after Morphisec reported the incident, but the…
Microsoft released an optional preview cumulative update, KB5074105, for Windows 11 that delivers 32 fixes addressing sign-in, boot, activation, and other quality issues. The non-security January preview lets admins test fixes and features—such as Cross‑Device Resume and expanded Windows Hello ESS support—before they arrive in next month’s Patch Tuesday. #KB5074105 #Windows11
Microsoft has released a fix for a December update that prevented Microsoft 365 customers from opening emails encrypted with “Encrypt Only” in classic Outlook, which caused affected users to see a message_v2.rpmsg attachment instead of readable content. The patch is available to Beta Channel customers now and will roll out to Current Channel and Current Channel Preview in February, with temporary workarounds including using the Encrypt option under the Options ribbon or reverting to a non-affected build via the officec2rclient.exe update command. #Microsoft #ClassicOutlook
Italian-led law enforcement, supported by Europol, Eurojust and Interpol, seized three industrial-scale illegal IPTV services and dismantled associated infrastructure across 14 countries, identifying 31 suspects and impacting hundreds of thousands of subscribers. The operation, which targeted services retransmitting content from Sky, DAZN, Mediaset, Amazon Prime, Netflix, Paramount and Disney+, coincided with heightened protections for the upcoming Milan Winter Olympics. #IPTVItalia #DarkTV
Microsoft will disable network NTLM authentication by default in upcoming Windows Server and client releases due to long-standing vulnerabilities that enable NTLM relay and pass-the-hash attacks. A three-phase rollout will add enhanced auditing, introduce IAKerb and a Local KDC to reduce NTLM fallback, and ultimately block network NTLM while allowing admins to re-enable it via policy. #NTLM #Kerberos
Illegal cryptocurrency flows reached a record $158 billion in 2025, a 145% increase from 2024 despite the illicit share of on-chain volume dipping slightly to 1.2%. TRM Labs attributes the surge to sanctions-linked activity tied to Russia-associated networks (notably A7 and the A7A5 stablecoin), expanded nation-state use, major hacks including the Bybit breach, and growing scam and laundering sophistication. #Bybit #A7A5
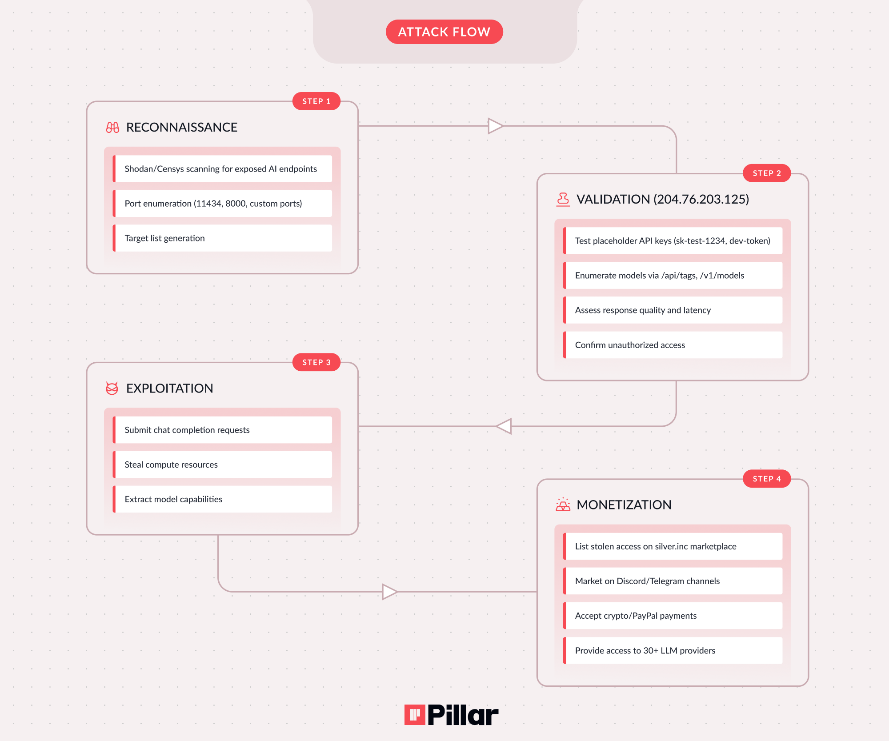
Researchers uncovered Operation Bizarre Bazaar, a December 2025–January 2026 campaign that recorded about 35,000 attack sessions where hackers broke into company AI systems to steal and resell access. Pillar Security Research traced the operation to an individual known as Hecker (aka Sakuya/LiveGamer101) and found stolen access sold via silver.inc at steep…
ShinyHunters claims to have stolen over 10 million records from Match Group, including user data tied to Hinge, Match.com, and OkCupid as well as hundreds of internal documents allegedly exposed via AppsFlyer. Match Group says it has terminated unauthorized access and is investigating with external experts, believes a limited amount of…
Dating app companies Bumble and Match Group reported cybersecurity incidents after the ShinyHunters group claimed to have leaked internal documents and millions of user records. Both firms say access was limited and contained, with Match notifying affected customers and Bumble confirming no impact to member accounts or private messages. #ShinyHunters #MatchGroup…

Coupang CEO Harold Rogers was questioned by Seoul police investigating whether the e-commerce company destroyed or hid evidence related to a November data breach. The breach affected 33.7 million customer accounts, prompted a police task force and probes of a former employee and a recovered smashed laptop, and Rogers said the…

The U.S. federal government seized three U.S.-registered internet domains—zamunda.net, arenabg.com and zelka.org—that operated in Bulgaria and allegedly distributed thousands of copyrighted TV shows, movies, video games and other works illegally. The domains drew tens of millions of mainly Bulgarian visitors annually, caused millions of illegal downloads worth millions of dollars in…

SecurityWeek’s weekly roundup condenses noteworthy but smaller cybersecurity stories into a single briefing covering acquisitions, legal settlements, threat disruptions, policy updates, and technical guidance. This week’s highlights include Mitsubishi Electric’s acquisition of Nozomi Networks, a fresh phishing wave targeting LastPass users, CISA’s RSA withdrawal and post-quantum cryptography guidance, the alleged upload…
A December 2025 campaign compromised at least 30 Polish wind and solar farms by exploiting default credentials, lack of multi‑factor authentication, and outdated or misconfigured OT and network devices. CERT Polska attributed the incident to Static Tundra while noting DynoWiper similarities to Sandworm-linked wipers, and reported attackers abused exposed FortiGate VPNs,…