
The AISURU/Kimwolf botnet launched a record-setting hyper-volumetric HTTP DDoS attack in November 2025 that peaked at 31.4 Tbps for 35 seconds and later ran the “The Night Before Christmas” campaign with wins up to 24 Tbps and 9 Bpps. Cloudflare and Google disrupted the supporting IPIDEA residential proxy infrastructure that had…
Category: Cyber Security News

Anthropic’s Claude Opus 4.6 discovered over 500 previously unknown high-severity vulnerabilities in open-source projects including Ghostscript, OpenSC, and CGIF. Anthropic validated the findings, coordinated patches with maintainers, and says the model can help defenders while it implements additional safeguards to limit misuse. #Anthropic #ClaudeOpus4_6 #Ghostscript #OpenSC #CGIF…
Zscaler has acquired browser security firm SquareX to integrate its Browser Detection and Response (BDR) technology into Zscaler’s Zero Trust platform. The move lets organizations secure users in standard browsers on managed and unmanaged devices without deploying a separate enterprise browser or full agent. #Zscaler #SquareX…
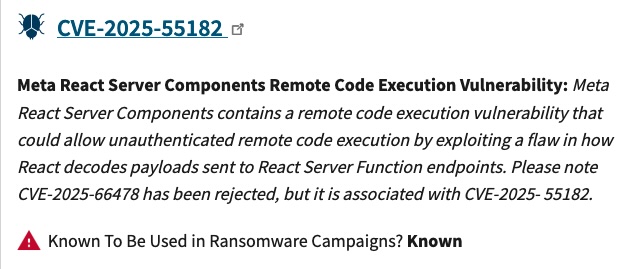
CISA has been updating its Known Exploited Vulnerabilities (KEV) catalog to mark flaws observed in ransomware campaigns, but those changes are made silently without public alerts, which can leave defenders unaware of shifting priorities. GreyNoise found CISA flipped the ransomware flag from ‘unknown’ to ‘known’ on 59 CVEs in 2025 and…
The growing threat from End-of-Support edge devices has become a national cybersecurity liability as threat actors exploit outdated firewalls, routers, VPN gateways, and other perimeter appliances to gain access and pivot into federal networks. The Binding Operational Directive BOD 26-02 mandates time‑bound inventory, decommissioning, replacement, and continuous discovery to eliminate these…
Ransomware operators are abusing virtual machines provisioned via ISPsystem’s VMmanager to host and deliver malicious payloads at scale, hiding C2 and distribution servers among legitimate infrastructure. Sophos found identical default Windows hostnames reused across multiple criminal campaigns — including WantToCry, LockBit, Qilin, Conti, BlackCat/ALPHV, and Ursnif — enabling evasion and complicating takedowns. #WantToCry #VMmanager
Spain’s Ministerio de Ciencia partially closed its electronic headquarters after a “technical incident” that a threat actor claims was a cyberattack and has published samples of allegedly stolen data. The attacker, using the alias “GordonFreeman,” says they exploited an IDOR vulnerability to gain admin-level access and is offering the data for sale. #MinisterioDeCiencia #GordonFreeman

Write 2 sentences summarizing the content. At the end, add hashtags for specific keywords mentioned in the article—such as names of malware, threat actors, or affected organizations/systems. Avoid general terms like #malware, #ransomware, or #cybersecurity. Use this format: #Keyword1 #Keyword2…
Researchers tracked a concentrated 72-hour APT28 spearphishing campaign that exploited the newly disclosed Microsoft Office vulnerability CVE-2026-21509 to compromise government and public-sector targets across Eastern Europe and beyond. The campaign delivered malicious Office documents that auto-executed, deploying MiniDoor, PixyNetLoader and a Covenant backdoor while abusing Filen cloud storage for command-and-control. #APT28…
CISA has ordered federal civilian agencies to remove end-of-life hardware and software from networks within 12 months after warning that unsupported edge devices are being widely exploited by sophisticated threat actors. Agencies must inventory listed devices within three months, decommission them within a year, implement continuous discovery within two years, and…

A routine business call turned into a macOS compromise after North Korean state-sponsored hackers lured a cryptocurrency-sector professional from messaging apps into a Microsoft Teams meeting and tricked them into running terminal commands under the pretense of fixing audio. Daylight Security links the campaign to BlueNoroff’s GhostCall operation, which installs a…

Lotus Blossom has resurfaced with a sophisticated supply chain attack against the Notepad++ infrastructure and deployed a new custom backdoor called Chrysalis to spy on targets in Southeast Asia and Central America. The campaign uses a Warbird-protected loader, DLL side‑loading, commodity tools like Cobalt Strike, and undocumented system calls to evade…
Cloud migrations often create visibility blind spots, and network-layer telemetry combined with Network Detection and Response (NDR) provides consistent, provider-agnostic visibility for detecting threats in multi- and hybrid-cloud environments. The article recommends enabling flow logs and traffic mirroring, standardizing and enriching telemetry with cloud inventory, and tuning baselines to detect threats such as coinminer beaconing, stolen credentials, and suspicious interactive admin activity. #Corelight #Kubernetes
Conpet, Romania’s national oil pipeline operator, disclosed a cyberattack that disrupted its corporate IT systems and took down its website while operational systems remained functional. The Qilin ransomware gang claimed responsibility, alleging nearly 1TB of stolen data and posting leaked documents, and authorities including national cybersecurity bodies and DIICOT are investigating. #Conpet #Qilin
Sapienza University of Rome has suffered a cyberattack that disrupted its IT systems, forcing a precautionary network shutdown and taking its website offline. Italian reports link the incident to ransomware activity attributed to a pro‑Russian actor called Femwar02 and a Rorschach/Bablock‑style strain, while national cybersecurity teams work to restore systems from backups. #SapienzaUniversity #Femwar02