
Bearlyfy, a pro‑Ukrainian hacker group, has carried out more than 70 attacks on Russian companies since January 2025 and escalated from low‑skill, small‑ransom operations to demanding hundreds of thousands of dollars while seeking both political damage and financial gain. Researchers say the group has developed and begun deploying its own Windows…
Category: Cyber Security News

A senior U.S. official accused the Chinese government of implicitly backing Chinese criminal syndicates that run large scam compounds across Southeast Asia and of commingling scam proceeds with state-linked projects. The testimony highlighted ties to developments like Yatai New City and warned that China’s selective crackdowns have driven these operations to…
An Armenian national, Hambardzum Minasyan, appeared in a U.S. federal court after prosecutors accused him of being a leading developer and administrator of the RedLine infostealer and he faces up to 30 years in prison following extradition and indictment on multiple conspiracy charges. Prosecutors say he maintained RedLine’s infrastructure, ran domains…

A China-linked state-sponsored actor has implanted kernel-level BPFdoor backdoors and passive implants deep within global telecommunications backbone infrastructure to maintain long-term, stealthy access for high-level espionage. Rapid7 found these sleeper tools working alongside CrossC2, TinyShell, credential harvesters, and brute-forcing utilities, with initial access abusing public-facing apps and vendor appliances such as…
AFC Ajax disclosed that a hacker exploited vulnerabilities in its IT systems, viewing email addresses of a few hundred people and personal details for fewer than 20 individuals with stadium bans. RTL journalists verified the flaws and demonstrated they could transfer VIP and season tickets, modify stadium ban records, and access broad fan data via exposed APIs and shared keys. #AFCAjax #RTL
Threat actors are targeting TikTok for Business accounts with a phishing campaign that uses Cloudflare Turnstile checks and Google Storage-hosted pages to evade security bots. Attackers use NiceNIC-registered domains and reverse-proxy fake login pages to capture credentials and session cookies, enabling account takeover even when 2FA is active. #TikTokForBusiness #PushSecurity
CISA warns that CVE-2026-33017, a critical code injection vulnerability in the Langflow AI-agent framework, is being actively exploited for unauthenticated remote code execution that can build public flows. Endor Labs observed exploitation beginning about 20 hours after disclosure with rapid scanning, Python-based attacks, and data harvesting; agencies are urged to upgrade to Langflow 1.9.0 or disable the vulnerable endpoint. #CVE-2026-33017 #Langflow
The U.K.’s FCDO has sanctioned Xinbi, a Telegram-based marketplace that sells stolen data and satellite internet equipment and provides cryptocurrency services used to support scam centres and launder proceeds. The action also targets the Cambodia-linked ‘#8 Park’ compound and its operator Legend Innovation Co to disrupt large-scale investment and romance scam operations tied to the Prince Group and illicit crypto flows. #Xinbi #8Park #PrinceGroup #LegendInnovationCo #Chainalysis #ByexExchange #ChenZhi
Internet Systems Consortium released BIND 9 updates to fix four vulnerabilities, including two high-severity flaws that can cause memory leaks or high CPU usage in resolvers during DNSSEC processing. Patches are available for BIND 9.18.47, 9.20.21, and 9.21.20, and ISC reports no known in-the-wild exploitation. #BIND #CVE-2026-3104…

Hightower Holding disclosed that a January 8–9, 2026 cyberattack led to the exfiltration of files containing names, Social Security numbers, and driver’s license numbers for 131,483 people. The company says the breach resulted from compromised user credentials, is offering 12 months of free identity theft and credit monitoring, and has not…
Node.js released security updates across its 20.x, 22.x, 24.x, and 25.x release lines to address multiple high-, medium-, and low-severity vulnerabilities and updated dependencies like undici. A notable issue is an incomplete fix for CVE-2026-21637 that left TLS SNICallback exception handling vulnerable to uncaught exceptions and potential remote DoS, alongside other…
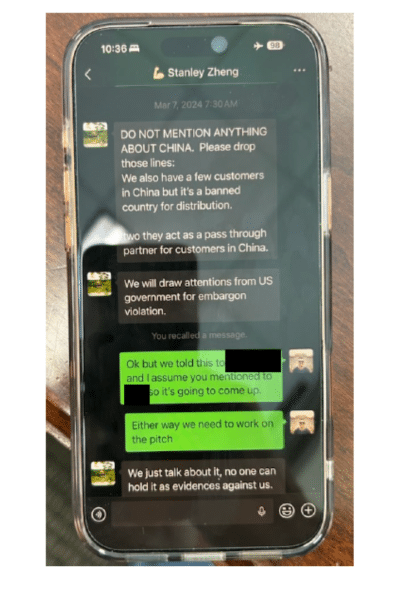
Federal prosecutors charged three men with allegedly conspiring to route export-controlled Nvidia A100 and H100 GPUs to China by placing a $170 million order for 750 servers through a Thailand-based front company. The scheme unraveled after the manufacturer flagged irregularities, a tipster alerted investigators, and seized communications and devices linked to…
The Nova Scotia Power data breach exposed sensitive information for more than 900,000 current and former customers, including driver’s license numbers and Social Insurance Numbers. The attack began with a SocGholish infection from a compromised website, followed by lateral movement, credential harvesting, data exfiltration and ransomware deployment before detection. #SocGholish #NovaScotiaPower…
Hambardzum Minasyan was extradited to the United States and charged with helping manage the RedLine infostealer operation by registering servers, domains, a cryptocurrency account, and file-sharing repositories used to distribute the malware and receive affiliate payments. International law enforcement actions, including the Dutch Operation Magnus seizure and U.S. charges against other suspects, underscore a coordinated effort to disrupt RedLine and pursue those responsible. #RedLine #HambardzumMinasyan
Russian police in the Rostov region arrested a Taganrog resident accused of owning and administering LeakBase, a major forum for buying and selling stolen data and hacking tools. The arrest was part of “Operation Leak,” an international action led by the FBI and Europol that seized the LeakBase domain and executed around 100 enforcement actions across multiple countries, with the forum’s data to be used as evidence. #LeakBase #FBI