Security researchers discovered a remote code execution vulnerability in Apache ActiveMQ Classic that went undetected for 13 years and can be exploited to run arbitrary system commands. Tracked as CVE-2026-34197 and found with the help of the Claude AI assistant, the flaw stems from Jolokia’s exposed addNetworkConnector enabling remote Spring XML loading. #ApacheActiveMQ #CVE-2026-34197
Category: Cyber Security News

Trellix analyzed Masjesu, an IoT botnet that infects a wide range of devices and is capable of launching high-volume DDoS attacks. The botnet spreads via router and IoT vulnerabilities, maintains persistence by masquerading as system components, and is controlled through multiple C&C domains and Telegram channels. #Masjesu #Trellix…
Signature Healthcare in Brockton, Massachusetts, diverted ambulances and activated incident response after a cyberattack that disrupted services including canceled chemotherapy infusions and temporary pharmacy closures. Surgeries were not impacted, but walk-in care remained open while the organization has not confirmed a ransomware claim and attackers’ motives remain unclear. #SignatureHealthcare #BrocktonHospital…
Russian-linked APT28 has been exploiting vulnerable SOHO routers, notably TP-Link devices, to carry out large-scale DNS hijacking and adversary-in-the-middle operations that intercept communications and harvest credentials. The U.S. Department of Justice and FBI executed a court-authorized disruption, Operation Masquerade, to neutralize the compromised router network and restore legitimate DNS settings while…

A cyberattack beginning April 6 disrupted Winona County’s critical systems and significantly impaired administrative and public-facing operations. Minnesota has activated the National Guard and coordinated with state and federal partners, including the FBI, to contain the incident and restore systems. #WinonaCounty #MinnesotaNationalGuard…
A critical remote code execution vulnerability in Flowise (CVE-2025-59528) is being actively exploited, allowing attackers to inject and execute arbitrary JavaScript via the CustomMCP mcpServerConfig setting. Users must upgrade to Flowise 3.1.1 (or at least 3.0.6) and remove unnecessary public exposure to prevent full system compromise. #Flowise #CVE-2025-59528…
Microsoft rolled back a server-side Bing update after it caused the Windows Start Menu search to show blank or broken results for some Windows 11 23H2 users. The company says the server-side fix is being gradually rolled out and will resolve automatically for connected devices with Web Search enabled. #Bing #Windows11

Proofpoint reports that TA416 has shifted its focus back to European government and diplomatic targets since mid-2025 and rapidly expanded operations into Middle Eastern diplomacy following the March 2026 Iran conflict. The group repeatedly adapts delivery chains—using web bugs, Cloudflare Turnstile abuse, OAuth redirect hijacking, and MSBuild/C# tooling—to deploy continually updated…
Iran-linked cyberattacks have disrupted multiple U.S. critical infrastructure sectors by targeting operational technology devices and internet-exposed PLCs. Federal agencies warn the activity manipulates HMI/SCADA project files and data, and they urge immediate review of IOCs and mitigations. #CyberAv3ngers #Handala…

A high-severity flaw in Docker Engine (CVE-2026-34040) allows attackers to bypass authorization plugins by sending a specially crafted, padded HTTP request that causes the daemon to forward requests without the body. The vulnerability — an incomplete fix for CVE-2024-41110 — can enable creation of privileged containers with host filesystem access and…

New research shows that despite maturing identity programs, hundreds of enterprise applications remain disconnected from centralized identity systems, creating an unmanaged “dark matter” attack surface. The rise of AI copilots and autonomous agents is amplifying credential risks by reusing stale tokens and navigating systems outside governance. #PonemonInstitute #ShadowAI…

Russia-linked APT28 (aka Forest Blizzard) conducted a campaign codenamed FrostArmada that compromised insecure MikroTik and TP‑Link SOHO routers to change DNS settings and hijack local network traffic for passive collection and AiTM credential theft. Active since May 2025 and peaking in December with communications from over 18,000 IPs across 120 countries,…
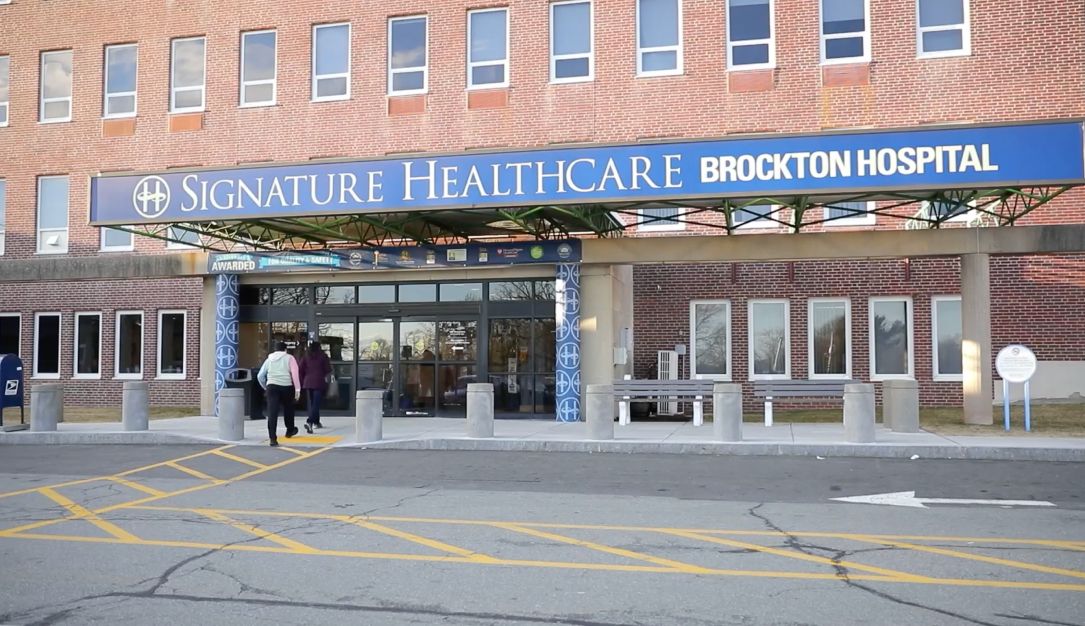
A cyberattack on Signature Healthcare and Signature Healthcare Brockton Hospital in Massachusetts forced ambulance diversions, activation of downtime procedures, and cancellations such as chemotherapy infusions while core emergency and inpatient services continue. Hospital officials are working with outside experts to investigate and restore systems, no group has claimed responsibility, and industry…
The FBI reports that U.S. victims lost nearly $21 billion to cyber-enabled crimes in 2025, driven mainly by investment scams, business email compromise, tech support fraud, and data breaches. IC3 complaints surpassed 1 million as losses rose 26% year-over-year, with emerging AI-related scams contributing $893 million in reported losses. #InvestmentScams #AIscams
A critical unauthenticated file upload vulnerability in the Ninja Forms File Uploads premium add-on (CVE-2026-0740) allows attackers to upload arbitrary files, including PHP, enabling remote code execution and full site takeover. Wordfence reports active exploitation with thousands of blocked attacks and urges users to upgrade to patched version 3.3.27 following disclosure by researcher Sélim Lanouar. #CVE20260740 #NinjaFormsFileUpload