The rise of SOHO router compromise campaigns, led by the Russia-linked threat actor Forest Blizzard, has turned poorly secured home and small-office devices into covert infrastructure for DNS hijacking and large-scale surveillance. By altering router DNS settings (often using dnsmasq) and conducting adversary-in-the-middle attacks against services like Outlook on the web…
Category: Cyber Security News
BleepingComputer will host a live webinar on April 30, 2026 exploring how threat actors leave observable signals across dark web forums, Telegram channels, and access broker marketplaces before launching attacks. Speakers from RansomLook and Flare Systems will explain how to identify meaningful chatter, track shifting attacker tactics, and turn external threat intelligence into prioritized defensive actions. #RansomLook #FlareSystems
Figure’s February 2026 breach exposed 967,200 email records, creating a large operational input that enables credential stuffing, AI-driven phishing, and help-desk social engineering without any exploited vulnerability. Legacy MFA is structurally insufficient against real-time relay (AiTM) attacks and MFA fatigue; true protection requires cryptographic origin binding, hardware-bound keys, and live biometric verification. #Figure #Evilginx
UNC6783 is targeting business process outsourcing (BPO) companies as a pathway to infiltrate major organizations, using phishing, social engineering, live-chat impersonation, and fake updates to steal sensitive data and deploy remote access malware. Google’s analysis and Mandiant recommendations emphasize measures such as FIDO2 hardware keys, live-chat monitoring, blocking Zendesk-like domains, and…
Bitcoin Depot, operator of over 25,000 Bitcoin ATMs, disclosed that attackers stole approximately 50.903 BTC (about $3.665 million) from company-controlled wallets after a March 23, 2026 breach. The company says the incident was contained to its corporate environment, engaged external cybersecurity experts and law enforcement, and warned its insurance may not fully cover resulting losses. #BitcoinDepot #ByteFederal
Attackers have been exploiting a zero-day in Adobe Reader via specially crafted PDFs since at least December, using a sophisticated fingerprinting-style exploit that runs on the latest Reader without user interaction. The exploit harvests local data using Acrobat APIs and can deploy follow-on RCE/SBX stages, so researchers advise not opening PDFs from untrusted sources until Adobe issues a patch. #AdobeReader #HaifeiLi
Eurail B.V. disclosed a December 2025 data breach that exposed the personal information of 308,777 travelers, including names, passport numbers, bank IBANs, health details, and contact information. Stolen data samples were posted on Telegram and offered for sale on the dark web, prompting customer notifications and advisory actions. #Eurail #ShinyHunters
European rail-pass operator Eurail disclosed that a December 2025 network breach resulted in stolen files from its AWS S3, Zendesk, and GitLab instances and that attackers published sample data on dark web channels. The company is notifying 308,777 customers about exposed identity details, including names and passport numbers. #Eurail #AWS_S3…

Researcher Haifei Li detected an actively exploited zero-day in Adobe Reader using his Expmon sandbox, identifying a malicious PDF that collects and exfiltrates system data and may enable sandbox escape and remote code execution. The exploit works against the latest Reader build, samples were submitted to Expmon and VirusTotal, and Adobe…
A financially motivated actor tracked as UNC6783 is targeting business process outsourcing firms and support staff to steal sensitive corporate data and extort high-value companies. GTIG links UNC6783 to a “Raccoon” persona that allegedly stole Adobe data from a BPO, and the actor lures staff with live chats to spoofed Okta…
The Bitcoin Depot disclosed that unauthorized actors accessed its internal systems and stole approximately 50.903 Bitcoin (about $3.665 million) by using compromised credentials tied to its digital asset settlement accounts. The company engaged external cybersecurity experts, notified law enforcement, says customer-facing systems show no evidence of compromise, and continues an active…
A cyberattack on Signature Healthcare, first detected April 6, 2026, disrupted critical systems at Signature Healthcare and Signature Healthcare Brockton Hospital, forcing downtime procedures, ambulance diversions, and outages that impacted laboratory testing, pharmacy services, and administrative operations. Chemotherapy infusions were temporarily canceled and later phased back in while surgeries and urgent…
Microsoft suspended developer accounts used to publish high-profile open-source projects, blocking maintainers from releasing Windows builds and security patches without prior notification or a quick reinstatement path. Affected projects include WireGuard, VeraCrypt, MemTest86, and Windscribe, and Microsoft says the suspensions were automatic for partners who missed mandatory Windows Hardware Program verification, a response that only accelerated after media attention. #WireGuard #VeraCrypt #MemTest86 #Windscribe #Microsoft
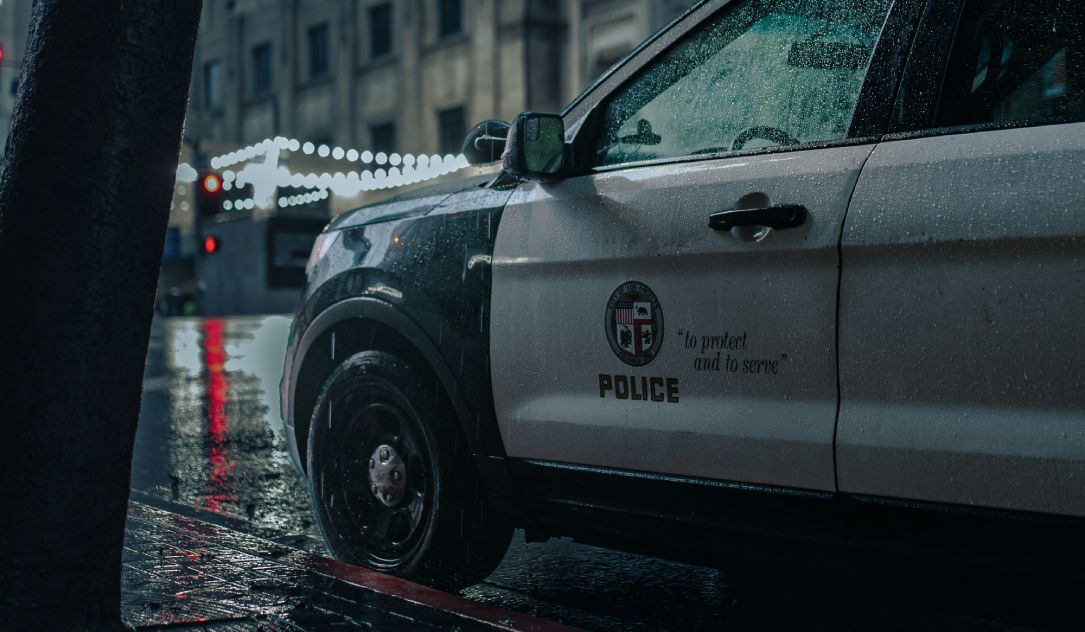
Hackers gained access to a Los Angeles City Attorney’s Office digital storage tool containing sensitive documents turned over in discovery from prior LAPD civil litigation. The LAPD says its systems were not breached and the City Attorney’s Office is working with law enforcement, forensic specialists, and the City’s ITA to investigate…
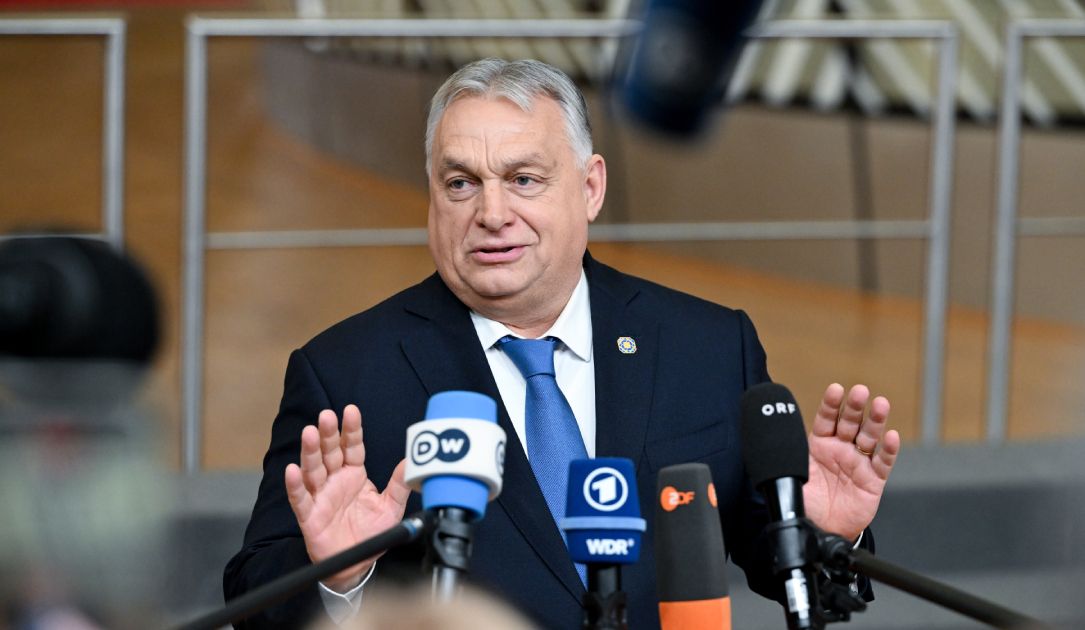
Days before Hungary’s parliamentary vote, TikTok said it removed covert networks, hundreds of impersonating accounts, and thousands of videos that used fake profiles to amplify political content aimed at Hungarian users. Investigations and fact-checkers described coordinated disinformation targeting both Péter Magyar and Viktor Orbán’s Fidesz amid disputed claims of foreign involvement…