The British government disclosed that Russian naval forces, including an attack submarine and vessels from the Main Directorate of Deep Sea Research (GUGI), were monitored conducting covert operations near critical undersea infrastructure north of the UK. UK authorities say the mission was tracked and disrupted by British and allied forces with…
Category: Cyber Security News
Nine vulnerabilities in the open-source DICOM server Orthanc (CVE-2026-5437 to CVE-2026-5445) can crash servers, leak sensitive data, and potentially enable remote code execution. CERT/CC and Machine Spirits advise updating affected Orthanc versions (1.12.10 and earlier) to 1.12.11, which fixes out-of-bounds reads, decompression-bomb and ZIP size abuses, unsafe HTTP header allocations, and…
The US government issued a joint advisory warning that Iran-linked hackers have targeted critical infrastructure by compromising industrial control systems and operational technology, with a focus on programmable logic controllers made by Rockwell Automation and other vendors. Attackers have abused legitimate engineering tools such as Rockwell’s Studio 5000 Logix Designer to…

Juniper Networks released patches for nearly three dozen vulnerabilities in Junos OS, Junos OS Evolved, vLWC, CTP OS, and Apstra that could enable privilege escalation, denial-of-service, or remote command execution. The most severe is CVE-2026-33784, a default high-privileged account password in the Support Insights vLWC, and Juniper says it is not…
This week’s roundup covers state-sponsored DNS hijacking campaigns, a $285 million exploit of Drift Protocol on Solana, regulatory uncertainty around EU CSAM detection, and findings that deleted Signal data can persist on iPhones. It also highlights the U.S. Treasury’s new Digital Asset Cybersecurity Initiative and a pattern of attackers combining infrastructure…

A threat actor built a working exploit for a critical unauthenticated RCE in Marimo (CVE-2026-39987) and began weaponizing it roughly nine hours after the bug’s public disclosure. The attacker used the unauthenticated terminal WebSocket endpoint to gain an interactive shell, quickly exfiltrated credential files and searched for SSH keys; users should…

MITRE Corporation has released the Fight Fraud Framework (MITRE F3), a behavior-based knowledge base that catalogs fraudsters’ tactics, techniques, and procedures to improve detection, prevention, and response. F3 adds fraud-specific tactics like positioning and monetization, aligns with and extends ATT&CK concepts, and is publicly available with visual maps and a GitHub…
Microsoft’s redesigned Recall protects stored captures inside VBS enclaves with AES-256-GCM, TPM-backed keys, Windows Hello, and PPL protections, but decrypted data is handed off to a less-protected process. TotalRecall Reloaded exploits that trust boundary by injecting a DLL into AIXHost.exe at user privilege to extract screenshots, OCR text, metadata, and indexed…
Escalation around Iran has exposed Gulf states to combined kinetic and cyber threats that endanger ports, energy facilities, desalination plants, and financial hubs. As a result, Gulf states—led by the UAE—are integrating cybersecurity into national defense and regional cooperation frameworks to protect critical infrastructure and economic continuity. #Iran #UAE…

Deleted Signal messages can sometimes be recovered from an iPhone because iOS stores notification previews in a system-level database rather than from Signal’s encrypted storage. FBI forensic extraction of lock-screen notification fragments yielded incoming message remnants used as evidence in the Prairieland ICE Detention Facility case. #Signal #PrairielandICE…

Unknown actors hijacked Nextend’s update infrastructure to push a trojanized Smart Slider 3 Pro v3.5.1.35 that delivered a multi-stage backdoor through the official update channel. The malicious build enabled pre-auth remote code execution, hidden admin creation, multi-location persistence, and credential exfiltration to a C2 domain before Nextend removed the update and…

DomainTools describes North Korea’s cyber program as a “mature portfolio model” that uses compartmentalized, parallel development pipelines to specialize missions and resist attribution. Three distinct tracks—Kimsuky for espionage, Lazarus Group for financial operations, and Andariel for disruptive attacks—operate independently with shared tooling and a loss‑tolerant posture. #LazarusGroup #Kimsuky…
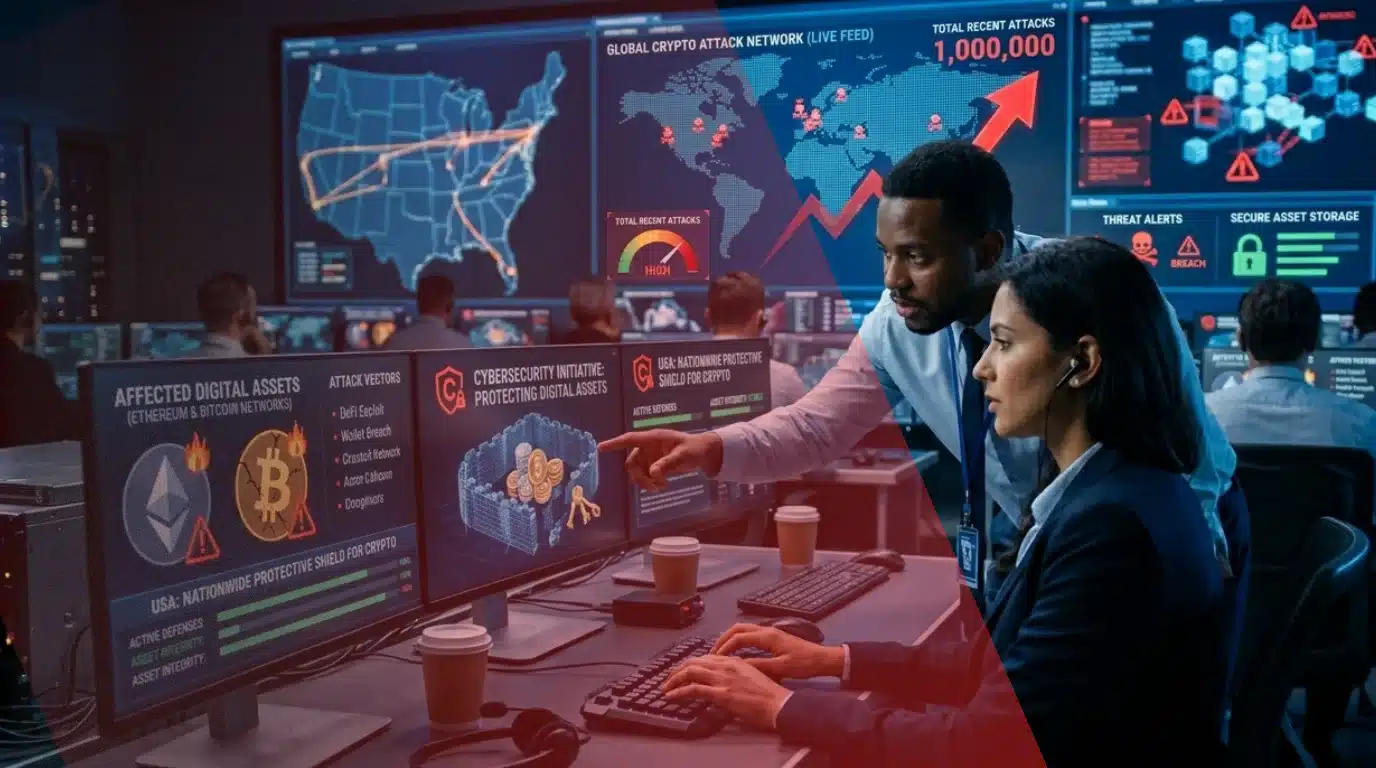
The U.S. Treasury’s OCCIP launched a digital asset cybersecurity initiative to provide eligible U.S.-based crypto firms with timely, actionable threat intelligence previously reserved for traditional financial institutions. The move responds to escalating attacks—including a reported $280 million theft from Drift and other multi-million-dollar breaches—and aims to strengthen industry-wide resilience through information…
GitLab has released critical security patches for Community and Enterprise editions to fix twelve vulnerabilities, including a high-severity websocket flaw tracked as CVE-2026-5173. Self-managed installations should upgrade immediately to patched versions 18.10.3, 18.9.5, or 18.8.9 to mitigate risks like unauthorized access, denial-of-service, and data exposure. #GitLab #CVE-2026-5173…
The FCC is proposing stricter Know-Your-Customer (KYC) rules for originating voice service providers to block illegal robocalls before they enter networks and protect consumers. The proposal would expand data collection, verification, monitoring, retention, and introduce per-call fines in response to enforcement gaps highlighted by cases involving Voxbeam and Axfone. #Voxbeam #Axfone…