Bitget says the $351.6 million theft from its systems closely matches techniques used by known North Korean threat actors, based on IP behavior and on-chain analysis. The company said the attackers abused a compromised backend system to approve fraudulent transfers, while hot wallets were affected and cold wallets were not. #Bitget…
Category: Cyber Security News

SecurityWeek’s weekly roundup covers major developments including the ShinyHunters defacement of Cl0p’s leak site, BragJack flaws in browser AI assistants, and malicious AI-related implants and botnets targeting secrets and credentials. It also highlights serious exposure across water utilities, industrial telemetry, Android banking apps, and Docker environments, alongside faster Ubuntu kernel response…

Daily Recap, Exploited critical flaws are driving active attacks across Roundcube, TeamCity, Check Point VPN, and WordPress, while SolarWinds and Adobe push urgent patches for RCE and other serious issues. In parallel, criminals target users and organizations with threats like RemControl, ClickFix infrastructure abuse, and AI-driven skimmers, alongside ongoing policy and security operations focus from CISA updates to new Windows 11 and Google AI compute changes. #Roundcube #TeamCity #CheckPoint #WordPress #SolarWinds #Adobe #RemControl #ClickFix #Terraform #MikroTik #AI #skimmers #AstranaHealth #GitLab #KB5124010 #FileHistory #agenticremediation #PrivateAICompute #IonQ #Ryuk #KarenVardanyan
Bitget said suspected North Korean hackers stole $351.6 million from its hot and warm wallets after unauthorized transfers were detected on Thursday evening. The exchange paused withdrawals, is investigating with law enforcement and security firms, and says its User Protection Fund will cover the losses. #Bitget #NorthKoreanHackers #Mandiant #SlowMist
Microsoft confirmed a known issue causing black screens and desktop loading problems after the August 2026 preview and later updates, mainly impacting Azure Virtual Desktop hosts using FSLogix. A temporary workaround is to manually launch explorer.exe, while enterprise customers can use Known Issue Rollback through specific Group Policy updates. #Microsoft #AzureVirtualDesktop #FSLogix #KB5120996 #KB5120998 #KB5124008 #KB5122880
A Kosovar national has pleaded guilty for helping run Rydox, a major illegal marketplace that sold stolen identities, login credentials, credit card details, and cybercrime tools. The operation was dismantled after an international law enforcement action that arrested administrators, seized infrastructure, and shut down the Rydox marketplace. #Rydox #ArditKutleshi #JetmirKutleshi #ShpendSokoli
Researchers at Graz University of Technology showed that file-change notifications in Linux, Android, Windows, and macOS can leak user activity such as typing rhythms, website visits, and app interactions. They also found serious impacts on Linux, Android, and Windows, including keystroke inference, WhatsApp file monitoring, and full path disclosure, with a…
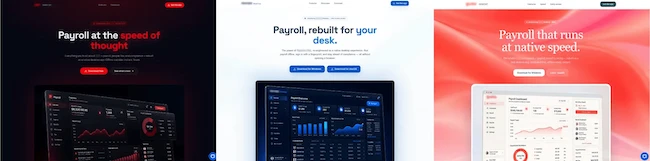
An attacker created fake desktop app pages for three major US payroll and HR platforms that do not offer desktop apps, then used them to install ScreenConnect for hidden remote access. The campaign used AI-generated lure pages, GitHub-hosted installers, and a single command-and-control server to potentially divert or drain payroll accounts. #ScreenConnect #Lovable #Vercel #GitHub

Docker has introduced Docker Cloud Sandboxes, a secure cloud-based environment for running AI agents and long-lived workflows without relying on a developer’s laptop or custom infrastructure. The release also adds next-generation Kits as standard OCI images, giving organizations a portable way to package agent logic, tools, and access controls with consistent policies across local and cloud execution. #Docker #DockerCloudSandboxes #OCI #CNCF
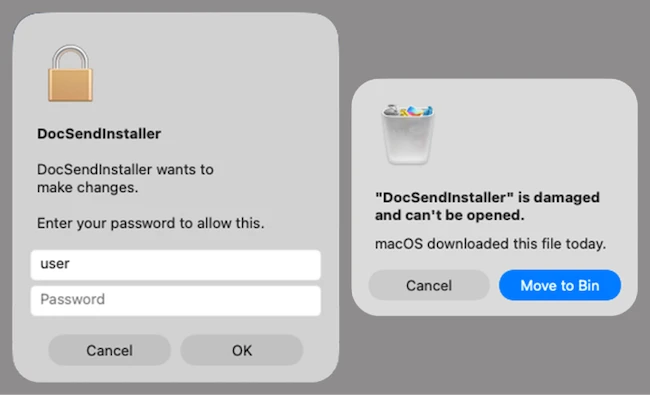
Kaspersky has uncovered a new MacSync variant that uses an infostealer and a persistent backdoor to steal credentials, crypto wallet data, files, and developer-related information from Mac users. The campaign spreads through a fake crypto wallet app called Toria and uses advanced infection chains, disguised prompts, and a backdoor posing as Finder to target developers and crypto enthusiasts. #MacSync #Kaspersky #Toria #Finder #Ledger #PAM #Keychain

CISA has added two critical vulnerabilities, CVE-2026-5430 in WSO2 products and CVE-2026-71362 in Adobe Commerce and Magento, to its Known Exploited Vulnerabilities catalog after evidence of active exploitation. The flaws can enable remote code execution or unauthorized access to sensitive customer data, and FCEB agencies must patch them by September 27,…

A flaw in Cloudflare Containers allowed one customer to read leftover data from disks previously used by other customers’ containers on the same server. Cloudflare says the issue has been fixed across Containers and Sandboxes, with no evidence that anyone else used the method. #Cloudflare #CloudflareContainers #CloudflareSandboxes #OrenYomtov #Accomplish…
Threat actors are exploiting a high-severity Roundcube flaw, tracked as CVE-2026-48842, which enables unauthenticated SQL injection through the virtuser_query plugin. Successful attacks can expose messages, address books, user identities, and other sensitive database content, prompting Roundcube to release fixes in versions 1.6.16 and 1.7.1. #Roundcube #CVE-2026-48842 #virtuser_query…

This roundup highlights new cybersecurity products focused on securing AI agents, strengthening exposure management, and improving incident response across enterprise and industrial environments. Vendors including Ping Identity, Akeyless, Orchid Security, Securin, Bitsight, Cohesity, and Nozomi Networks are adding controls to help organizations understand, validate, and govern emerging AI-driven and operational risks. #PingIdentity #Akeyless #OrchidSecurity #Securin #Bitsight #Cohesity #NozomiNetworks
A VikingCloud survey of 200 security and IT leaders found that attacks at multi-location retail and franchise chains often spread beyond the initial site, and that security tools or real-time visibility did not reduce that spread. The strongest factor was governance: companies with a corporate security mandate saw less lateral movement, while many incidents still never reached executive leadership. #VikingCloud #KevinPierce #franchisees