
Booking.com has notified some customers that an unauthorized third party may have accessed booking information such as names, email addresses, phone numbers, and details shared with accommodations. The company says customer accounts were not breached, no payment data was accessed, it has contained the issue and updated reservation PINs, but it…
Category: Cyber Security News

Unknown hackers breached the systems of European gym chain Basic-Fit and downloaded personal data for around 1 million members across Belgium, the Netherlands, Luxembourg, France, Spain and Germany. Basic-Fit said passwords and identity documents were not accessed, the intrusion was stopped within minutes, affected members were notified and the company reported…
The CPUID website was compromised and briefly served trojanized installers of CPU-Z, HWMonitor, HWMonitor Pro, and PerfMonitor that loaded a malicious cryptbase.dll via DLL sideloading. The campaign distributed the STX RAT to over 150 victims across individuals and multiple industries, with differing compromise windows reported and links to a broader 10-month…
An international law enforcement operation called Operation Atlantic targeted multimillion-dollar cryptocurrency theft schemes across the United States, the United Kingdom, and Canada, identifying over $45 million in stolen funds and freezing about $12 million for return to victims. The week-long effort disrupted approval phishing campaigns used in pig butchering scams, took…
OpenAI disclosed it was affected by the Axios NPM supply-chain attack in which compromised maintainer credentials were used to publish malicious packages that downloaded a cross-platform RAT. OpenAI halted affected notarizations and revoked and will rotate its macOS signing certificate as a precaution while investigators attribute the campaign to North Korean-linked…
Zimbabwe is stepping up cybersecurity measures as digital crime rises, with expanded internet access and mobile money use exposing systemic weaknesses. Officials warn cybercriminals now use advanced tools like deepfake voice cloning, automated phishing platforms, and adaptive malware, and the government is pursuing AI-driven defenses including the Zimbabwe AI Cyber Shield….

OpenAI disclosed that a GitHub Actions workflow used to sign its macOS apps downloaded a malicious Axios package (version 1.14.1) tied to a supply-chain compromise, but said no user data or internal systems were accessed. The company is revoking and rotating the signing certificate, blocking older macOS app versions after May…
Google has enabled end-to-end encryption (E2EE) in Gmail for enterprise users on Android and iOS, allowing users to read and compose encrypted messages natively within the mobile app. The feature uses client-side encryption (CSE) in Google Workspace and is available immediately for Enterprise Plus customers with the Assured Controls or Assured…
The ChipSoft ransomware incident on April 7 disrupted healthcare operations after the Dutch software vendor was hit, forcing hospitals to disconnect systems and trigger widespread precautionary shutdowns. Z-CERT is coordinating response and monitoring while ChipSoft works to restore platforms such as Zorgportaal and HiX Mobile, and affected hospitals have relied on…
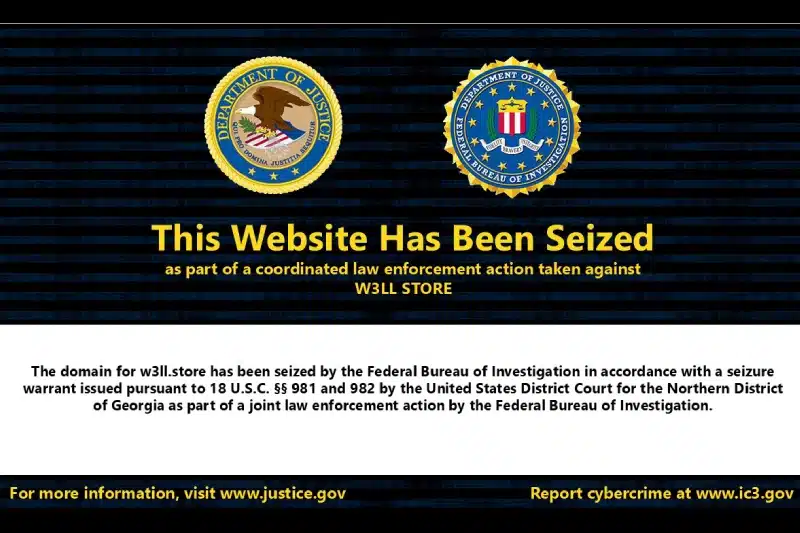
International law enforcement, led by the FBI Atlanta Field Office and Indonesian police, dismantled the W3LL phishing infrastructure that enabled credential theft and attempted fraud exceeding $20 million. The takedown targeted a phishing-as-a-service ecosystem including the W3LLSTORE marketplace and tools used to target corporate accounts such as Microsoft 365, and authorities…

Adobe has released emergency updates for Acrobat and Acrobat Reader to address a critical zero‑day vulnerability (CVE-2026-34621) that is being actively exploited in the wild. The flaw is a JavaScript prototype pollution issue that can lead to arbitrary code execution and affects multiple Acrobat DC and Acrobat 2024 builds disclosed by…

Unknown threat actors briefly compromised CPUID’s website (cpuid[.]com) and replaced download links for CPU-Z and HWMonitor with trojanized installers to serve malicious executables. The attack used a malicious CRYPTBASE.dll for DLL side‑loading and anti‑sandbox evasion to deploy STX RAT, affecting over 150 victims across multiple countries and industries. #STXRAT #CPUID…

Cybersecurity Threat Research ‘Weekly’ Recap.
This week highlighted a broad surge in supply‑chain and package ecosystem attacks, AI-themed lure campaigns around Claude and related tooling, evolving infostealer and RAT families (STX RAT, Lumma/Remus), trojanized installers and MaaS campaigns (ClickFix, CastleLoader), ransomware operations (Storm1175/Medusa, NightSpire) and pervasive vulnerability disclosures, with notable data exfiltration tied to TeamPCP and a focus on defense exercises and immutable backups.
#TeamPCP #Axios #STXRAT #Remus #Lumma #CastleLoader #ClipBanker #HWMonitor #ScreenConnect #Storm1175 #Medusa #NightSpire #BeastRansomware #Sinobi #EvilTokens #Graphalgo #ForestBlizzard #APT35 #DPRK #Handala #MOIS #OpenClaw #Marimo #Kubernetes #FortiGate
Attackers began exploiting a critical remote code execution vulnerability in the Marimo open-source Python notebook platform within 10 hours of its public disclosure. The flaw (CVE-2026-39987) in the /terminal/ws WebSocket endpoint allowed unauthenticated interactive shell access, enabling rapid credential theft observed by Sysdig and prompting Marimo to release version 0.23.0. #Marimo #CVE-2026-39987

Adobe released emergency patches for a critical Acrobat and Reader zero-day that has been exploited in the wild for several months. The vulnerability, tracked as CVE-2026-34621 with a CVSS score of 9.6, enables arbitrary code execution via improperly controlled prototype attribute modifications and affects Acrobat/Reader on Windows and macOS. #CVE-2026-34621 #AdobeAcrobat…