Attackers are exploiting a critical remote code execution flaw in the Marimo reactive Python notebook (CVE-2026-39987) to deploy a new variant of NKAbuse hosted on Hugging Face Spaces. Sysdig observed rapid post-disclosure exploitation that delivered a dropper and a kagent binary for persistence and remote access, and recommends upgrading to Marimo 0.23.0 or blocking the /terminal/ws endpoint if upgrading is not possible. #NKAbuse #Marimo
Category: Cyber Security News
AI-enabled SOC tools often speed up triage by summarizing, enriching, and suggesting next steps for alerts, but many demos overpromise on autonomous incident response. True impact comes when AI is embedded into end-to-end, reliable workflows that integrate tools, provide auditability, and keep humans in the loop. #Jamf #Udemy
ATHR is a commercial cybercrime platform that automates voice-phishing attacks using AI voice agents and optional human operators to socially engineer victims and harvest account credentials. Advertised on underground forums for $4,000 plus a 10% commission, ATHR automates the full TOAD attack chain—from spoofed, brand-specific emails to Asterisk/WebRTC calls—targeting services like Google and Coinbase. #ATHR #Coinbase
Matthew Lane, now 20, played a central role in the PowerSchool breach that exposed data tied to roughly 60 million students and 10 million teachers and prompted millions in ransom payments. He pleaded guilty, was sentenced to four years in prison with over $14 million in restitution, and his case highlights…
Two U.S. nationals were sentenced for helping North Korean IT workers pose as U.S. residents and secure employment at over 100 U.S. companies, generating more than $5 million for the DPRK and causing about $3 million in damages to victim firms. The scheme used shell companies, fake IDs, hosted company laptops, and fraudulent accounts to provide DPRK workers remote access to corporate networks, and investigations continue with several suspects at large. #DPRK #FBI
The ShinyHunters extortion group leaked data tied to 13.5 million McGraw Hill user accounts after exploiting a misconfiguration in a Salesforce-hosted webpage. Over 100GB of files containing names, addresses, phone numbers, and email addresses were published, and the group has also targeted Rockstar Games’ Snowflake environment and other organizations. #ShinyHunters #McGrawHill #Salesforce #RockstarGames #Snowflake
Microsoft is investigating an issue causing this month’s KB5082063 security update to fail to install on some Windows Server 2025 systems, with affected devices also reporting 0x800F0983 errors when applying the April 2026 cumulative updates. Some servers may also boot into BitLocker recovery after installing KB5082063; Microsoft says affected configurations are typically enterprise-managed and is looking into the root cause. #WindowsServer2025 #KB5082063
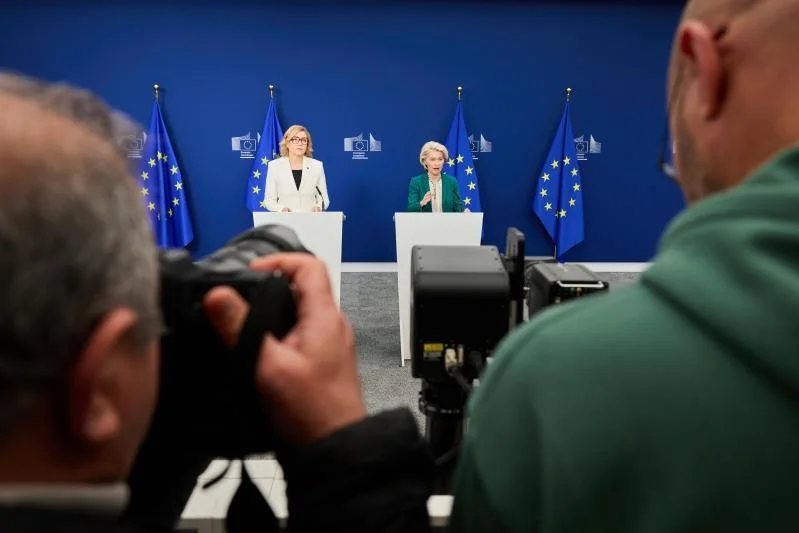
European Commission President Ursula von der Leyen announced a Europe-wide age verification app intended to strengthen children’s online safety by enabling age proof without revealing personal identity. The open-source, privacy-focused tool is ready for rollout, backed by enforcement efforts and planned integration with national digital wallets. #EuropeanCommission #AgeVerificationApp…

Daily Recap, Microsoft released April 2026 updates fixing 167 flaws, including two zero-days in SharePoint (CVE-2026-32201) and Defender (CVE-2026-33825), and urged urgent Office/Defender patches for Windows 11 25H2/24H2, Windows 10 ESU, and Windows Server 2025. The roundup also covers extortion-linked incidents involving Kraken and McGraw-Hill, the JanaWare Adwind RAT campaign targeting Turkey, and policy moves such as Virginia’s geolocation ban and Russia blocking Bluesky, alongside AI defense advances like OpenAI’s GPT-5.4 Cyber.
#SharePoint #Defender #Kraken #McGrawHill #JanaWare #AdwindRAT #Turkey #Virginia #Bluesky #OpenAI #GPT54Cyber

April’s Patch Tuesday delivered critical fixes across Adobe, Fortinet, Microsoft, SAP and many other vendors, led by an SQL injection in SAP Business Planning and Consolidation/SAP Business Warehouse (CVE-2026-27681, CVSS 9.9) that can execute arbitrary database commands. Adobe Acrobat Reader (CVE-2026-34621) is facing active in-the-wild RCE exploitation while FortiSandbox and Microsoft…

A critical authentication-bypass vulnerability in nginx-ui (CVE-2026-33032) enables attackers to invoke MCP tools via the unauthenticated /mcp_message endpoint to restart Nginx, modify configs, reload the server, and harvest credentials. Pluto Security dubbed the flaw MCPwn, researchers found about 2,689 exposed instances worldwide and a patch was released in nginx-ui 2.3.4 on…

Threat actors are abusing n8n’s managed cloud-hosted workflows and exposed webhook URLs on the *.app.n8n.cloud domain to run phishing campaigns that deliver malicious payloads and fingerprint devices. Cisco Talos warns these campaigns use n8n-hosted pages and CAPTCHA triggers to fetch modified RMM installers (including Datto and ITarian) for persistent remote access,…

A 16-year-old has been arrested in Northern Ireland after an attack disrupted the C2K education system used by almost all schools, temporarily taking services offline and hindering access for hundreds of thousands of pupils and teachers. Authorities say the incident was targeted at a small number of schools and may have…

NIST announced it will limit enrichment of CVE records to vulnerabilities that meet new prioritization criteria after an exponential surge in submissions made it impossible to document every report. Going forward, NIST will enrich only CVEs listed in CISA’s catalog of exploited vulnerabilities, those affecting federal or critical products, and will…
A new C# malware family called AgingFly has been used in Ukraine against local governments and hospitals to steal authentication data from Chromium-based browsers and the WhatsApp Windows client. CERT-UA attributes the campaign to UAC-0247 and describes a complex LNK→HTA→scheduled-task attack chain that stages payloads, uses open-source tools like ChromElevator and ZAPiDESK to exfiltrate credentials, and dynamically compiles command handlers received from a C2 server. #AgingFly #CERT-UA