
Athr is a for-sale, fully automated callback-phishing platform that spoofs security alerts from major providers and routes victims to human operators or AI voice agents. For $4,000 plus a cut of the take, operators can run integrated campaigns that harvest account credentials and six-digit verification codes using realistic templates, telephony routing, and live monitoring. #ATHR #Coinbase
Category: Cyber Security News
Check Point researchers uncovered a SystemBC botnet of more than 1,570 infected hosts tied to a Gentlemen ransomware affiliate that used the proxy for covert payload delivery. The Gentlemen RaaS, active since mid‑2025 with Go and C lockers (including an ESXi variant), employs a human‑operated toolkit—Cobalt Strike, Mimikatz and GPO propagation—and a hybrid X25519/XChaCha20 encryption scheme. #SystemBC #GentlemenRansomware
Two sentences summarizing the content. FakeWallet is a campaign of 26 malicious apps that impersonated popular wallets like MetaMask, Coinbase, Trust Wallet, OneKey, and Ledger to steal recovery/seed phrases and drain cryptocurrency. Kaspersky links the campaign to the SparkKitty operation, noting the apps used typosquatting, fake branding, iOS provisioning profiles, and phishing to sideload trojanized wallets and exfiltrate mnemonics. #FakeWallet #SparkKitty
North Korean state-sponsored hackers, likely the Lazarus Group (TraderTraitor), stole about 116,500 rsETH — roughly $290–293 million — from the KelpDAO DeFi project by poisoning RPC nodes to forge cross-chain messages. The attackers laundered funds through Tornado Cash, prompted rsETH contract freezes across Ethereum and L2s, and triggered an ongoing investigation by LayerZero and partners. #LazarusGroup #KelpDAO
Sophos reports an increase in threat actors abusing the QEMU machine emulator to create covert reverse SSH backdoors and deploy ransomware and remote access tools. Two campaigns—STAC4713 (linked to PayoutsKing/Gold Encounter) and STAC3725—leveraged exposed SonicWall VPNs, SolarWinds Web Help Desk (CVE-2025-26399), and CitrixBleed2 (CVE-2025-5777) to establish persistence, harvest credentials, and exfiltrate…
Tyler Robert Buchanan pleaded guilty in a U.S. court to conspiring with the Scattered Spider group to hack dozens of companies and steal millions in cryptocurrency. He and co-conspirators used SMS phishing, a phishing kit, Telegram data exfiltration, and SIM swapping to harvest credentials, bypass MFA, and drain victims’ cryptocurrency wallets….
Researchers at Forescout discovered 20 vulnerabilities in Silex and Lantronix serial-to-IP converters, tracked as BRIDGE:BREAK, that allow unauthenticated remote code execution, firmware tampering, and device takeover. The flaws put OT and healthcare systems at risk—researchers demonstrated sensor manipulation and DoS via malicious firmware—and vendors have released patches while CISA has published…
An attacker moved through third-party systems to steal credentials and sensitive data from Vercel after compromising a Context.ai employee’s machine with Lumma Stealer. Vercel and Context.ai say a limited number of customers were affected, investigators including CrowdStrike and Mandiant are involved, and a group claiming to be ShinyHunters is attempting to sell the stolen data. #LummaStealer #ShinyHunters

The FTC is ramping up enforcement of the Take It Down Act to curb AI-enabled harms like nonconsensual sexualized deepfakes and voice‑cloning scams. With the DOJ already securing a conviction and a May takedown provision requiring platforms to remove sexual deepfakes within 48 hours, the agency is preparing to target noncompliant companies such as xAI’s Grok while prioritizing protections for children. #TakeItDownAct #Grok
Researchers at Pillar Security disclosed a prompt injection vulnerability in Google’s Antigravity agent that allowed attackers to combine injected prompts with a file-creation capability to achieve remote code execution. The flaw bypassed Antigravity’s Secure Mode by invoking a native file-search tool before sandbox protections could evaluate commands, highlighting the danger of unvalidated input to agentic AIs. #Antigravity #PillarSecurity
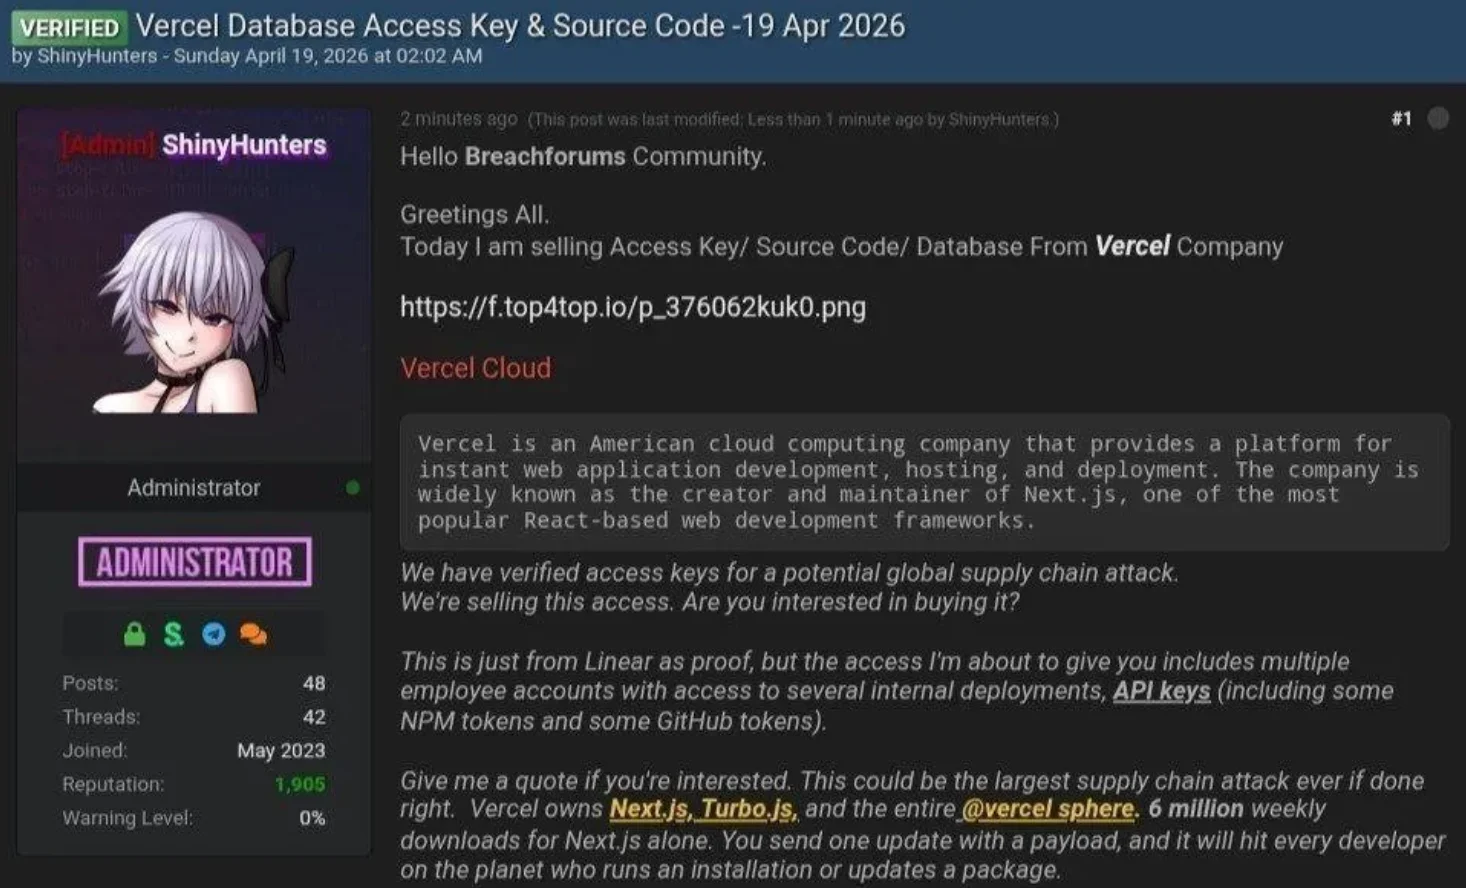
Vercel suffered a security breach after a third-party AI tool compromise (Context.ai) allowed attackers to hijack a Vercel employee’s Google Workspace account and access some internal environments and environment variables. A limited subset of customers had credentials compromised, and Vercel has notified affected users, advised rotating secrets, engaged Google Mandiant and other experts, and deployed additional protections. #Vercel #ContextAI #GoogleWorkspace #ShinyHunters #BreachForums #NextJS #Turbopack
Nearly $290 million in cryptocurrency was stolen after North Korean-linked hackers known as TraderTraitor (part of the Lazarus operation) exploited a single-verifier setup tied to Kelp and LayerZero, minting fake rsETH and using it as collateral to drain funds. LayerZero blamed Kelp’s single-DVN configuration, said it will block single-verifier integrations, and affected platforms like Aave and law enforcement are involved in assessing responses. #TraderTraitor #Lazarus #LayerZero #Kelp #rsETH #Aave
Italy’s data protection regulator fined Poste Italiane SpA €6.6 million and Postepay SpA €5.9 million, totaling €12.5 million, for allegedly illegally processing millions of users’ personal data through invasive monitoring. The regulator said the Postepay and BancoPosta apps required users to authorize monitoring of installed and running applications in a way it deemed excessively invasive, insufficiently disclosed, and not necessary for fraud prevention. #PosteItaliane #Postepay
The Seiko USA website was defaced with an extortion message claiming attackers accessed its Shopify backend and stole the company’s customer database. The page warned of a 72-hour deadline to negotiate or the attackers would publish names, emails, phone numbers, order and shipping data, and account details; Seiko USA has not publicly confirmed the breach and removed the message. #SeikoUSA #Shopify
Bluesky said a sophisticated DDoS attack beginning April 15 caused widespread outages that disrupted feeds, notifications, threads and search, but engineers mitigated the attack and the application has remained stable since April 16. The company reported no evidence of unauthorized access to private user data while an Iran-linked group calling itself 313 Team claimed responsibility, though Bluesky has not confirmed the attribution. #Bluesky #313Team