
A former ransomware negotiator, Angelo Martino, pleaded guilty to collaborating with BlackCat operators in 2023 to provide confidential victim negotiation details and help maximize ransom demands. Martino and two other incident responders also admitted to deploying BlackCat, extorting victims for about $1.2 million in one case, and authorities seized roughly $10…
Category: Cyber Security News

Researchers at Forescout Vedere Labs uncovered 22 vulnerabilities, labeled BRIDGE:BREAK, in Lantronix and Silex serial-to-IP converters that put nearly 20,000 devices online at risk of hijack and data tampering. Vendors have released patches, and users are urged to remove internet exposure, change default credentials, and segment networks to limit attacker movement….

A third man, Angelo Martino, has pleaded guilty to participating in ransomware attacks while working for a cybersecurity company hired to negotiate with hackers. Authorities say Martino and two co-defendants provided confidential negotiation information to the BlackCat/Alphv group, received payments, and face up to 20 years in prison. #BlackCat #AngeloMartino…
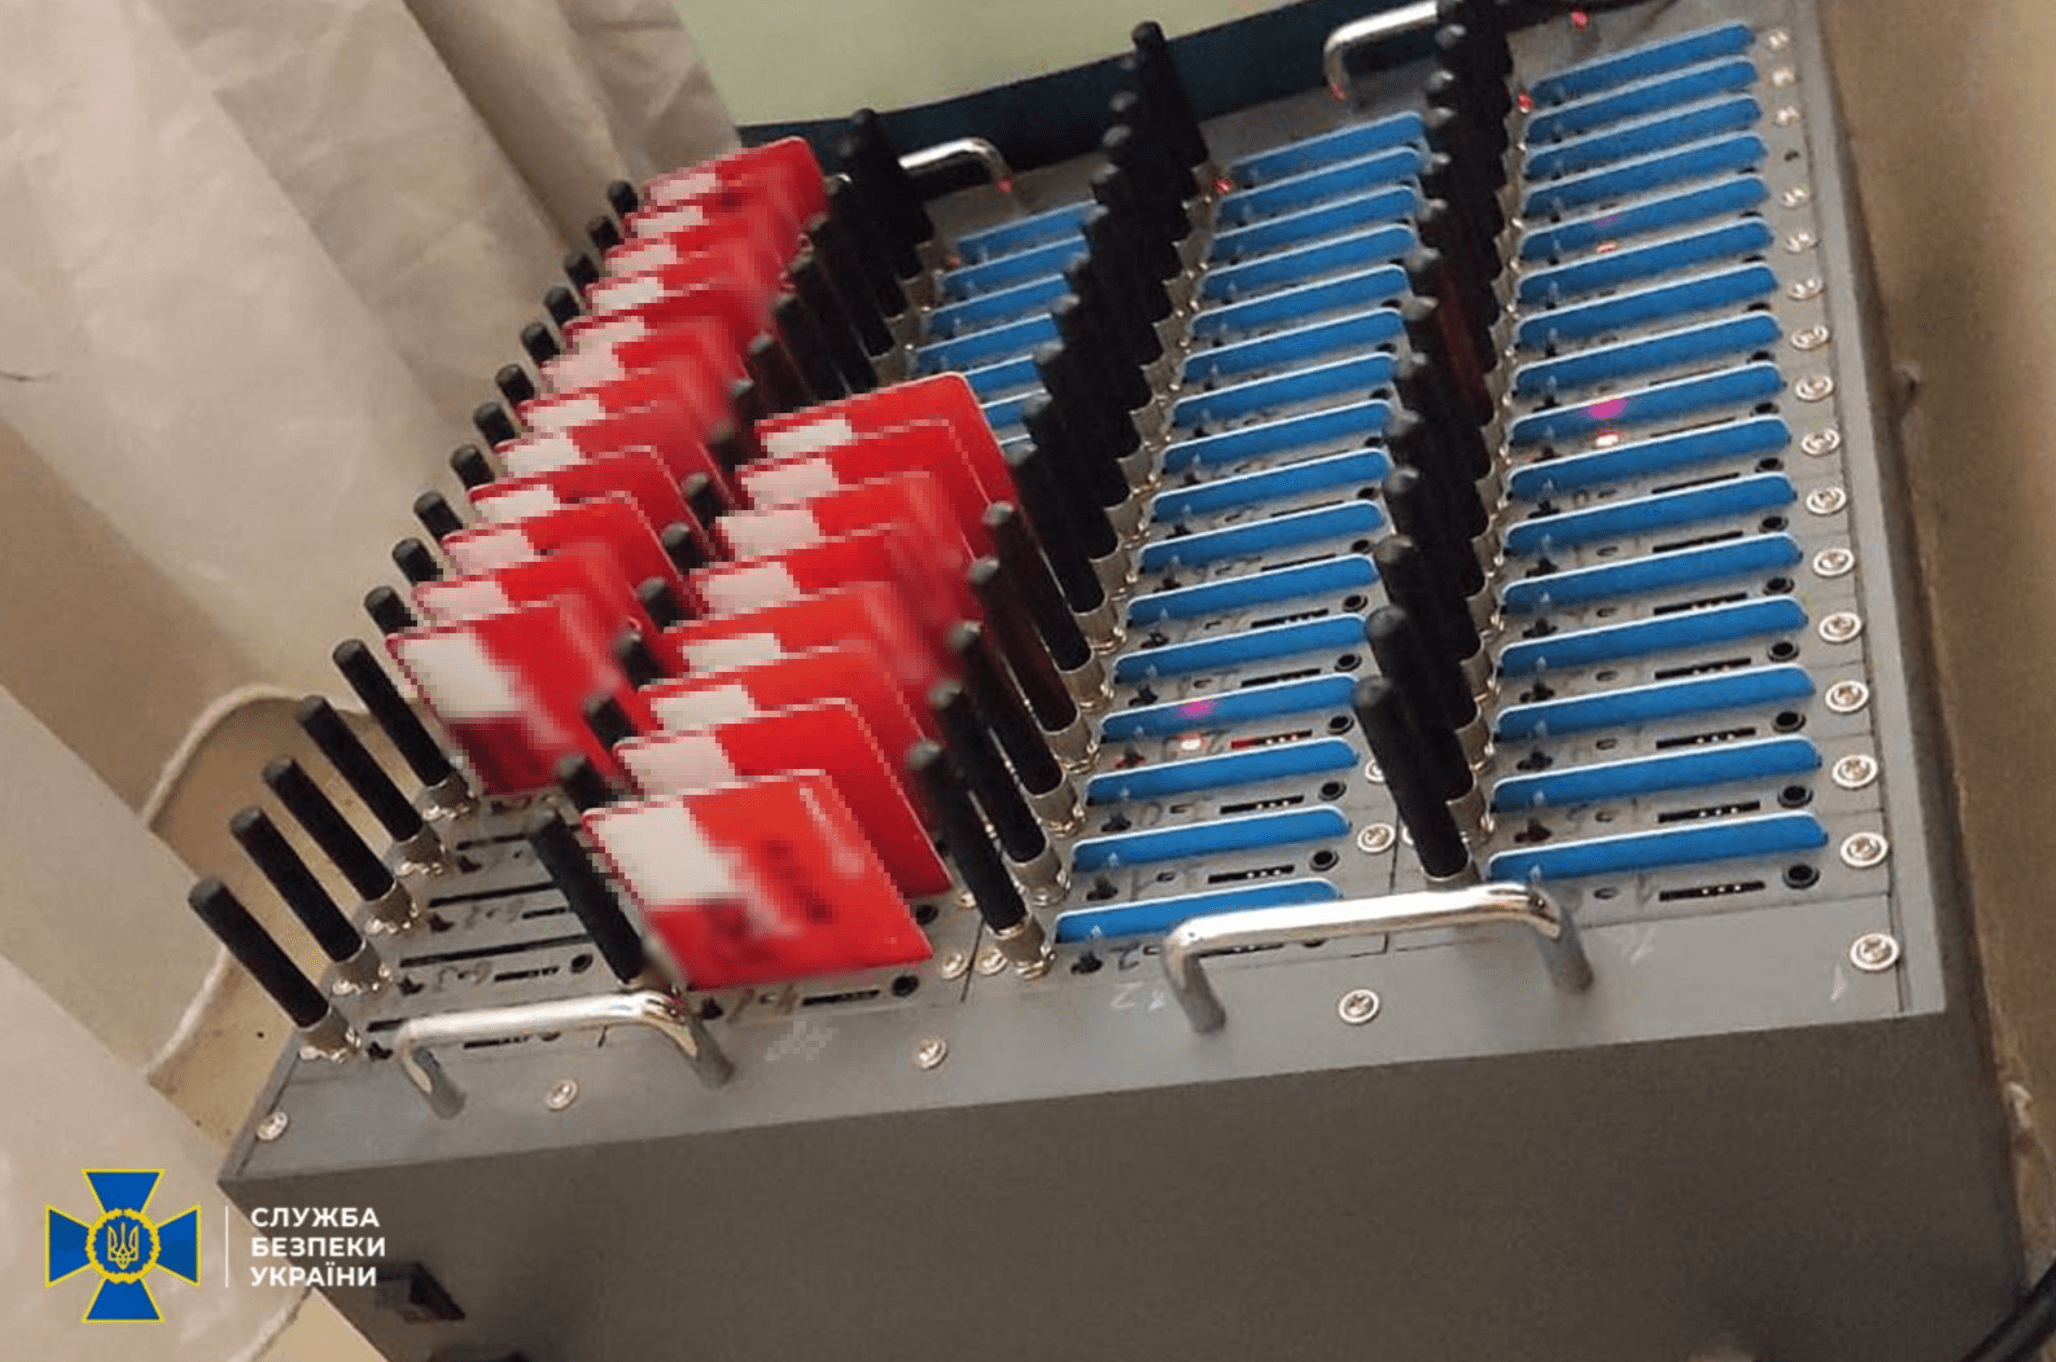
Ukrainian authorities dismantled a bot farm in Zhytomyr that supplied nearly 20,000 fake social media profiles and thousands of SIM-based Telegram accounts to Russian intelligence for disinformation operations. The suspect was detained, investigators seized equipment and about 2,000 SIM cards, and faces up to six years in prison amid findings that the accounts were used to spread propaganda, false mining claims, and targeted phishing. #RussianIntelligence #SBU
A popular cloud platform, Vercel, suffered a breach traced to a compromised third-party AI tool, Context.ai, which allowed attackers to access an employee’s Google Workspace account and some non-sensitive environment variables. Vercel is investigating with Mandiant and law enforcement, has warned affected customers to rotate credentials, and cautioned that deleting projects or accounts does not remove all risk. #Vercel #ContextAI
The European Union has imposed sanctions on two pro‑Russian organizations, Euromore and the Foundation for the Support and Protection of the Rights of Compatriots Living Abroad (Pravfond), for spreading disinformation and supporting Kremlin hybrid influence operations against the EU and Ukraine. The measures freeze any assets within the EU and bar EU citizens and companies from providing funds or economic resources, while noting Euromore’s domain now redirects to Euroview Media which republishes material from RT and Sputnik. #Euromore #Pravfond
China-linked APT Mustang Panda has shifted its focus from purely geopolitical espionage to target Indian financial organizations, using spear-phishing and DLL sideloading to deliver a variant of its LotusLite backdoor disguised as regional banking software. The campaign relies on unsophisticated but disciplined tradecraft that remains effective against inconsistent basic defenses and appears aimed at intelligence collection rather than direct financial theft. #MustangPanda #LotusLite
Ofcom has opened an investigation under the UK’s Online Safety Act into Telegram after receiving evidence from the Canadian Centre for Child Protection and conducting its own assessment that the platform is being used to share child sexual abuse material; Ofcom is also probing Teen Chat, Chat Avenue, and X over grooming risks and AI-generated nonconsensual explicit content. If Ofcom finds compliance failures it can impose fines up to £18 million or 10% of qualifying worldwide revenue and seek court orders to block or disrupt services, while Telegram denies the allegations and says it has virtually eliminated public CSAM since 2018. #Telegram #Ofcom
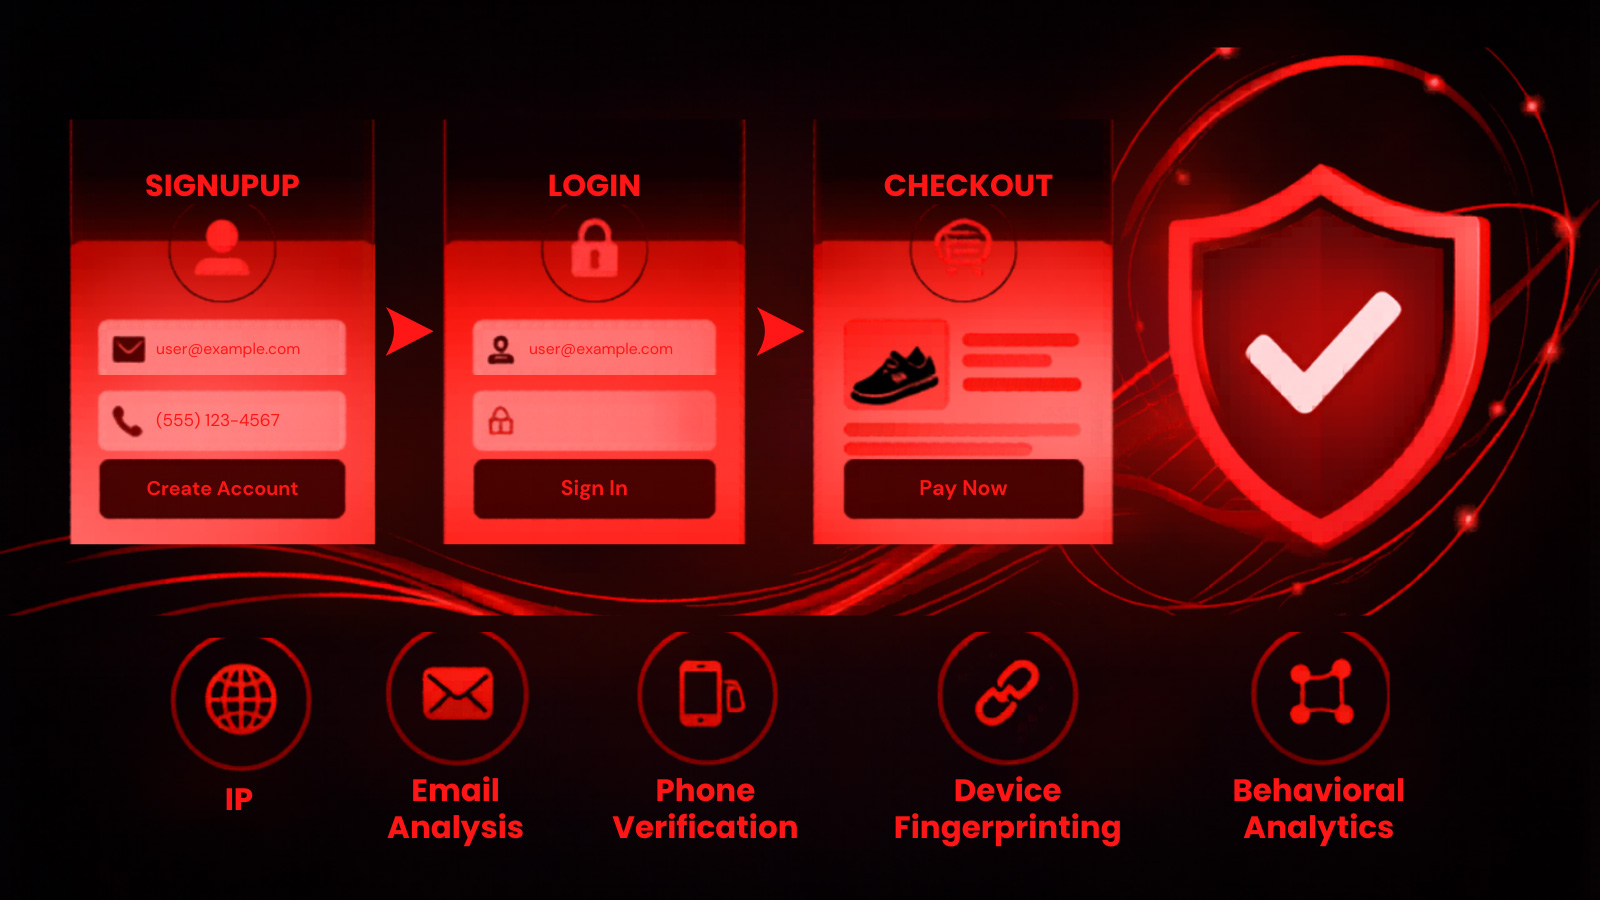
Modern threat intelligence platforms combine dozens of real-time risk signals to stop bots, credential stuffing, synthetic identities, and account takeover attempts without adding friction for legitimate users. IPQS applies this layered, frictionless approach across signup, login, and checkout using unified risk scores and tiered responses to protect revenue and user experience. #IPQS #AccountTakeover
A 2025 analysis by Australian researcher Morgan Robertson found 6,122 internet-facing Perforce P4 servers, many misconfigured and exposing highly sensitive information. Several active instances still allow unauthenticated read or write access and some expose superuser accounts, putting intellectual property and personal data at risk. #PerforceP4 #MorganRobertson…
FakeWallet is a campaign that published over two dozen fake cryptocurrency apps to the Apple App Store to harvest users’ recovery phrases and private keys. Kaspersky links the apps to the SparkKitty toolkit, noting they typosquat major wallets and use browser-based phishing and Ledger-targeting implants to distribute infected wallet versions. #FakeWallet…
CISA added eight actively exploited vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog on April 21, 2026, covering products such as PaperCut NG/MF, JetBrains TeamCity, Quest KACE SMA, Zimbra Collaboration Suite, Kentico Xperience, and Cisco Catalyst SD‑WAN Manager. Federal remediation deadlines for April–May 2026 accompany the update as CISA urges prioritized…
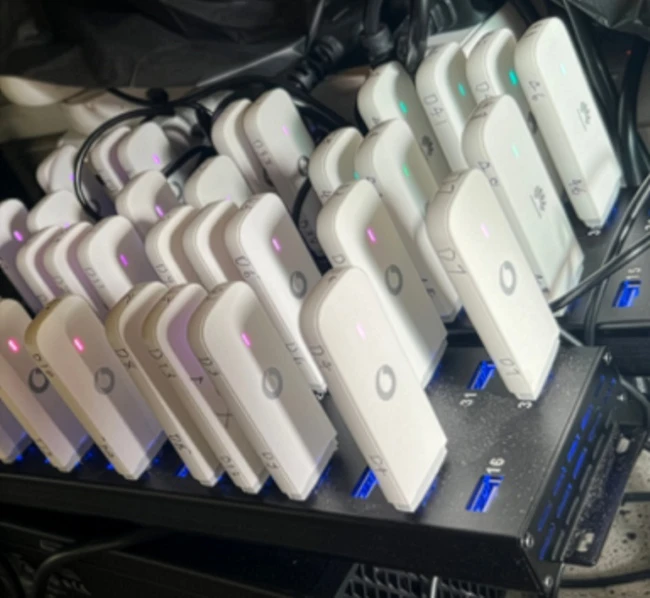
Infrawatch’s investigation found racks of phones and 4G/5G modems running ProxySmart-powered SIM farms operating across at least 94 locations in 17 countries, with a heavy concentration in the United States. ProxySmart provides device management, automated IP rotation, OS fingerprint spoofing, and tunneling features that enable commercial mobile proxy services used for account automation and likely large-scale fraud. #ProxySmart #Infrawatch

CISA added eight vulnerabilities to its Known Exploited Vulnerabilities catalog, including three affecting Cisco Catalyst SD-WAN Manager (CVE-2026-20133, CVE-2026-20128, CVE-2026-20122), with Cisco confirming active exploitation of two of those in March 2026. US federal civilian agencies must remediate all eight flaws by April 20, 2026, while other listed issues include exploited bugs in PaperCut NG/MF linked to Lace Tempest, JetBrains TeamCity, Quest KACE appliances, and Synacor Zimbra. #CiscoCatalystSDWAN #CVE-2026-20133 #LaceTempest #PaperCutNGMF #Zimbra
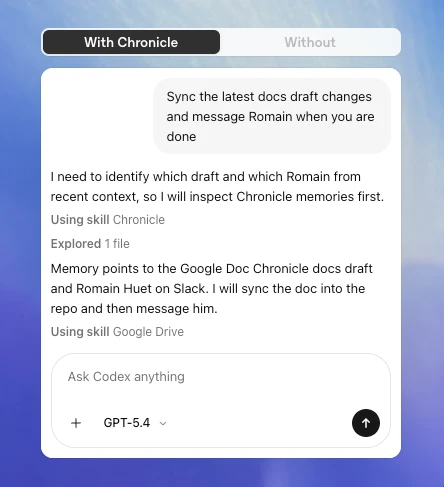
OpenAI’s Chronicle captures recent screen activity to build contextual memories so the Codex coding assistant can interpret references, identify relevant sources, and understand users’ tools and workflows without repeated prompts. The opt-in macOS research preview for ChatGPT Pro stores temporary screen captures locally, processes selected frames through ephemeral Codex sessions, and includes pause controls and privacy considerations such as prompt injection risk and unencrypted local markdown storage. #Chronicle #Codex