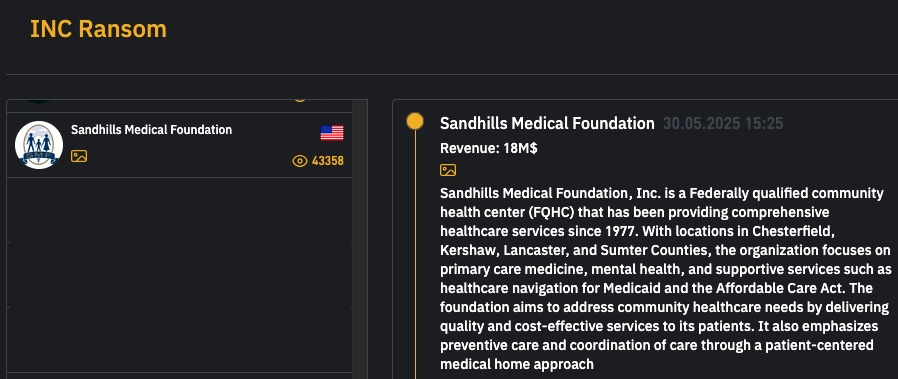
Sandhills Medical Foundation disclosed a ransomware attack discovered on May 8, 2025, that exposed personal and health information for nearly 170,000 individuals. The Inc Ransom group posted the allegedly stolen files online while the provider works with law enforcement, cybersecurity experts, and a forensics firm and notifies affected patients. #SandhillsMedicalFoundation #IncRansom…
Category: Cyber Security News
Hackers exploited two authentication bypass flaws in the Qinglong open-source task scheduler to deploy cryptominers on developers’ servers, with attacks beginning in early February before the issues were publicly disclosed. The issues (CVE-2026-3965 and CVE-2026-4047) stem from a mismatch between middleware authorization and Express.js routing and were effectively fixed in PR #2941 after an initial insufficient mitigation; #Qinglong #CVE-2026-3965
European Commission says Meta failed to prevent children under 13 from accessing Instagram and Facebook and violated the Digital Services Act by not adequately assessing or mitigating risks to minors. The commission has issued preliminary findings requiring stronger age verification and risk-mitigation measures, with potential fines up to 6% of annual…
U.S. and Chinese law enforcement jointly raided at least nine scam centers in Dubai, resulting in 276 arrests and federal fraud and money laundering charges against alleged operators of pig-butchering investment schemes. Investigators traced the networks using Meta data, financial and cryptocurrency records, and the operation is part of broader actions…
The House voted 235-191 to renew Section 702 of the Foreign Intelligence Surveillance Act for three years, extending warrantless surveillance authorities and sending the bill to the Senate one day before the authority was set to expire. The measure includes concessions — such as a ban on a Federal Reserve digital…
Quick Page/Post Redirect, installed on more than 70,000 WordPress sites, contained a backdoor added five years ago that allowed arbitrary code to be injected via a hidden self-update mechanism. The compromised updater pointed to an external domain (anadnet[.]com), pushed a tampered 5.2.3 build that added a passive SEO backdoor for logged-out users, and WordPress.org has temporarily pulled the plugin pending review. #QuickPagePostRedirect #anadnet
Multiple official SAP npm packages were compromised in an apparent TeamPCP supply-chain attack that inserted a malicious preinstall script to steal developer credentials and CI secrets. The attack used a setup.mjs loader that downloads the Bun runtime to run an obfuscated information-stealer which exfiltrates tokens, SSH keys, cloud and Kubernetes credentials, and memory-scraped CI secrets, then uploads data to public GitHub repos. #TeamPCP #SAP
Lawmakers at a House Homeland Security subcommittee hearing debated whether data centers should be designated a standalone critical infrastructure sector as rapid AI-driven growth and targeting increase their strategic importance. Panelists highlighted recent Iranian drone strikes on Amazon and Bahrain facilities, the market concentration among AWS, Azure and Google Cloud, and calls for clearer federal coordination and protection. #AmazonWebServices #IranianDrones
GitHub patched a critical remote code execution vulnerability that could have allowed attackers to access millions of private repositories. The flaw (CVE-2026-3854), reported by Wiz, was confirmed and fixed quickly on GitHub.com, but many GitHub Enterprise Server instances remain vulnerable and must be upgraded immediately. #CVE-2026-3854 #GitHub
Unapproved AI apps can create persistent OAuth bridges between enterprise platforms and third-party services, and when those providers are compromised attackers can pivot into corporate environments. The Vercel incident involving Context.ai illustrates how shadow AI integrations and widespread OAuth sprawl across SaaS amplify risk and demand tighter consent controls and browser-level visibility. #Vercel #ContextAI
Ukrainian police in Lviv arrested three suspects who hacked over 610,000 Roblox accounts and sold them for about $225,000. Authorities seized cash and multiple devices after searches and say the group used info‑stealing malware disguised as a game‑enhancer to harvest credentials, targeting at least 357 elite accounts. #Roblox #Robux

Researchers uncovered that threat actors are now deploying custom AI autonomous agents that automate attacks directly into the kill chain, including mapping Active Directory and seizing Domain Admin credentials in minutes. A technical webinar with Picus Security will present Autonomous Exposure Validation as a new defensive paradigm to close the speed…

Researchers discovered malicious code embedded in the npm package “@validate-sdk/v2” that acts as a credential and crypto-wallet stealer when introduced as a dependency to other projects. ReversingLabs calls the campaign PromptMink and links it to North Korean actor Famous Chollima, which leverages AI-generated code, layered dependencies, typosquatting and transitive-dependency tricks to…

Cybersecurity researchers warn of a supply chain campaign called “mini Shai-Hulud” that poisoned SAP-related npm packages ([email protected], @cap-js/[email protected], @cap-js/[email protected], @cap-js/[email protected]) by adding a preinstall hook that downloads and executes a Bun-based credential stealer. The malware harvests developer, GitHub, npm, and cloud secrets, encrypts and exfiltrates them to victim-owned GitHub repositories, and…
Austrian and Albanian authorities, supported by Europol and Eurojust, dismantled a large cryptocurrency investment fraud ring that stole an estimated €50 million from victims worldwide and arrested 10 suspects after coordinated raids on April 17. The operation ran professionally organized call centres in Tirana with up to 450 staff who lured victims to fake trading platforms, used remote-access tools and pressure tactics to steal funds, then laundered proceeds and re-scammed victims with fake recovery fees. #Europol #Tirana