Microsoft is previewing a modernized Run dialog in Windows 11 Build 26300.8346 that adopts Fluent Design, supports dark mode, and shows improved performance over the legacy dialog. The optional feature removes the Browse button due to minimal usage, is enabled via Settings > Advanced Settings, and is rolling out alongside Share UI improvements for AAD users and new Magnifier zoom presets. #Windows11 #Microsoft
Category: Cyber Security News
Two cybersecurity incident responders, Ryan Goldberg and Kevin Martin, were sentenced to four years in prison after pleading guilty to conspiring to obstruct commerce by extortion for conducting covert ALPHV/BlackCat ransomware attacks that abused their incident response positions. The scheme involved co-conspirator Angelo Martino, produced a $1.2 million extortion, included leaks…
CISA ordered federal agencies to patch CVE-2026-41940 in cPanel & WHM by May 3 after confirmation of active exploitation that can grant attackers full control of hosts, configurations, databases, and managed websites. Vendors and hosting providers have issued patches and detection tools while many providers took emergency measures to protect customers….
The Senate Judiciary Committee advanced the GUARD Act, which would bar AI companies from allowing children to use AI companions and require chatbots to disclose they are not human and lack professional credentials. The bill mandates strict age verification with ongoing ID or biometric checks, criminalizes AI sexual solicitation of minors,…

Researchers disclosed a China-aligned espionage campaign tracked as SHADOW-EARTH-053 that has targeted government and defense organizations across South, East, and Southeast Asia and Poland, using web shells and ShadowPad implants. The actors exploit N-day Exchange and IIS vulnerabilities, deploy Godzilla web shells and DLL sideloading, use tunneling tools and credential-stealing utilities,…

A newly discovered Vietnamese-linked operation codenamed AccountDumpling is using Google AppSheet as a phishing relay to send deceptive Meta Support emails that harvest Facebook credentials for resale. The campaigns employ multiple lures and hosting platforms (Netlify, Vercel, Google Drive, Canva) to collect passwords, 2FA codes, ID photos and other data which…

Five national cybersecurity agencies urged organizations to treat agentic AI as a core cybersecurity concern, warning the technology is already being deployed in critical infrastructure and defense sectors with insufficient safeguards. Their guidance advises folding agentic AI into existing security frameworks—applying zero trust, least-privilege, cryptographic identities, encrypted communications and human sign-off for high-impact actions—while highlighting five risk categories and flagging prompt injection as a key threat. #AgenticAI #PromptInjection
French authorities have detained a 15-year-old suspected of selling data stolen from France’s document agency ANTS after the breach was advertised on a cybercriminal forum. Investigators say the alias “breach3d” offered between 12 and 18 million records (ANTS later confirmed 11.7 million impacted accounts) and the suspect now faces charges including unauthorized access, data exfiltration, and possession of offending software. #ANTS #breach3d

Researchers warn that two cybercrime clusters, Cordial Spider and Snarky Spider, carry out rapid, high-impact data-theft and extortion campaigns that operate almost entirely within trusted SaaS environments while leaving minimal forensic traces. Using vishing to funnel victims to SSO-themed adversary-in-the-middle pages, they capture credentials and MFA codes, register new devices, suppress…
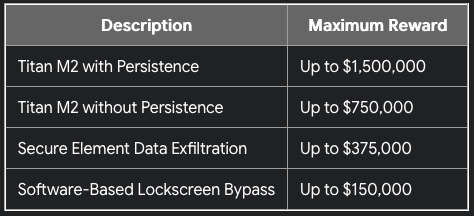
Google has restructured its Chrome and Android Vulnerability Reward Programs to prioritize high-impact, hard-to-discover flaws and to incentivize actionable reports that include proposed patches. Payouts increased for select Android/Pixel exploits while many Chrome base rewards and bonuses were reduced as Google shifts to concise proof-of-concept submissions in response to a surge…

This week’s roundup highlights coordinated sanctions, high-profile arrests, major data exposures, and critical vulnerabilities shaping the threat landscape. Key items include OFAC’s designation and a Tether freeze, the arrest of a Scattered Spider suspect, ADT’s customer data leak, dangerous ICS and IDE flaws, and North Korean social engineering targeting crypto firms….
Microsoft released an optional preview update (KB5083631) that fixes a bug causing Remote Desktop (.rdp) security warning dialogs to render incorrectly on multi-monitor systems with mixed display scaling after the April 2026 updates across supported Windows versions. The April security changes introduce one-time and connection-time RDP warnings to block risky resource redirections and counter RDP abuse in phishing campaigns by actors such as APT29. #APT29 #Windows11
Criminal IP has partnered with Securonix to integrate its exposure-based threat intelligence directly into the ThreatQ platform, allowing organizations to enrich IP indicators with real-time context without changing existing workflows. The integration automates continuous enrichment—providing maliciousness scoring, VPN/proxy detection, open ports, and vulnerability insights—to accelerate triage, prioritization, and response within ThreatQ. #CriminalIP #ThreatQ
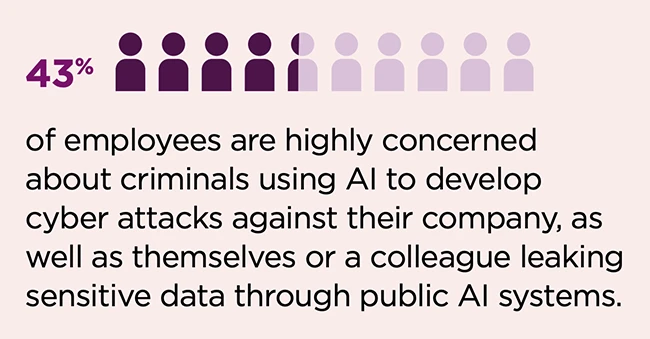
Between one-fifth and one-third of enterprise employees use AI outside IT governance, driven by gaps in tooling and inconsistent training that push many to consumer services. Lenovo’s report warns this shadow AI adoption increases risks of data leakage and compliance failures and urges governance, in-context training, and standardized AI interfaces to regain control. #Lenovo #ChatGPT
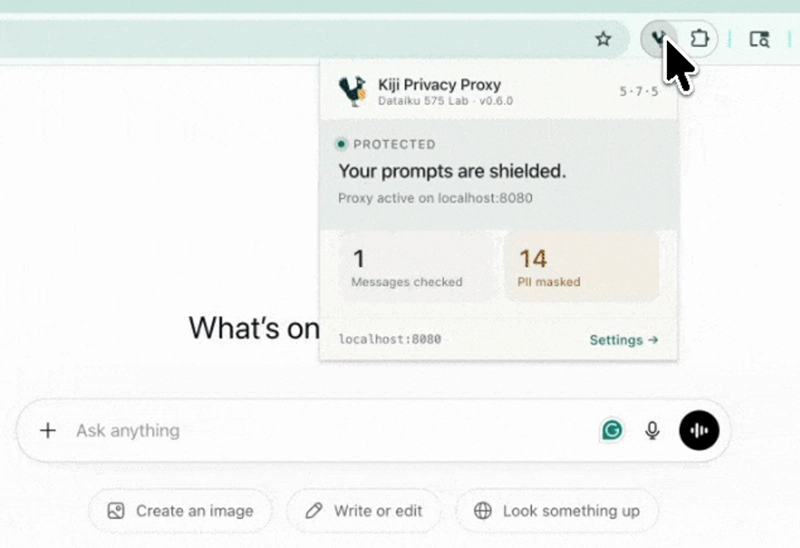
Dataiku has released Kiji Privacy Proxy, an open-source local gateway that detects and masks personally identifiable information in requests before they are sent to external AI APIs. The tool performs local PII detection with a quantized DistilBERT model (ONNX Runtime), substitutes realistic dummy values, forwards masked requests to providers like OpenAI and Anthropic, and restores original values in responses to preserve application behavior. #KijiPrivacyProxy #Dataiku