Attackers are increasingly abusing Amazon Simple Email Service (SES) by using exposed AWS access keys to send large volumes of highly convincing phishing emails that bypass authentication checks and reputation-based blocks. Kaspersky links the surge to automated secret-scanning tools that harvest leaked IAM keys from public GitHub repos, .env files, Docker images, backups, and S3 buckets, enabling scalable phishing and BEC campaigns. #AmazonSES #TruffleHog
Category: Cyber Security News
A 19-year-old woman, Kaelyn Lunglhofer, alleges the dating app Meete took a TikTok video of her without consent, edited it with a voiceover into an advertisement, and used geofencing to target the ad to people near her, including men in her dorm. She is suing multiple companies behind Meete under federal and Tennessee laws seeking $750,000 and any ad revenue, saying the ads damaged her reputation and put her at risk of harassment. #Meete #Snapchat
Trellix disclosed that attackers gained unauthorized access to a portion of its source code repository and is working with outside forensic experts and law enforcement to investigate. The company says it has found no evidence so far that the code was altered or exploited, and the incident follows recent supply-chain and repository breaches affecting Checkmarx, Cisco, and HackerOne/Navia. #Trellix #LAPSUS$
A malicious PyTorch Lightning package (lightning==2.6.3) published on PyPI delivered a credential‑stealing JavaScript payload that executed automatically on import and spawned a background process. Microsoft Defender detected and blocked the routine (identified as ShaiWorm), the package was reverted to 2.6.1, and users who imported the compromised release are advised to rotate all secrets. #ShaiWorm #PyTorchLightning

Progress Software has released patches for MOVEit Automation to address two vulnerabilities, including CVE-2026-4670—a critical authentication bypass (CVSS 9.8)—and CVE-2026-5174, an improper input validation issue that could enable privilege escalation. Affected releases (…

An active phishing campaign dubbed VENOMOUS#HELPER has been targeting multiple vectors since at least April 2025, using legitimate Remote Monitoring and Management tools to establish persistent remote access. The operation delivers a JWrapper-packaged executable that installs SimpleHelp as a service, elevates privileges for full desktop control, and stages ConnectWise ScreenConnect as…
Trellix says part of its source code repository was breached and it is working with forensic experts while notifying law enforcement. Details are scarce, and the timing suggests a possible link to a wider supply-chain campaign tied to groups like TeamPCP and Lapsus. #Trellix #Lapsus…
Microsoft confirms the April 2026 security updates have added the kernel driver psmounterex.sys to the Vulnerable Driver Blocklist, causing third‑party backup applications that use VSS snapshots to fail to mount or browse backup images. The hardening addresses CVE-2023-43896, and Microsoft urges customers to install updated application versions with newer drivers instead of uninstalling or pausing the update. #psmounterex.sys #VSS
Cyberattacks are evolving faster than many MSPs can respond to, with AI-driven phishing and brand impersonation now serving as primary entry points that outpace traditional email defenses. BleepingComputer and Kaseya will host a live webinar on May 14, 2026, at 2:00 PM EDT to explain how attacks progress and why SaaS backups plus a BCDR strategy are essential for rapid recovery and maintaining uptime. #BleepingComputer #Kaseya
Progress Software warned customers to patch a critical authentication bypass vulnerability (CVE-2026-4670) in MOVEit Automation that allows remote, unauthenticated attackers to bypass authentication in low-complexity, no-interaction attacks. The company released patched updates (and a fix for a related privilege escalation CVE-2026-5174), recommends upgrading with the full installer despite an expected outage, and noted over 1,400 online instances with some tied to U.S. government agencies. #MOVEitAutomation #Clop
Threat actors in underground forums are developing structured, process-driven loan fraud schemes that exploit onboarding and verification workflows using stolen identities and social engineering. Flare researchers identified a reproducible method targeting small- to mid-sized credit unions that bypasses knowledge-based authentication and monetizes approved loans before detection. #CreditUnions #Flare
Threat actors are exploiting a long-standing Linux kernel vulnerability, CVE-2026-31431 (dubbed Copy Fail), that allows authenticated users with code execution to modify in-memory cache pages of readable setuid-root binaries and obtain a root shell. CISA has added the flaw to its Known Exploited Vulnerabilities catalog and urged rapid patching, while Microsoft…
DigiCert reported that on April 2 a threat actor delivered a malicious payload disguised as a screenshot via its customer chat, infecting support endpoints and using proxied analyst access and initialization codes to obtain EV Code Signing certificates. By April 17 DigiCert revoked 60 certificates — 27 linked to the actor…
Thirty-three cybersecurity M&A deals were announced in April 2026, continuing consolidation in the sector after more than 420 acquisitions in 2025. Notable transactions include Airbus’ acquisition of Quarkslab for sovereign cybersecurity, Cyera’s purchase of Ryft to bolster agentic AI data security, and Palo Alto Networks’ planned acquisition of Portkey to establish…
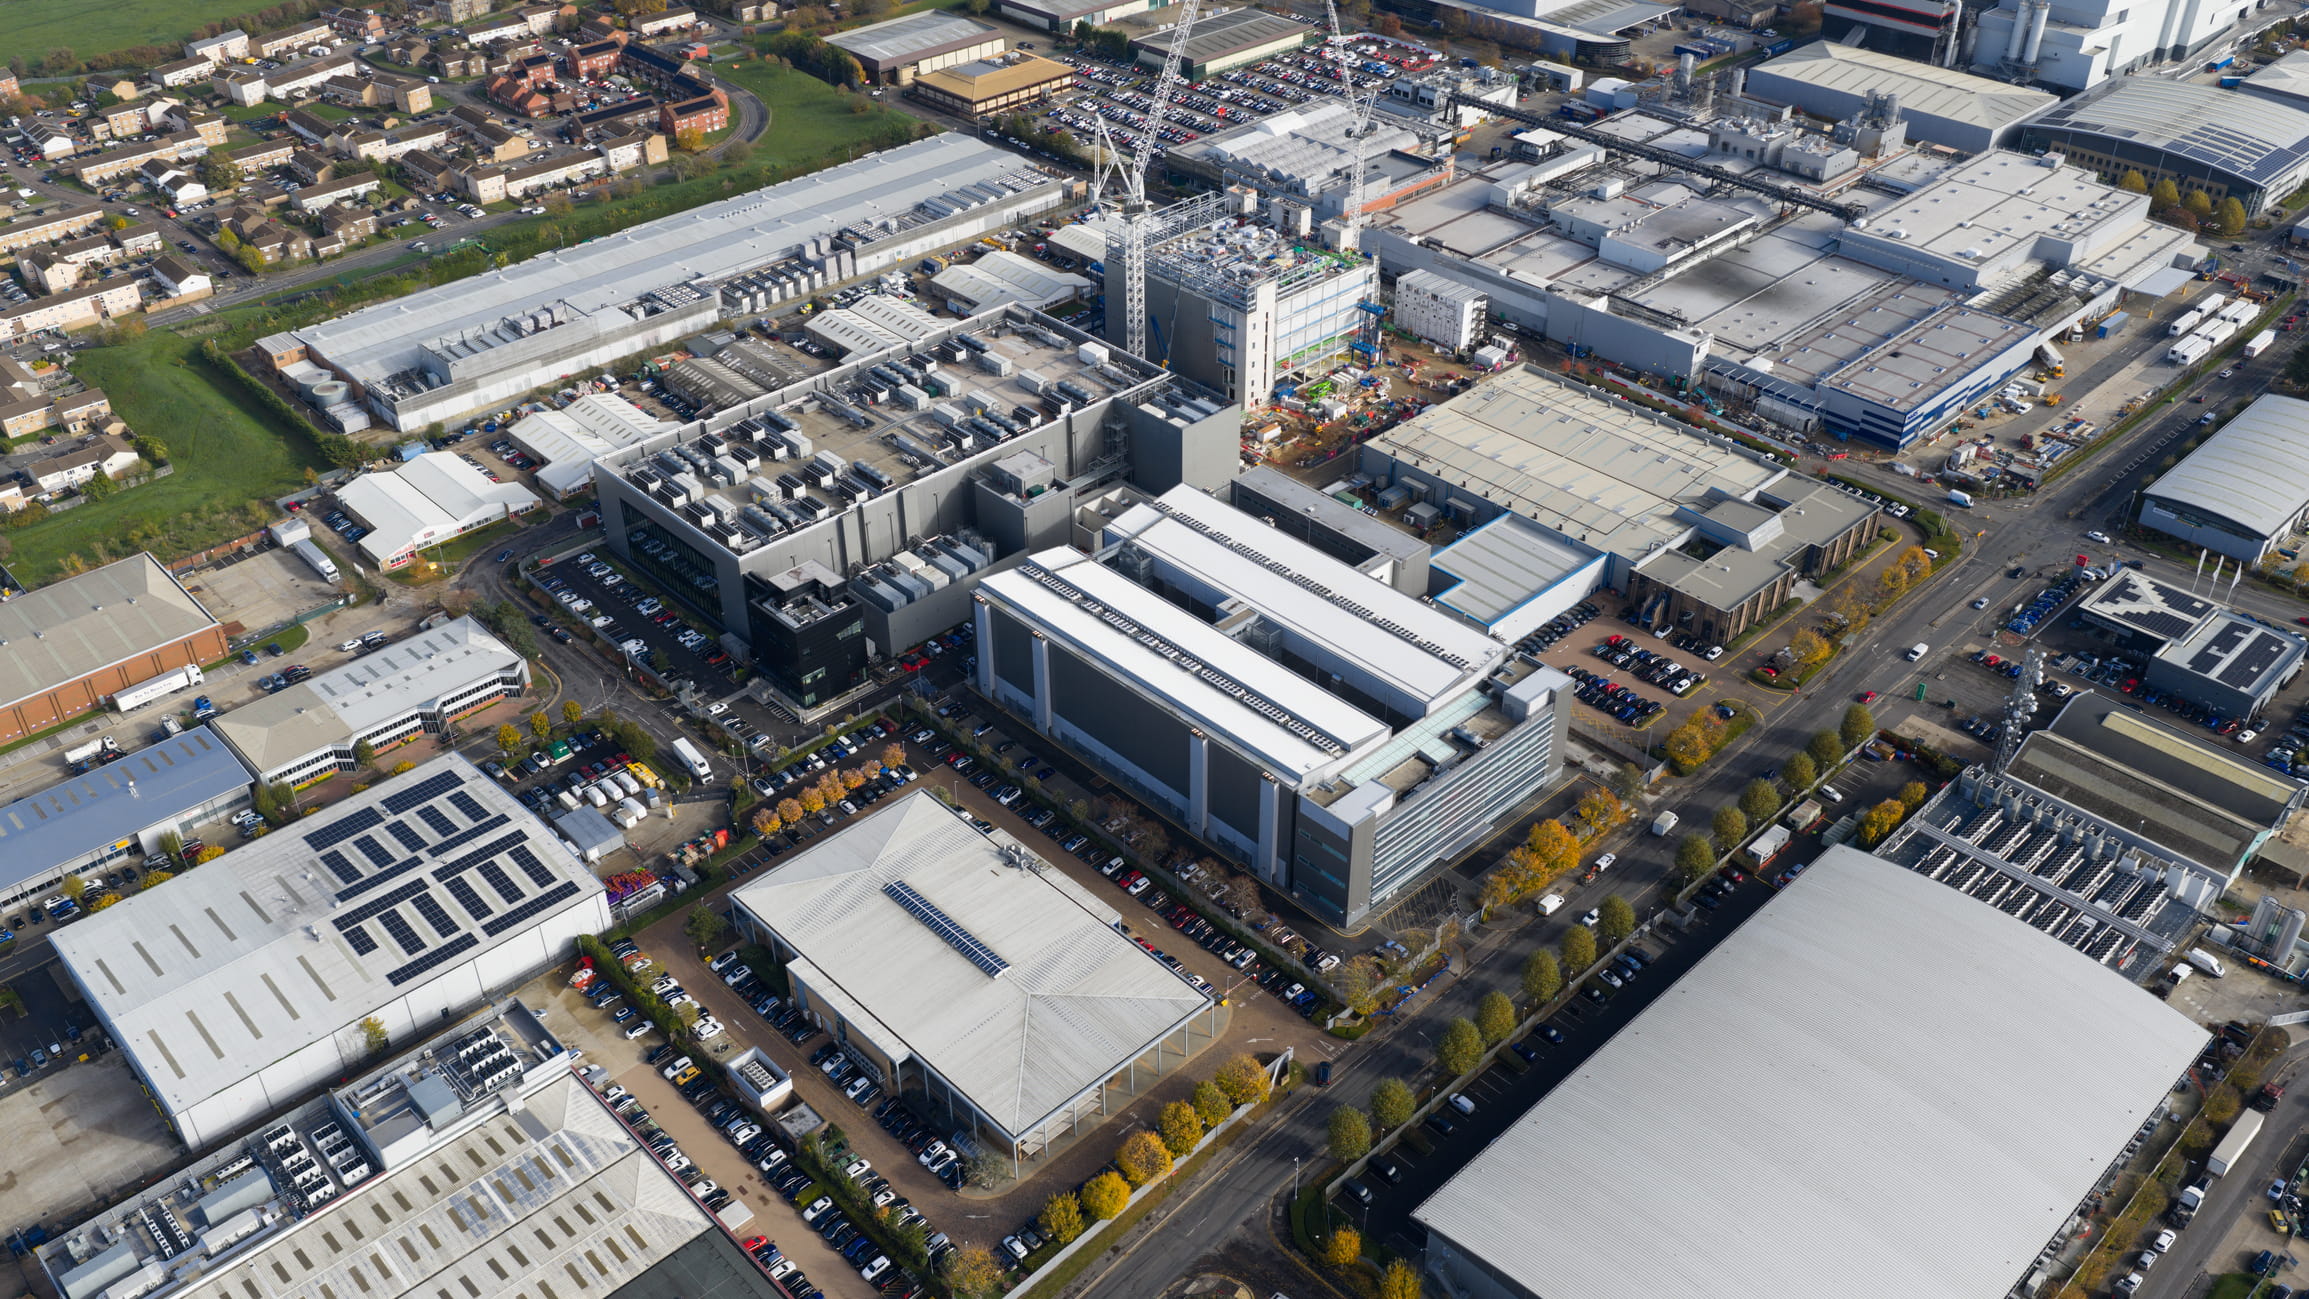
Missile and drone strikes on Middle East cloud data centers and cyber incidents that wiped servers have exposed how growing AI-driven workloads make data centers strategic, high-value targets whose disruption can cascade into economic and national security harm. The article urges companies and governments to treat data center resilience as critical infrastructure by hardening power, cooling, building management, remote access, and supply chains to withstand both kinetic and cyber attacks. #Handala #Stryker