A Virginia man, Sohaib Akhter, was convicted for deleting 96 government databases and stealing a password that led to unauthorized access to an email account. The case involved data tied to the EEOC and a Washington, D.C.-based company that serves more than 45 U.S. federal agencies. #SohaibAkhter #EEOC…
Category: Cyber Security News
Alan Bill, a key operator of the Kingdom Market dark web marketplace, was sentenced to more than 16 years in prison for helping run a platform that sold drugs, stolen financial data, fake IDs, counterfeit currency, and malware. The takedown involved coordinated action by U.S. and European law enforcement, with German…
General Motors agreed to pay $12.75 million to settle California allegations that it collected and sold millions of consumers’ driving data without consent through OnStar. The deal also requires GM to stop selling driving data for five years, delete retained data after 180 days without consent, and strengthen its privacy controls….

The webinar explains how “Patient Zero” incidents often begin with a single employee click and how AI-powered phishing makes these initial infections harder to detect. It also outlines how to contain an infected device quickly and recover before the breach spreads across the organization. #PatientZero #GenerativeAI #AIPhish #ZeroTrust…

Researchers uncovered 28 fraudulent Android apps on Google Play that claimed to provide call, SMS, and WhatsApp history for any phone number, but instead charged users for fake data and financial loss. The campaign, named CallPhantom, targeted Android users in India and the Asia-Pacific region and used deceptive developers, subscription traps,…

TCLBANKER is a newly identified Brazilian banking trojan that targets 59 banking, fintech, and cryptocurrency platforms while using advanced anti-analysis and environment-gating techniques to evade detection. It also spreads through hijacked WhatsApp Web sessions and Microsoft Outlook accounts, combining credential theft, remote control, and social engineering to expand its reach. #TCLBANKER…
Braintrust said hackers accessed an AWS account and may have exposed org-level AI provider API keys, prompting the company to advise customers to rotate their secrets immediately. The incident was discovered on May 4, affected at least one customer, and led to internal lockdowns, secret rotations, and an ongoing investigation. #Braintrust…

Poland’s Internal Security Agency (ABW) reported a sharp rise in attacks against industrial control systems and other OT infrastructure in 2024 and 2025, with intrusions aimed at disrupting critical services such as water supply. The report highlights breaches at several Polish water treatment facilities and names APT28, APT29, and UNC1151 as…

This week’s roundup covers urgent federal patching proposals, new malware and espionage operations, and notable law enforcement actions across banking, transit, and technology sectors. It also highlights threats tied to Cisco firewalls, Microsoft Phone Link, North Korea-linked campaigns, and the Drone industry. #CloudZ #Pheno #OperationSilentRotor #ScarCruft #BirdCall #PamDOORa #Firestarter #CISA #Cisco…
NVIDIA confirmed that GeForce NOW user information was exposed in a breach affecting only Armenia, caused by a compromise at a third-party regional partner, not NVIDIA’s own network. The incident exposed personal details such as names, emails, phone numbers, and dates of birth, while claims by a ShinyHunters-named actor appear to have come from an impersonator. #NVIDIA #GeForceNOW #GFNam #ShinyHunters
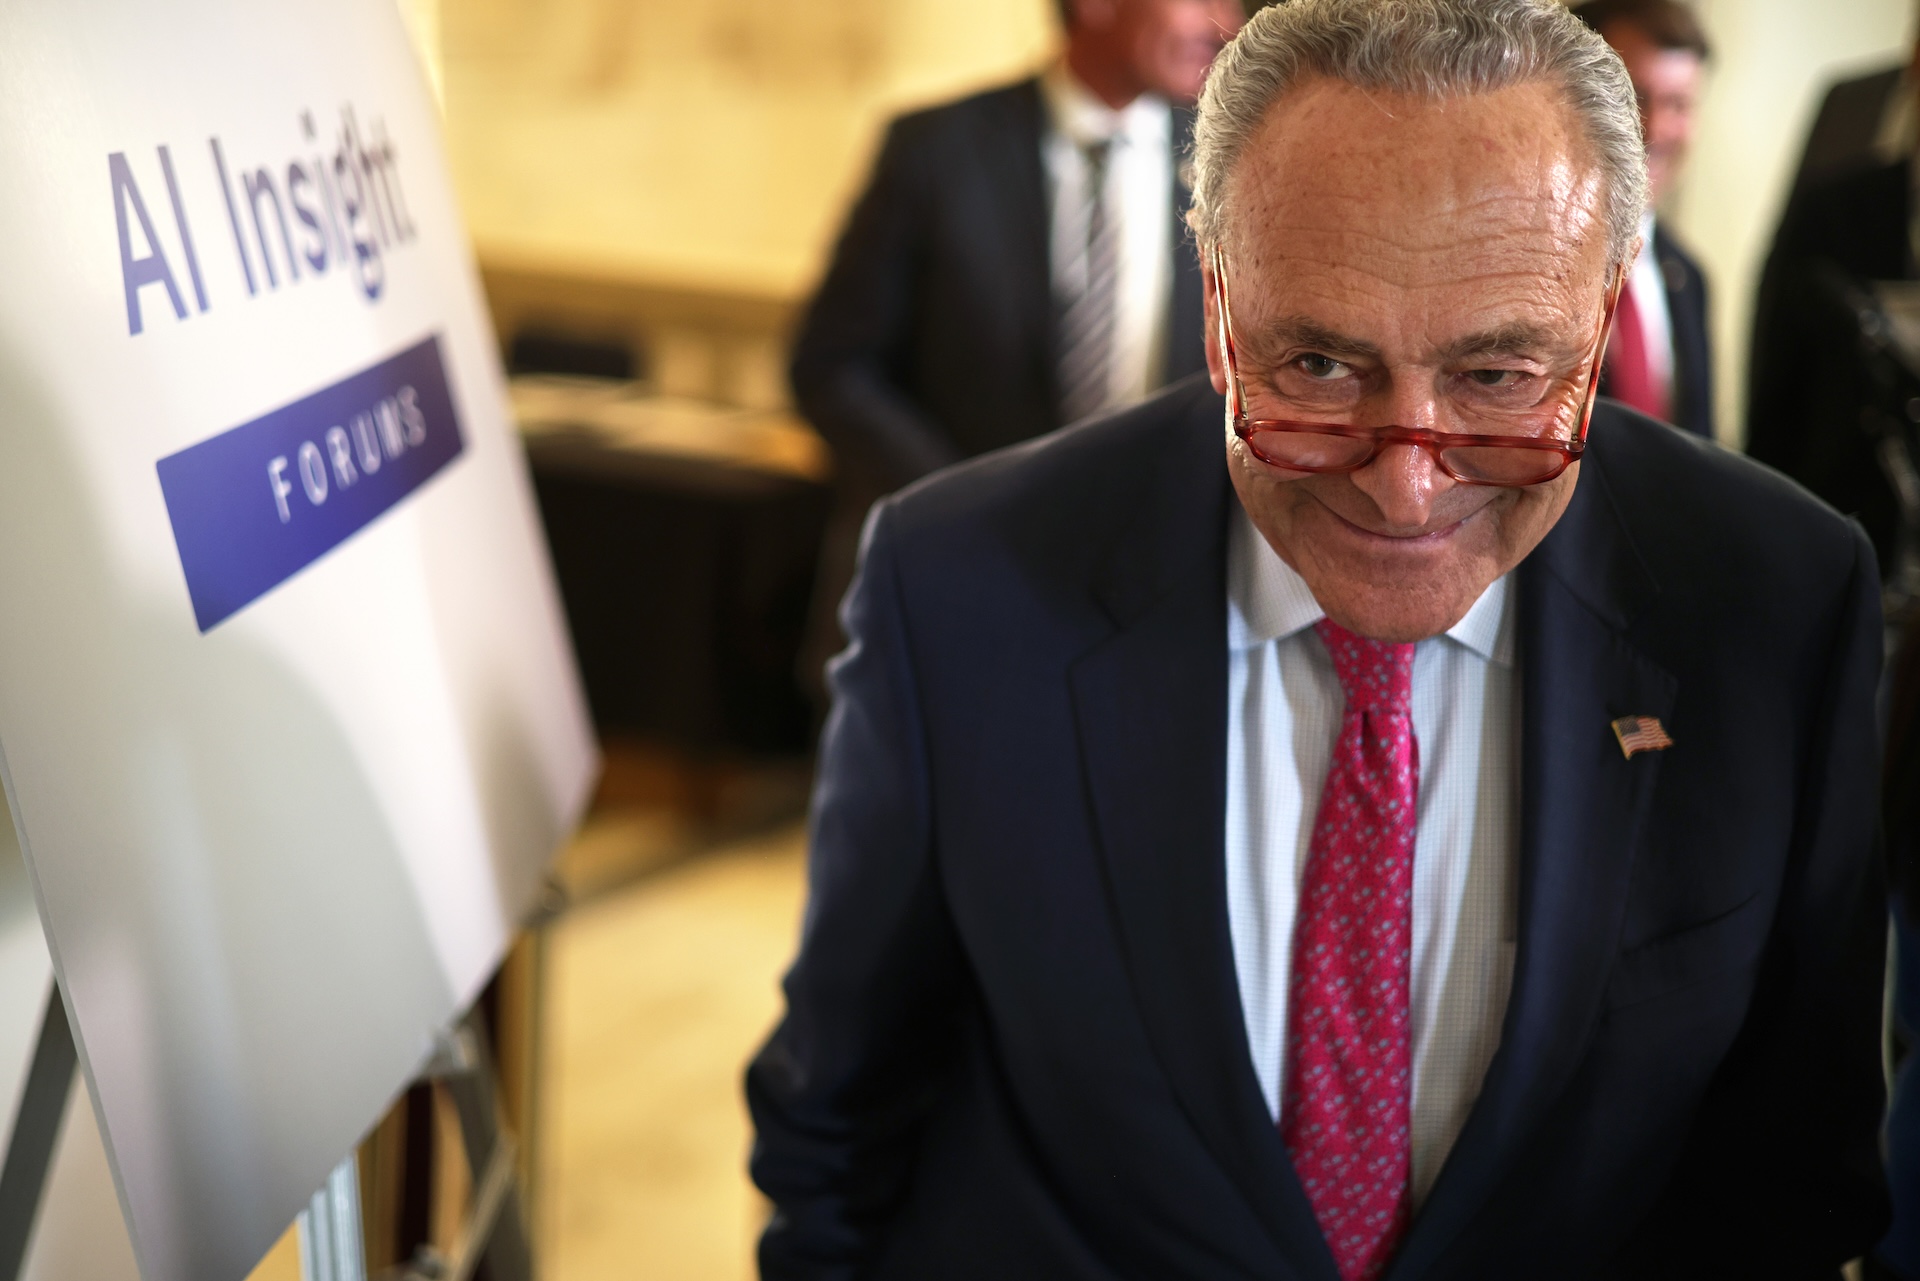
Senate Minority Leader Chuck Schumer urged the Department of Homeland Security to strengthen coordination with state, local, tribal and territorial governments against AI-enabled hacking threats. He warned that critical services such as hospitals, power grids, water systems, schools, elections, and emergency services could be exposed if defensive planning does not keep pace with frontier AI. #ChuckSchumer #DepartmentofHomelandSecurity #CISA
CISA has ordered U.S. federal agencies to patch an actively exploited zero-day in Ivanti Endpoint Manager Mobile (EPMM), tracked as CVE-2026-6973, within four days due to the risk of remote code execution on exposed systems. Ivanti says the issue affects only on-prem EPMM and has released fixed versions, while urging customers to review admin accounts and rotate credentials where needed. #CVE-2026-6973 #IvantiEPMM #CISA
RansomHouse claimed responsibility for the attack on Trellix’s source code repository and posted screenshots as supposed proof of access to the company’s systems. Trellix says it is investigating the breach, has notified law enforcement, and has found no evidence that its source code release or distribution process was affected. #RansomHouse #Trellix
The article argues that rising security spend and SOC headcount are not fixing the real problem: an outdated operating model that leaves too many alerts waiting for human investigation. It highlights how Prophet Security’s Prophet AI can reduce investigation time, cut SIEM costs, and shift analysts toward higher-value work while noting where humans must still lead, such as insider threat cases and novel TTPs. #ProphetSecurity #ProphetAI #JBPoindexterCo #Cabinetworks #GoogleMandiant #MTrends #CrowdStrike #IBM
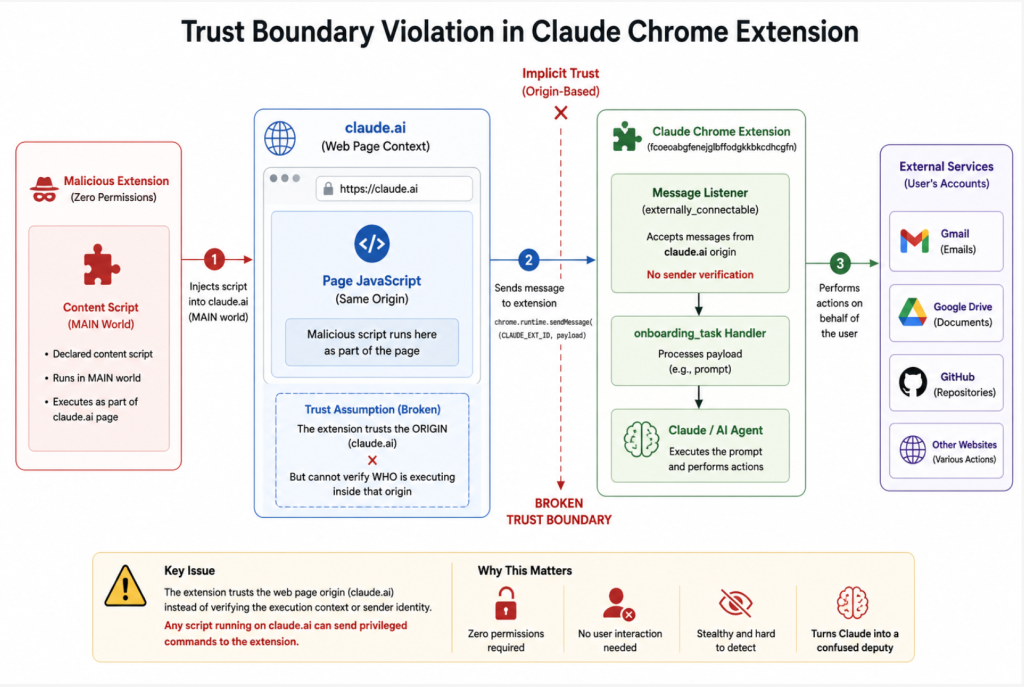
LayerX found a flaw in Anthropic’s Claude Chrome extension that lets other extensions inject hidden instructions and take control of the AI agent. The issue enabled unauthorized access to Google Drive, Gmail, and GitHub data, and LayerX says the partial fix still left some takeover paths open. #Anthropic #Claude #LayerX #Chrome #GoogleDrive #Gmail #GitHub