Hackers are exploiting CVE-2026-8181 in the Burst Statistics WordPress plugin to bypass authentication and gain admin-level access on affected sites. Wordfence says the flaw has already been targeted at scale, with more than 7,400 blocked attacks and many sites still exposed if they have not upgraded to version 3.4.2. #BurstStatistics #CVE-2026-8181 #Wordfence #WordPress
Category: Cyber Security News
TeamPCP is threatening to leak nearly 450 Mistral AI repositories after claiming to have stolen internal source code and data from a compromised codebase management system. Mistral AI says the incident stemmed from the TanStack supply-chain attack, but that its core repositories, hosted services, and research environments were not compromised. #TeamPCP #MistralAI #TanStack #MiniShaiHulud
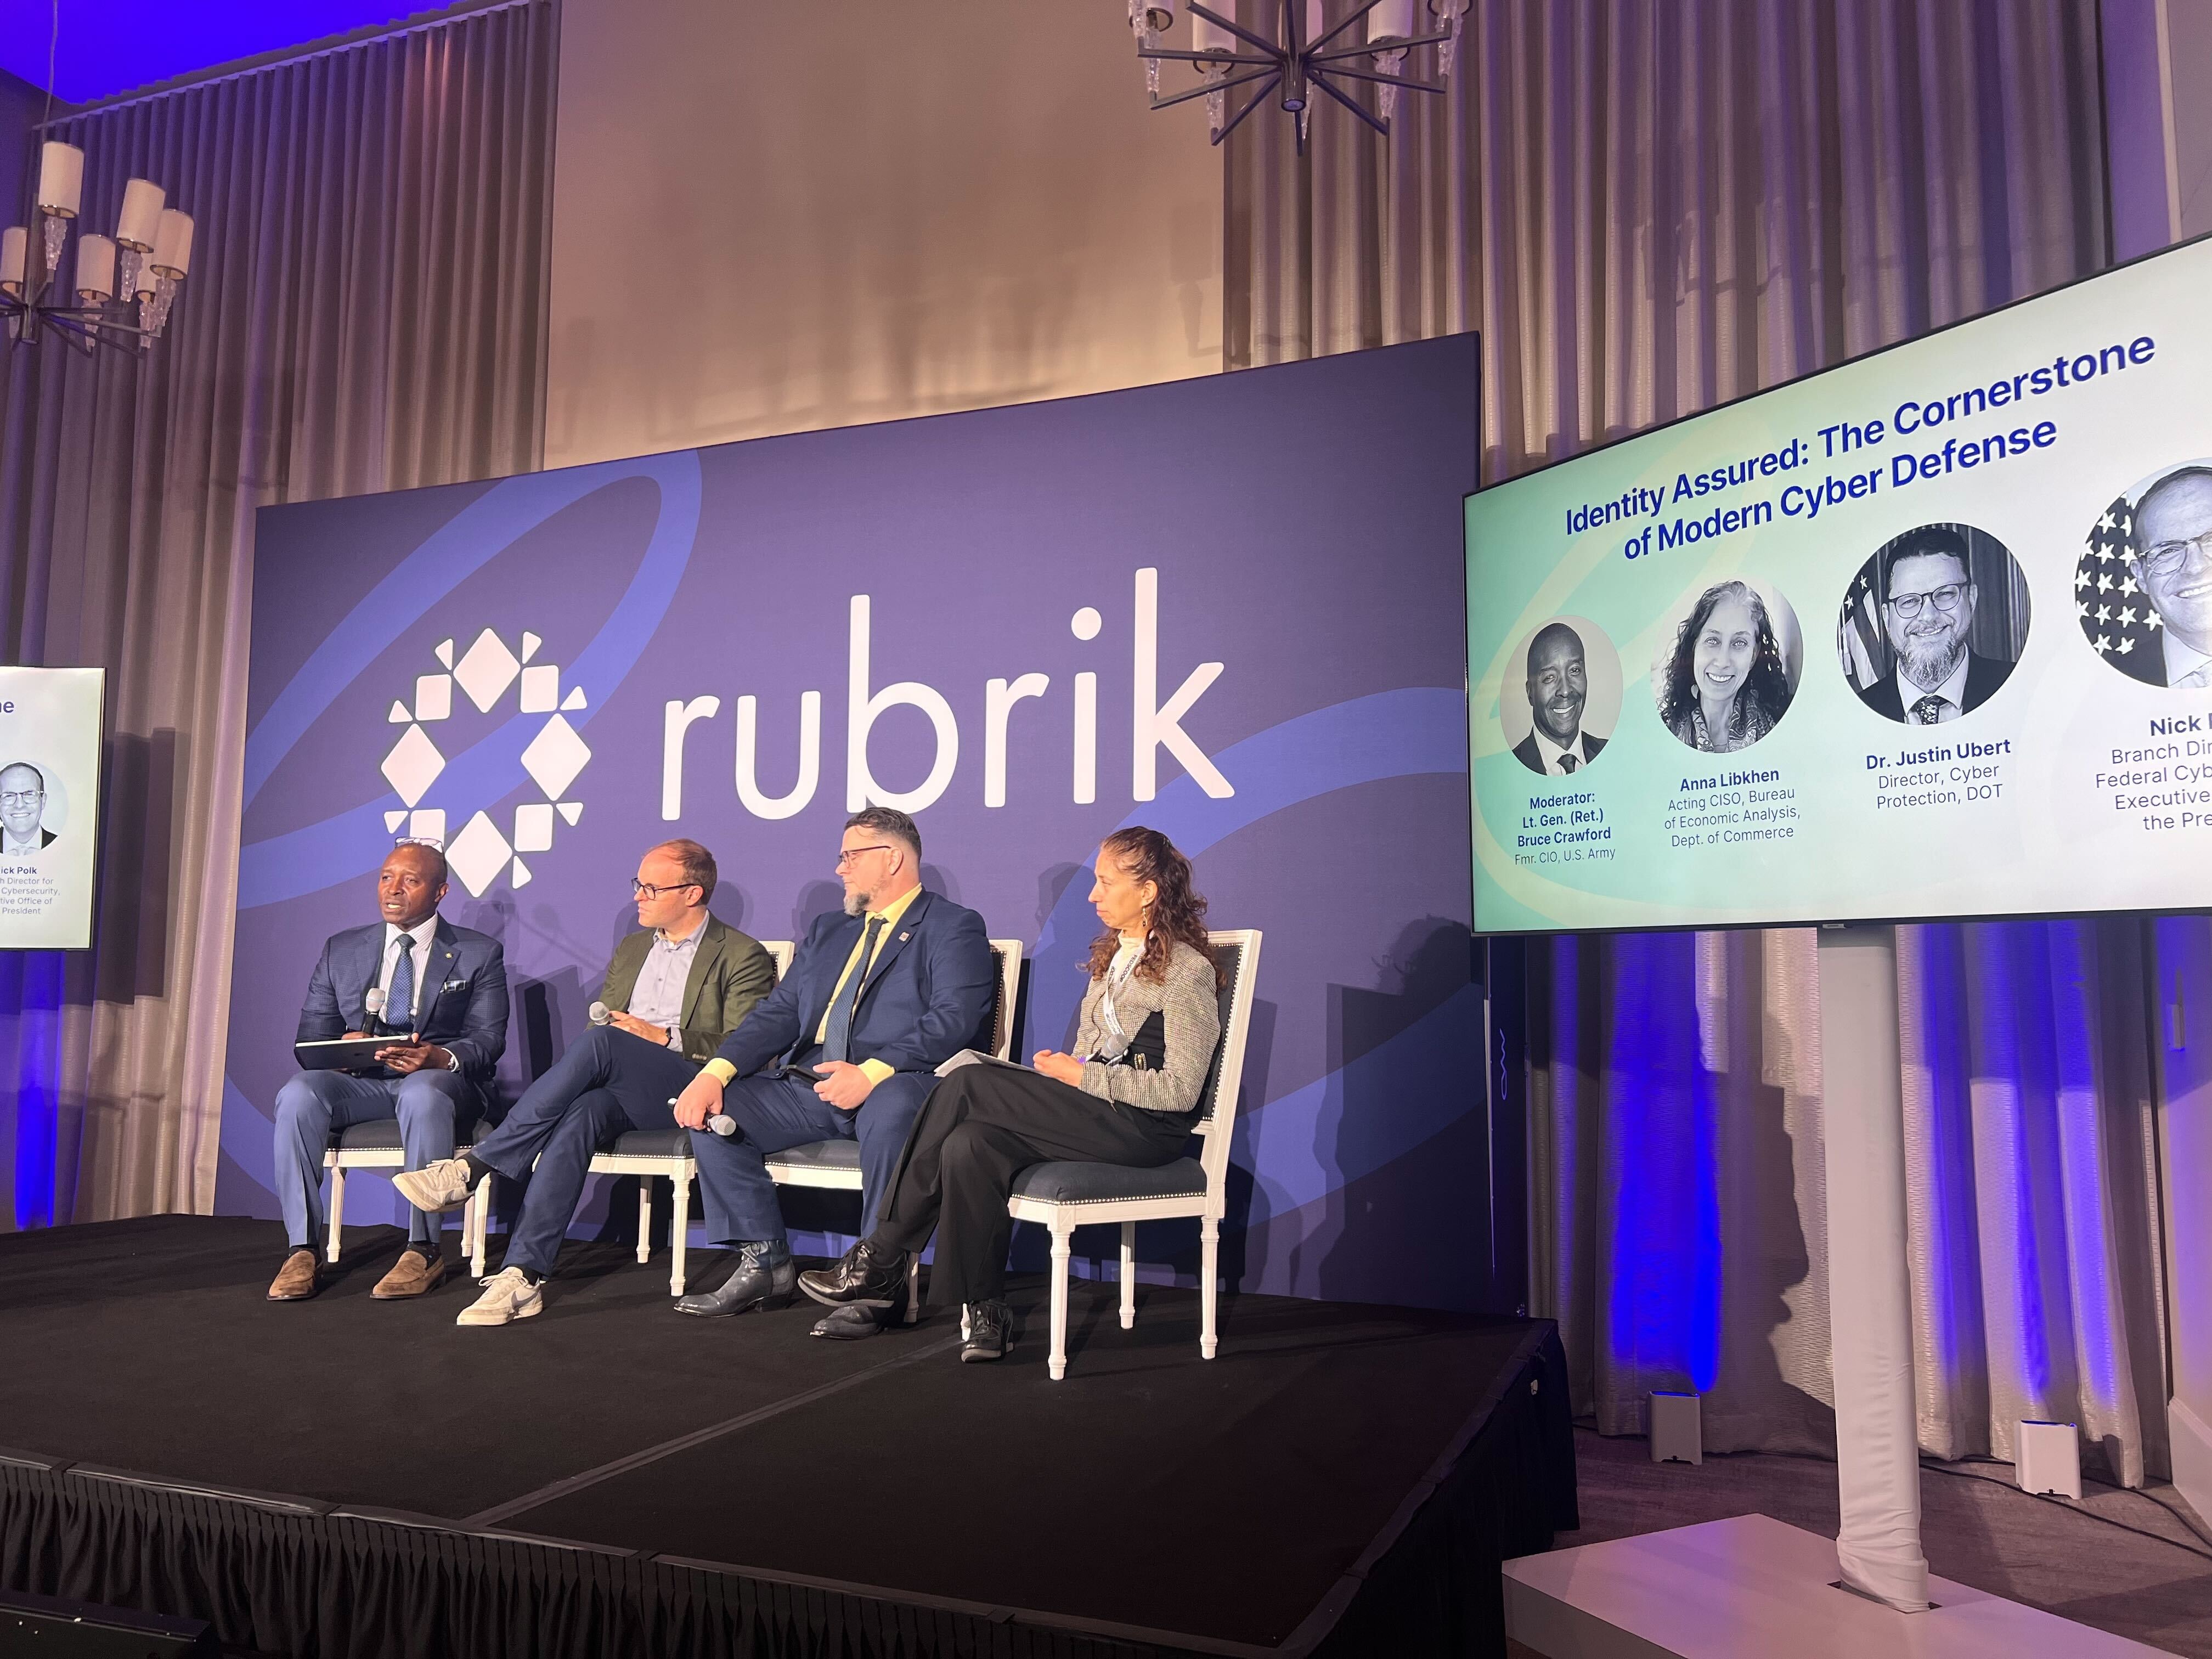
AI is pushing federal agencies to place greater emphasis on identity security, since attackers still need trusted access to networks before they can exploit systems. Officials warned that AI tools can speed up attacks, hide malicious behavior, and turn automated agents into dangerous insider threats. #NickPolk #JustinUbert #AnnaLibkhen #Anthropic #ClaudeSonnet #Opus4 #ChatGPT5 #DepartmentOfTransportation #DepartmentOfCommerce #BureauOfEconomicAnalysis
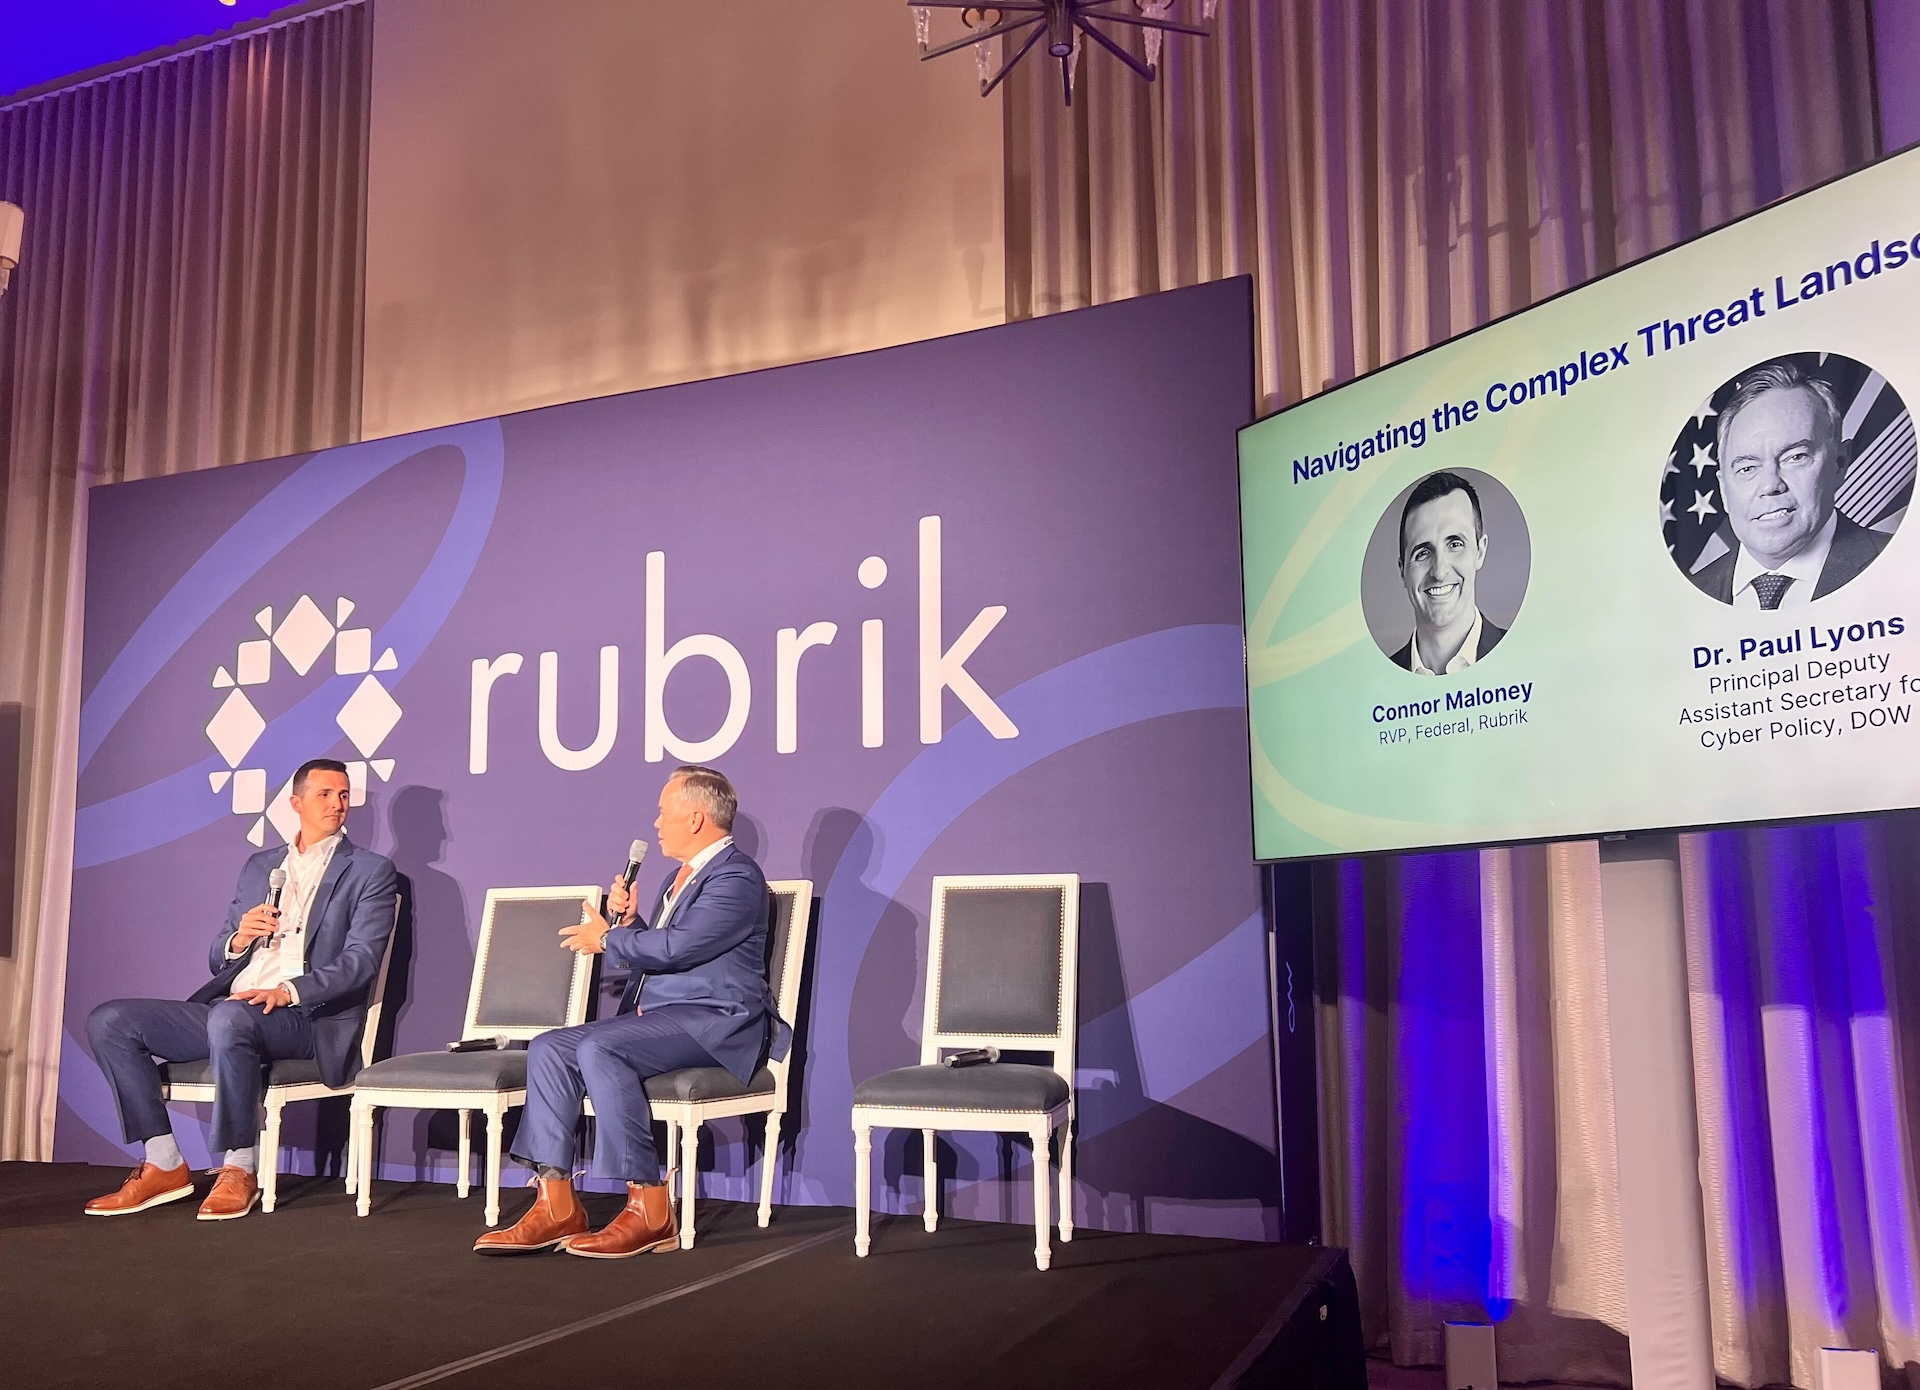
Advanced AI models like Mythos are being described by a senior Defense Department official as a watershed moment that will fundamentally change warfare and cyber operations. The Pentagon sees both opportunity and risk in using these systems for cyber defense, vulnerability hunting, and broader military strategy, while also raising supply chain concerns involving Anthropic and Claude. #Mythos #Anthropic #Claude #PaulLyons #DepartmentofWar
Cisco warned that CVE-2026-20182, a critical authentication bypass in Catalyst SD-WAN Controller and Manager, was actively exploited in zero-day attacks to gain administrative access. The flaw can let attackers register rogue peers, manipulate SD-WAN network configuration, and deepen access within affected environments. #CVE-2026-20182 #Cisco #CatalystSDWAN #CISA #Rapid7 #UAT-8616

Ghostwriter has launched new spear-phishing attacks against Ukrainian government organizations, using malicious PDFs, geofencing, and a JavaScript version of PicassoLoader to deploy Cobalt Strike. The wider report also highlights Gamaredon’s Ukraine-focused campaigns, BO Team-linked operations against Russian organizations, and Hive0117’s phishing activity for financial theft. #Ghostwriter #PicassoLoader #CobaltStrike #Gamaredon #BOTeam #HeadMare…

This roundup highlights a wave of active threats, from Palo Alto Networks PAN-OS exploitation and Langflow RCE abuse to phishing-driven intrusions, data exposure, and supply chain abuse. Attackers are increasingly blending trusted tools, fake support channels, and open-source components to steal credentials, deploy payloads, and maintain covert access. #PANOS #CVE20260300 #OperationGriefLure…
Mythos Preview appears to be exceptionally effective at finding software vulnerabilities, with XBOW confirming Anthropic’s claim that it outperforms other models in source code audits. However, its performance is more mixed in judgment, exploit validation, and cost efficiency, where it can be overly literal and is not always best-in-class. #Anthropic #MythosPreview…
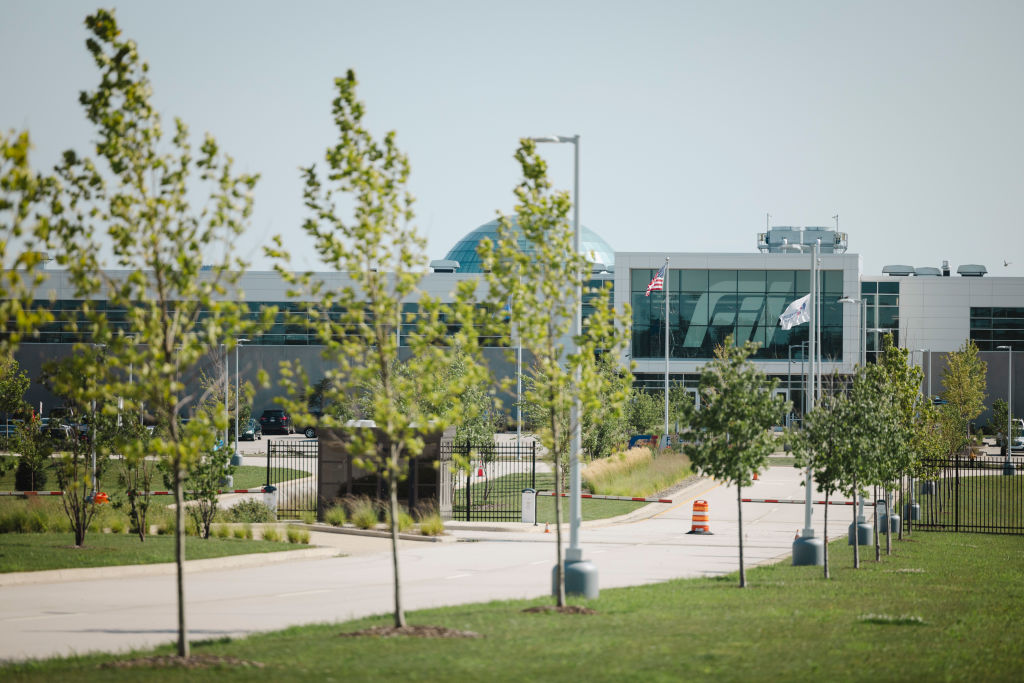
Foxconn is recovering from a cyberattack that disrupted some of its North American factories, while the Nitrogen ransomware group claims it stole 8 terabytes of data from the company. Nitrogen says the alleged theft includes confidential Intel, Apple, Google, Dell, and Nvidia materials, but Foxconn has only confirmed the breach and said affected factories are resuming normal production. #Foxconn #Nitrogen #Apple #Intel #Google #Dell #Nvidia
Cybercriminals are adapting the ransomware playbook to steal freight, using phishing, email compromise, and fraudulent carrier identities to reroute cargo into criminal hands. NMFTA says the transportation sector faces rising cyber-enabled cargo crime, and urges stronger controls, better reporting, and industry-focused guidance through its framework and resources. #NMFTA #VeriskCargoNet #FBIIC3 #USDOT #FMCSA #FreightFraudPreventionHub
An 18-year-old heap buffer overflow in NGINX, tracked as CVE-2026-42945, can cause denial of service and may allow remote code execution under specific conditions. DepthFirst AI also uncovered three additional memory corruption flaws in NGINX components, while F5 has released fixes for affected NGINX and related products. #CVE-2026-42945 #NGINX #F5 #DepthFirstAI
Linux distributions are warning users about Fragnesia, a new kernel flaw tracked as CVE-2026-46300 that can let a local attacker escalate privileges to root through the XFRM ESP-in-TCP subsystem. Microsoft says the issue is similar to Dirty Frag and Copy Fail, urges immediate patching, and notes that while a PoC exists,…
Data center security has long been trapped between protection and performance, but DPU-based security moves defenses off the host CPU and onto dedicated silicon. This approach improves visibility across VMs and containers, blocks hypervisor-level blind spots, and helps prevent attacks like the VMware ESXi zero-days and the ESXiArgs campaign without slowing…
KongTuke has shifted to Microsoft Teams to carry out social engineering attacks, tricking employees into running a malicious PowerShell command that installs ModeloRAT and can establish persistent access in under five minutes. ReliaQuest says the campaign uses rotating Microsoft 365 tenants, Unicode display-name tricks, and stronger persistence features, making it harder to block and remove. #KongTuke #MicrosoftTeams #ModeloRAT #ReliaQuest
Linux distros are deploying patches for Fragnasia (CVE-2026-46300), a high-severity Linux kernel flaw in the XFRM ESP-in-TCP subsystem that can let unprivileged local attackers gain root privileges. The issue is linked to the Dirty Frag vulnerability class and comes as administrators are also dealing with the actively exploited Copy Fail flaw and earlier root-level bugs like Pack2TheRoot. #Fragnasia #CVE-2026-46300 #DirtyFrag #CopyFail #Pack2TheRoot #XFRM