
Major tech firms including Snap, Roblox, and Meta have pledged new safety changes for children in the UK after pressure from Ofcom, with measures focused on limiting adult contact, improving age checks, and reducing grooming risks. Ofcom said TikTok and YouTube did not commit to significant changes and warned it will…
Category: Cyber Security News
CISA has introduced a new nomination form that lets researchers, vendors, and industry partners outside the U.S. government report vulnerabilities for possible inclusion in the Known Exploited Vulnerabilities catalog. The move is intended to speed up validation, disclosure, and patching of actively exploited bugs, including those tracked in the KEV, as…
Two members of Congress warned that recent cuts have weakened CISA at a time when foreign adversaries, especially China, are probing U.S. civilian networks and critical infrastructure. They argued that restoring the agency’s staffing, funding, and partnerships is essential to helping utilities, local governments, and smaller organizations defend themselves and recover from intrusions. #CISA #SaltTyphoon #China #DonBacon #JamesWalkinshaw
Authorities arrested Canadian national Jacob Butler, accused of helping run the Kimwolf DDoS botnet and using it to power thousands of attacks against government and other targets. The case links Kimwolf to the Aisuru botnet family, major infrastructure seizures, and renewed botnet activity despite prior takedowns. #Kimwolf #Aisuru #JacobButler #DepartmentofDefense

Microsoft has disclosed that CVE-2026-41091 and CVE-2026-45498 in Defender are being actively exploited in the wild, with the former allowing local privilege escalation to SYSTEM and the latter causing denial of service. CISA has added both flaws to its KEV catalog, while Microsoft says the issues are fixed in Defender Antimalware…

This week’s cybersecurity roundup shows attackers increasingly abusing trusted tools, cloud features, and legitimate services instead of forcing obvious break-ins. From Pwn2Own Berlin 2026 zero-days and Composer token leakage to Storm-2949 cloud abuse, Gunra ransomware, OrBit rootkit activity, and AI-driven intrusions, the pattern is faster, stealthier, and built around normal workflows….

Researchers uncovered Showboat, a modular Linux post-exploitation framework used since at least mid-2022 in attacks against a telecommunications provider in the Middle East and related victims in Afghanistan, Azerbaijan, the U.S., and Ukraine. The activity is linked to China-aligned clusters such as Calypso, alongside shared tooling and infrastructure that suggest a…
Google accidentally exposed details of an unfixed Chromium flaw that can keep JavaScript running after the browser is closed, enabling remote code execution on affected devices. The issue, reported by researcher Lyra Rebane, impacts Chromium-based browsers like Google Chrome and Microsoft Edge and could be used to build a silent botnet from a single malicious website visit. #Chromium #GoogleChrome #MicrosoftEdge #LyraRebane

European authorities shut down First VPN and arrested its alleged administrator in a multinational operation led by France and the Netherlands, with support from Europol and Eurojust. Investigators say the service was widely used by cybercriminals to hide infrastructure and identities in cases involving data theft, fraud, and ransomware attacks. #FirstVPN #Europol #Eurojust
CISA acting director Nick Andersen warned that protecting the open-source software underpinning modern infrastructure will require difficult security choices as attacks accelerate. He cited incidents like the malicious axios updates and the broader activity of TeamPCP, saying traditional vulnerability management is no longer enough. #CISA #NickAndersen #axios #TeamPCP

President Donald Trump delayed an executive order that would have created a 90-day testing and vetting regime for frontier AI models before public release, citing concerns about weakening U.S. competitiveness with China. The draft plan would have involved the NSA, Treasury, CISA, and NIST in evaluating AI models and sharing information with critical infrastructure defenders, amid growing concerns about military, hacking, and cybersecurity misuse of advanced AI. #OpenAI #Anthropic #NSA #CISA #NIST
Apple said it blocked over $11 billion in fraudulent App Store transactions across the last six years, including more than $2.2 billion in 2025 alone. The company also rejected millions of risky app submissions and account creations while using human review and machine learning to stop fraud, stolen cards, and deceptive apps. #AppStore #Apple
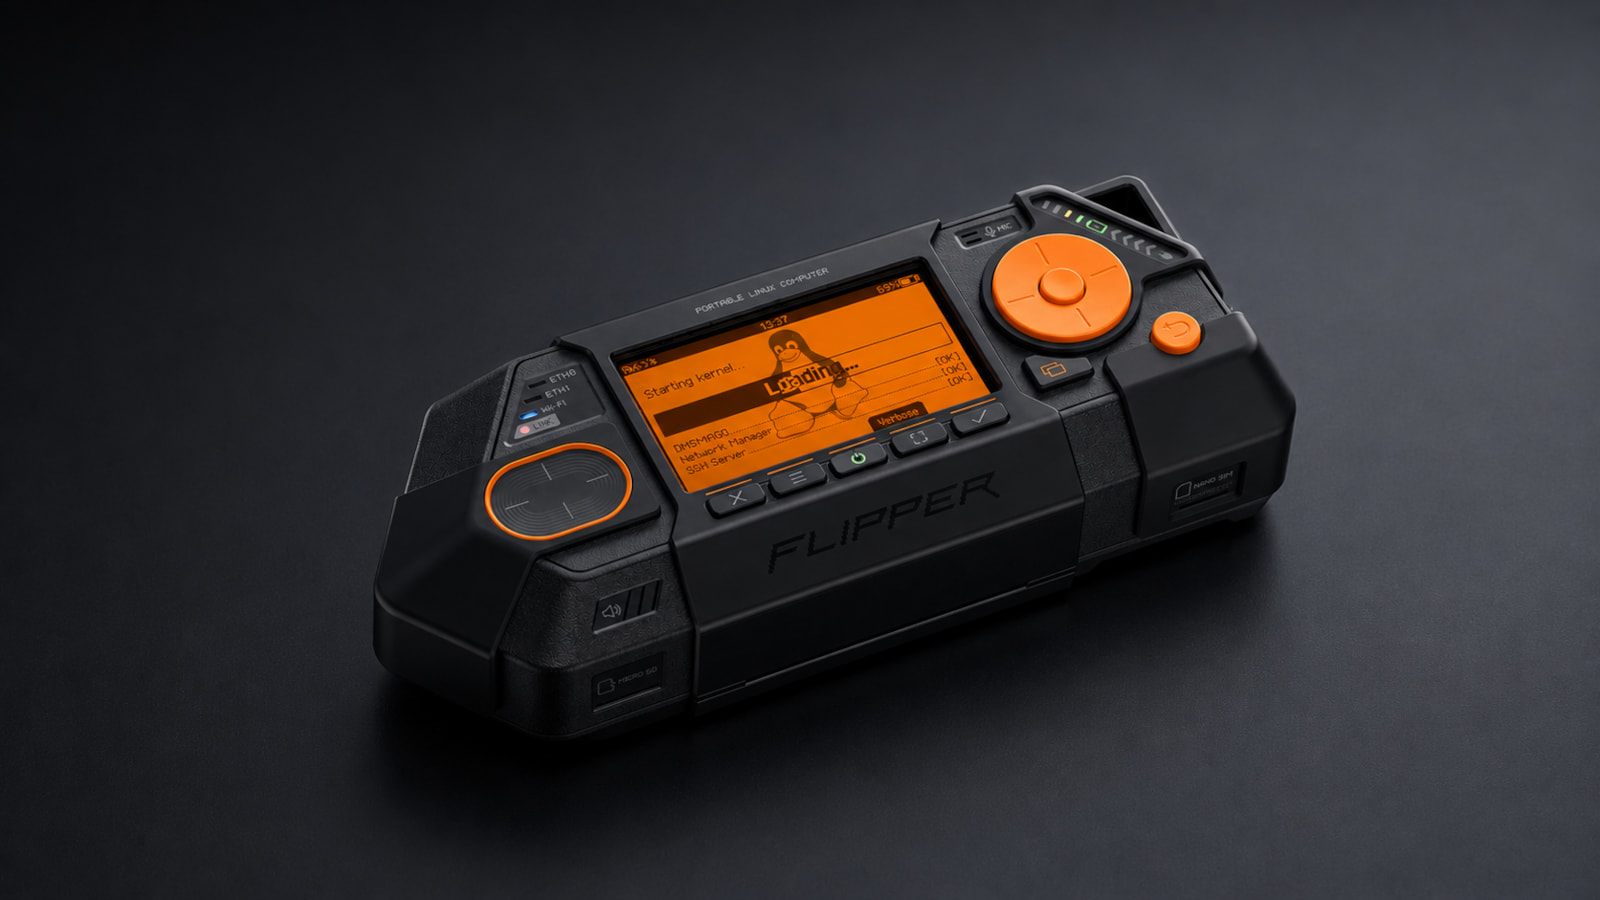
Flipper Devices is developing Flipper One, an open Linux-based platform for connected devices that goes beyond the Flipper Zero’s offline radio-focused pentesting features. The project aims to support hardware experimentation, SDR analysis, and modular networking use cases, but it is still in active development and faces major technical and software support challenges.
#FlipperOne #FlipperDevices #FlipperZero #RK3576 #FlipCTL
First VPN, a privacy-focused VPN service heavily used in ransomware and data theft operations, has been taken offline in a coordinated international law enforcement action. Investigators seized its servers and domains, arrested the administrator, and uncovered data linking thousands of users to cybercrime cases worldwide. #FirstVPN #Europol #Eurojust #1vpnscom #1vpnsnet #1vpnsorg
Cisco has released fixes for CVE-2026-20223, a maximum-severity Secure Workload flaw that could let unauthenticated attackers obtain Site Admin privileges through crafted REST API requests. The issue can expose sensitive data and allow configuration changes across tenant boundaries, while Cisco says no workarounds exist and there is no evidence of in-the-wild exploitation so far. #CiscoSecureWorkload #CVE-2026-20223 #Cisco #PSIRT