Daily Recap, Ghost CMS (CVE-2026-26980) flaws were actively exploited in a large-scale ClickFix campaign to compromise 700+ websites via malicious redirects and payload delivery, while the FBI warned that Kali365 is used to phish Microsoft 365 accounts. The recap also covered healthcare data breaches at the Oncology Institute and Radiology Associates of Richmond (266,000 affected), supply-chain risks involving poisoned Laravel-Lang packages, and broader threat activity including YellowKey and GreenPlasma along with APT activity from Screening Serpens, Nimbus Manticore, and Void Dokkaebi. #GhostCMS #CVE-2026-26980 #ClickFix #Kali365 #Microsoft365 #OncologyInstitute #RadiologyAssociatesofRichmond #Laravel-Lang #AnthropicMythos #Mythos #TrapDoor #MiniShaiHulud #JDownloader #r77 #GeminiCLI #ClaudeCode #YellowKey #GreenPlasma #ScreeningSerpens #NimbusManticore #VoidDokkaebi #CoinbaseCartel #TheGentlemen
Category: Cyber Security News

Threat actors are exploiting CVE-2026-26980 in Ghost CMS to steal admin API keys, inject malicious JavaScript, and fuel large-scale ClickFix attacks across more than 700 compromised websites. The campaign uses cloaking, fake CAPTCHA pages, and multiple loaders to deliver payloads and eventually drop Windows malware, including a modified Grape desktop client…
The Oncology Institute has confirmed that a previously disclosed cybersecurity incident affected patient information after a third-party software vendor detected unauthorized access to its systems. The breach appears to be part of a broader incident impacting multiple healthcare organizations, with TriZetto Provider Solutions and Kroll linked to the disclosures. #TheOncologyInstitute #TriZettoProviderSolutions…
A patched SQL injection vulnerability in the Ghost CMS, tracked as CVE-2026-26980, has been mass-exploited to compromise more than 700 websites. Attackers used stolen Admin API keys to inject malicious JavaScript loaders for ClickFix attacks, affecting sites linked to DuckDuckGo, Harvard University, and Oxford University. #Ghost #CVE-2026-26980 #DuckDuckGo #HarvardUniversity #OxfordUniversity #ClickFix…
The FBI is warning that the Kali365 phishing-as-a-service platform is helping attackers hijack Microsoft 365 and Entra accounts by abusing OAuth device code authentication to steal session tokens and bypass MFA. Researchers say the service is widely used in campaigns that capture browser sessions and tokens, giving threat actors access to mailboxes, cloud apps, and victim environments. #Kali365 #Microsoft365 #MicrosoftEntra #ShinyHunters #ArcticWolf
Four Composer packages maintained by Laravel-Lang were poisoned after attackers rewrote Git tags to point to malicious code in a supply chain attack. The payload installed a PHP credential stealer that targeted cloud secrets, SSH keys, browser data, VPN configs, and other sensitive credentials across multiple operating systems. #LaravelLang #flipboxstudioinfo #laravel-lang/lang…

Anthropic says its Claude Mythos model has uncovered more than 23,000 potential vulnerabilities across over 1,000 open source software projects, with 1,726 already confirmed and over 1,000 rated high or critical severity. The company says more findings are under review and that organizations like Mozilla and Palo Alto Networks have also…
Radiology Associates of Richmond (RAR) disclosed a data breach that affected the protected health information of 266,183 individuals after hackers accessed its internal systems on or about July 25, 2025. The investigation later found that files may have included names, Social Security numbers, government-issued ID numbers, financial data, and medical and…

Cybersecurity Threat Research ‘Weekly’ Recap. Attackers continued to exploit the software supply chain and developer ecosystems, including crypto-stealers like #TrapDoor and#Mini Shai-Hulud-style install payloads, typosquatted modules with DNS backdoors, and trojanized JDownloader deliverables that included the #r77 rootkit bot. The recap also covers AI- and SEO-lure campaigns impersonating #Gemini CLI and #Claude Code, newly disclosed Windows zero-days #YellowKey and #GreenPlasma, and regional APT activity from #Screening Serpens, #Nimbus Manticore, #Void Dokkaebi, plus continuing crime waves involving #CoinbaseCartel and #The Gentlemen, alongside infrastructure abuse tracked through #VBCloud and #EchoCreep.
#TrapDoor #Mini Shai-Hulud #Coruna #JDownloader #r77 #Gemini CLI #Claude Code #YellowKey #GreenPlasma #LummaStealer #PurpleFox #ScreenConnect #LogMeIn Rescue #Screening Serpens #Nimbus Manticore #Cloud Atlas #VBCloud #PowerShower #RevSocks #Webworm #EchoCreep #GraphWorm #UNG0002 #Cobalt Strike #InvisibleFerret #BeaverTail #CoinbaseCartel #The Gentlemen #ShinyHunters #Andariel #Agent Tesla #ValleyRAT #Banana RAT #Kubernetes #CVE-2021-25740
XLab discovered a large-scale campaign exploiting CVE-2026-26980 in Ghost CMS to steal admin API keys and inject malicious JavaScript that drives ClickFix attack flows. The activity has affected more than 700 domains, including sites linked to Harvard University, Oxford, Auburn University, and DuckDuckGo, and leveraged payloads such as UtilifySetup.exe. #GhostCMS #CVE-2026-26980 #ClickFix #UtilifySetup.exe #HarvardUniversity #OxfordUniversity #AuburnUniversity #DuckDuckGo

Daily Recap, Exploited vulnerabilities and zero-days dominated the news: LiteSpeed cPanel Plugin CVE-2026-48172 is abused for root access, Drupal core SQL injection issues are being actively exploited and added to CISA KEV, and Trend Micro warned that an Apex One zero-day is in use in the wild. Phishing activity also accelerated with the FBI flagging the Kali365 phishing-as-a-service kit targeting Microsoft 365 tokens, while Ghostwriter used Prometheus to target Ukraine government entities and authorities pursued infrastructure actions including a global VPN service dismantling linked to 25 ransomware groups. #CVE-2026-48172 #LiteSpeed #cPanel #root #Drupal #CISAKEV #DrupalSQLi #ApexOne #Kali365 #Microsoft365 #FBI #Ghostwriter #Prometheus #Ukraine #VPN #Netherlands #Webworm #Discord #MicrosoftGraph
A supply chain attack against Laravel Lang localization packages abused GitHub tags and Composer distribution to deliver malicious releases that installed a credential-stealing payload. The campaign used a dropper from flipboxstudio[.]info to deploy the DebugElevator infostealer, targeting browser data, cloud secrets, Git credentials, and other sensitive credentials. #LaravelLang #DebugElevator #flipboxstudio
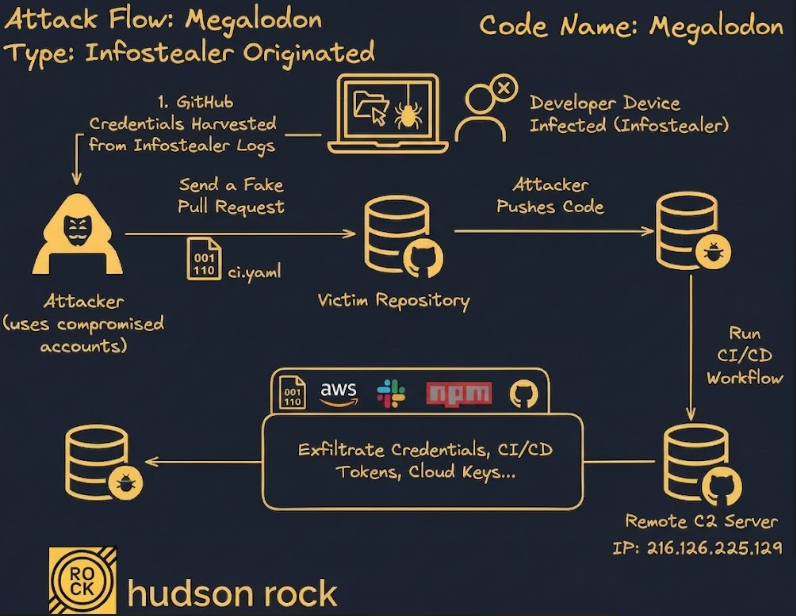
Megalodon is a large automated supply chain attack that infected over 5,000 GitHub repositories by abusing GitHub Actions workflows to steal secrets such as AWS keys, GCP tokens, SSH private keys, and GitHub OIDC tokens. Hudson Rock and other researchers traced the campaign to infostealer-compromised accounts and linked the spread to the open-sourced Shai Hulud framework from TeamPCP. #Megalodon #GitHubActions #ShaiHulud #TeamPCP #HudsonRock

Anthropic says Project Glasswing has uncovered more than 10,000 high- or critical-severity vulnerabilities in widely used software, including a critical flaw in WolfSSL that could enable certificate forgery. The initiative also helped stop a fraudulent $1.5 million wire transfer and is pushing defenders to speed up patching and harden systems. #ProjectGlasswing…

A coordinated supply chain attack has affected eight Packagist packages by hiding malicious code in package.json instead of composer.json, allowing it to evade PHP-focused review. The payload attempts to download and run a Linux binary from GitHub Releases during install or build workflows, with traces found across hundreds of GitHub files….