California Attorney General Rob Bonta sued 23andMe, now Chrome Holding Co., over its failure to protect sensitive genetic and personal data in a 2023 breach that exposed information from nearly 7 million customers. The complaint says the company failed to stop credential-stuffing attacks, missed signs of intrusion, and made misleading public statements about the incident. #23andMe #ChromeHoldingCo #RobBonta #CaliforniaAttorneyGeneral
Category: Cyber Security News
Threat actors are abusing ChatGPT’s content-sharing feature and Google ads to promote fake OpenAI outage pages that push users toward malware disguised as the ChatGPT desktop app. The LLMShare campaign uses a legitimate chatgpt.com shared page and then redirects victims to a cloaked download site at openew[.]app that delivers malicious installers. #ChatGPT #LLMShare #openewapp #OpenAI
A North Carolina man was sentenced to 121 months in prison for selling lead lists containing the personal data of more than 7 million elderly Americans to Jamaican scammers who used them for lottery fraud. He earned over $5.2 million from the scheme, while victims suffered losses exceeding $9.5 million. #TroyMurray #SteveDixon #JamaicanScammers
Google says Chrome Device Bound Session Credentials (DBSC) is now generally available and rolling out to protect Google accounts from takeover by binding session cookies to a specific device. The feature makes stolen cookies far less useful to attackers, including groups behind Lumma and Rhadamanthys, because the required cryptographic keys stay tied to the device’s security hardware. #Chrome #DBSC #GoogleWorkspace #Lumma #Rhadamanthys

GREYVIBE is a previously undocumented threat actor that has been conducting persistent attacks against Ukraine and Ukraine-related entities since at least August 2025, using phishing, fake CAPTCHA pages, and fraudulent websites to deliver custom malware. WithSecure says the group appears Russian-speaking and aligned with Kremlin interests, while also showing links to…

Google has released Chrome 148 with fixes for 151 vulnerabilities, including 22 critical flaws that could lead to remote code execution or sandbox escape. The most severe bugs include CVE-2026-9872, CVE-2026-9873, CVE-2026-9874, CVE-2026-9875, and CVE-2026-9876, with researchers earning major bug bounty rewards. #Chrome148 #CVE-2026-9872 #CVE-2026-9873 #CVE-2026-9874 #CVE-2026-9875 #CVE-2026-9876…
California Attorney General Rob Bonta sued Chrome Holding Co., formerly 23andMe, over a 2023 breach that exposed sensitive genetic and health data from nearly 7 million people. The lawsuit says the company failed to use basic protections like password resets and multifactor authentication, allowing attackers to exploit stolen credentials and later…
BTMOB is an Android remote access trojan sold as a malware-as-a-service platform with a builder that lets criminals create customized phishing-based payloads without coding. It targets users mainly in Brazil and Latin America, using fake Google Play pages, Accessibility abuse, and multiple theft and remote-control features. #BTMOB #SpySolr #ESET #ANYRUN #Cyble

GreyVibe, a likely Russian threat group, has been targeting Ukrainian and Ukraine-related organizations with AI-generated lures and custom malware since at least August 2025. Its campaigns use multiple attack chains and tools such as LegionRelay, PhantomRelay, and FallSpy, suggesting a hybrid operation that may blend state-aligned goals with cybercriminal tradecraft. #GreyVibe #WithSecure #LegionRelay #PhantomRelay #FallSpy #PhantomMail #PhantomClick #PrincessClub #DroneLink #Nebo #UAC-0098
ShinyHunters claimed responsibility for a breach at Charter Communications that led to the exposure of personal data from 4.9 million accounts after a vishing attack on an employee’s Microsoft Entra account. The group also leaked data taken from Charter’s Salesforce instance after the company reportedly refused to pay the ransom demand, while Charter said no sensitive personal information or CPNI was exfiltrated. #ShinyHunters #CharterCommunications #MicrosoftEntra #Salesforce
A Google security engineer was charged after allegedly using confidential “Year in Search” data to profit more than $1.2 million by betting on Polymarket under the alias AlphaRaccoon. Prosecutors and the CFTC say he misused internal Google information, moved the proceeds through crypto services, and now faces criminal and civil penalties. #MicheleSpagnuolo #Google #Polymarket #CFTC #AlphaRaccoon

Kimsuky targeted South Korean military and corporate entities with fake security software and Webex lures to deliver HTTPSpy and other payloads, while using techniques like JSONPing and stolen meeting schedules to improve infection success. Kaspersky also reported that Kimsuky is evolving its toolset with VS Code tunneling, DWAgent, and new malware…

Daily Recap, Sentencing and breach headlines dominated today: a Romania-linked hacking case delivered a 5-year prison term to target Oregon government systems, while Carnival Cruise confirmed a data breach affecting nearly 6 million people; a separate sextortion conviction resulted in a 33-year sentence for targeting 145 children. On the threat side, Grandoreiro malware and the BTMOB RAT campaign continue cross-platform targeting across Windows and Android, alongside GPU mining malware spreading via SEO poisoning and AI chatbots, plus an npm package that reportedly stole files from a Claude AI user directory on GitHub.
#Oregon #RomaniaHack #CarnivalCruise #Grandoreiro #BTMOB #Sextortion #Edamame #npm #ClaudeAI #GitHub #SEOpoisoning #AIChatbots
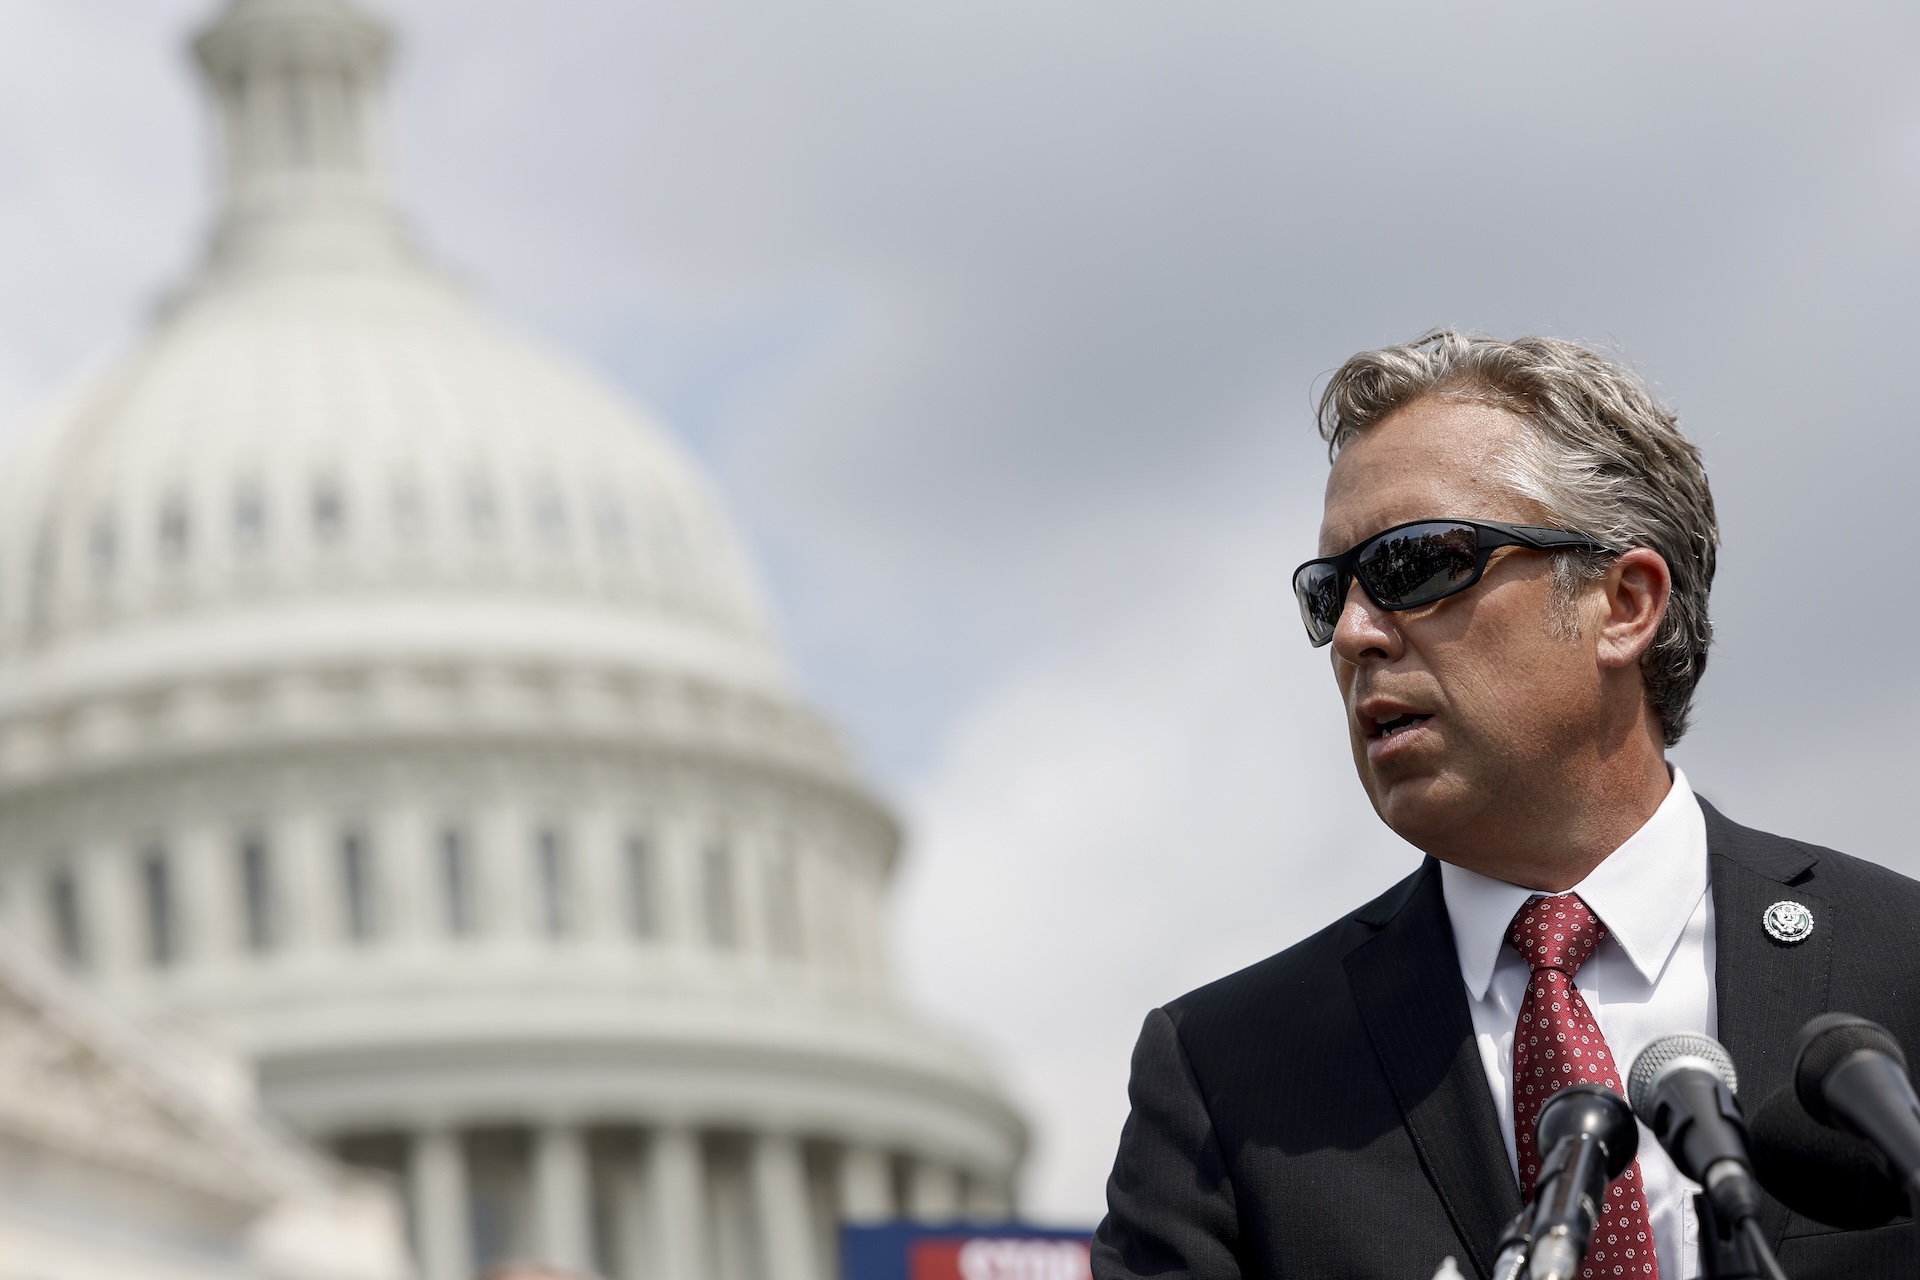
A House Homeland Security subcommittee will hold an open June 4 hearing focused on how frontier AI models are affecting cybersecurity, with witnesses from Google Threat Intelligence, the Frontier Model Forum, Corridor Security, and the Electronic Frontier Foundation. Lawmakers are responding to concerns that adversaries, including China, could steal AI capabilities, weaponize AI-enabled tools, and use advanced models to uncover new cyber vulnerabilities. #GoogleThreatIntelligence #FrontierModelForum #CorridorSecurity #ElectronicFrontierFoundation #AndyOgles #SeanCairncross #TrumpAdministration

Rapid7 disclosed a critical Gogs vulnerability that can let an authenticated user achieve remote code execution by abusing a malicious branch name during the “Rebase before merging” flow. The flaw affects all supported platforms and can expose repositories, credentials, and private data across tenants, while Rapid7 has released a Metasploit module…