TA4922 is a Chinese-speaking cybercrime group that has expanded its operations across Asia, Europe, and South Africa by using social engineering, phishing, and multiple malware families to gain access to victim organizations. Proofpoint says the group is financially motivated and has used tools like Atlas RAT, RomulusLoader, SilentRunLoader, and ValleyRAT in…
Category: Cyber Security News

CISA has urged federal agencies to urgently patch CVE-2026-45247, a critical PHP object injection flaw in the Mirasvit Full Page Cache Warmer for Magento 2 that is being exploited in the wild for remote code execution. Organizations running Mirasvit Cache Warmer versions before 1.11.12 should update immediately, and defenders can look…

CISA has added CVE-2026-45247 affecting Mirasvit Cache Warmer for Magento to its Known Exploited Vulnerabilities catalog after reports of active exploitation. The flaw allows unauthenticated remote code execution through a crafted CacheWarmer cookie and has been observed in attacks targeting Magento stores worldwide. #CVE-2026-45247 #Mirasvit #Magento #CISA #Sansec #Imperva…

A severe Visual Studio Code vulnerability can let attackers steal a user’s GitHub token by luring them into opening a specially crafted Jupyter notebook on github.dev. Microsoft released a fix on June 3 after the zero-day disclosure, while the issue also affects the desktop version of VS Code with the potential…

Cisco has patched a high-severity flaw in Unified Communications Manager and Unified Communications Manager Session Management Edition, warning that proof-of-concept code is already available. The issue, tracked as CVE-2026-20230, could let attackers perform SSRF attacks and potentially gain root privileges on affected systems, while separate fixes were also issued for Webex…

CISA Acting Director Nick Andersen said the agency will issue a binding operational directive by the end of the week to help federal agencies implement the president’s artificial intelligence executive order. The directive will emphasize vulnerability management and testing AI models, while CISA also prepares to provide partners with specific AI…

Researchers uncovered a malspam campaign that abuses Google’s DoubleClick domain to hide its redirect chain and deliver DesckVB RAT through a phishing email attachment. The attack uses dynamic victim personalization, multiple loaders, and defense evasion techniques to gain persistence, disable security tools, and take control of infected systems. #DoubleClick #DesckVBRAT…

SafeBreach researcher Or Yair showed that a single poisoned notification on Android could trick Google Gemini into faking messages, opening windows, joining Zoom calls, and even poisoning long-term memory without any malicious app installed. Google has since patched the issue with server-side mitigations after the Fake Context Alignment bypass was reported…

Europol said European authorities arrested 29 alleged cybercriminals and dismantled a large piracy network that distributed illegal streams of major sports, films, and TV content. Operation Kratos 2 disrupted nine organized crime groups and led to the takedown of tens of thousands of illegal URLs tied to streaming infrastructure across multiple countries. #Europol #OperationKratos2 #Streameast #UEFAEuropaLeague #LaLiga #beINMediaGroup
The U.S. Treasury’s OFAC has sanctioned Nobitex, Iran’s largest cryptocurrency exchange, for helping facilitate payments tied to terrorist activity, sanctions evasion, and IRGC-linked transactions. The action also targets other Iranian exchanges and named executives, following findings that Nobitex was tied to ransomware-related wallets and broader support for the Iranian regime. #Nobitex #IRGC #OFAC #Wallex #Bitpin #Ramzinex #PredatorySparrow
A Chinese-speaking cybercrime group tracked as TA4922 has expanded operations into Europe, using new malware such as Atlas RAT, RomulusLoader, and SilentRunLoader alongside localized phishing lures. Proofpoint says the actor is highly active, financially motivated, and may be using AI-assisted development to accelerate its malware arsenal. #TA4922 #AtlasRAT #RomulusLoader #SilentRunLoader #ValleyRAT
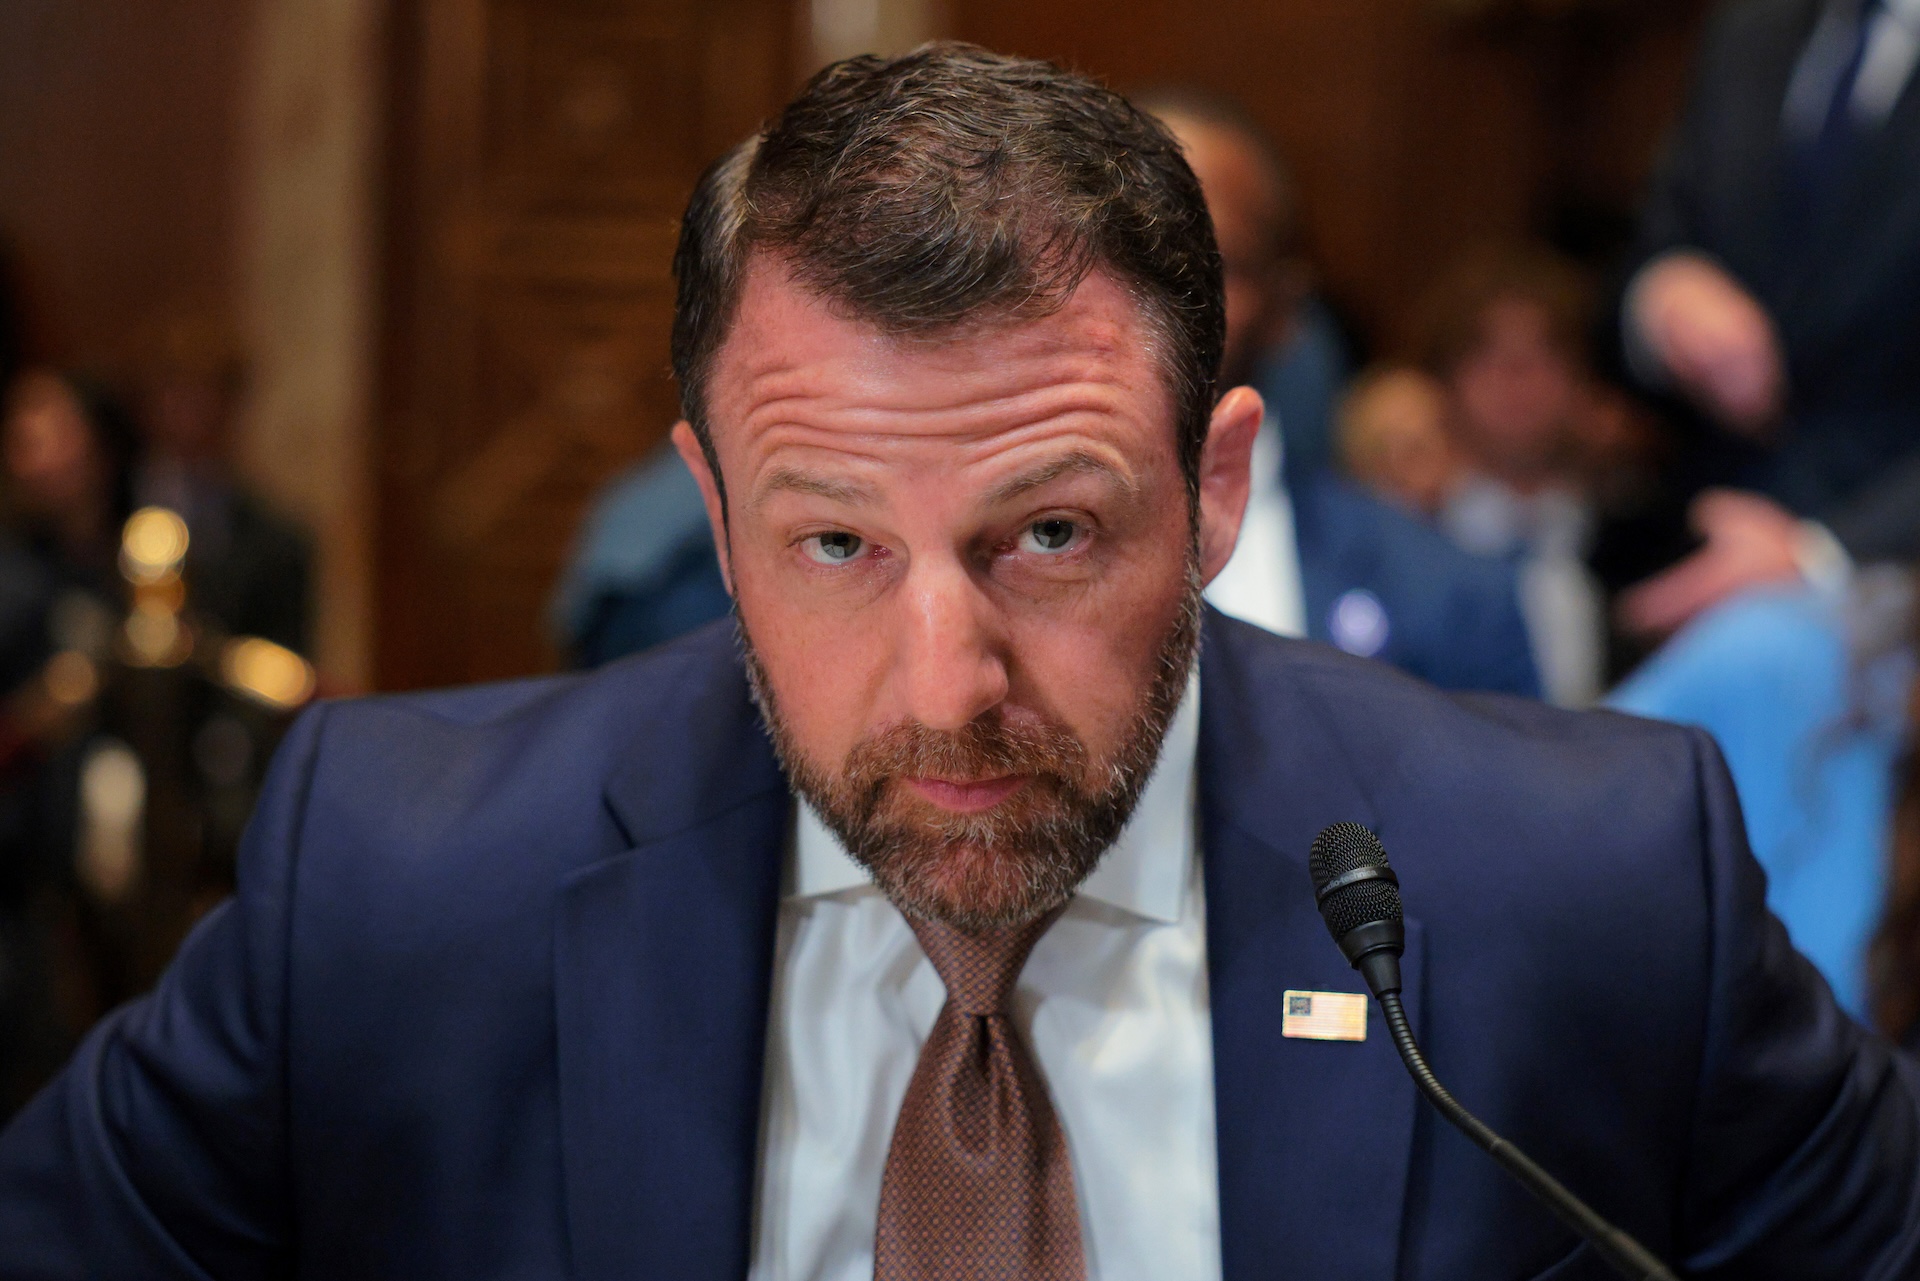
DHS Secretary Markwayne Mullin told Congress that CISA would ideally have 2,800 personnel, as the agency faces proposed Trump administration cuts and ongoing debate over its future role. Lawmakers and experts are also concerned about reduced funding, the lack of a Senate-confirmed CISA director, and whether cybersecurity responsibilities should be shifted more heavily to states and local governments. #CISA #MarkwayneMullin #AndrewGarbarino #DonaldTrump
Coralogix announced a $200 million Series F funding round, bringing its total funding to $550 million and its valuation to $1.6 billion. The company will use the new capital to expand its AI-native observability platform, telemetry data lake architecture, and global growth, while strengthening cloud-native SIEM and AI-SPM capabilities. #Coralogix #Advent…
A new HTTP/2 denial-of-service method called HTTP/2 Bomb can crash major web servers from a single machine by combining HPACK compression amplification with flow-control stalling. Researchers found it can exhaust huge amounts of memory on NGINX, Apache HTTP Server, Microsoft IIS, Envoy, and Cloudflare Pingora, with some fixes already available for nginx and Apache. #HTTP2Bomb #NGINX #ApacheHTTPServer #MicrosoftIIS #Envoy #CloudflarePingora #CVE-2026-49975
CISA, the FBI, the NSA, the Department of Energy, and other U.S. partners warned that attackers are targeting internet-exposed automatic tank gauge (ATG) systems used across critical infrastructure to monitor fuel and liquid storage tanks. The advisory says intruders can exploit weak authentication and software flaws to change settings, disable alerts, and increase the risk of leaks or equipment failures. #CISA #FBI #NSA #DepartmentofEnergy #ATG