Security leaders from Datadog, Jamf, ASOS, and Tines warn that AI is accelerating “wild code” sprawl as employees build apps, automations, and agents outside IT visibility. They argue that policy alone is not enough, and that organizations need governed tools, data classification, use-case registries, and continuous technical controls to track and secure AI-driven work. #Claude #Datadog #Jamf #ASOS #Tines #ClaudeCode #ClaudeTokens #Google
Category: Cyber Security News
The FBI warns that criminals are using couriers to collect cash from victims of cryptocurrency investment scams, including pig butchering and romance baiting schemes. After victims are manipulated into sending money, scammers use in-person pickups, passwords, or dollar bill serial numbers to retrieve cash and keep the fraud cycle going. #FBI #pigbutchering #romancebaiting
More than 73,000 French government employees were reportedly affected after DINUM said Tchap was breached through account hijacking on June 7, 2026. An unknown threat actor calling itself misere claimed the theft of account data and 13.5GB of files, but the exact cause and motivation remain unverified. #DINUM #Tchap #misere…
Novo Nordisk disclosed a cybersecurity incident that involved unauthorized access to a limited number of internal IT systems containing personal data from clinical trial participants and healthcare providers. The company said the exposed information did not include direct identifiers, and no known cybercrime group has claimed responsibility. #NovoNordisk #Ozempic #Wegovy #Rybelsus…

Oleksii Oleksiyovych Lytvynenko pleaded guilty in a US court for his role in the Conti ransomware operation, including helping develop a malware loader and possessing data from multiple victims. His case follows his extradition from Ireland and adds to efforts to hold members of the Conti network accountable after the gang’s…

Palo Alto Networks says an unknown threat actor is actively exploiting CVE-2026-0257 in PAN-OS to gain unauthorized access to GlobalProtect portals and initiate VPN connections. The company has shared IoCs and urged customers to check for suspicious gateway-connected events, while CISA has already added the flaw to its KEV catalog. #CVE-2026-0257…

Fraudulent Facebook accounts are being used to impersonate politicians, public figures, and trusted organizations across the Middle East and North Africa to push fake offers and lure victims into scam funnels. The activity has been linked to Sniper Dz, a PhaaS platform that abuses browser notifications, link-aggregation services, and traffic redirection…

Cybersecurity Threat Research ‘Weekly’ Recap. This week covered supply-chain and developer-focused intrusions (Shai-Hulud, Mini Shai-Hulud/Miasma/Hades, UNK_DeadDrop, GoFlateLoader) plus phishing and social-engineering campaigns that targeted Microsoft account tokens, social-media lure downloads, and FIFA/World Cup 2026 fraud kits. It also highlighted cloud/identity abuse and enterprise compromises (Entra Agent ID blueprint abuse, Azure DNS takeover, Duo Auth Proxy exposure, PulseRAT, MLTBackdoor) alongside ransomware/extortion/data theft cases (Tengu/Shisa, ShinyHunters) and defenses tied to flaws like ITScape (CVE-2026-46316).
The FBI, Google, and Black Lotus Labs dismantled Outsider Enterprise, a Chinese phishing-as-a-service operation that used AI and distributed kits to steal credit card data and passwords through massive SMS campaigns. The takedown, part of Operation Riptide, targeted infrastructure linked to millions of fraudulent URLs, 3.8 million stolen credit card records, and billions in losses. #OutsiderEnterprise #OperationRiptide #Google #FBI #ATT #TMobile #Verizon

Daily Recap, U.S. export controls compelled Anthropic to take Fable 5 and Mythos 5 offline for foreign nationals, underscoring tighter access to advanced AI models. Elsewhere, Chinese-linked actors showed long-running stealth in an authentication hijack and Linux backdoor campaigns, while Arch Linux AUR package hijacking pushed an infostealer and eBPF rootkit. #Anthropic #Fable5 #Mythos5 #Fable5 #Mythos5 #AuthHijack #LinuxBackdoor #ArchLinuxAUR #eBPF #Conti #ShinyHunters #OraclePeopleSoft #Coupang #23andMe #phpBB #FISA #DeepfakePornSite

Zscaler’s 2026 phishing report says phishing volume is falling, but attackers are shifting to more targeted, higher-conversion campaigns that cause greater losses. Phishers are also increasingly using cloud infrastructure, especially AWS, while countries like Canada and Spain saw major drops in activity and the services and government sectors saw sharp increases. #Zscaler #AWS #FBI #ChatGPT

The U.S. government ordered Anthropic to suspend foreign access to Fable 5 and Mythos 5 after citing a national security concern tied to a reported jailbreak method that could bypass their safety limits. Anthropic disabled the models, disputed the severity of the finding, and said it is working to restore access as soon as possible. #Anthropic #Fable5 #Mythos5 #HowardLutnick #DarioAmodei
A former IT employee, Ezekiel Dean Potter, was sentenced to 21 months in prison for a prolonged campaign against the Saydel Community School District that deleted accounts, disrupted classroom operations, and caused tens of thousands of dollars in damage. Prosecutors said he kept using retained credentials after leaving the district, targeted services including Apple School Manager, Schoology, Gmail, and Facebook, and will now pay restitution and face supervised release. #SaydelCommunitySchoolDistrict #EzekielDeanPotter #AppleSchoolManager #Schoology #Google #GoDaddy #CaseysStoreSupportCenter #ThePrinterInc
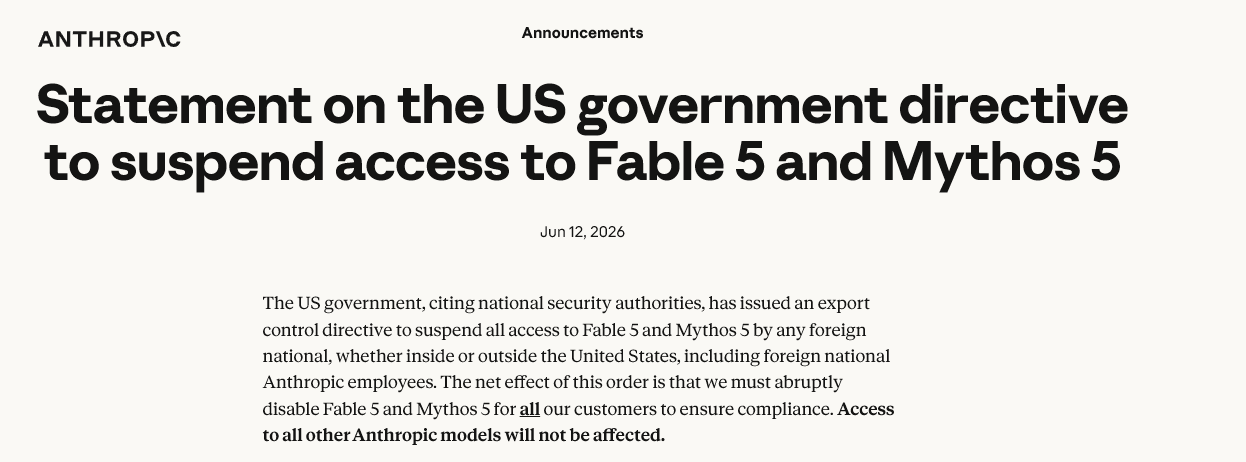
U.S. export controls on Fable 5 and Mythos 5 are pushing frontier AI labs toward KYC-based access controls, but cybercriminals are already preparing to bypass them with stolen sessions, synthetic identities, and pre-verified accounts. The shift could also create new high-value targets for data theft, since AI platforms may have to store passports, biometrics, and other sensitive documents that attackers can later exploit. #Fable5 #Mythos5 #Claudeai #OpenAI #Lumma #Vidar #RedLine #HudsonRock #ZachXBT
Daily Recap, urgent patching focus returned as CISA directed federal agencies to address actively exploited Ivanti issues, while Oracle mitigated a PeopleSoft zero-day tied to data theft and Microsoft resolved Windows update failures linked to the WUSA installer. Across breaches and espionage, Novo Nordisk disclosed clinical trials exposure, tchap accounts were reported as affected in France, and threat activity included Iran’s Handala claiming access to Cal Water and Russia’s Void Blizzard facing charges, with ShinyHunters also linked to PeopleSoft exploitation. #Ivanti #CISA #Oracle #PeopleSoft #WUSA #NovoNordisk #tchap #Maine #Handala #CalWater #VoidBlizzard #ShinyHunters #Europol #AudiA6 #ClaudeFable5 #Anthropic #CyberCorps