India’s government told the Delhi High Court that Telegram was warned about alleged exam-paper leak channels roughly two weeks before the app was blocked and admitted it could not proactively detect the offending content. The nationwide ban disrupted access beyond India, while Telegram is challenging the move as unlawful and the court’s decision is still pending. #Telegram #DelhiHighCourt #NEETUG2026 #NationalTestingAgency #RelianceJio
Category: Cyber Security News
Apple has released Beats Firmware Update 1B211 to fix CVE-2025-20701, a high-severity Bluetooth flaw in Beats Studio Buds that could let nearby attackers eavesdrop on conversations. The issue affects the Airoha SoC and was disclosed by ERNW researchers Dennis Heinze and Frieder Steinmetz, with related vulnerabilities CVE-2025-20700 and CVE-2025-20702 also enabling deeper device compromise. #BeatsStudioBuds #CVE-2025-20701 #Airoha #ERNW #DennisHeinze #FriederSteinmetz

Israeli cybersecurity startup Dream has raised $260 million in a new funding round, lifting its valuation to $3 billion and bringing total funding to more than $410 million. The company plans to expand its sovereign AI and national cyber defense platforms, Sphere, Hero, and Atlas, across multiple global regions. #Dream #Sphere…

Sen. Mark Warner warned that deep staffing cuts at CISA, along with the loss of support for the MS-ISAC, are weakening federal cyber defense and reducing assistance for state and local critical infrastructure operators. He urged DHS and CISA to restore support, while demanding detailed records on vacancies, regional service delivery,…
Ukraine has been granted access to the EU Cybersecurity Reserve, enabling it to request EU-approved experts for help during major cyberattacks that exceed its own response capacity. The move deepens Kyiv’s security ties with Brussels amid ongoing Russian cyberattacks and could eventually allow Ukrainian cybersecurity firms to join the reserve as…

Kodak confirmed a data breach after ShinyHunters claimed to have stolen more than 2.2 million records, including customer personal information and corporate data. The company says the incident was limited in scope and contained, while law enforcement and external cybersecurity experts continue to investigate. #Kodak #ShinyHunters…
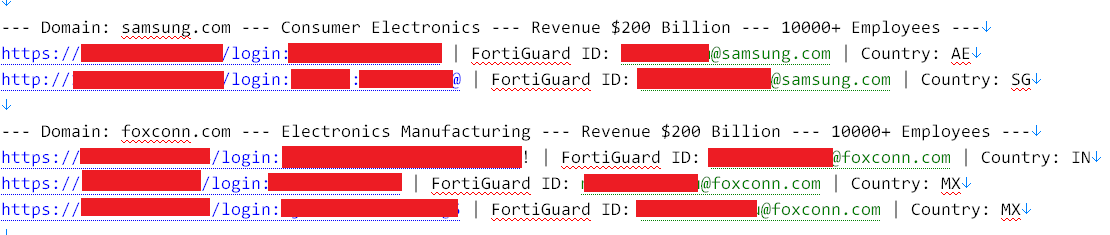
A massive cyber espionage campaign compromised tens of thousands of Fortinet firewalls and VPN gateways across 194 countries, exposing credentials and enabling deep network intrusions. The operation, linked to a Russian-speaking cybercriminal group, affected major organizations such as Foxconn, Samsung, Comcast, Siemens, Lenovo, PwC, Accenture, and Oracle, with confirmed breaches including a Turkish NATO defense contractor. #Fortinet #FortiGate #HudsonRock #VolodymyrDiachenko #KevinBeaumont

Britain’s cyber chief warned that hostile states are behind most attacks on the country’s critical national infrastructure, with the NCSC handling more than 200 incidents in a year and often stopping breaches before they fully develop. He said cyberspace should be viewed as a constant contest, cited Volt Typhoon as a…

Microsoft has disclosed that it is preparing a patch for a Microsoft Defender zero-day named RoguePlanet, now tracked as CVE-2026-50656. The flaw is a privilege escalation issue in the Microsoft Malware Protection Engine, and researcher Chaotic Eclipse says the exploit can deliver SYSTEM-level access under certain race-condition conditions. #RoguePlanet #CVE-2026-50656 #MicrosoftDefender…

Check Point Research uncovered a threat actor using fake reputation tactics across news sites, GitHub, SourceForge, YouTube, VirusTotal, and a WordPress phishing hub to promote malicious warez. The campaign delivers a Rust-based cryptocurrency clipboard hijacker hidden in Solana and Pump.fun sniper bots and crash-game predictors, targeting Windows and macOS users seeking…
Google will begin using IP addresses for ad measurement and personalization in the EEA, the UK, and Switzerland starting on or shortly after August 3, 2026, bringing a routine technical signal into regions where it is treated as personal data. The change raises consent and fingerprinting concerns under GDPR and UK rules, with Google, the ICO, and the IAB Europe TCF now central to how IP-based personalization will be handled. #Google #ICO #IABEuropeTCF

Daily Recap, US regulators reported record $3.5 billion in 2025 losses from imposter scams as the FTC warned about rising victim costs, while the UK plans to ban social media access for children under 16 and other governments moved to strengthen fraud and reporting controls. CISA and vendors also warned about active exploitation of cPanel, Cisco SD-WAN/vManage, and Fortinet FortiSandbox flaws, alongside major intrusion and espionage updates including DragonForce using Microsoft Teams relays and NarwhalRAT delivery via fake Microsoft alerts. #ImposterScams #FTC #UK #cPanel #CiscoSDWAN #CiscoVmanage #FortinetFortiSandbox #DragonForce #BackdoorTurn #MicrosoftTeams #Astral #iRhythm #ShinyHunters #CalWater #Google #NarwhalRAT #LiteLLM #Copilot #SprySOCKS #OptinMonster #TrustCloud #NewCore
Attackers are exploiting multiple Fortinet FortiSandbox flaws, including CVE-2026-39808 and CVE-2026-39813, after patches were released in April, with researchers observing active exploitation across several countries. The activity appears to involve multiple independent operators and could lead to broader attacks against trusted FortiSandbox environments and connected Fortinet devices. #Fortinet #FortiSandbox #CVE-2026-39808 #CVE-2026-39813 #CVE-2026-25089

Cato Networks documented how an attacker known as Poisson compromised a small French automotive business, stole credentials, and then used OpenSSH and Tailscale to keep access even after the Havoc C2 server went offline. The case shows that removing a command-and-control server is not enough if an attacker has already built…
Today’s attackers are increasingly “logging in” through social engineering, MFA fatigue, session hijacking, credential theft, and help desk impersonation to bypass traditional defenses. This webinar will explain the modern identity attack chain, review recent breach lessons, and show how organizations can improve detection and response with identity threat detection and adaptive…