CISA is warning organizations to secure internet-facing Fortinet firewalls and VPNs after the FortiBleed campaign exposed more than 86,000 valid credentials across 194 countries. Investigators say the attack has been linked to a Russian-speaking threat actor using large-scale brute force and SSL VPN interception to compromise networks, including government and critical…
Category: Cyber Security News

This week’s roundup covers major security issues ranging from a critical phpBB authentication bypass and compromised WordPress plugins to stealthy long-term intrusion by Velvet Ant and malicious JetBrains Marketplace plugins stealing AI keys. It also highlights cloud and browser risks, including GCP Config Connector privilege escalation, Chrome extension flaws in MaXSS…
CISA warned Fortinet customers to secure their devices after the FortiBleed leak exposed credentials for nearly 74,000 firewalls and VPN gateways worldwide. The leak is linked to attacks on internet-accessible Fortinet devices and includes data that could help threat actors plan future intrusions. #CISA #Fortinet #FortiBleed #FortiGate
A New York man, Anthony Belford, was indicted for cyberstalking after allegedly using fake social media and email accounts to spread AI-generated nude images and racist false claims about a Georgia college student. The case highlights how spoofed profiles, intimate image abuse, and impersonation can be used to harass victims across multiple platforms. #AnthonyBelford #FBI #FTC
CISA has ordered federal agencies to patch a critical Splunk Enterprise flaw, CVE-2026-20253, after confirming it is being actively exploited in attacks. The vulnerability affects multiple Splunk Enterprise versions and can enable unauthorized file operations and potentially remote code execution, prompting urgent fixes and mitigation guidance from Splunk and CISA. #CVE-2026-20253 #SplunkEnterprise #CISA #BOD26-04
Microsoft has confirmed a Windows Recycle Bin bug that shows internal $Rxxxxx.ext filenames in the delete confirmation dialog instead of the original file name. The issue affects all supported Windows client and server versions after the June 2026 security updates, and Microsoft says a fix is in development with a temporary business workaround available. #Microsoft #Windows #RecycleBin
Many organizations rely on multi-factor authentication as a key safeguard, but attackers are increasingly bypassing it by abusing legitimate authentication workflows instead of stealing passwords. The webinar “Stop chasing alerts: Automating email security with behavioral AI” will show how Device Code phishing, BEC, and ATO attacks can evade traditional defenses and how behavioral AI can help detect compromise earlier. #DeviceCodePhishing #AbnormalAI #BleepingComputer #NovantHealth

Microsoft has identified CryptoBandits, a Windows-based cryptocurrency clipper that combines clipboard theft, screenshot exfiltration, wallet address substitution, and lightweight backdoor capabilities for remote code execution. The malware spreads through malicious .lnk files, uses a bundled Tor client with a local SOCKS5 proxy for hidden-service C&C communication, and targets cryptocurrency seed phrases…
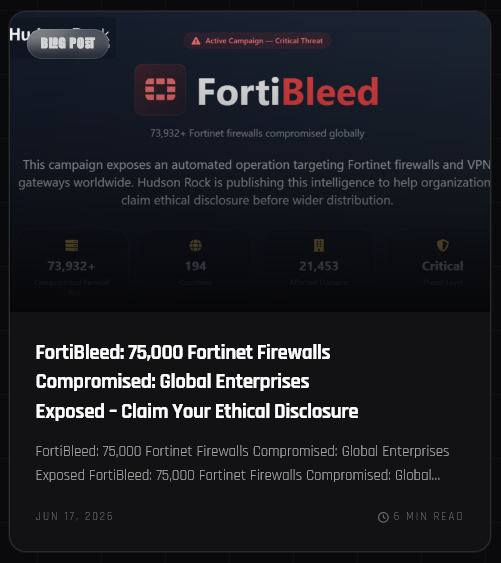
Hudson Rock reported an unprecedented response to the FortiBleed/Fortinet compromise, with over 100,000 views, thousands of ethical disclosures, and rapid action from SOC teams and CERTs worldwide. The intelligence was quickly amplified by NCSC, CISA, INCD, and major media outlets, while Hudson Rock integrated the dataset into Cavalier, its API, and a free lookup portal for affected organizations. #FortiBleed #Fortinet #HudsonRock #CISA #NCSC #INCD #Cavalier
Authorities in the Netherlands, Canada, the US, and Germany disrupted SocGholish infrastructure and cleaned up nearly 15,000 infected WordPress sites with support from Europol and private partners. The long-running FakeUpdates framework has been used to deliver loaders and payloads including Gholoader, MintsLoader, GhostWeaver, LockBit, RansomHub, AsyncRAT, and NetSupport RAT through compromised…
Cisco has agreed to acquire WideField Security to boost Splunk’s Agentic SOC with deeper identity lifecycle and session intelligence. The deal will help organizations uncover identity exposures, monitor authentication risks, and secure human and AI-driven activity at scale. #Cisco #Splunk #WideFieldSecurity…
Authorities disrupted the SocGholish botnet, also known as FakeUpdates, and seized infrastructure used by Evil Corp and other cybercrime groups to steal data and gain network access. The coordinated operation removed 106 servers, remediated nearly 15,000 infected websites, and warned that traffic distribution systems are being used to deliver ransomware and phishing attacks. #SocGholish #FakeUpdates #EvilCorp #OperationEndgame #OperationRiptide
The Gentlemen ransomware-as-a-service operation is actively maintaining a set of EDR killers, led by the GentleKiller tool, to help affiliates evade security defenses during attacks. ESET says the group also uses external tools like HexKiller, ThrottleBlood, and HavocKiller, and has tied the activity to FortiGate-based targeting, the Romanian energy provider Oltenia, and a SystemBC proxy botnet. #Gentlemen #GentleKiller #HexKiller #ThrottleBlood #HavocKiller #FortiGate #Oltenia #SystemBC

Daily Recap, patching and vulnerability updates dominated today as CISA ordered U.S. federal agencies to address an actively exploited critical Joomla plugin issue, while browser and enterprise-targeted fixes rolled out for Google Chrome, Firefox, Fortinet FortiSandbox, Rockwell Automation ICS, and LiteSpeed/Joomla. On the campaign side, new Rokarolla Android malware stole PINs, SMS codes, and crypto funds, ClickFix and GhostTree expanded evasion techniques, and ShinyHunters’ extortion claims were confirmed by Kodak. #CISA #Joomla #FortinetFortiSandbox #RockwellAutomation #LiteSpeed #Rokarolla #ClickFix #GhostTree #JetBrains #SteamWorkshop #WallPaperEngine #Kodak #ShinyHunters #iRhythm
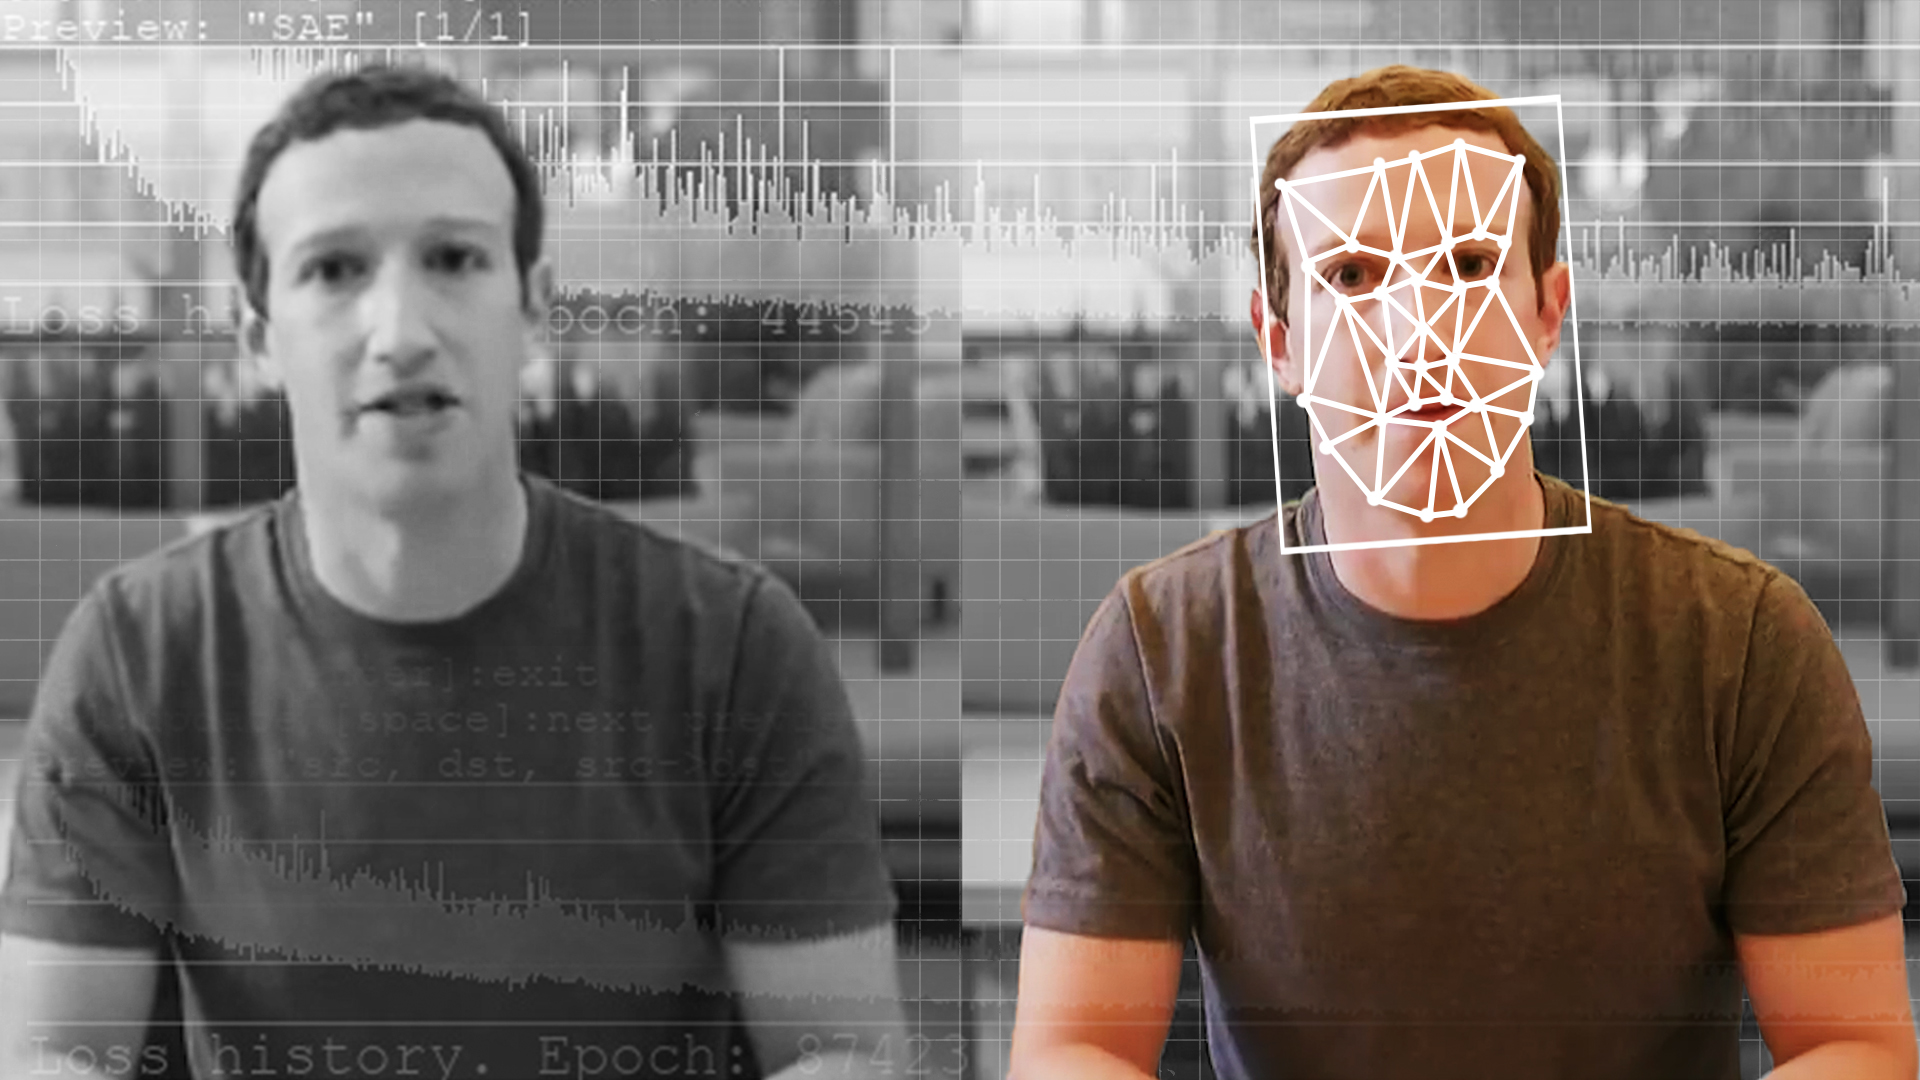
The Senate Judiciary Committee advanced the NO FAKES Act, a bill designed to stop unauthorized AI deepfakes of artists, performers, and public figures by giving people control over their digital replicas. Critics including tech and civil liberties groups warn the measure could enable overbroad takedowns of lawful speech, satire, parody, and political content. #NOFAKESAct #ChrisCoons #MarshaBlackburn #NetChoice #ACLU #EFF