CIA Director John Ratcliffe said the agency is undergoing a major transformation to move faster on emerging technologies, especially frontier AI, which he described as having capabilities akin to “digital nuclear weapons.” He outlined changes including a revamped cyber and digital organization, a faster procurement process, and deeper partnerships with private…
Category: Cyber Security News

Threat actors are exploiting CVE-2026-33017 in Langflow to gain unauthenticated remote code execution and deploy a Monero miner through a multi-stage infection chain. The campaign uses the lambsys binary to disable security tools, persist via cron and SSH keys, remove traces, and spread to other hosts reachable with reused credentials. #Langflow…

RustDuck is a new two-stage malware family that compromises home routers, IP cameras, Android boxes, and exposed servers to build a botnet for DDoS attacks. QiAnXin’s XLab says it is rapidly evolving, rewriting its core in Rust, and using strong anti-analysis and encrypted communications to evade detection. #RustDuck #QiAnXinsXLab #RustoBot #AISURU…

Microsoft research shows that attackers can poison MCP tool descriptions to hijack AI agents and quietly exfiltrate company data without triggering obvious alarms. The report warns that as agents in Microsoft 365 Copilot, Copilot Studio, and Azure AI Foundry gain real-world permissions, organizations must treat connected tools as supply-chain risks and…
Business Email Compromise is a coordinated fraud operation that goes far beyond a simple email scam, involving mailbox access, financial process reconnaissance, infrastructure, and cash-out planning. Underground discussions show growing use of AI, call centers, and mule networks to increase the realism and success rate of BEC campaigns. #BusinessEmailCompromise #Flare #Bigjack #blackhatpakistan #O365
Microsoft found a malicious Chrome Web Store extension called “Search for perplexity ai” that impersonates Perplexity AI and reroutes search traffic through attacker-controlled infrastructure while collecting browsing activity. The extension uses fake Perplexity branding and a lookalike domain, and users who installed it should remove it and rotate critical passwords as a precaution. #PerplexityAI #Searchforperplexityai #ChromeWebStore
The Department of Homeland Security is restoring a critical information-sharing framework for critical infrastructure through the new ANCHOR-CI program, which will replace the former CIPAC structure. The initiative will let government and private-sector stakeholders coordinate on cyber threats, vulnerabilities, and resilience efforts while operating outside the Federal Advisory Committee Act. #CIPAC #ANCHORCI #CISA #DHS
Aflac Life Insurance Japan disclosed that hackers accessed its systems multiple times and stole personal information from about 4.38 million customers and agents. The breach affected policyholder portal data, disrupted multiple services, and exposed sensitive details including names, addresses, phone numbers, dates of birth, and insurance account information, with some premium…
Adversa AI discovered GuardFall, a structural flaw in multiple open source AI agents that lets malicious Bash instructions slip past pattern-based guards and execute with the operator’s authority. The issue can expose secrets, exfiltrate AWS credentials, or damage development environments through poisoned content such as README files, Makefiles, or MCP server…
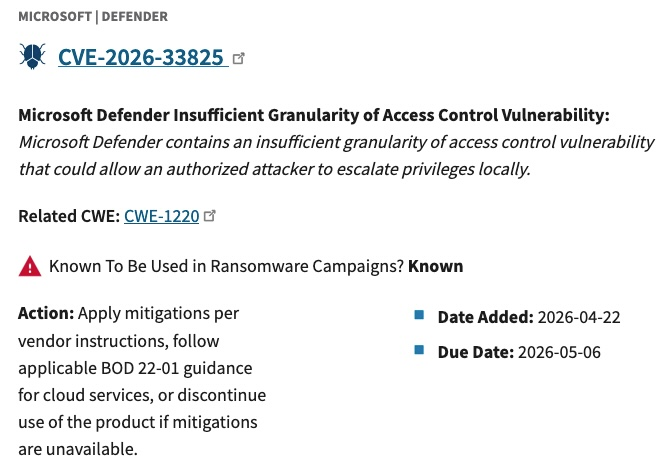
CISA says the Microsoft Defender vulnerability BlueHammer, tracked as CVE-2026-33825, is being used in ransomware attacks. The flaw was publicly disclosed on April 2, patched by Microsoft on April 14, and later added to CISA’s Known Exploited Vulnerabilities catalog after Huntress observed it being exploited as a zero-day. #BlueHammer #CVE-2026-33825 #MicrosoftDefender…
Microsoft has added a Teams admin policy that lets organizers block third-party bots from joining meetings without approval, improving control over external participants. The update helps reduce abuse by malicious apps and supports stronger safeguards against social engineering and unauthorized access in Teams. #MicrosoftTeams #TeamsAdminCenter #DefenderPortal
Aflac disclosed that attackers breached Aflac Japan’s systems and stole sensitive policy, personal, and bank account information, while the company said its U.S. systems were not accessed. The incident is being investigated with external experts and Japanese authorities, and it follows a previous Aflac breach amid broader attacks on insurance companies, with signs linked to Scattered Spider. #Aflac #AflacJapan #ScatteredSpider
Leaked Black Basta chat logs show ransomware groups operating like corporate syndicates, using organized staffing, outsourced services, victim profiling, and deadline manipulation to maximize extortion payouts. The analysis also highlights how modern ransomware has become a specialized, multi-extortion business that forces CISOs to prepare, rehearse, and understand the criminal ecosystem before an incident occurs. #BlackBasta #Conti

A critical authentication bypass in SimpleHelp RMM, tracked as CVE-2026-48558, has been exploited to gain fully authenticated technician sessions and deliver malware through internet-facing servers. Blackpoint observed attackers deploying TaskWeaver and Djinn Stealer to fingerprint systems and steal developer secrets, while CISA added the flaw to its KEV catalog and urged…
Nissan has confirmed a data breach tied to a zero-day campaign against Oracle PeopleSoft customers, with attackers suspected of stealing employee records across the US, Canada, Mexico, and Brazil. The campaign is widely linked to ShinyHunters, and other known targets include the University of Nottingham, the NAIC, Illinois Central College, and…