
Daily Recap, Agentic ransomware techniques were documented for the first time as Sysdig tracked JADEPUFFER, while prompt injection attacks demonstrated how AI agents can be manipulated into making crypto payments. North Korean actors continued supply-chain pressure by targeting open source developers, and researchers also flagged trojanized PoC repos and malicious PyPI packages. #JADEPUFFER #Sysdig #NorthKorea #PoC #PyPI
Category: Cyber Security News
Microsoft is testing Cloud Rebuild in Windows 11 Insider Preview builds, a recovery feature that can remotely reinstall the operating system from the cloud when a device is broken or won’t boot. The feature is part of Microsoft’s Windows Resiliency Initiative and joins Point-in-Time Restore, Quick Machine Recovery, and a new post-BSOD memory scan recommendation to improve Windows 11 recovery and reliability. #CloudRebuild #Windows11 #WinRE #QuickMachineRecovery #PointInTimeRestore
BeyondTrust has patched two critical authentication bypass flaws in its Remote Support and Privileged Remote Access products, warning that exposed instances could let unauthenticated attackers access protected appliances under specific configurations. The company also fixed two high-severity issues, while prior BeyondTrust flaws have been used in attacks against U.S. government systems and linked to #SilkTyphoon and #CVE-2026-1731.
Microsoft will enable the Windows settings backup and restore tool by default on eligible Microsoft Entra-joined and Microsoft Entra hybrid-joined enterprise devices starting with Windows 11 26H2. The change applies only when admins have not already set a policy, while restore remains disabled by default and must still be explicitly configured by IT. #MicrosoftEntra #Windows11 #WindowsBackup

China-aligned attackers breached U.S. and Canadian university networks to steal sensitive data and maintain persistent access through webshells and backdoors. The campaign targeted physics and engineering departments and used Roundcube flaws CVE-2024-42009 and CVE-2025-49113 to gain access, with evidence pointing to the threat cluster UNK_MassTraction and the use of VShell. #UNK_MassTraction #Roundcube #VShell #CVE-2024-42009 #CVE-2025-49113

BeyondTrust has patched four critical flaws in Remote Support and Privileged Remote Access that could let attackers bypass access controls, trigger denial-of-service conditions, or reach unauthorized data under certain configurations. The company said the issues were found internally during security assessments, and users should update immediately to RS 25.3.3 or later…

CERT/CC warned that several Tenda firmware versions contain an undocumented authentication backdoor tracked as CVE-2026-11405, allowing attackers to bypass password checks and gain full administrative access to the web management interface. The flaw is still unpatched, and users are advised to disable remote management and change the default LAN IP address…
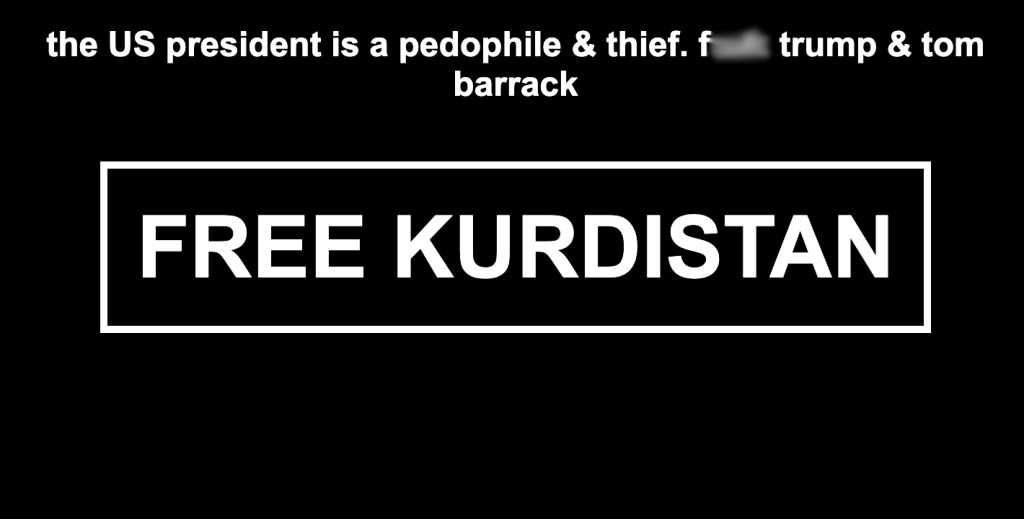
Multiple U.S. Army subdomains, including oil.army.mil and ai2c.army.mil, were defaced in a 404 hijacking campaign that displayed pro-Kurdistan messages and insults aimed at President Donald Trump and U.S. Ambassador Tom Barrack. The Army says the affected pages were hosted on a legacy third-party platform and has secured them while investigators continue to examine how the defacement occurred. #U.S.Army #oil.army.mil #ai2c.army.mil #TomBarrack #DonaldTrump
Medtronic has notified more than 3.8 million people that their data may have been exposed in an attack reportedly linked to ShinyHunters, with accessed information including Social Security numbers, health-related data, names, contact details, and dates of birth. The company says there is no evidence the data was publicly posted and…

BonkDAO said attackers drained $20 million worth of BONK through a malicious governance proposal that exploited large token holdings to redirect coins into their wallets. The organization notified law enforcement and is working to recover funds, while Upbit temporarily suspended BONK deposits and withdrawals after the incident. #BonkDAO #BONK #Upbit #Solana…
Canada’s Communications Security Establishment (CSE) disclosed that it carried out state-authorized active cyber operations in 2025 against a foreign extremist group, overseas drug traffickers tied to fentanyl chemicals, and a ransomware-as-a-service gang. The operations disrupted recruitment, diminished trafficking activity, and disabled ransomware infrastructure while deleting stolen data advertised on the dark…

A use-after-free flaw in Linux KVM, tracked as CVE-2026-53359 and nicknamed Januscape, can be triggered from a guest VM to panic the host and potentially lead to host code execution on both Intel and AMD systems. The issue affects the legacy shadow MMU path in x86 KVM, and the fix requires…

An Iranian hacking group linked to MOIS has been using the modular Cavern (Cav3rn) C2 framework to target Israeli organizations, especially IT providers and government sectors. The campaign uses trojanized SysAid updates, DLL side-loading, and multiple anti-analysis .NET components to enable reconnaissance, lateral movement, and data theft. #Cavern #Cav3rn #CavernManticore #MuddyWater…
Securonix uncovered Veil#Drop, a multi-stage malware delivery framework that uses compromised websites, JavaScript launchers, and PowerShell download cradles hosted on Blogspot to deliver malware. The chain ultimately infects victims with PureLog Stealer, which harvests credentials, cookies, tokens, browser history, and other sensitive data from multiple browsers and applications. #VeilDrop #PureLogStealer #Blogspot…
Vietnamese authorities have arrested seven suspects accused of operating HiAnime, a massive anime piracy streaming service that drew hundreds of millions of monthly visitors before it was shut down. The case follows a multi-year investigation with support from ACE, U.S. authorities, and Vietnamese agencies, and it also links the operators to millions in illegal ad revenue and large-scale copyright infringement. #HiAnime #ACE #VietnamMinistryOfPublicSecurity