
Varonis uncovered a critical flaw in Google Cloud Dialogflow CX, dubbed Rogue Agent, that could let attackers silently control agents, alter conversations, and steal sensitive information. The issue affected Code Blocks running in shared Cloud Run environments and was patched by Google Cloud after disclosure. #DialogflowCX #RogueAgent #GoogleCloud #CloudRun…
Category: Cyber Security News
CISA ordered U.S. federal agencies to patch an actively exploited Langflow vulnerability, CVE-2026-55255, after researchers observed in-the-wild attacks targeting AI app servers. The flaw lets authenticated attackers access other users’ flows, steal sensitive data, and consume resources, with exploitation tied to opportunistic, financially motivated threat activity. #Langflow #CVE-2026-55255 #CISA #Sysdig
KDDI disclosed that attackers exploited a zero-day vulnerability in third-party software to breach an email platform used by five Japanese ISPs, exposing email addresses and passwords for millions of current and former customers. The company has since forced password changes, deployed EDR, and coordinated with Japanese authorities and affected ISPs to contain the incident. #KDDI #STNet #JCOM #ChubuTelecommunicationsC #NIFTYCorporation #BIGLOBE

Daily Recap, Linux and virtualization issues topped the roundup, including a Januscape-disclosed Linux kernel vulnerability that enables VM escape on Intel/AMD systems affecting KVM guest-to-host isolation, alongside rapid probing of a Gitea Docker flaw (CVE-2026-20896) shortly after disclosure. State-sponsored and criminal activity also featured prominently, with Iran-linked actors using a modular Cavern C2 framework, Chinese espionage groups leveraging Roundcube exploit chains and Armored Likho continuing targeting of government and electric power, while BeyondTrust patched critical authentication-bypass issues and CERT/CC warned of a hidden Tenda admin backdoor—plus phishing delivery of EtherRAT and Blogspot-hosted Veil#Drop staging. #Januscape #KVM #Gitea #CVE-2026-20896 #Cavern #Iran #Israeli #Roundcube #Armored Likho #BeyondTrust #PRA #Tenda #EtherRAT #VeilDrop #Blogspot #HiAnime #BONK
CISA has directed U.S. federal agencies to patch the actively exploited Adobe ColdFusion vulnerability CVE-2026-48282 by Friday after reports showed attackers were using it to achieve remote code execution on unpatched systems. Adobe and security researchers warned that exploitation began shortly after disclosure, with hundreds of ColdFusion instances exposed online and additional ColdFusion and Campaign Classic flaws also recently patched. #AdobeColdFusion #CVE-2026-48282 #CISA #RyanDewhurst #Shadowserver
Ubiquiti has patched seven critical vulnerabilities in UniFi OS, including CVE-2026-50746 in UniFi Connect Application that could allow command injection on affected host devices. The company also fixed six additional critical flaws across UniFi Talk, UniFi Access, UniFi Protect, UniFi OS Server, and multiple Ubiquiti devices, urging users to update immediately. #Ubiquiti #UniFiOS #CVE-2026-50746
KDDI said a cyberattack against an email platform it operates for five Japanese internet service providers exposed 12.2 million customer email addresses and 7.6 million passwords. The company traced the intrusion to a vulnerability in third-party software, patched the flaw, and said its separate consumer email services were not affected. #KDDI…

CISA has added four actively exploited vulnerabilities affecting Adobe ColdFusion, Joomlack Page Builder, Langflow, and JoomShaper SP Page Builder to its Known Exploited Vulnerabilities catalog. The attacks include rapid post-disclosure exploitation, zero-day file upload abuse, web shell deployment, and cross-tenant IDOR activity used to steal keys and deliver additional payloads. #CVE-2026-48282…

Researchers at Nebula Security disclosed GhostLock (CVE-2026-43499), a 15-year-old Linux kernel flaw that can let a logged-in local user gain full root access on unpatched systems, and it can also escape containers. Nebula published working exploit code after turning the bug into a 97%-reliable root exploit, and it is also part…

Britain’s National Cyber Security Centre has outlined Cyber Shield, a sovereign defense capability that would use agentic AI to find and fix vulnerabilities across government networks and critical national infrastructure at machine speed. The plan pairs red and blue AI agents for offensive testing and real-time defense, with early trials set…
The Supreme Court has allowed Texas to enforce the App Store Accountability Act while lower courts continue to review its legality. The law requires age verification and parental consent for minors to download apps, and it is being challenged by tech groups and youth advocates over First Amendment concerns. #TASAA #CCIA…

A critical flaw in Google Dialogflow CX, dubbed Rogue Agent by Varonis, could have let an attacker with edit rights on one Code Block-enabled agent compromise other agents in the same Google Cloud project. Google fixed the issue, and there is no sign it was used in a real attack. #DialogflowCX…
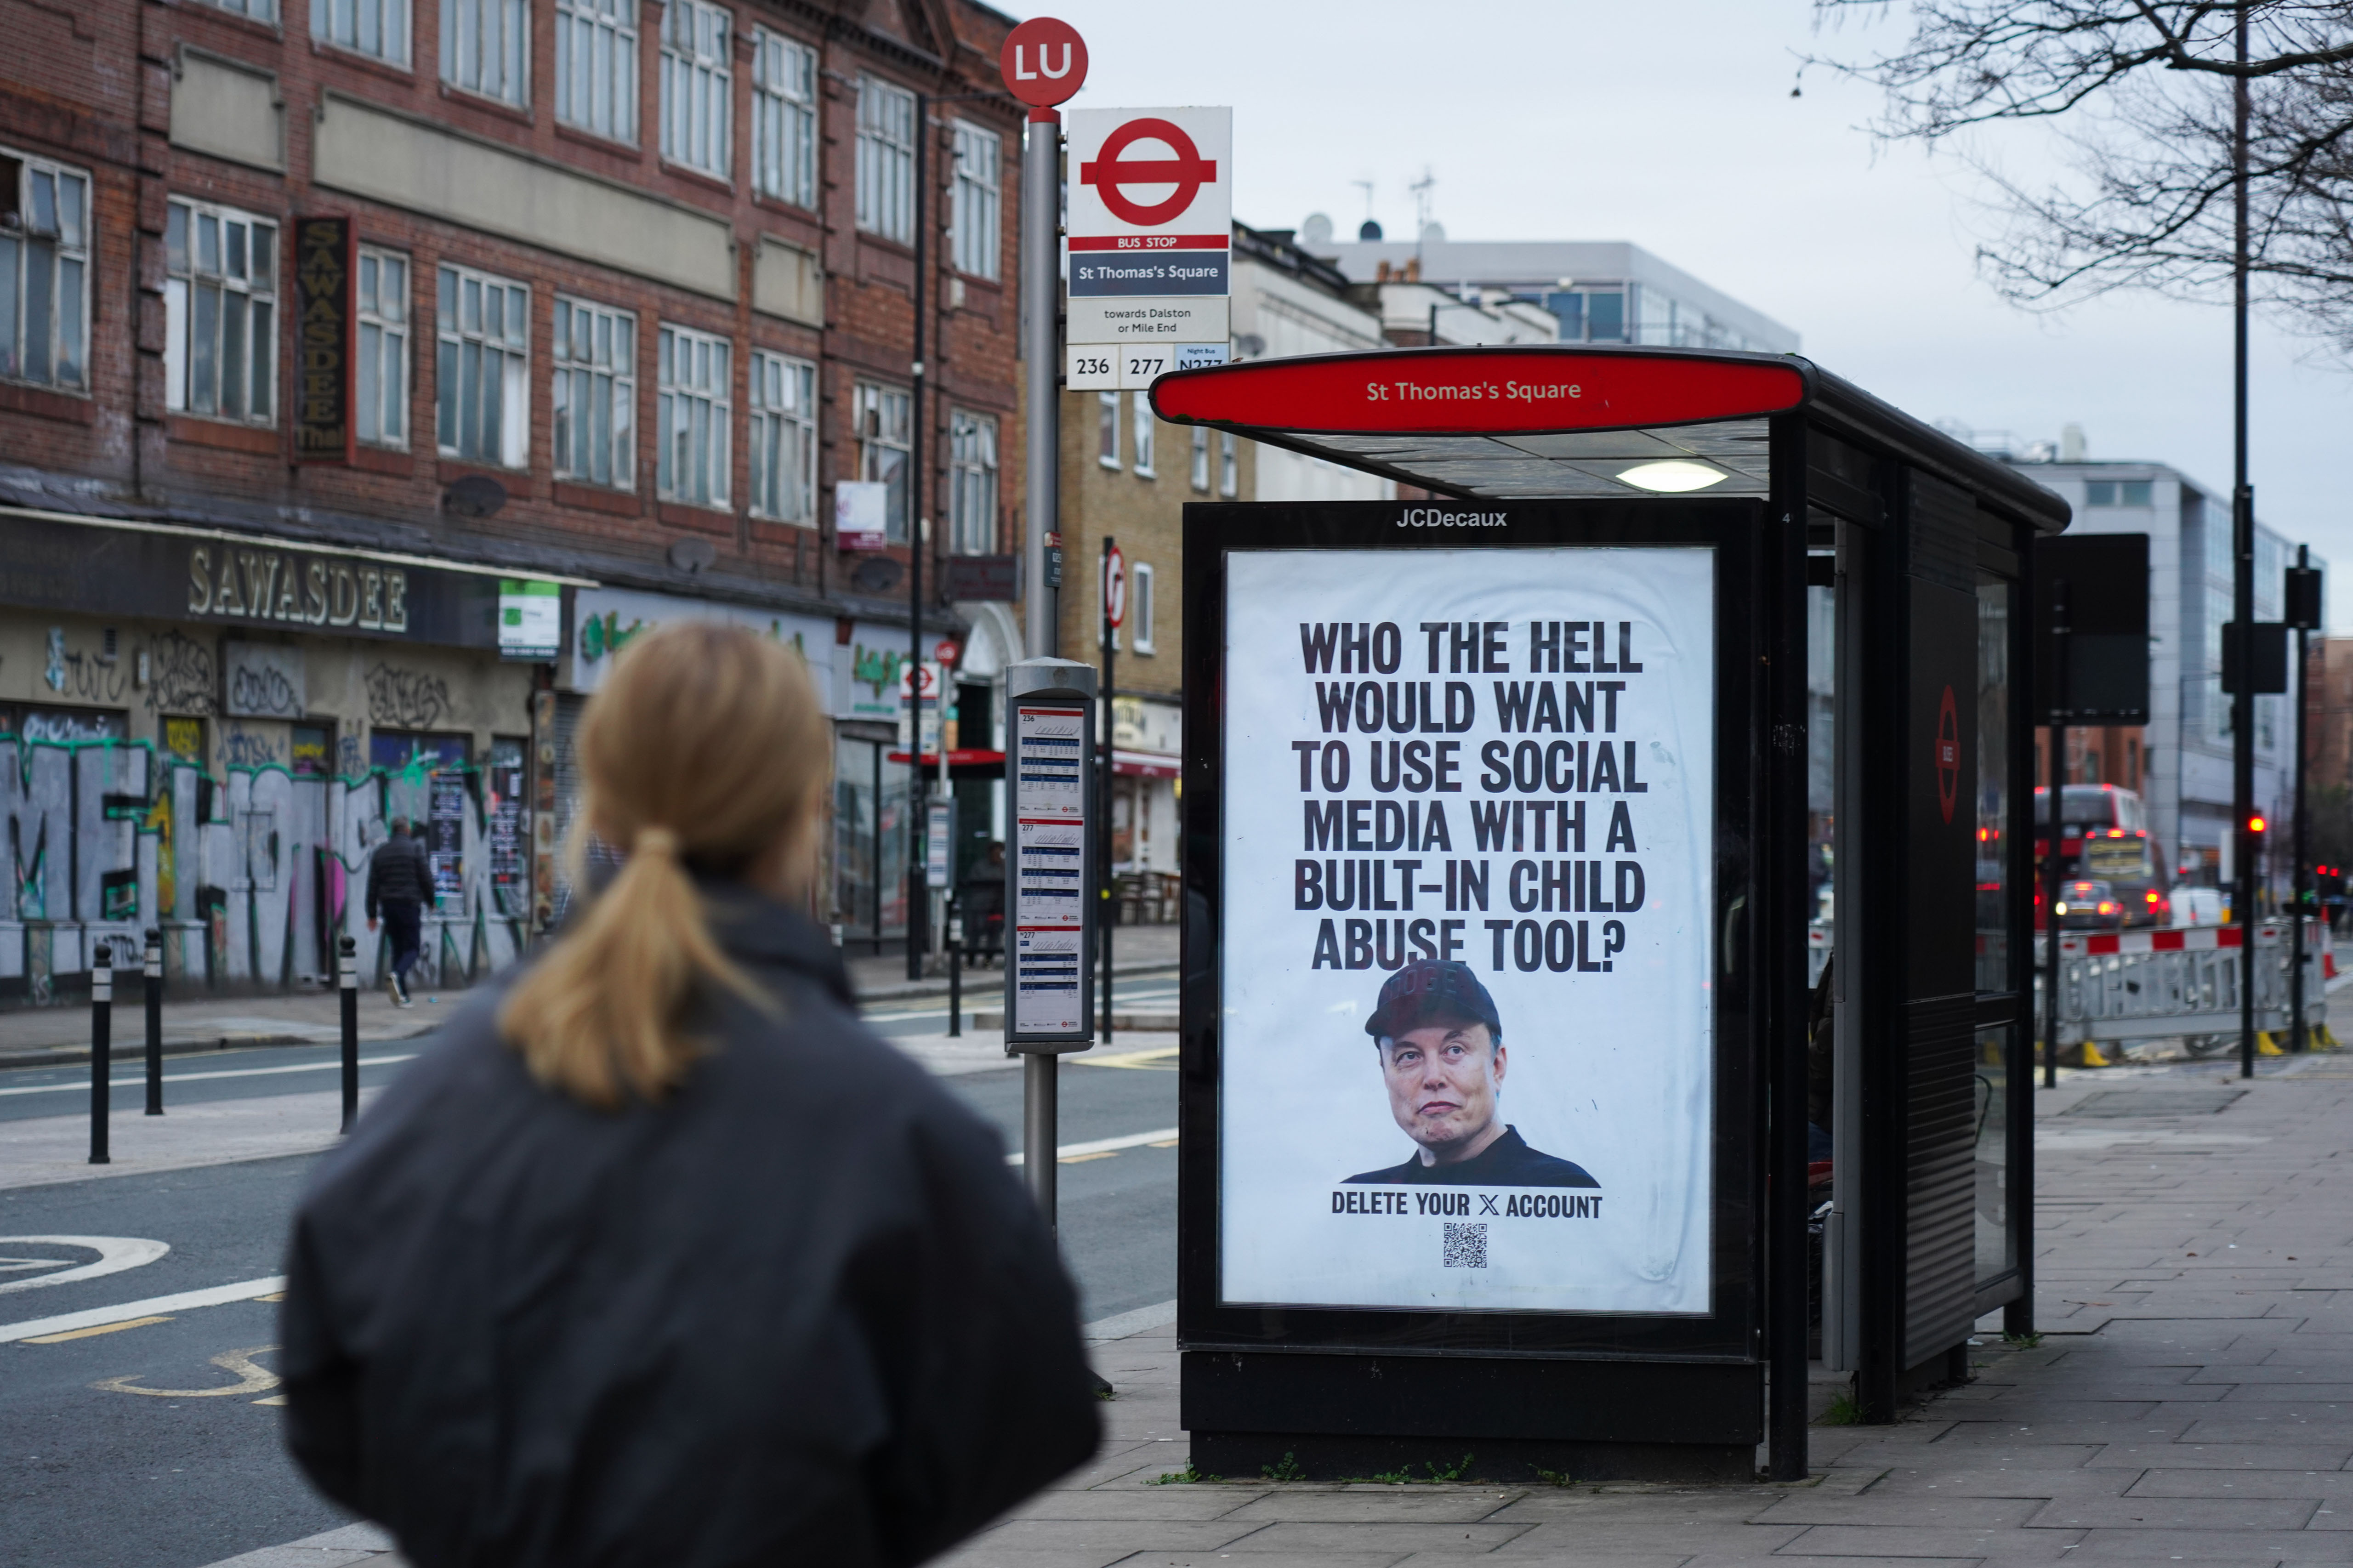
A class-action lawsuit against xAI now includes two more anonymous plaintiffs who allege Grok was used to create and spread nonconsensual deepfake CSAM from real photos of minors. The amended complaint also adds Stability AI, claiming Stable Diffusion helped fuel an ecosystem of “nudify apps” and modified models used to generate abusive content. #xAI #Grok #StabilityAI #StableDiffusion
Spanish police arrested an alleged member of Cyber Army of Russia Reborn after an FBI tip and a joint investigation tied him to support activities for pro-Russian hacktivists and attacks affecting critical infrastructure. The case is part of Operation Riptide, and investigators seized devices, froze cryptocurrency assets, and linked the suspect to Cyber Army of Russia Reborn and NoName057(16). #CyberArmyofRussiaReborn #NoName05716 #OperationRiptide
Accenture confirmed a security breach after a threat actor known as 888 claimed to have stolen 35 GB of source code and related files from the company. The incident reportedly involved sensitive assets such as RSA keys, SSH keys, Azure PATs, Azure Storage access keys, and configuration files, while Accenture said the issue was isolated and remediated. #Accenture #888 #AzureDevOps