
The jscrambler npm package version 8.14.0 was compromised with a preinstall hook that drops a Rust infostealer for Windows, macOS, and Linux, targeting developer secrets, cloud credentials, wallets, and AI tool config files. The malicious release was published directly to npm from a legitimate maintainer account, and users who installed it…
Category: Cyber Security News
Threat actors are abusing the GitHub API with dormant ghost accounts, leaked credentials, and automated scanners to enumerate organizations, repositories, and user accounts over several months. In some cases, the activity escalated from reconnaissance to cloning repositories and exfiltrating data from targeted organizations. #GitHubAPI #Datadog…
The Australian Cyber Security Centre warned of a global campaign exploiting vulnerabilities in CMS platforms and plugins to deploy webshells on vulnerable sites, with many Australian businesses already impacted. The activity targets products including WordPress, Craft CMS, MaxSite CMS, MetInfo CMS, and Joomla JCE, and may be assisted by AI to speed up large-scale exploitation. #ACSC #WordPress #CraftCMS #MaxSiteCMS #MetInfoCMS #JoomlaJCE #Webshells

Daily Recap, Threat activity highlighted targeting of a Pakistani police force by China- and India-linked hackers, new Helix SharePoint-related vishing theft tactics, and GigaWiper’s Windows backdoor that blends disk wiping, fake ransomware, and spyware. Patch and response updates included Zimbra’s critical XSS fix, Palo Alto Networks’ 13 vulnerability updates, Microsoft’s additional Windows security expectations plus OWA Light retirement, and npm supply-chain hardening via Injective SDK and npm 12’s install-script changes, while BlackCat and DigitalMint cases progressed through sentencing. #China #India #Pakistani #Helix #SharePoint #Okta #Microsoft365 #Forg365 #GigaWiper #GitHub #InjectiveSDK #Zimbra #XSS #PaloAltoNetworks #Microsoft #OWALight #ExchangeServer #npm12 #BlackCat #DigitalMint #INTERPOL #NSA #TailoredAccessOperations
Researchers demonstrated Ghostcommit, a pull-request attack that hides malicious instructions inside a PNG so AI code reviewers miss it and later leak repository secrets from .env files. The attack exploited review blind spots in tools like Cursor and Bugbot, while the researchers also released a multimodal defense to inspect images, conventions, and agent behavior. #Ghostcommit #Cursor #ClaudeSonnet #CodeRabbit #Bugbot #ASSETResearchGroup

Zimbra is warning customers to update the Classic Web Client after discovering a critical stored XSS flaw that could let specially crafted emails execute malicious code in a user’s session. The issue can expose mailbox information, session data, and account settings, and users are advised to upgrade to Zimbra Collaboration Suite…
A researcher uncovered nine vulnerabilities in CryptWare CryptoPro Secure Disk, a pre-boot encryption tool used in enterprise environments and possibly within Diebold Nixdorf ATM security components. The findings suggest attackers could potentially bypass encryption, run arbitrary code during pre-boot, and steal cash through ATM jackpotting, though Diebold disputes the direct impact on its machines. #CryptWare #CryptoProSecureDisk #DieboldNixdorf #VynamicSecuritySuite #Ploutus
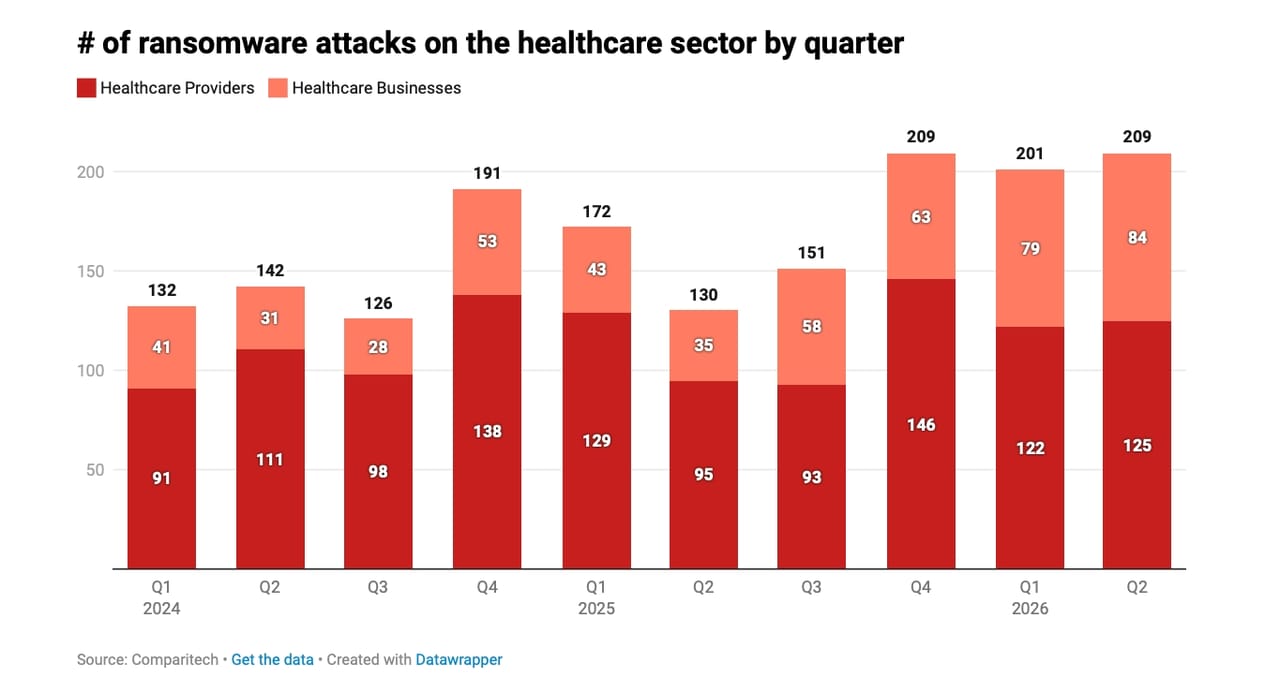
Cyberattacks on healthcare rose sharply in the first half of 2026, with ransomware and data breaches hitting providers, vendors, and medical-billing firms alike. Attackers are increasingly exploiting central service hubs like Unimed and TriZetto Provider Solutions to reach multiple organizations and maximize extortion pressure. #UniversityofMississippiMedicalCenter #Unimed #TriZettoProviderSolutions #QualDermPartners #Qilin #TheGentlemen

A recent Supreme Court ruling in Chatrie v. United States found that geofence searches of cell phone location history require a warrant, and legal scholars say the logic could extend to automated license plate readers (ALPRs). The decision may force major changes in police use of ALPR networks, which can reveal…
U.S. prosecutors marked major progress this week in cases tied to Ryuk and Blackcat/AlphV, including guilty pleas and prison sentencing for key participants. The cases highlight how insider access and ransomware negotiation expertise were used to help attackers extort victims, while companies like DigitalMint have tightened controls after the revelations. #Ryuk…

The European Parliament has voted to restore voluntary CSAM scanning powers for major tech companies, giving firms like Google, Microsoft, and Meta legal cover to continue message checks until 2028. Critics warn the move deepens privacy risks in Europe and could pave the way for a broader “Chat Control 2.0” that…
Six vulnerabilities in U-Boot could let attackers run code during device boot, bypassing security controls and potentially installing persistent firmware malware. Binarly reported the flaws in U-Boot’s FIT signature verification code, and patches have been accepted upstream, though many vendor firmware updates are still needed. #UBoot #Binarly #FIT
Karen Serobovich Vardanyan pleaded guilty to taking part in Ryuk ransomware attacks that targeted three U.S.-based organizations between 2019 and 2020. He agreed to pay nearly $1.2 million in restitution and now faces up to 15 years in prison, with immigration consequences after his sentence. #Ryuk #KarenSerobovichVardanyan
A Bulgarian national, Rossen G. Iossifov, was charged in Kentucky for allegedly stealing $290,000 in government-seized cryptocurrency while already serving prison time for laundering money from American fraud victims. Prosecutors say he routed the funds through multiple exchanges and mixing services, tying the case to the Alexandria Online Auction Fraud Network and his earlier RG Coins laundering operation. #RossenGIossifov #RGCoins #AlexandriaOnlineAuctionFraudNetwork
Hackers are actively exploiting CVE-2026-20896, a critical authentication bypass in Gitea’s official Docker image that can let attackers impersonate any user, including administrators. Gitea and Singapore’s cybersecurity agency have urged users to upgrade to fixed versions or restrict trusted proxy settings while reviewing logs for signs of compromise. #CVE-2026-20896 #Gitea #Sysdig #CSA