Sen. Ron Wyden warned that Canada’s proposed Lawful Access Act could let Canadian authorities secretly pressure U.S. tech companies to enable surveillance of Americans and weaken product security. He urged U.S. officials to review the bill and tighten the U.S.-Canada CLOUD Act agreement to block extraterritorial backdoor and tracking mandates. #LawfulAccessAct…
Category: Cyber Security News

n8n fixed a token-exchange identity-binding flaw, CVE-2026-59208, that could log an Enterprise user into the wrong account when multiple external issuers were trusted. The issue affected releases below 2.27.4 and 2.28.0, and n8n recommends patching or reducing the trusted issuer list if token exchange cannot be turned off. #n8n #CVE-2026-59208 #RFC8693…

This week’s threats leaned on lookalike repos, trojanized installers, weak defaults, and old flaws to quietly turn trusted software and services into attack paths. The activity spanned fake NuGet packages, Starland RAT, WLDR agent, Spirals ransomware, Chrome Sync abuse, and multiple abuse campaigns tied to GitHub, GitHub Releases, and Hugging Face….

Owen Flowers and Thalha Jubair were sentenced to five and a half years for the 2024 Transport for London hack, which disrupted 148 systems, exposed customer data, and cost TfL an estimated £29 million. Prosecutors tied the pair to Scattered Spider, while the case also highlighted related attacks on US healthcare…
OkoBot is a malicious framework that uses ClickFix attacks and fake GitHub software repositories to deliver more than 20 payloads aimed at stealing cryptocurrency wallet seed phrases, credentials, and other sensitive data. Kaspersky says the campaign evolved from TookPS, uses multiple stages including an SSH bot, and has heavily targeted users in Brazil while remaining active globally. #OkoBot #TookPS #Kaspersky #SeedHunter #Rilide
A flaw in Anthropic’s Claude for Chrome extension could let a malicious browser extension trigger built-in AI workflows by faking user clicks, potentially abusing Claude’s access to connected services like Gmail, Google Docs, Google Calendar, and Salesforce. Manifold Security found that the extension failed to verify the browser’s trusted-event flag, and Anthropic has acknowledged the report while the issue remains reproducible in version 1.0.80. #Anthropic #Claude #ClaudeforChrome #ManifoldSecurity #Gmail #GoogleDocs #GoogleCalendar #Salesforce
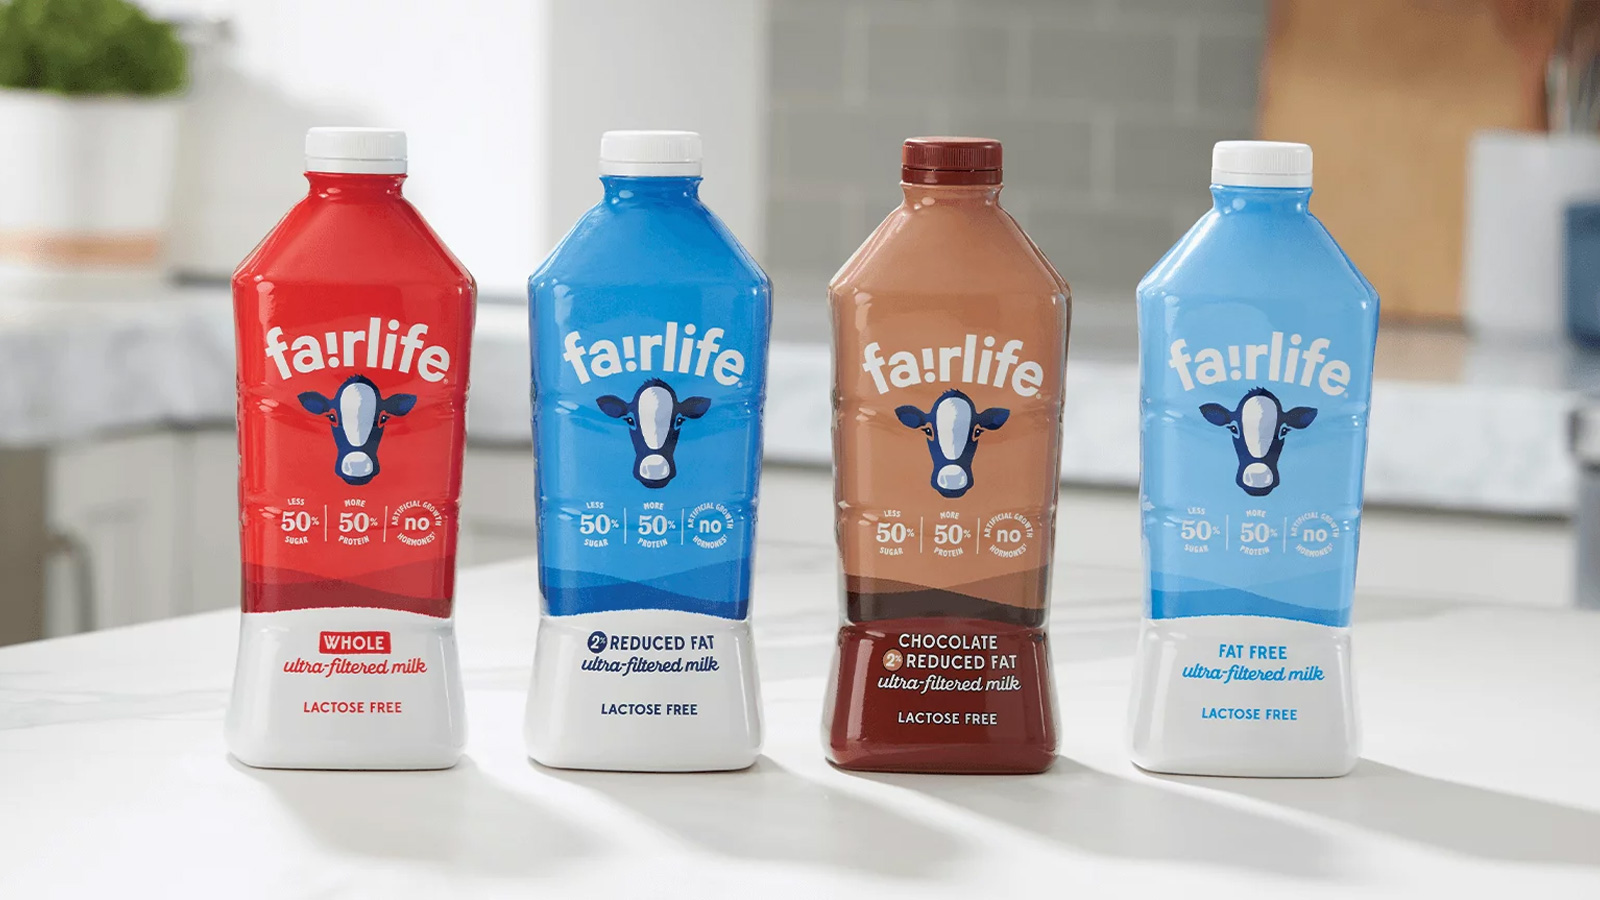
Coca-Cola says a ransomware attack on its Fairlife subsidiary disrupted operations and temporarily suspended production of Fairlife products across the United States. The company has activated response plans, notified law enforcement, and is investigating whether any data was stolen or which ransomware group is responsible. #CocaCola #Fairlife
ClickLock is a new macOS info-stealer that uses fake Cloudflare verification and forced password prompts to steal credentials, cryptocurrency data, browser information, and macOS authentication data. Group-IB found it has already affected at least 100 systems in 33 countries and can also install a persistent GSocket backdoor for remote access. #ClickLock #GroupIB #GSocket
Three Russian nationals and two St. Petersburg-based bulletproof hosting providers were indicted for allegedly supporting attacks on critical infrastructure across 21 states and multiple countries, causing more than $62 million in losses. The companies Media Land and ML.Cloud are accused of providing infrastructure and technical support for malware, ransomware, phishing, and brute-force campaigns. #MediaLand #MLCloud #Volosovik #Pankova #Zatolokin

The Federal Rotational Cyber Workforce program, launched in 2022 to move cyber employees between federal agencies, produced only eight approved participants before fading due to low advertised positions and budgetary constraints. The GAO said OPM never followed through on planned improvements, and the program is set to officially end next summer. #OfficeofPersonnelManagement #GovernmentAccountabilityOffice #Connect.gov
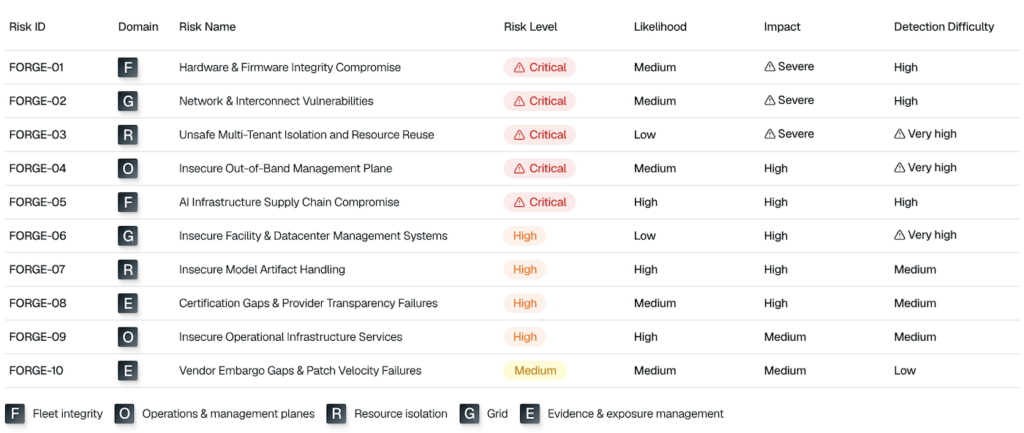
AI’s rapid growth is driving a new wave of data center construction, but AI data centers have fundamentally different security and architectural requirements than traditional facilities. Lava Labs warns that these environments are being built faster than they are being secured, creating major risks around firmware, networking, multi-tenant isolation, and supply…
Two members of the Scattered Spider cybercrime group, Thalha Jubair and Owen Flowers, were sentenced to five years and six months in prison in the UK for their role in the 2024 attack on Transport for London. The breach caused major disruption and £29 million in losses, and authorities say the…
OT security differs from IT because legacy systems, limited protections, and difficult patching make vulnerabilities far more dangerous, especially when denial of service can halt critical operations or endanger lives. As OT and IT converge, researchers are urged to report vulnerabilities responsibly through CISA so vendors and coordinated response teams can…

Daily Recap, Microsoft’s record July Patch Tuesday delivered 622 fixes, including 2–3 actively exploited zero-days, alongside Windows 11 cumulative updates and an extended security update for Windows 10 as organizations rush to remediate. SAP, Adobe, and VMware pushed urgent high-severity patches, SonicWall warned SMA1000 flaws are being exploited as zero-days, CISA urged updates for actively exploited SharePoint issues, and security investigations targeted cybercrime infrastructure linked to ransomware enablers as phishing and malvertising campaigns continued to evolve. #Microsoft #Windows11 #Windows10 #SAP #Adobe #VMware #NetWeaver #ColdFusion #VMwareAvi #AviLoadBalancer #SonicWall #SMA1000 #SharePoint #ProgressShareFile #FirstVPN #ClickFix #LastPass #Bitwarden #Artlist #EDR #BindLink #NATO #GoldEagle
23andMe, now Chrome Holding Co., agreed to pay $18 million to settle claims from 43 attorneys general after a 2023 breach exposed the genetic data of 6.9 million customers. The settlement follows findings that the company lacked basic protections like multifactor authentication and failed to respond to suspicious logins and known vulnerabilities, while later legal actions and bankruptcy proceedings continued to shape the case. #23andMe #LetitiaJames #TTAMResearchInstitute #ICO