Hackers are actively exploiting CVE-2026-50522 in Microsoft SharePoint to steal machine keys and keep access even after patching. The attacks can enable forged authentication tokens, and the public PoC has been quickly used against vulnerable on-premises SharePoint servers. #CVE-2026-50522 #MicrosoftSharePoint #watchTowr #Defused #Janggggg
Category: Cyber Security News
North Korea’s IT worker scheme is sending money through front companies, intermediaries, and sanctioned entities that help fund the regime’s broader priorities, including weapons production and support for Russia’s war effort in Ukraine. DTEX traced payments from an internal server to entities such as Korea Ryonbong General Corp, Sobaeksu, Saenal, and Songkwang, showing the money flows upward through a wider DPRK network. #KoreaRyonbongGeneralCorp #Sobaeksu #Saenal #Songkwang #PC1234
The House Intelligence Committee approved a fiscal 2027 intelligence bill that would launch a cyberthreat intelligence-sharing pilot for one state and require assessments of current federal information-sharing practices with state and local governments. The legislation also adds election security measures, expands AI use for intelligence and cyber missions, and orders a review of foreign cyberthreats to critical energy infrastructure. #ODNI #DHS #FBI #NSA #JimHimes #JasonCrow #ChrissyHoulahan #RickCrawford
Hackers are actively exploiting the WordPress Core “wp2shell” vulnerability suite, using unauthenticated REST API abuse to deploy persistent webshells, malicious plugins, and rogue administrator accounts. WordPress has released patched versions and forced automatic updates, while researchers continue to track ongoing attack activity and live patching rates. #wp2shell #WordPressCore #SearchLightCyber #Wiz #Defiant #SansTechnologyInstitute #CMSmap

Hidden text on a web page could trick AWS Kiro into rewriting its own MCP configuration and executing attacker-controlled code on a developer’s machine, bypassing the normal approval flow. AWS has patched the flaw in newer releases, with Intezer confirming the issue was fixed in v0.11.130 and noting no CVE was…
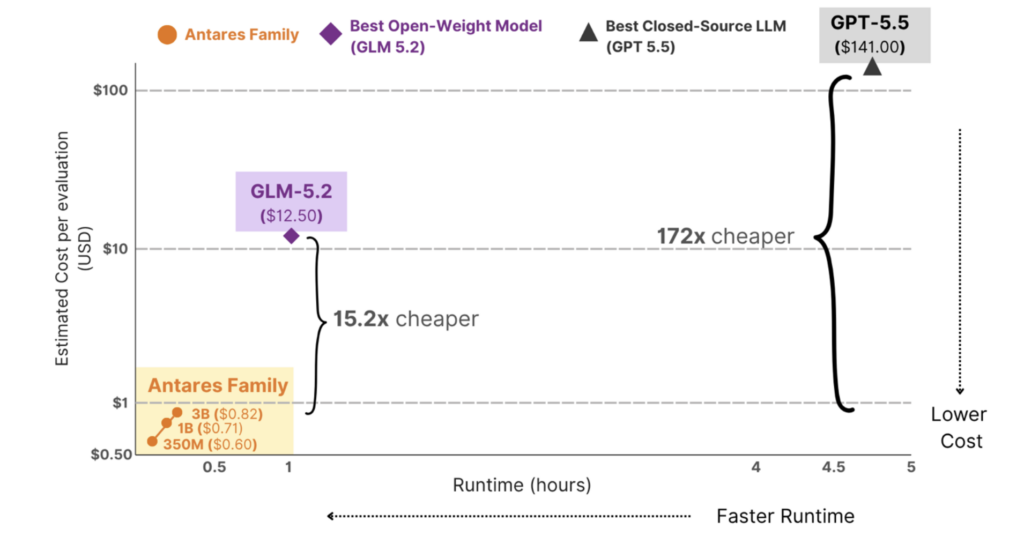
Cisco Foundation AI has introduced Antares, an open-weight small language model family designed to help security teams locate known vulnerabilities in codebases quickly and at lower cost. Cisco says the models, Antares-350M and Antares-1B, are especially useful for budget-constrained organizations and are backed by a new Vulnerability Localization Benchmark. #CiscoFoundationAI #Antares…
President Donald Trump’s executive order directs the Department of War to strengthen mapping, vetting, and reporting rules for critical defense supply chains, with a broad focus that reaches software, services, and technology used in national security systems. The order also raises new cybersecurity concerns by exposing sensitive supply chain data as…
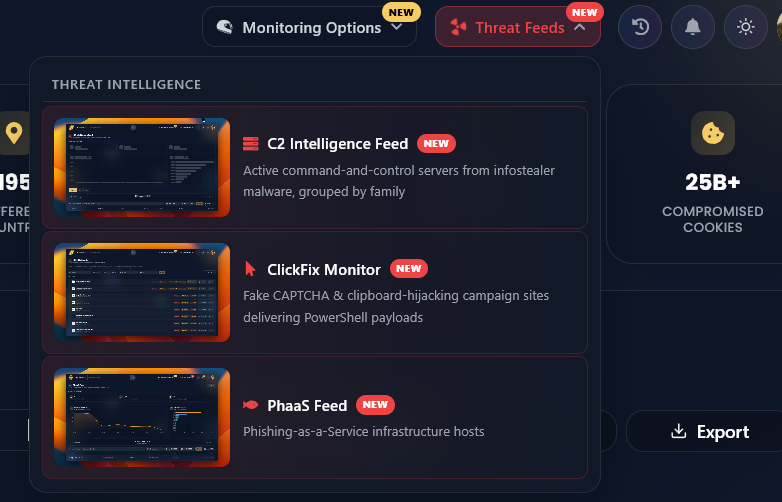
Hudson Rock has introduced three new Threat Feed modules in Cavalier: C2 Data, ClickFix, and PhaaS, giving security teams visibility into active attacker infrastructure and phishing operations. The new PhaaS intelligence helps defenders track kits like Eviltokens, Kali365, and SessionSerpent, while linking hosting infrastructure to infostealer telemetry for proactive blocking. #Cavalier #HudsonRock #Eviltokens #Kali365 #SessionSerpent #ClickFix
The U.S. Justice Department seized more than 1,000 websites and blocked 1,970 domains used to illegally stream FIFA World Cup 2026 matches, as part of coordinated operations with FIFA, ACE, and other media partners. Authorities also warned that these illicit streaming sites can expose users to malware, unsafe connections, and scams while disrupting piracy networks in multiple countries. #FIFA #OperationOffsides #OperationRedCard #LosCiberinfiltrados #PirloTV
The Colonial Pipeline attack and the rise of Volt Typhoon show how stolen credentials, weak access controls, and unmanaged devices can give attackers long-term access to critical infrastructure. Zero trust, MFA, and device-bound access are now essential to reduce risk across OT, IT, cloud, and SaaS environments. #ColonialPipeline #VoltTyphoon #CISA #SpecopsDeviceTrust
HollowGraph is a newly discovered malware that abuses Microsoft 365 calendar events and the Microsoft Graph API for covert command-and-control communication. Group-IB says it may be linked to Cavern Manticore and shows signs of targeted activity against Israeli entities, using encrypted calendar attachments, DNS tunneling, and Microsoft Entra ID credentials. #HollowGraph…
SecurityWeek has launched the Critical Impact Awards to recognize individuals, organizations, and technologies making measurable contributions to industrial cybersecurity. Winners will be announced live at the 2026 ICS Cybersecurity Conference in Nashville, with judging based on merit, evidence, and independent review. #SecurityWeek #CriticalImpactAwards #ICSCybersecurityConference #WNashville…
Empirical has raised $25 million in Series A funding, bringing its total funding to $37 million, to expand predictive cybersecurity tools built for the agentic AI era. The Chicago-based startup will further develop Foundation and Radiant, which help organizations forecast threats and prioritize remediation using data-driven risk intelligence. #Empirical #Foundation #Radiant…
Free unofficial micropatches are available for LegacyHive, a Windows zero-day in the User Profile Service that can let non-admin attackers escalate privileges and trigger code execution when an administrator logs in. The flaw was disclosed by Nightmare Eclipse, confirmed by researchers and Kevin Beaumont, and Microsoft says it is investigating while ACROS Security’s 0Patch offers protection for supported Windows versions. #LegacyHive #NightmareEclipse #0Patch #MicrosoftDefenderForEndpoint
Microsoft has shared manual mitigations for WSUS servers affected by a sync issue that causes Windows Update scans to fail or time out. The fix helps organizations clean up excess metadata, restore normal synchronization, and resume deploying Windows updates through WSUS and Configuration Manager. #Microsoft #WSUS #WindowsUpdate