Sandworm_Mode is a self-propagating worm spreading through code repositories and software supply chains, targeting AI coding assistants, cloud services, CI/CD pipelines, and major LLM provider credentials. CrowdStrike says the malware blends into noisy development environments, delays actions to evade detection, and may be designed to secure long-term access. #Sandworm_Mode #CrowdStrike #TeamPCP #LLMProviders
Category: Cyber Security News
A Government Accountability Office report found that seven out of 10 federal cyber regulations requiring written reports to agencies are duplicated elsewhere, creating overlapping obligations for the private sector. Efforts by the Office of the National Cyber Director and the Department of Homeland Security to harmonize these rules have made limited progress, even as CIRCIA and other reporting requirements continue to add complexity. #GAO #CIRCIA #OfficeoftheNationalCyberDirector #DepartmentofHomelandSecurity
Stadler Rail says the Everest ransomware gang demanded about $12.3 million after breaching a data exchange platform shared with one of its suppliers, but the company refused to pay and filed a criminal complaint. The incident did not affect Stadler’s IT systems or production, and the stolen data reportedly included only non-security-relevant technical information. #StadlerRail #Everest

VulnCheck says CVE-2026-29059 in Windmill is being actively exploited to abuse the get_log_file endpoint for arbitrary file reads, with attackers trying to access sensitive data such as /etc/passwd and, in some cases, SUPERADMIN_SECRET. CISA has also added multiple flaws to its KEV catalog, while exploitation activity is surging against WordPress wp2shell…
Palo Alto Networks announced its intent to acquire Embrace to add Real User Monitoring capabilities to its Observability platform and expand into Digital Experience Monitoring. It also introduced Synthetics, a new in-house capability that validates application performance globally and complements the company’s broader observability push. #PaloAltoNetworks #Embrace #Chronosphere #CortexAgentiX…
Hackers reportedly stole source code and user data from Suno, exposing 55.3 million unique email addresses along with phone numbers and payment records. A separate leak tied to Paidwork may have exposed data on 23.3 million users, including names, password hashes, bank account numbers, and financial transaction details. #Suno #Paidwork #HaveIBeenPwned…
Guardio researchers found that the Adobe Acrobat Chrome extension could be abused to access WhatsApp Web conversations and rendered data without authentication through a chain of flaws dubbed HermeticReader. The issue, tracked as CVE-2026-48294, affects Adobe Acrobat Chrome extensions version 26.5.2.1 and below and has been fixed in version 26.5.2.3. #AdobeAcrobat #Guardio #HermeticReader #CVE202648294 #WhatsAppWeb
Eclypsium launched InfraTrust and its monthly InfraTrust Pulse to help organizations prioritize infrastructure, firmware, networking, and edge-device vulnerabilities based on exploitability, exposure, and real-world risk rather than CVSS alone. The inaugural July 2026 report tracked 61 advisories from 14 vendors and highlighted actively exploited flaws in SonicWall SMA1000 and Fortinet FortiSandbox, alongside risks affecting Dell, F5, Juniper, and NVIDIA systems. #SonicWall #Fortinet #Dell #F5 #Juniper #NVIDIA #InfraTrustPulse
Enterprise AI can improve productivity, but it also expands ransomware risk when assistants and agents inherit broad identities, permissions, and access to sensitive business systems. The article explains that AI mainly accelerates existing attack stages like reconnaissance, credential abuse, and data theft, and recommends least privilege, monitoring, and human approval for high-risk actions. #GTG-2002 #GLOBALGROUP #AcronisGenAIProtection #Microsoft365 #CloudSecurityAlliance
A coordinated identity attack against a wireless services account combined social engineering, SIM swapping, OTP abuse, and session hijacking, exposing how one-time authentication can fail against determined adversaries. The incident shows why organizations must continuously evaluate identity risk across the full session and protect high-risk actions with stronger verification. #ScatteredSpider #ShinyHunters…

A vulnerability in Adobe’s Acrobat Chrome extension could have let attackers silently steal WhatsApp chats, contacts, and account details by luring victims to a malicious webpage. Guardio dubbed the attack HermeticReader, and Adobe later patched the UXSS-class flaw as CVE-2026-48294. #AdobeAcrobat #Guardio #HermeticReader #WhatsAppWeb #CVE-2026-48294…
Microsoft has confirmed that the Extended Security Update program for Exchange Server 2016 and 2019 will end in October 2026, with no further extensions planned. IT admins are being urged to migrate to Exchange Server Subscription Edition or move to Exchange Online before support stops completely. #Exchange2016 #Exchange2019 #ExchangeServerSE #ExchangeOnline
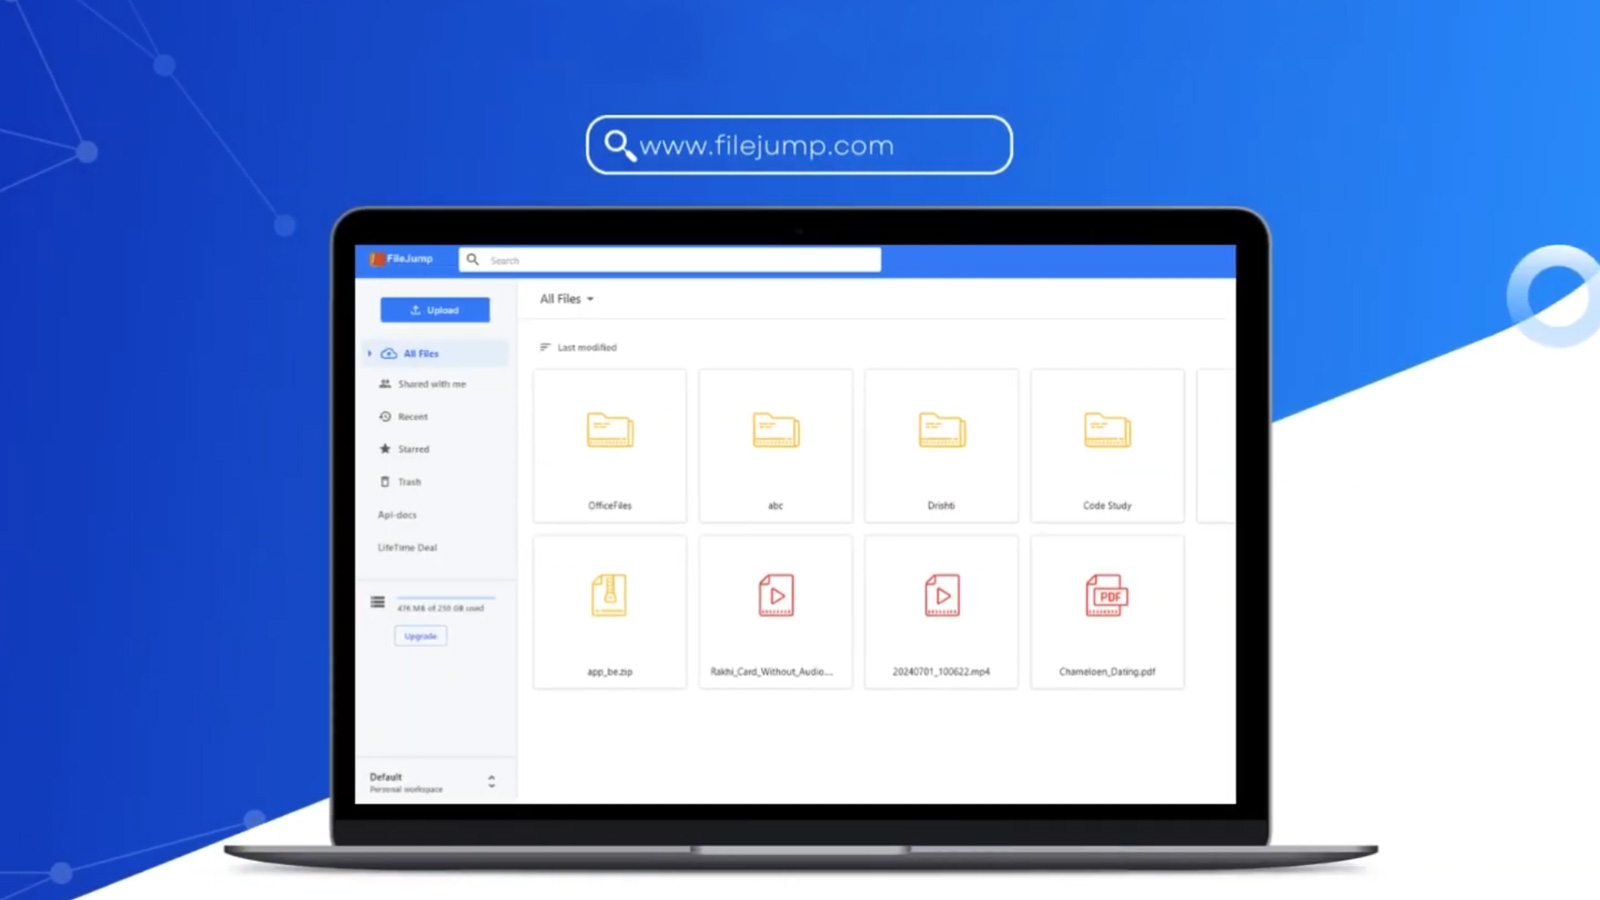
FileJump offers 2TB of lifetime cloud storage for a one-time $59 payment, replacing recurring subscription fees with a single purchase. The service includes zero-knowledge encryption, file preview and version history features, sharing tools, WebDAV support, and cross-platform access through web, mobile, and desktop apps. #FileJump #OnlyOffice #WebDAV
CISA has ordered U.S. federal agencies to urgently patch CVE-2026-0770, a critical Langflow flaw that lets unauthenticated attackers achieve root remote code execution. KEVIntel reported active exploitation and observed attempts to deploy malware, steal AWS credentials, and collect environment variables and container metadata. #CVE-2026-0770 #Langflow #CISA #KEVIntel
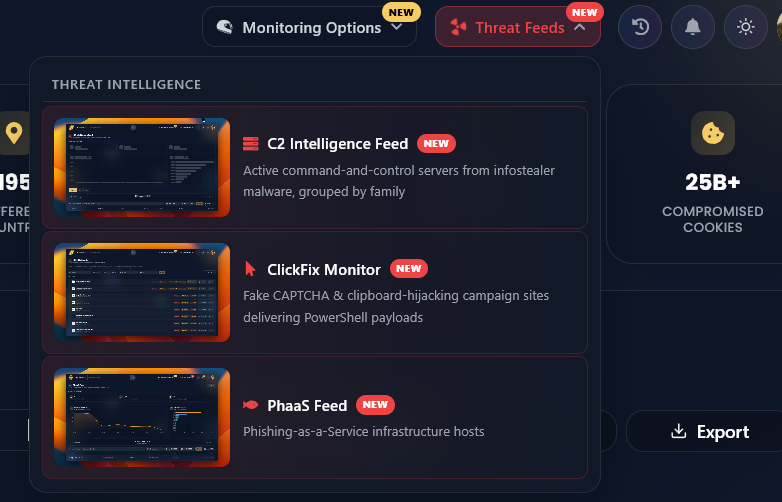
Cavalier has introduced three new Threat Feed modules—C2 Data, ClickFix, and PhaaS—to help security teams track active attacker infrastructure, malicious verification pages, and phishing kits in real time. The new ClickFix Monitor also links malicious sites to infostealer credential telemetry, helping identify how compromised accounts led to takeovers such as the Artlist breach. #Cavalier #ClickFix #PhaaS #Artlist #HudsonRock