Artificial intelligence is accelerating enterprise adoption of confidential computing by making data protection for models, agents, and sensitive workloads more practical and valuable. But as AI agents retain context and memory, companies are now facing new security challenges that are forcing a rethink of how confidential computing should protect AI “minds.” #ConfidentialComputing #GoogleCloud #MicrosoftAzure #Nvidia #Apple #ServiceNow
Category: Cyber Security News

A Russian state-backed espionage group used CVE-2025-66376 in Zimbra’s Classic UI to read Western mailboxes for months, stealing recent email, directories, saved passwords, and 2FA recovery codes. The campaign, tracked as TA488 and CL-STA-1114, used crafted HTML emails with the ZimReaper payload and targeted government, defense, transportation, financial, and US organizations…
Chick-fil-A disclosed a data breach after a credential stuffing attack targeted Chick-fil-A One customer accounts on its mobile app and website. The attackers may have accessed personal and payment-related data, and the company reset passwords, logged out affected users, and restored drained balances. #ChickfilA #ChickfilAOne…
The State Department will restrict visas for cybercriminals involved in cyberscams, sextortion, and other cyber-enabled crimes, with some family members also potentially affected. The move, backed by Secretary of State Marco Rubio, is aimed at disrupting transnational scam networks such as those tied to the Huione Group and deterring foreign-based fraud. #HuioneGroup #MarcoRubio
Ukraine’s CERT has identified a campaign by UAC-0099 that distributes a ZIP archive containing legitimate Notepad++ components alongside a malicious plugin, LunchPoke, to gain persistence and deploy additional tooling. The activity uses disguised files and scheduled tasks rather than a software vulnerability or supply-chain compromise, and CERT-UA recommends updating Notepad++, 7-Zip, and WinRAR to reduce risk. #UAC-0099 #LunchPoke #Notepad++ #CERT-UA #APT44 #Sandworm
CISA says the Russian state-sponsored group Laundry Bear, also known as Void Blizzard, is targeting Zimbra Collaboration servers with phishing and the now-patched CVE-2025-66376 XSS flaw to steal email data and bypass MFA. The campaign has hit organizations across government, defense, education, energy, media, and NGOs, while exfiltrating stolen information through the group’s Flowerbed framework and AiTM phishing kits. #LaundryBear #VoidBlizzard #Zimbra #CVE202566376 #Flowerbed
A malvertising campaign on Bing is using a fake Claude desktop app installer hosted on a legitimate Claude.ai domain to spread SectopRAT malware. Researchers say the FakeAgent operation compromised at least 29 organizations and used anti-analysis tricks, malicious loaders, and EtherHiding-based C2 retrieval to support the infection chain. #Claude #SectopRAT #FakeAgent #Huntress #Anthropic
Origin Energy has confirmed a data breach that exposed customers’ personal information, including names, addresses, dates of birth, phone numbers, and partial financial details. The company is investigating the impact, notifying affected customers, and working with Australian authorities after a threat actor called “John Doe” claimed responsibility and threatened to leak the data. #OriginEnergy #JohnDoe #AFP #AustralianCyberSecurityCentre #OAIC
Dolphin X is a remote access trojan that advertises an AI-powered profiler to score infected victims and help attackers prioritize the most valuable targets. Varonis Threat Labs found that its operator panel also includes credential-stealing capabilities aimed at more than 300 applications, including browsers, crypto wallets, password managers, and cloud tools. #DolphinX #VaronisThreatLabs #DanielKelley #Kontraktnik
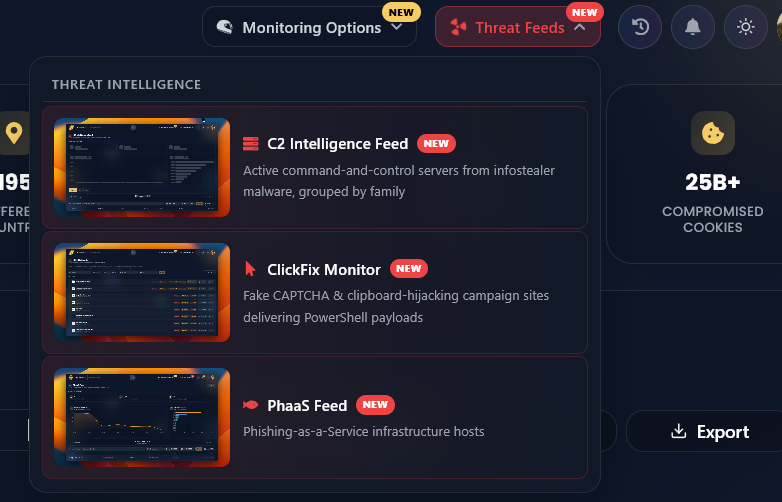
Hudson Rock has launched three new Cavalier Threat Feed modules—C2 Data, ClickFix, and PhaaS—to help security teams identify active attacker infrastructure and block threats before they reach users. The feeds expose infostealer C2 servers, malicious ClickFix pages, and phishing-host networks, while also linking many of them to compromised credentials that enabled the initial takeover. #Cavalier #HudsonRock #ClickFix #PhaaS #Vidar #Redline #Stealc #Artlist #EtherHiding
A Russian state-sponsored threat group known as Laundry Bear, also called Void Blizzard, has been exploiting a zero-day flaw in Zimbra Collaboration Suite since July 2025 to steal sensitive data from governments and commercial organizations. The campaign, which was patched only in November 2025, has targeted multiple sectors and prompted a joint advisory from the United States and more than a dozen allied countries. #LaundryBear #VoidBlizzard #ZimbraCollaborationSuite #CVE-2025-66376
On July 14, 2026, the White House launched Gold Eagle, a federal AI-driven clearinghouse to identify and prioritize software vulnerabilities across government and critical infrastructure before attackers can exploit them. The article argues that frontier AI, rising exploit speed, and massive CVE volume are forcing organizations to shift from traditional patching…

Zenity Labs disclosed AgentForger, a critical CSRF flaw in OpenAI’s ChatGPT Workspace Agents that could let a phished employee unknowingly create an invisible autonomous agent controlled by an attacker. The attack could abuse ChatGPT Agent Builder parameters to hide the agent, accept attacker emails as commands, and enable covert access to…
Microsoft Teams and several Microsoft 365 services, including SharePoint, Excel, and the Microsoft 365 Admin Center, are experiencing an ongoing outage that is affecting users. Microsoft has acknowledged the disruption and is investigating the issue under incident MO1437424. #MicrosoftTeams #SharePoint #Excel #Microsoft365
Check Point Software has patched CVE-2026-16232, an actively exploited authentication bypass in SmartConsole that can let unauthenticated attackers obtain an administrator application token. CISA has added the flaw to its KEV catalog and urged organizations to patch immediately, with attackers able to alter security policies if the Management Server is exposed and Trusted Clients are not restricted. #CheckPointSoftware #SmartConsole #CVE2026-16232 #CISA