
Tengu is a Mirai-derived botnet that uses multiple persistence tricks, including a hardware watchdog reboot loop, to survive process termination on compromised Linux devices. Nozomi Networks Labs found it supports many DDoS methods, proxying, command execution, and payload retrieval, with samples tied to C2 infrastructure at 64[.]89.163.8 and telemetry also showing…
Category: Cyber Security News

Anthropic said Claude Mythos Preview helped derive a key-recovery attack against HAWK-256 by exploiting a hidden lattice symmetry, and the company released reproducibility code while stressing that the result does not affect production systems. It also reported a 200- to 800-fold speedup for an attack on seven-round AES-128, but said the…
SSO improves convenience and centralizes access, but the 2025 University of Pennsylvania breach shows how a compromised PennKey account can expose many internal systems and large amounts of data. Strong passwords, phishing-resistant MFA, and tighter control over identity provider assets, certificates, OAuth secrets, and delegated permissions are essential to secure SSO. #UniversityofPennsylvania #PennKey #FIDO2 #WebAuthn #passkeys #SAML #OIDC
Frenos raised an additional $1.52 million in seed funding, bringing its total to $6.4 million, with support from Momenta, Exposition Ventures, and Riptide Ventures. The OT security startup also launched SAIRA Co-Work, an AI reasoning agent that helps deliver evidence-based insights during complex investigations. #Frenos #SAIRACoWork #Momenta #ExpositionVentures #RiptideVentures…
Apple released major security updates across iOS, iPadOS, macOS, watchOS, tvOS, visionOS, and Safari, fixing hundreds of vulnerabilities that could enable sensitive data access, arbitrary code execution, privilege escalation, and other attacks. The most notable issue highlighted was CVE-2026-43810, which could allow remote kernel memory corruption, though Apple did not report…
Cyera has agreed to acquire Oasis Security in a $1 billion deal, combining data security with agentic access management for enterprise AI environments. The acquisition will unify identity and data security to govern what human users, machines, and AI agents can see and do across critical systems. #Cyera #OasisSecurity #AgenticAccessManagement…
More than 24,000 internet-exposed servers are leaking authentication password hashes because of CVE-2013-4786, an old IPMI 2.0 flaw in Baseboard Management Controller interfaces. Researchers also found evidence of weak factory and dictionary-based credentials, and an exposed HPE iLO 4 page showing a ransom note, suggesting active abuse of these systems. #CVE-2013-4786 #IPMI #BMC #Supermicro #HPEiLO4

Daily Recap, Organizations are facing a surge in shadow AI agents, with guidance on discovery and security as Nvidia and other tech giants push an AI security alliance to protect expanding AI systems and agent deployments. Meanwhile, attackers continue to evade detection with MedusaHVNC, supply-chain defenses were strengthened by GitHub and PyPI using time-based protections, and new breach disclosures from Coca-Cola and MCBS keep ransomware and large-scale exposure in focus.
#ShadowAI #Nvidia #AIAlliance #MedusaHVNC #GitHub #PyPI #CocaCola #Fairlife #MCBS #Wyden #ZeroTrust #VPN
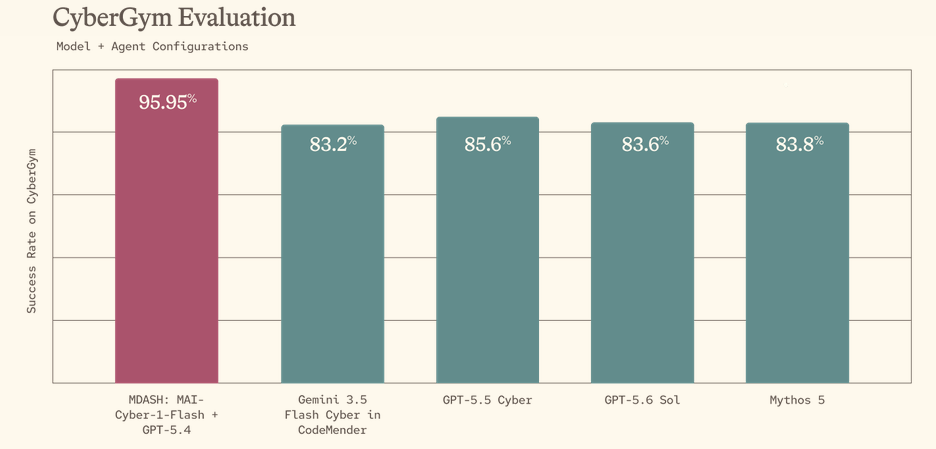
Microsoft has introduced MAI-Cyber-1-Flash, its first cybersecurity AI model, and says it outperformed Google’s 3.5 Flash Cyber, OpenAI’s GPT-5.6 Sol, and Anthropic’s Mythos 5 in vulnerability discovery. The model is integrated into MDASH and will be available through Project Perception, which enters public preview on August 3. #Microsoft #MAI-Cyber-1-Flash #MDASH #ProjectPerception…
Medical Computer Business Services (MCBS) says a 2025 network breach exposed sensitive data belonging to 1,261,464 people, including names, Social Security numbers, medical history, and insurance details. The PEAR ransomware group claimed the attack and alleged it stole 3.3 terabytes of data from MCBS systems. #MCBS #PEARRansomware
Origin Energy said a data breach has affected 900,000 current and former customers, exposing personal and account-related information. The company is still investigating the incident as a criminal matter, while warning that stolen data could be used in scams even if it is not publicly leaked. #OriginEnergy…
Arista Networks has released patches for a critical OS injection flaw in VeloCloud Orchestrator On-Prem, tracked as CVE-2026-16812, after confirming it was actively exploited as a zero-day. CISA has also added the vulnerability to its KEV catalog, while urging federal agencies to patch it quickly and investigate logs for signs of…
Threat actors are actively exploiting a critical Fastjson remote code execution flaw, tracked as CVE-2026-16723, affecting widely used Spring Boot fat-jar deployments and Fastjson 1.x versions. Organizations in multiple sectors have already been targeted, and defenders are urged to move to Fastjson 2.x or enable SafeMode to reduce risk. #Fastjson #CVE-2026-16723…
The US government has updated its advisory on Iran-linked attacks against critical infrastructure, warning that hackers have targeted industrial control systems from Siemens, Schneider Electric, and Rockwell Automation. Investigators say the attackers used malicious PLC project files, altered HMI and SCADA data, and disabled safety logic in multiple OT environments. #Siemens…
Check Point has disclosed an actively exploited zero-day authentication bypass in SmartConsole, tracked as CVE-2026-16232, that can let unauthenticated attackers obtain an application login token and gain administrator access. The flaw affects exposed Security Management Server and Multi-Domain Security Management Server deployments, and CISA has added it to its known exploited vulnerabilities catalog while urging rapid patching. #CheckPoint #SmartConsole #CVE-2026-16232 #CISA