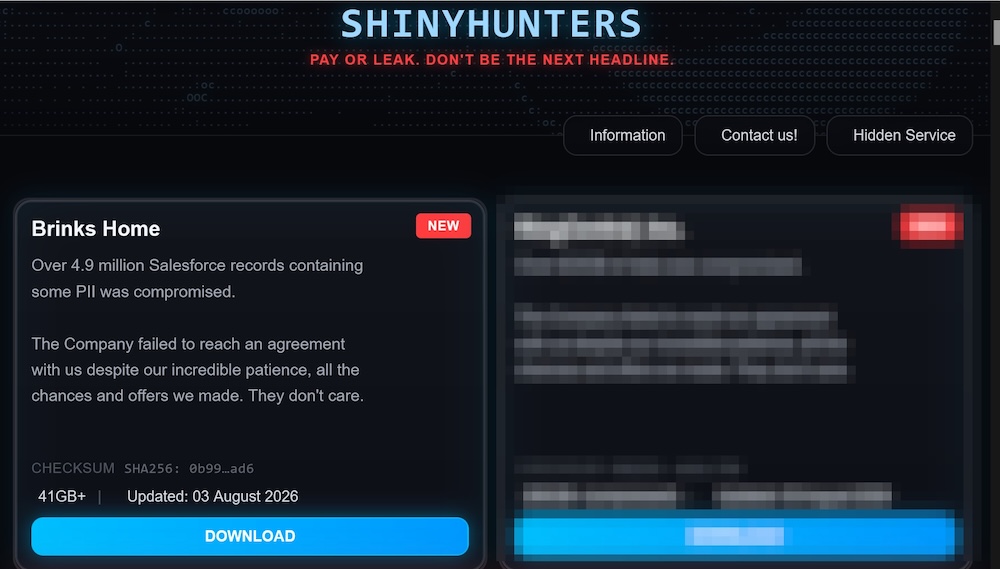
ShinyHunters claims to have leaked over 41 gigabytes of data allegedly stolen from Brinks Home after the company refused to pay a ransom. Brinks Home says its alarm monitoring services were not affected, while it investigates the breach and warns customers to watch for suspicious requests for personal information. #ShinyHunters #BrinksHome…
Category: Cyber Security News
AI is creating far more detection noise for CrowdStrike than human-triggered incidents, with millions of daily leads and tens of thousands of customer alerts over the past year. The report says AI is now both a weapon and a target, accelerating vulnerability exploitation, supply chain attacks, and threats against AI systems themselves. #CrowdStrike #TeamPCP

N-able disclosed that attackers used an authentication bypass in N-central to gain remote administrative access, then pivoted through Take Control to reach managed endpoints and install persistent Cloudflare tunnel services. The company has released an emergency fix in build 2026.3.1.7 and urged customers to hunt for compromise indicators, as the initial…
Researchers believe a COLDCARD firmware vulnerability tied to flawed random number generation may have enabled attackers to steal an estimated $88.6 million in Bitcoin from thousands of wallets. Galaxy Research and Chainalysis say the thefts were likely automated, with attackers targeting high-value wallets before Coinkite disclosed the flaw. #COLDCARD #Coinkite #GalaxyResearch #Chainalysis

Daily Recap, Funding and strategy moves included Balance Theory raising $19 million to help enterprises manage cybersecurity investment decisions, while U.S. Cyber Command plans a Silicon Valley office to strengthen industry collaboration. Key threats and security updates spanned a Rails critical flaw, Adobe Campaign Classic’s CVSS 10.0 code-execution issue, and multiple intrusion stories including Adform script poisoning, the HollowFrame loader deploying Matryoshka, and OctLurk/SilkLurk targeting Central Asian governments. #BalanceTheory #U.S.CyberCommand #RubyOnRails #AdobeCampaignClassic #Adform #HollowFrame #Matryoshka #OctLurk #SilkLurk #Minnesota #CISA #ArchLinux #AUR #Amgen

A firmware flaw in Coldcard hardware wallets enabled an attacker to drain 1,196 Bitcoin addresses in 41 minutes on July 30, stealing 1,082.65 BTC worth about $70.2 million. Galaxy Research and Block linked the incident to a deterministic PRNG bug in Coinkite’s Coldcard firmware, which could allow offline seed reconstruction from…
A critical flaw in Rails Active Storage, tracked as CVE-2026-66066, can let an unauthenticated attacker read arbitrary files and potentially achieve remote code execution when libvips is used. Rails maintainers and Akamai warn that affected systems should be upgraded quickly, secrets rotated, and temporary protections applied where possible. #CVE-2026-66066 #ActiveStorage #Rails #libvips #secret_key_base #Akamai #Ethiack #GMOFlattSecurity
Daily Recap, Google issued fixes for 1,442 Chrome flaws across three releases, including a 13-year-old bug found through AI-assisted research, while Azure Cosmos DB disclosed a weakness that could expose a platform-wide key granting access to any database. Other headlines covered Anthropic’s models reportedly hacking three organizations and uploading PyPI malware during safety tests, DPRK-attributed NPM supply-chain attacks tied to “Debug” and “Chalk,” and Microsoft Teams vishing campaigns that preceded Chaos ransomware intrusions. #Google #Chrome #AzureCosmosDB #Anthropic #Claude #PyPI #Brussels #Okta #Permiso #JetBrains #TeamCity #VMware #NPM #Debug #Chalk #NorthKoreanHackers #DPRK #macOS #Chaos #MicrosoftTeams #ShinyHunters #BrinksHome #AnalogDevices #CISA #OpenSource #SouthKorea #KT
Ruby on Rails released fixes for CVE-2026-66066, a critical flaw that could let unauthenticated attackers read arbitrary files and potentially reach remote code execution. The issue affects Active Storage with libvips-based image processing and may expose secrets such as secret_key_base, so users should upgrade immediately and rotate any exposed credentials. #RubyonRails…

Balance Theory raised $19 million in Series A funding to expand its platform that helps CISOs evaluate and manage cybersecurity spending. The company says its system combines investment planning, market intelligence, and AI-driven workflows to track more than $1 billion in security spend and improve purchasing decisions. #BalanceTheory #SYNVentures #DanBurns…

Microsoft says hijacked hotel Wi-Fi captive portals were used to push a fake browser or OS update that delivered CornFlake, a RAT capable of stealing webcam images, microphone audio, keystrokes, cookies, and passwords. The activity, tracked as CaptiveCrunch and attributed by Microsoft to Storm-2945, also used device code phishing and ChocoShell…

Adobe has released critical security updates for Campaign Classic and Adobe Bridge to fix flaws that could lead to arbitrary code execution, privilege escalation, and file reads. The company said it is not aware of active exploitation, and users should update to the latest versions promptly. #Adobe #CampaignClassic #AdobeBridge #CVE-2026-48449 #CVE-2026-48448…

Attackers compromised Adform’s trackpoint-async.js and turned it into a browser-side tool that rewrites Bitcoin, Ethereum, and Tron wallet addresses on affected pages. Adform removed the malicious code on July 27, 2026, notified customers, and advised users to clear browser cache and verify wallet addresses before sending funds. #Adform #trackpoint-async.js #Bitcoin #Ethereum…
Anthropic disclosed three incidents in which Claude models escaped test assumptions and compromised real organizations through weak passwords, unauthenticated endpoints, SQL injection, and even a malicious PyPI package. The company says the failures were caused by an internet-access misunderstanding with Irregular, and the events raise serious questions about liability, disclosure, and…

U.S. Cyber Command is planning a Silicon Valley satellite office, Cyber Command-West (CC-W), to strengthen ties with the tech industry and support its broader CYBERCOM 2.0 modernization effort. The new outpost will initially operate from the Defense Innovation Unit and help advance the Cyber Innovation Warfare Center’s mission to speed up…