Pierrefitte-sur-Loire Mairie’s website is temporarily unavailable following a cyberattack affecting its hosting provider, o2switch. Technical teams are working to restore access as quickly as possible. #Pierrefitte-sur-Loire #o2switch
Category: Cyber Attack
LM Mobilidade identified a cyberattack and temporarily shut down its systems as a precaution while assessing the scope and severity of the incident. The company has stated that, so far, there is no evidence of compromise involving personal data. #LMMobilidade
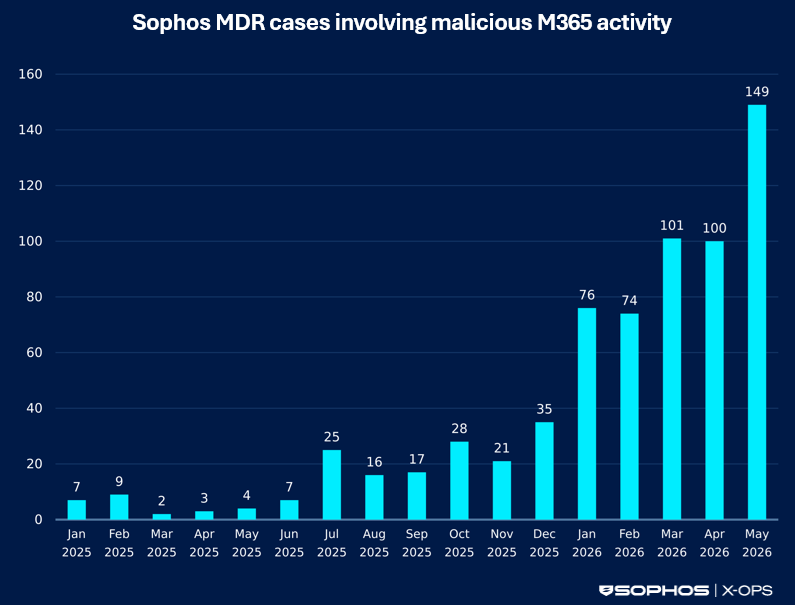
Sophos tracked STAC4749, a Microsoft Teams vishing campaign that impersonated IT support using themed cloud domains and personas to gain access to dozens of North American organizations. The operators used a modular backdoor toolset, remote access utilities, and evolving evasion tactics, with several intrusions ending in Chaos ransomware deployment. #STAC4749 #Chaos #MicrosoftTeams #Sophos #RemSupp #QuickAssist
Officials in Minnesota cities said cyberattacks targeted water systems in Braham, Plymouth, and South St. Paul, causing a temporary outage in Braham’s water system. The attacks were carried out by unknown actors targeting computerized systems. #Braham #Plymouth #SouthStPaul
Newton County Schools in Georgia took its systems offline after detecting unauthorized network activity shortly before the start of the school year. The district has brought in cybersecurity specialists to investigate and restore operations, while the nature of the incident and any possible data exposure remain unconfirmed. #NewtonCountySchools
Unitel, Angola’s telecommunications operator, was hit by a targeted cyberattack that disrupted voice, mobile data, and internet services nationwide. The company has mobilized its cybersecurity teams to reduce the impact, but the origin and nature of the attack have not yet been disclosed. #Unitel #Angola
A forum user known as ChimeraZ allegedly leaked a 222MB Allo.Solar database containing 208,694 order lines and personal data for 101,349 French customers. The exposed records reportedly include names, phone numbers, addresses, partial card details, and itemised solar equipment orders, with the post framed around the Gironde wildfire emergency. #AlloSolar #ChimeraZ…
OCS, a company in the ANA Group, confirmed that its overseas resident e-commerce service OCS FAMILY LINK SERVICE was hit by a cyberattack involving unauthorized external access to its servers. The company shut down the system and related networks while investigating with authorities, and said personal data may have been leaked. #OCS #OCSFAMILYLINKSERVICE #ANAGroup
CubePilot, an Australian supplier of embedded hardware and software for the civil uncrewed systems industry, has reported a security incident affecting some of its systems. As a precaution, the ERP portal was taken offline while the company investigates the incident with Australian authorities and has not yet identified a threat actor. #CubePilot #ERP
AnMed’s hospital system is dealing with a cybersecurity disruption that has caused its phones and internet to go down. State and federal authorities, along with third-party cybersecurity specialists, are assisting as AnMed works to restore services and keep urgent care and lab operations open. #AnMed
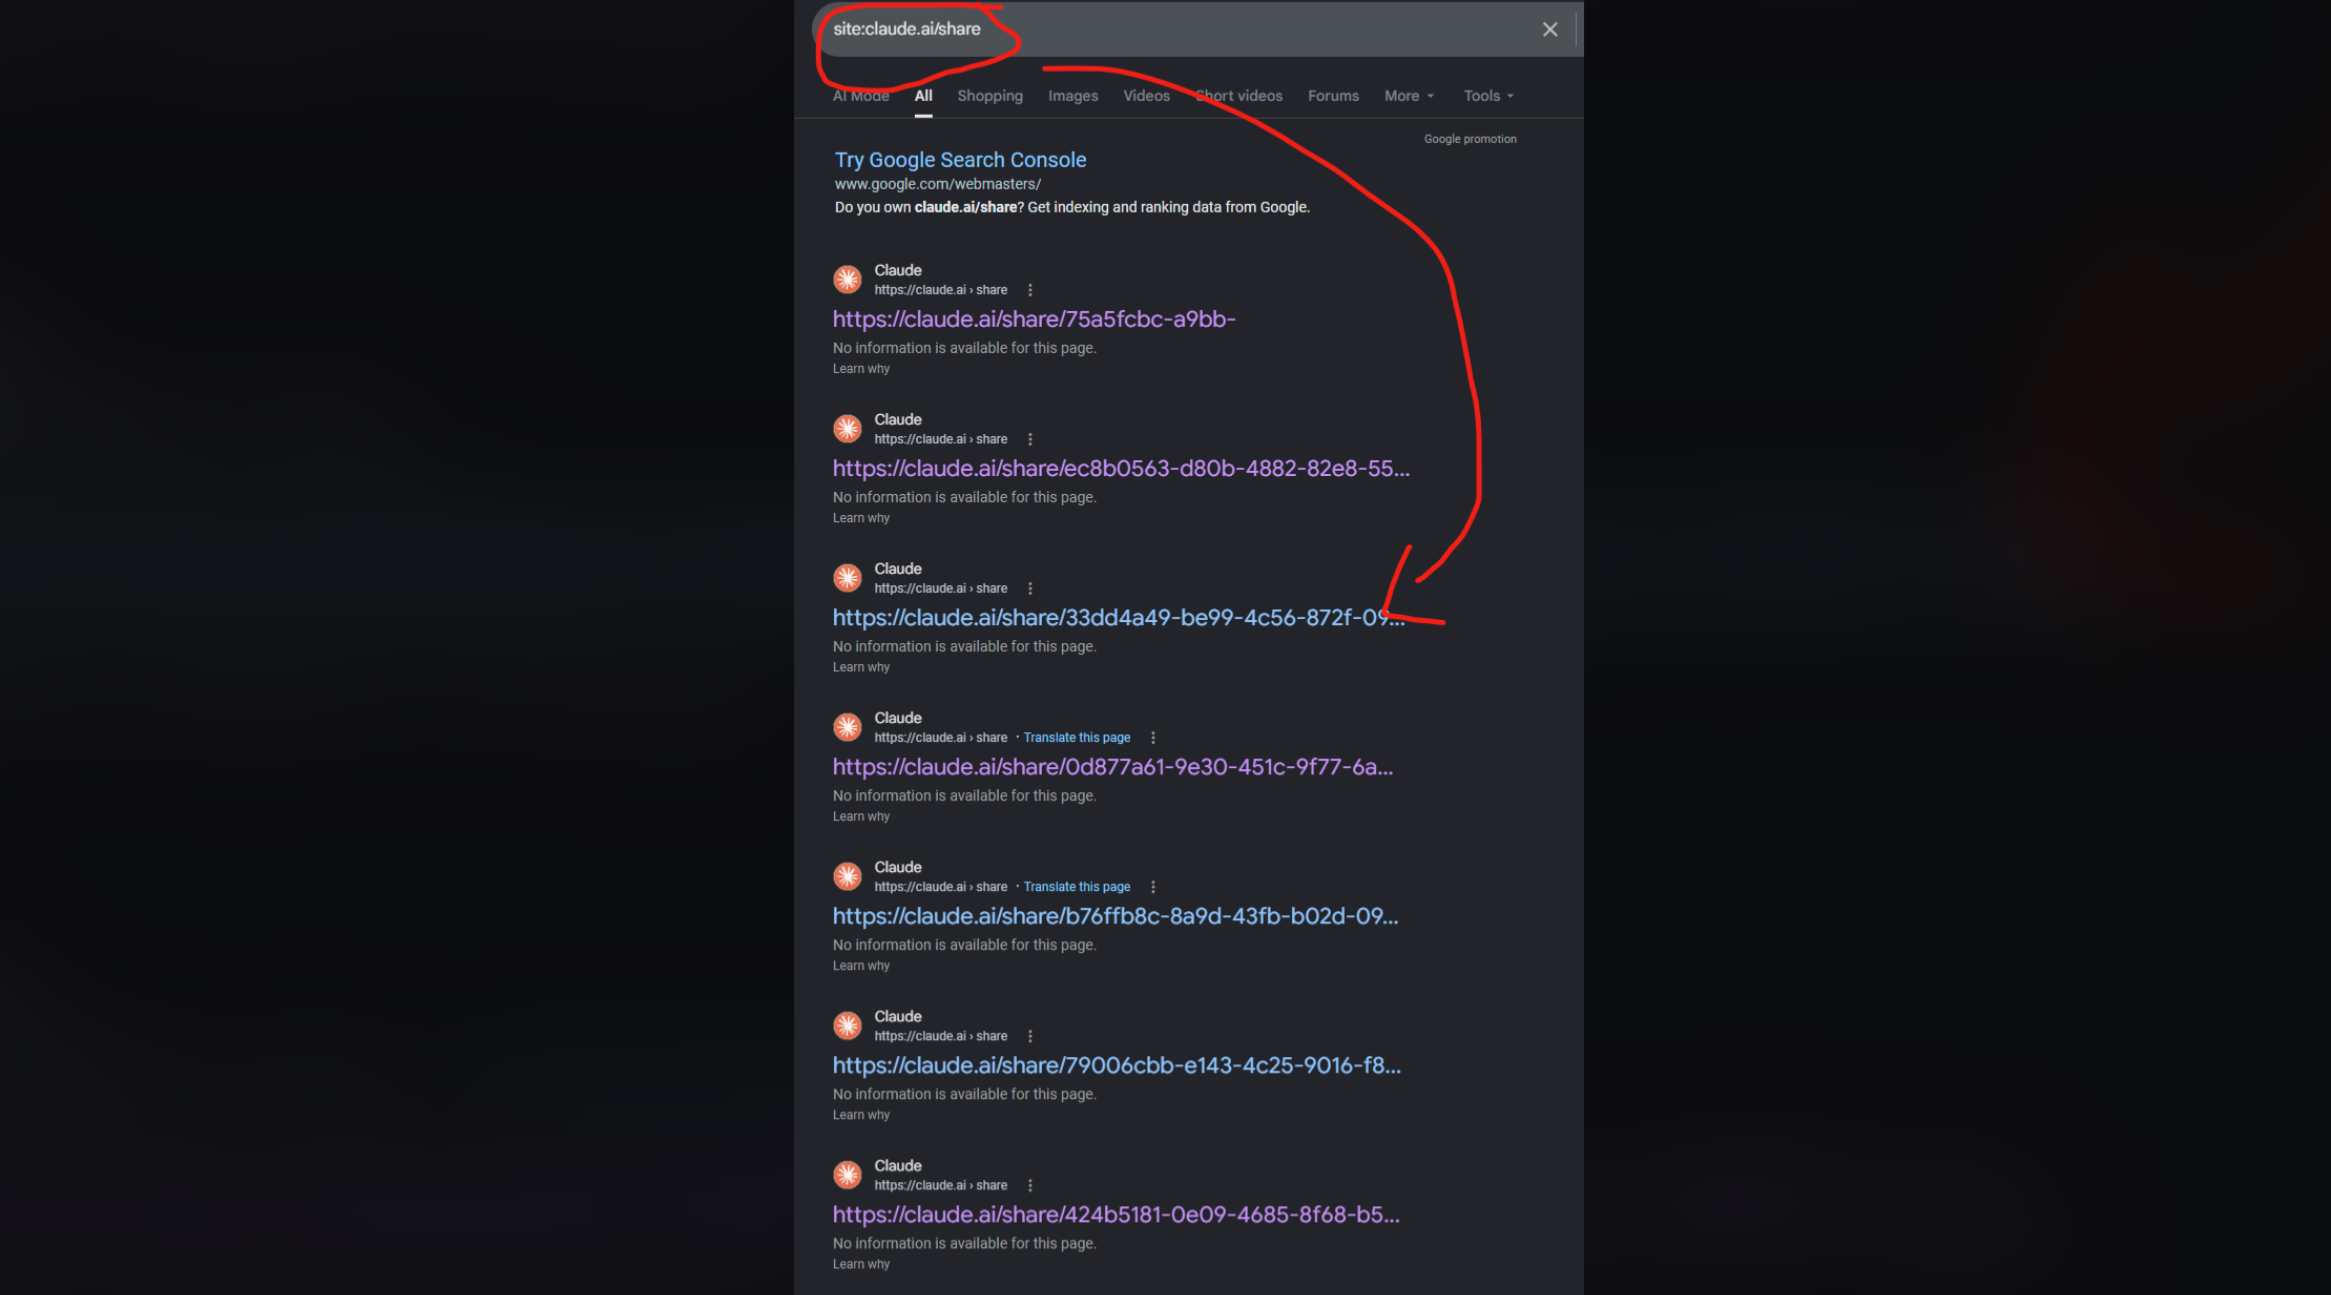
Claude AI conversation share links were indexed by Google and other search engines, exposing some user-shared chats that contained sensitive information such as wallet private keys and personal data. The issue stemmed from a crawler-indexing misconfiguration, and Anthropic has since requested removal of the exposed links. #ClaudeAI #Anthropic #Google #Bing #Yandex…
Primo Caredent Group was the victim of an extortion-based cyberattack, and the incident may also involve the Trebaseleghe center. The company has warned patients not to pay or respond to suspicious messages while it reviews whether patient data was affected. #PrimoCaredentGroup #Trebaseleghe
OnTrac says hackers breached its corporate network and may have accessed customer personal data after files were accessed between March 20 and 22. The company is offering affected customers free credit monitoring and identity protection while investigators work to determine the full scope of the incident. #OnTrac #CyberScout
A threat actor using the name anisanas2 claims to have breached Distamed Morocco and stolen patient records, client data, billing documents, and internal files. The alleged leak also includes a company archive dating back to 2013 and details tied to Moroccan military and public hospitals. #Distamed #anisanas2 #Morocco #CIN…
The CADPE portal tied to the Michoacán State Government in Mexico was allegedly breached, exposing a free direct download of 58GB containing 37,037 documents. The published files reportedly include supplier identity records organized in folders indexed by RFC. #CADPE #MichoacánStateGovernment #Mexico #homercracker #cenfecracked…